
stumpy
 stumpy-dev/stumpy
Scalable Python library for time series analysis via matrix profiles, enabling motif discovery, anomaly detection, semantic segmentation, and…
anomaly-detectiongeneral-purpose-utilitiesmachine-learning
stumpy-dev/stumpyScalable Python library for time series analysis via matrix profiles, enabling motif discovery, anomaly detection, semantic segmentation, and…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 nzymeorg/nzyme
WiFi, Bluetooth and Ethernet Threat Detection.
 baidu/openrasp
Runtime application self-protection engine that hooks into application servers to monitor and block malicious database queries, file operations, and…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
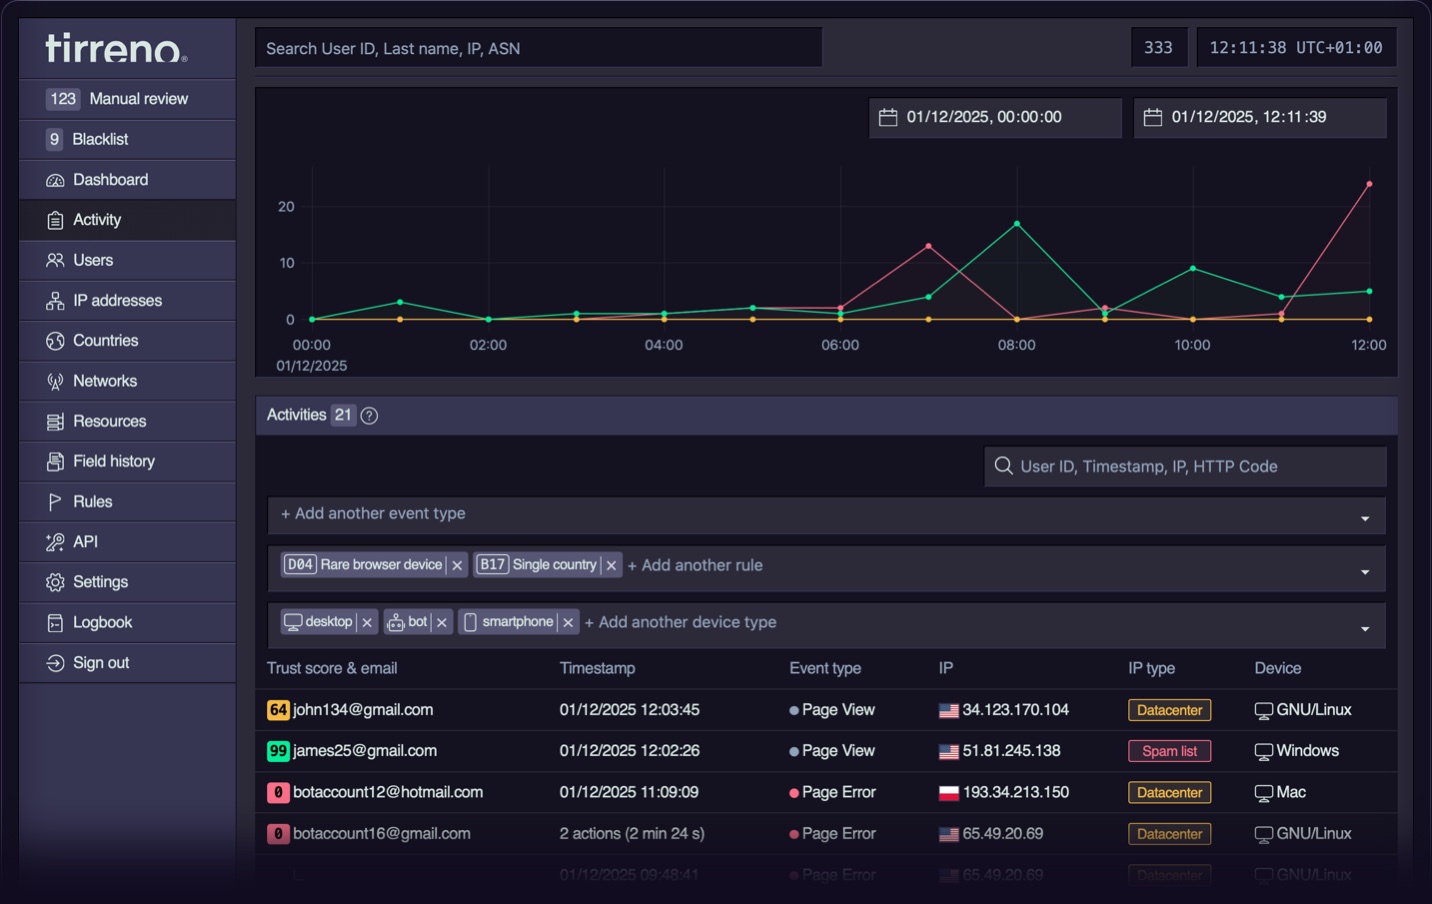 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 seldonio/alibi-detect
Algorithms for outlier, adversarial and drift detection
 betterdb-inc/monitor
Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 endgameinc/dga_predict
LSTM-based classifier for detecting domain generation algorithm (DGA) domains, with Keras implementations of neural network and bigram models for DNS…