
CVE-2023-35674
 thampakon/cve-2023-35674
ช่องโหว่ CVE-2023-35674 *สถานะ: ยังไม่เสร็จ*
android-securityexploitationmobile-security+2
thampakon/cve-2023-35674ช่องโหว่ CVE-2023-35674 *สถานะ: ยังไม่เสร็จ*
 sahalll/cve-2024-54916
Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…
 uthrasri/frameworks_opt_net_wifi_cve-2021-0466
 vino-theva/cve-2019-6447
This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…
 nanopathi/packages_apps_managedprovisioning_cve-2021-39692
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 sandarufdo/es-file-explorer-open-port-vulnerability---cve-2019-6447
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 vinukalana/cve-2019-6447-android-vulnerability-in-es-file-explorer
This repository is developed to understand CVE-2019-6447
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
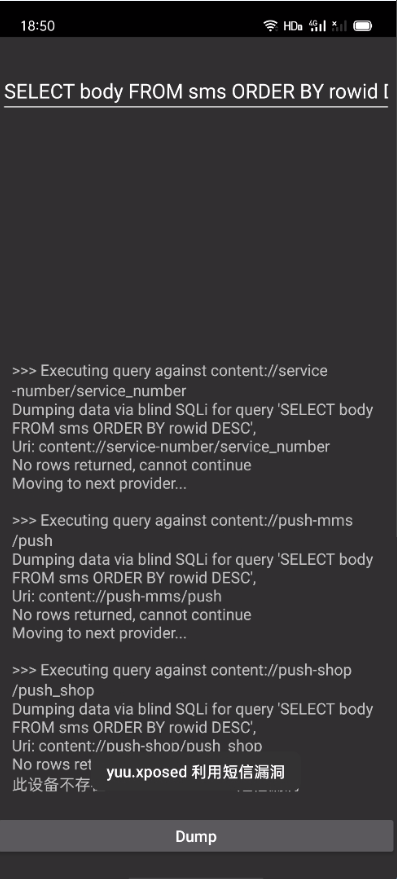 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
 linuxoid-cn/mi8e5-unlocker-by-cve-2026-43499
基于 CVE-2026-43499 的 8E5 机型自动化解锁辅助工具,仅限授权安全研究与自有设备使用。
 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
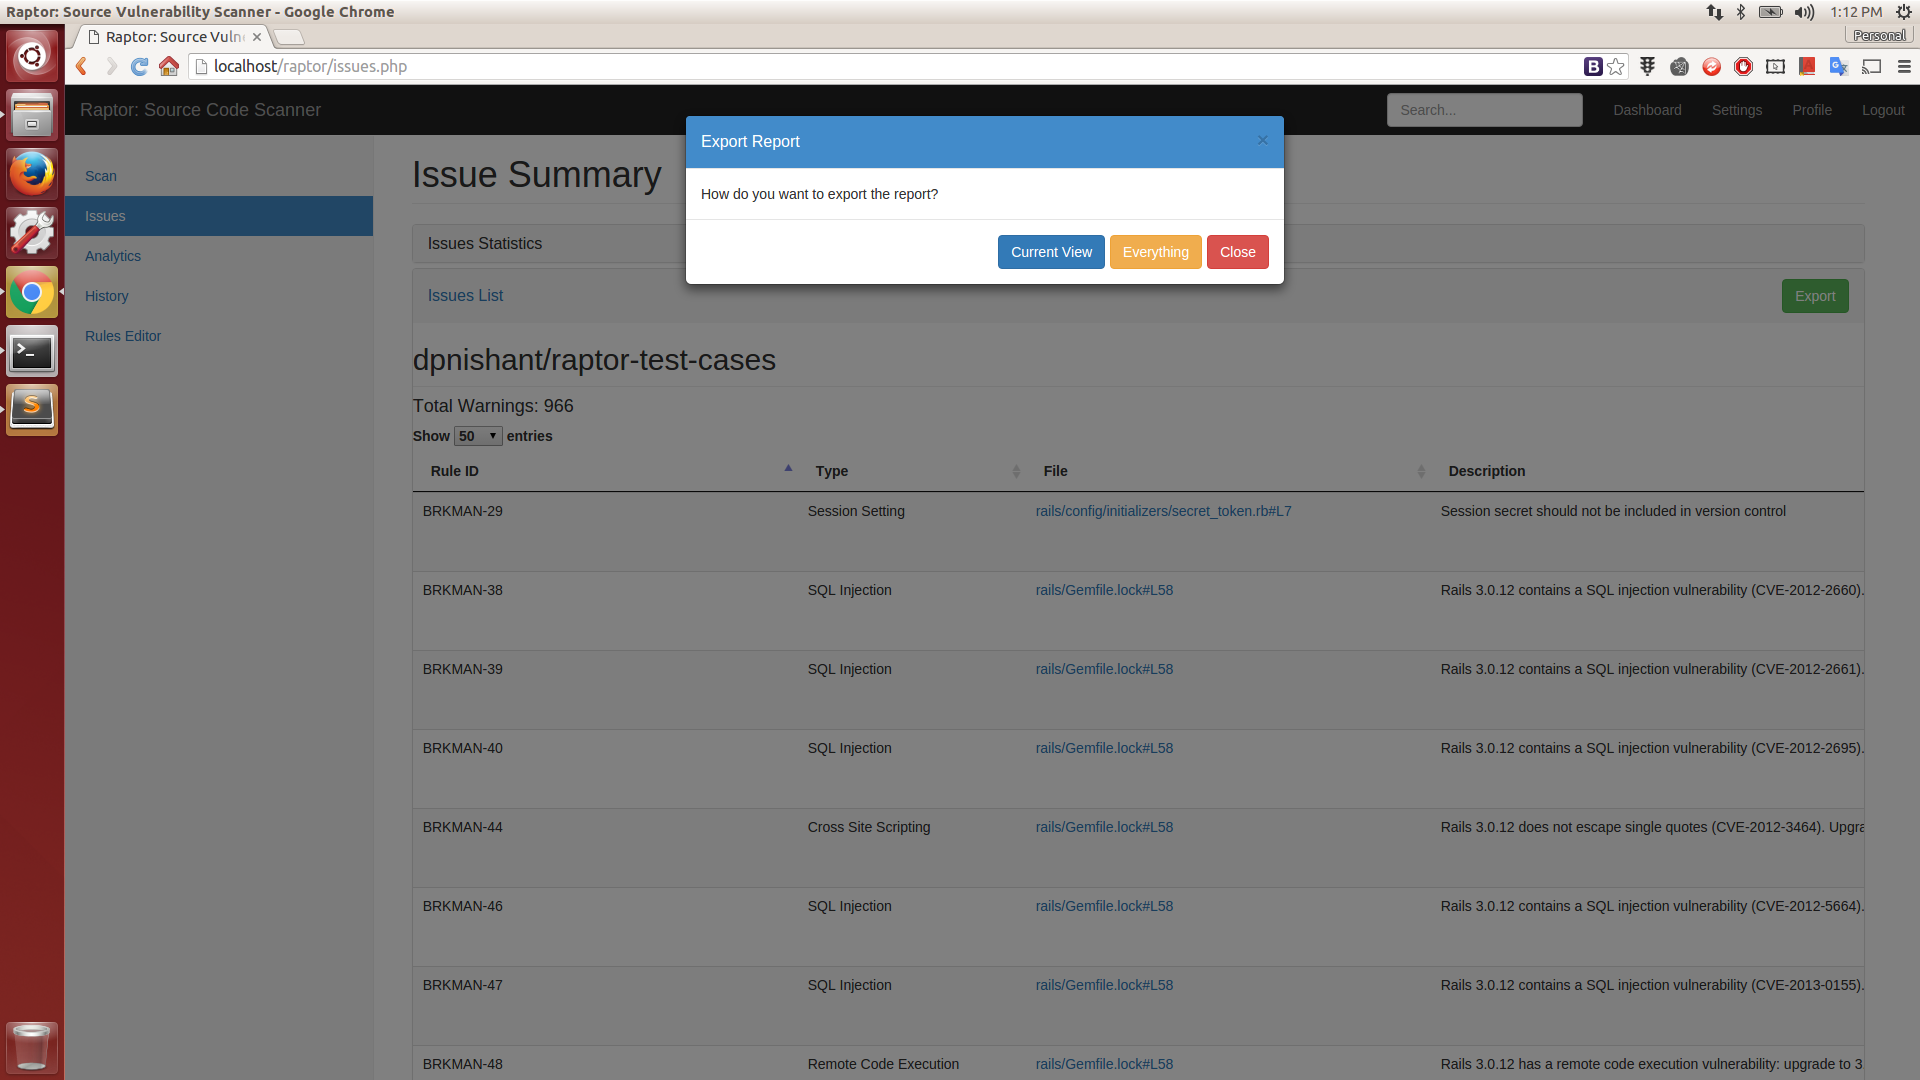 dpnishant/raptor
Web-based Source Code Vulnerability Scanner
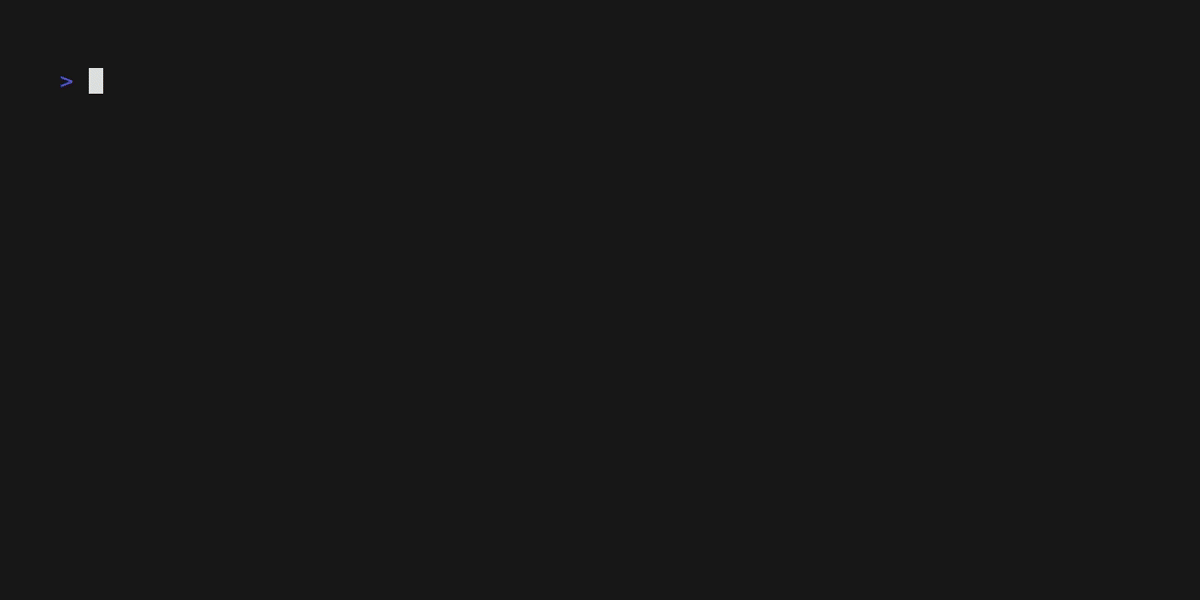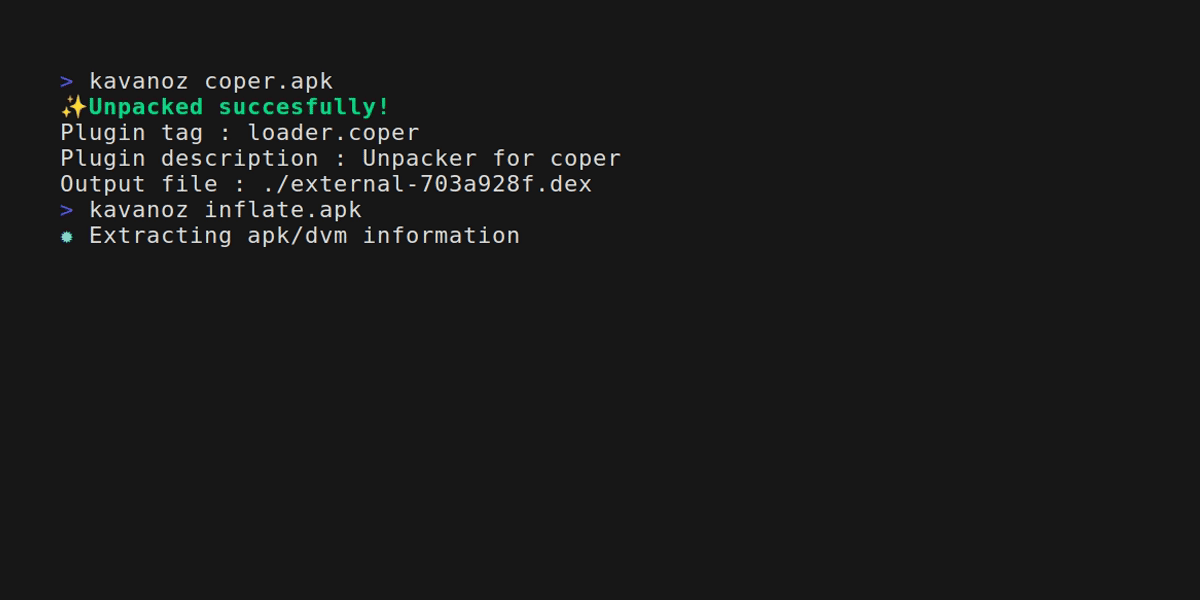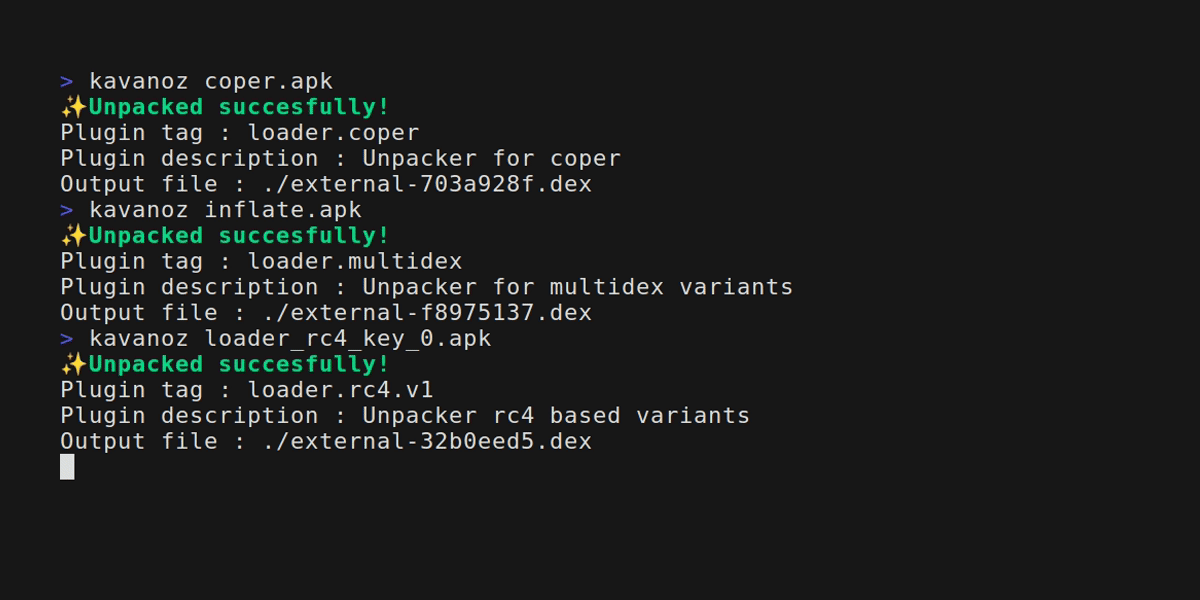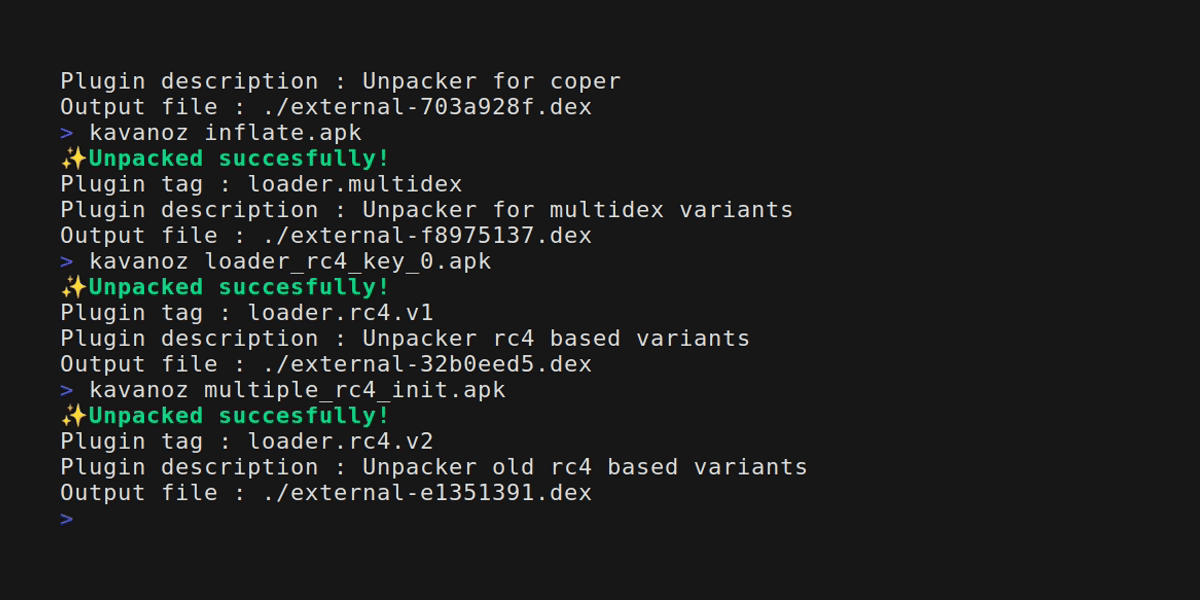 eybisi/kavanoz
Statically unpacking common android banker malware.
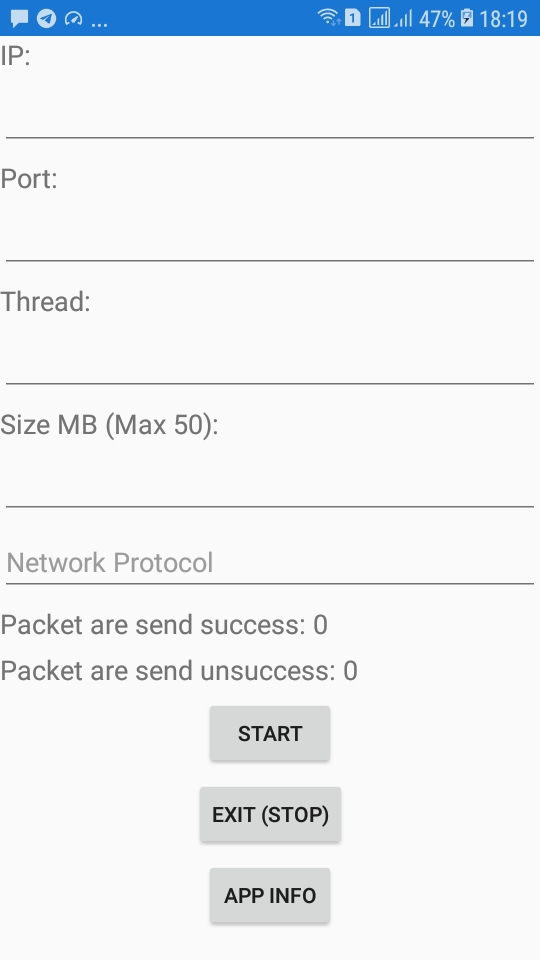 blueskychan-dev/ddospacket
Use own Phone to DoS Attack without Termux! (Android 5.1+)