
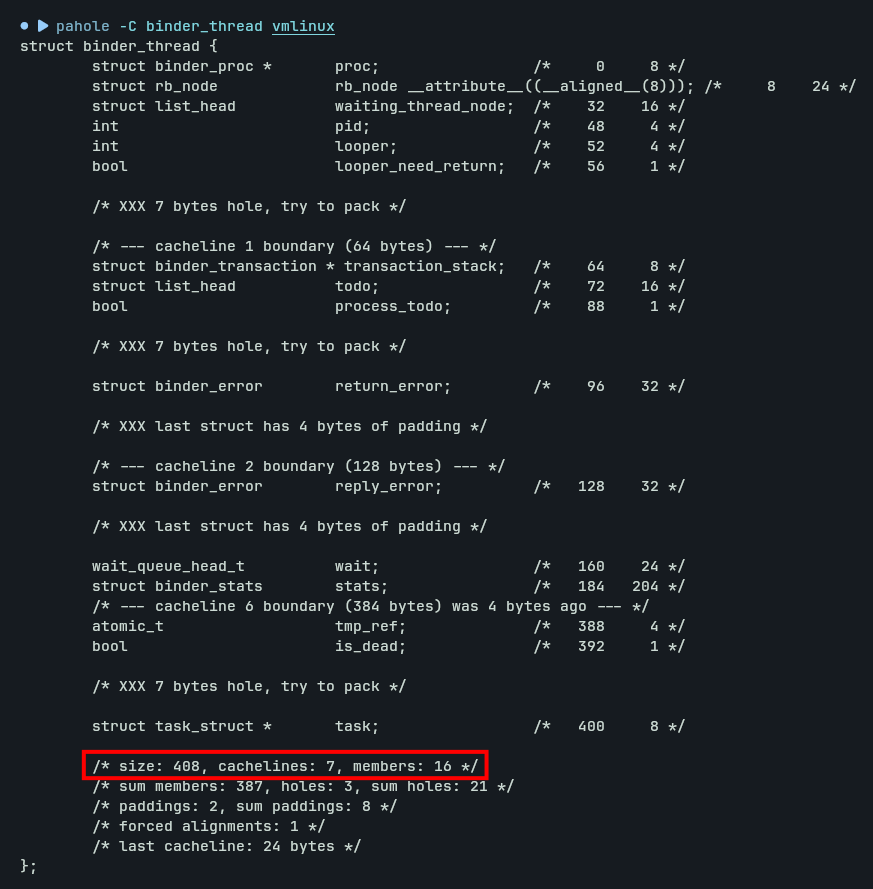
CVE_2019_2215
 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
android-securitybinary-exploitationeducation+5
0xbinder/cve_2019_2215Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 jakestone594/f_hid-4.14-backports
Backports of three published f_hid fixes (incl. CVE-2026-31721, CVE-2026-31606) to an EOL Linux 4.14.190 Android vendor kernel, with on-device…
 xyzasian/janus-cve-2017-13156
Java-based exploit tool for CVE-2017-13156 that bypasses Android APK signature verification by appending a DEX file to an existing APK, enabling code…
 k0mraid3/k0mraid3s-system-shell-prebuilt
Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…
 reverseclabs/cve-2021-25374_samsung-account-access
This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 linkedin/qark
Tool to look for several security related Android application vulnerabilities
 viliuskraujutis/androidbroadcastsmonitor
A tool to subscribe to receive all standard Android broadcasts on your Android device.
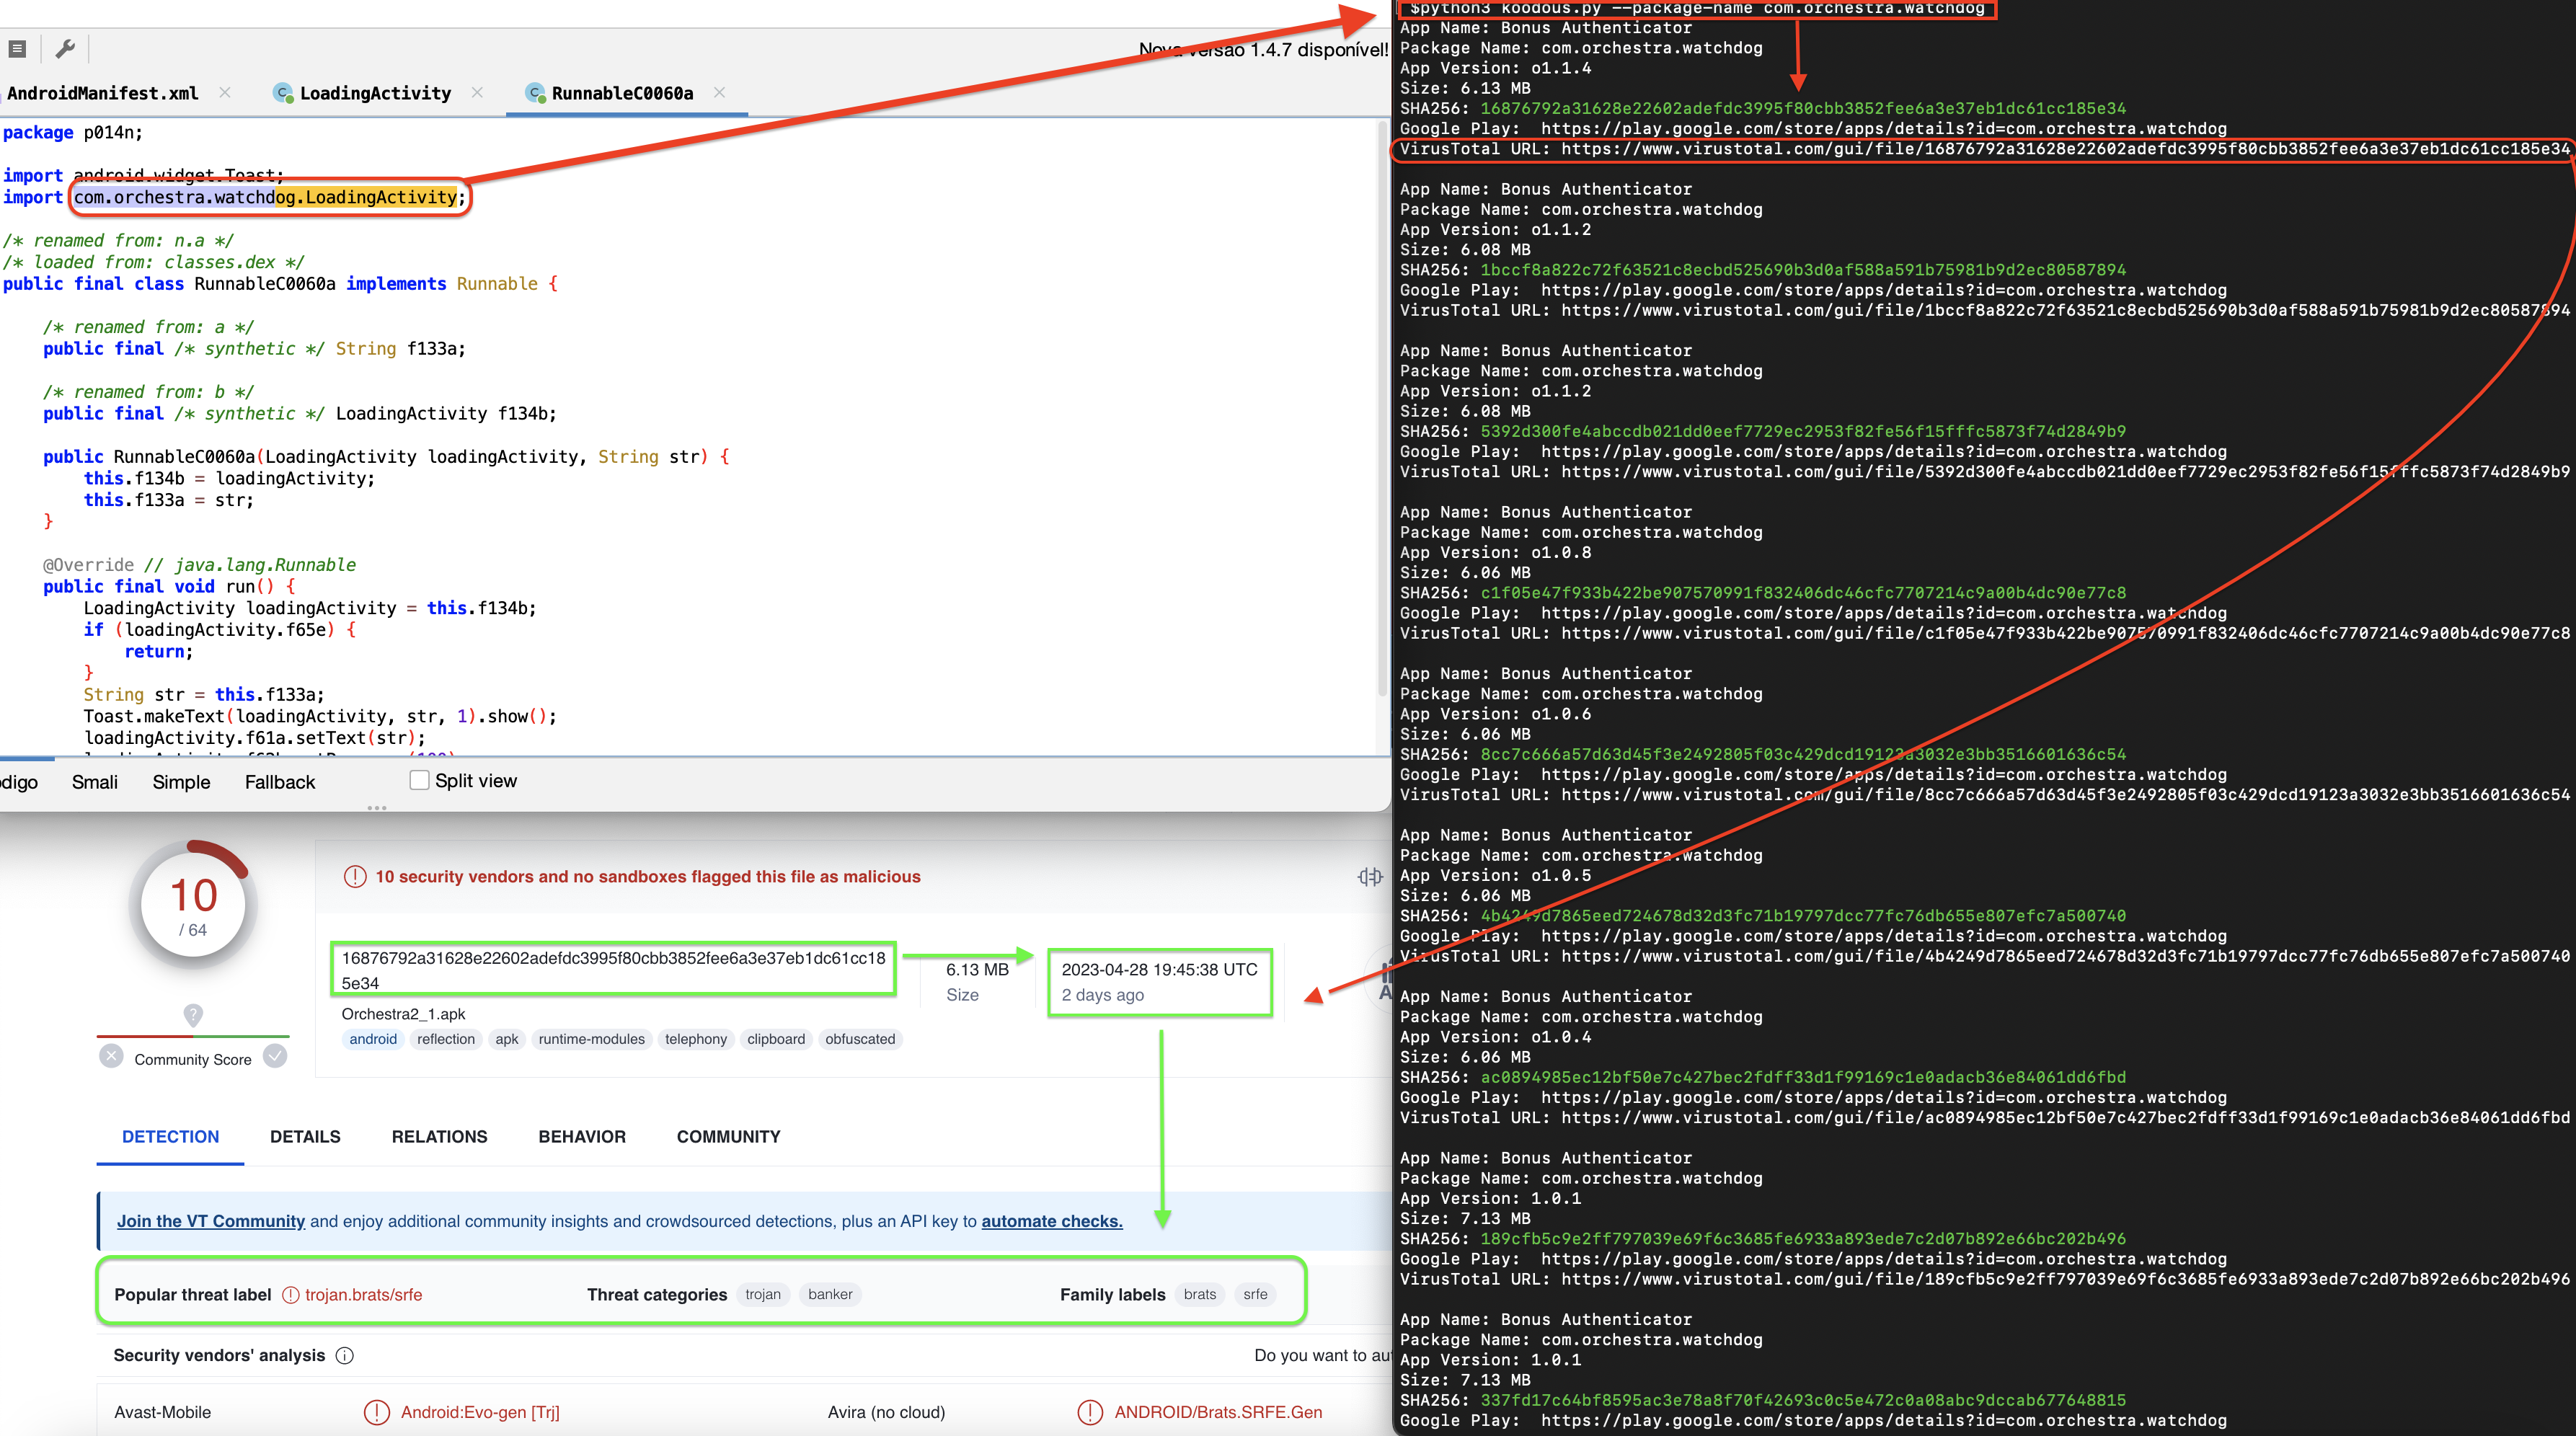 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 virtualesp/springpeace
(Hopefully) A tool to root for (most) Android devices through CVE-2026-43499
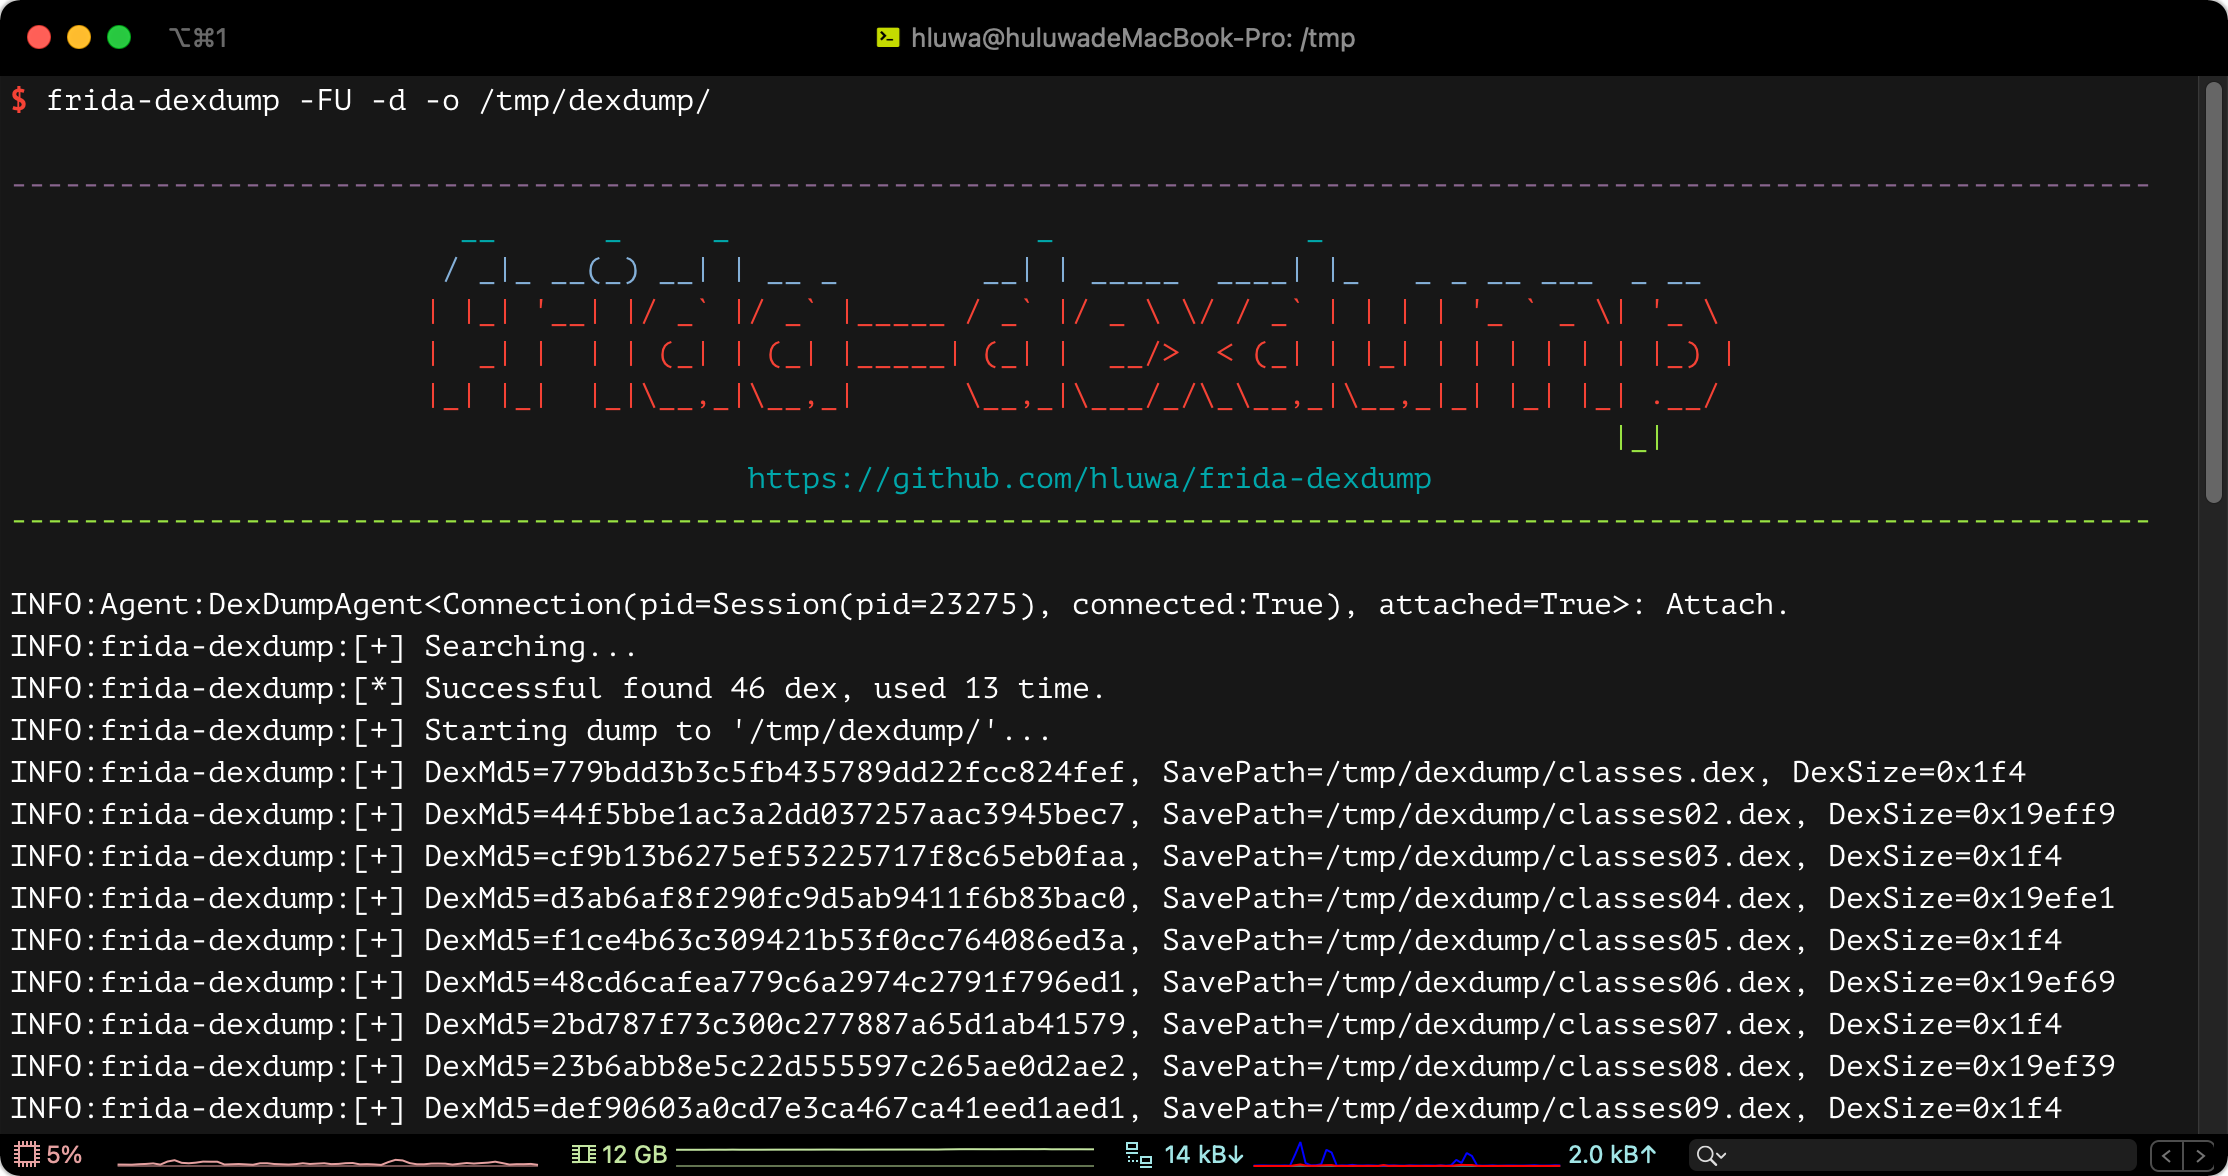 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 rscloura/doldrums
A Flutter/Dart reverse engineering tool
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 rev-code/androidclient
Android remote administration client
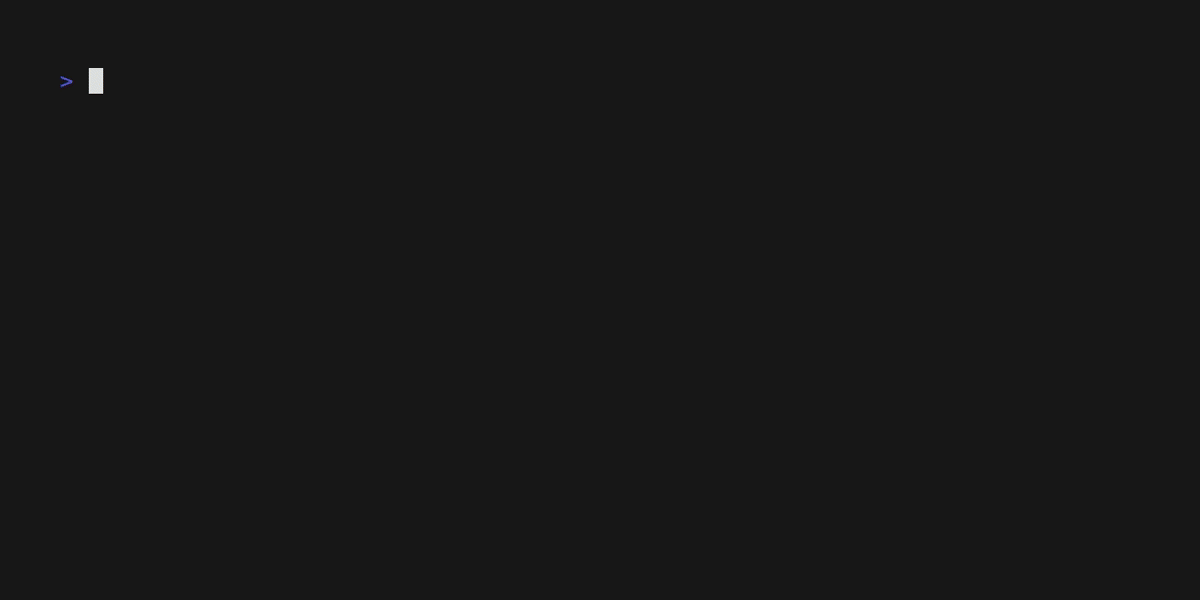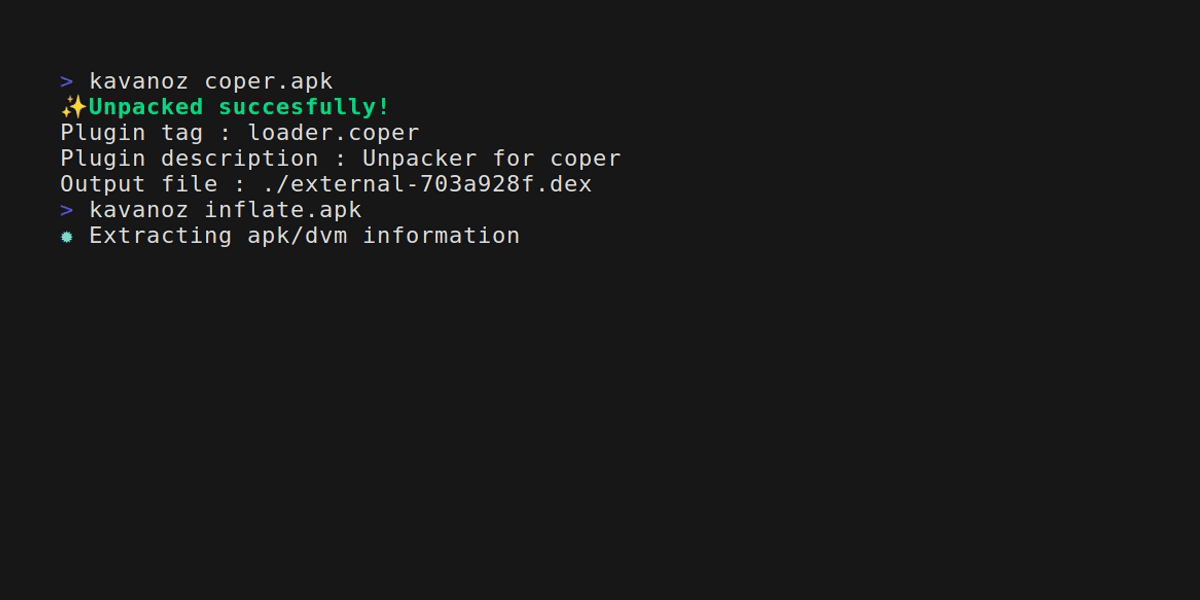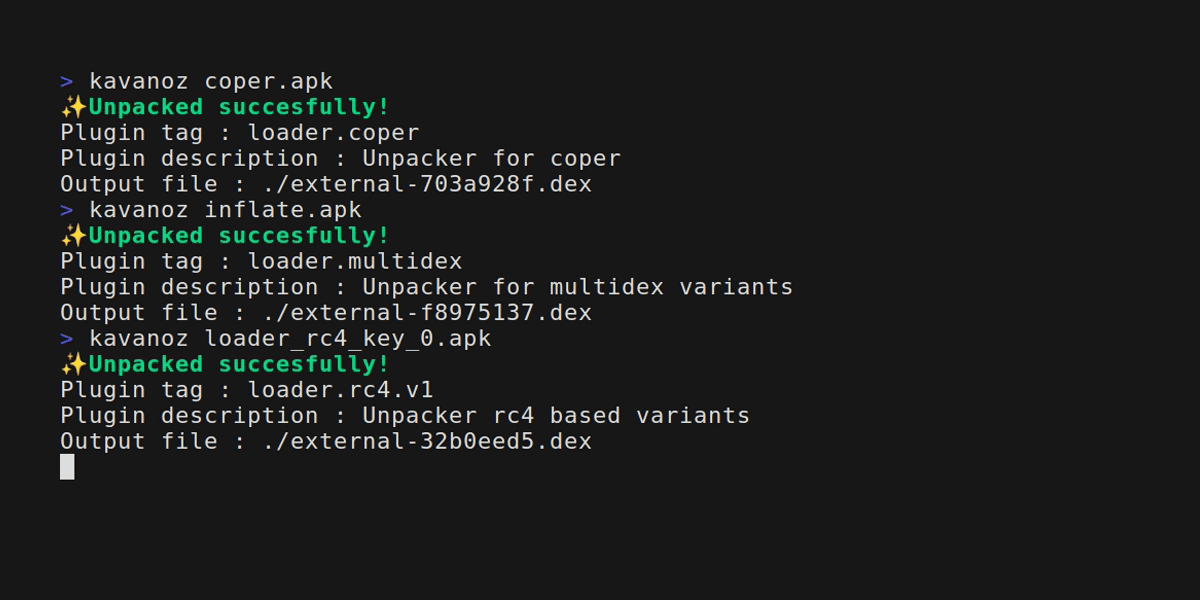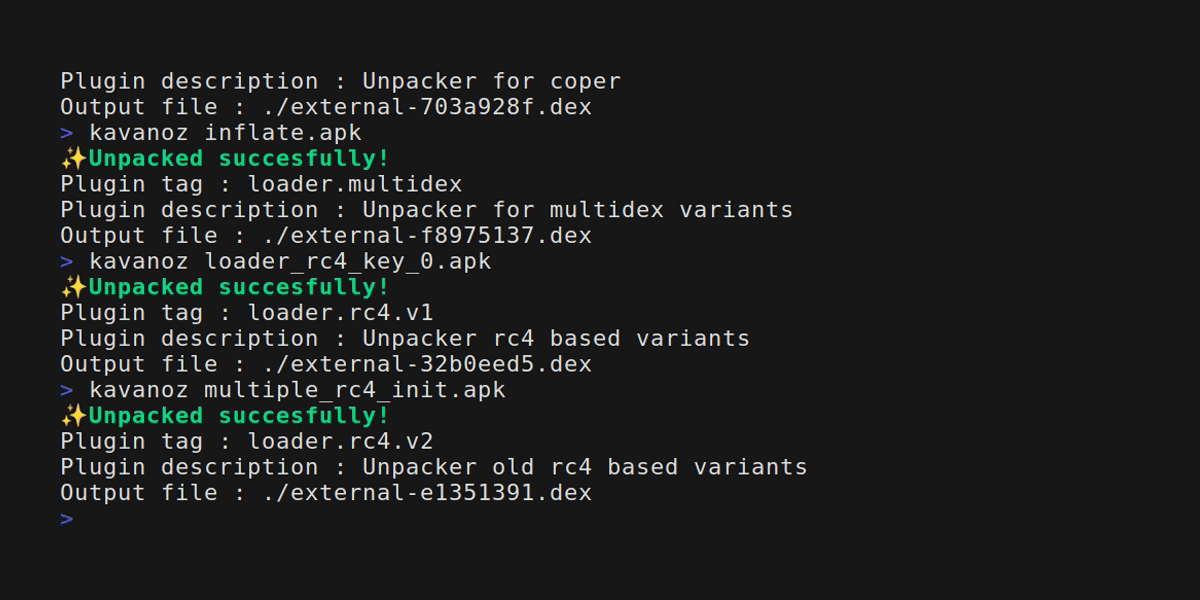 eybisi/kavanoz
Statically unpacking common android banker malware.
 michalbednarski/resourcepoison
Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…