
framework_base_AOSP10_r33_CVE-2020-0137
 nanopathi/framework_base_aosp10_r33_cve-2020-0137
android-securityvulnerability-analysisexploitation+2
nanopathi/framework_base_aosp10_r33_cve-2020-0137 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
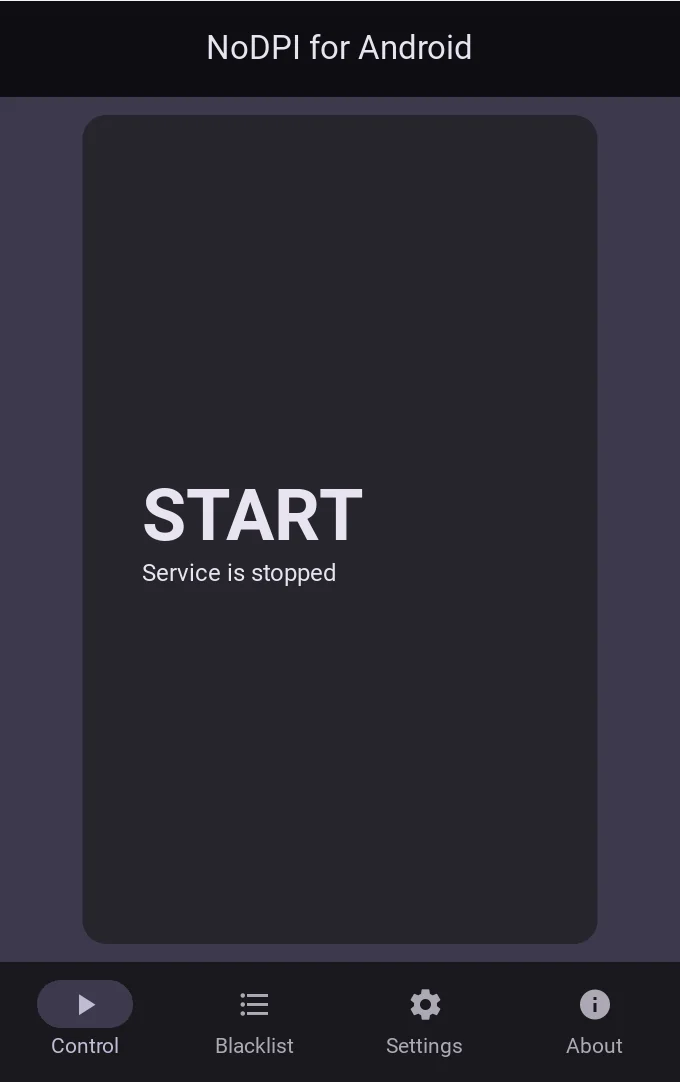 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 maoabc/nmmp
dex-vm used to protect the android classes.dex file
 openbba0/bba
Android app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 google/android-classyshark
Android and Java bytecode viewer
 thespeedx/tbomb
This is a SMS And Call Bomber For Linux And Termux
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
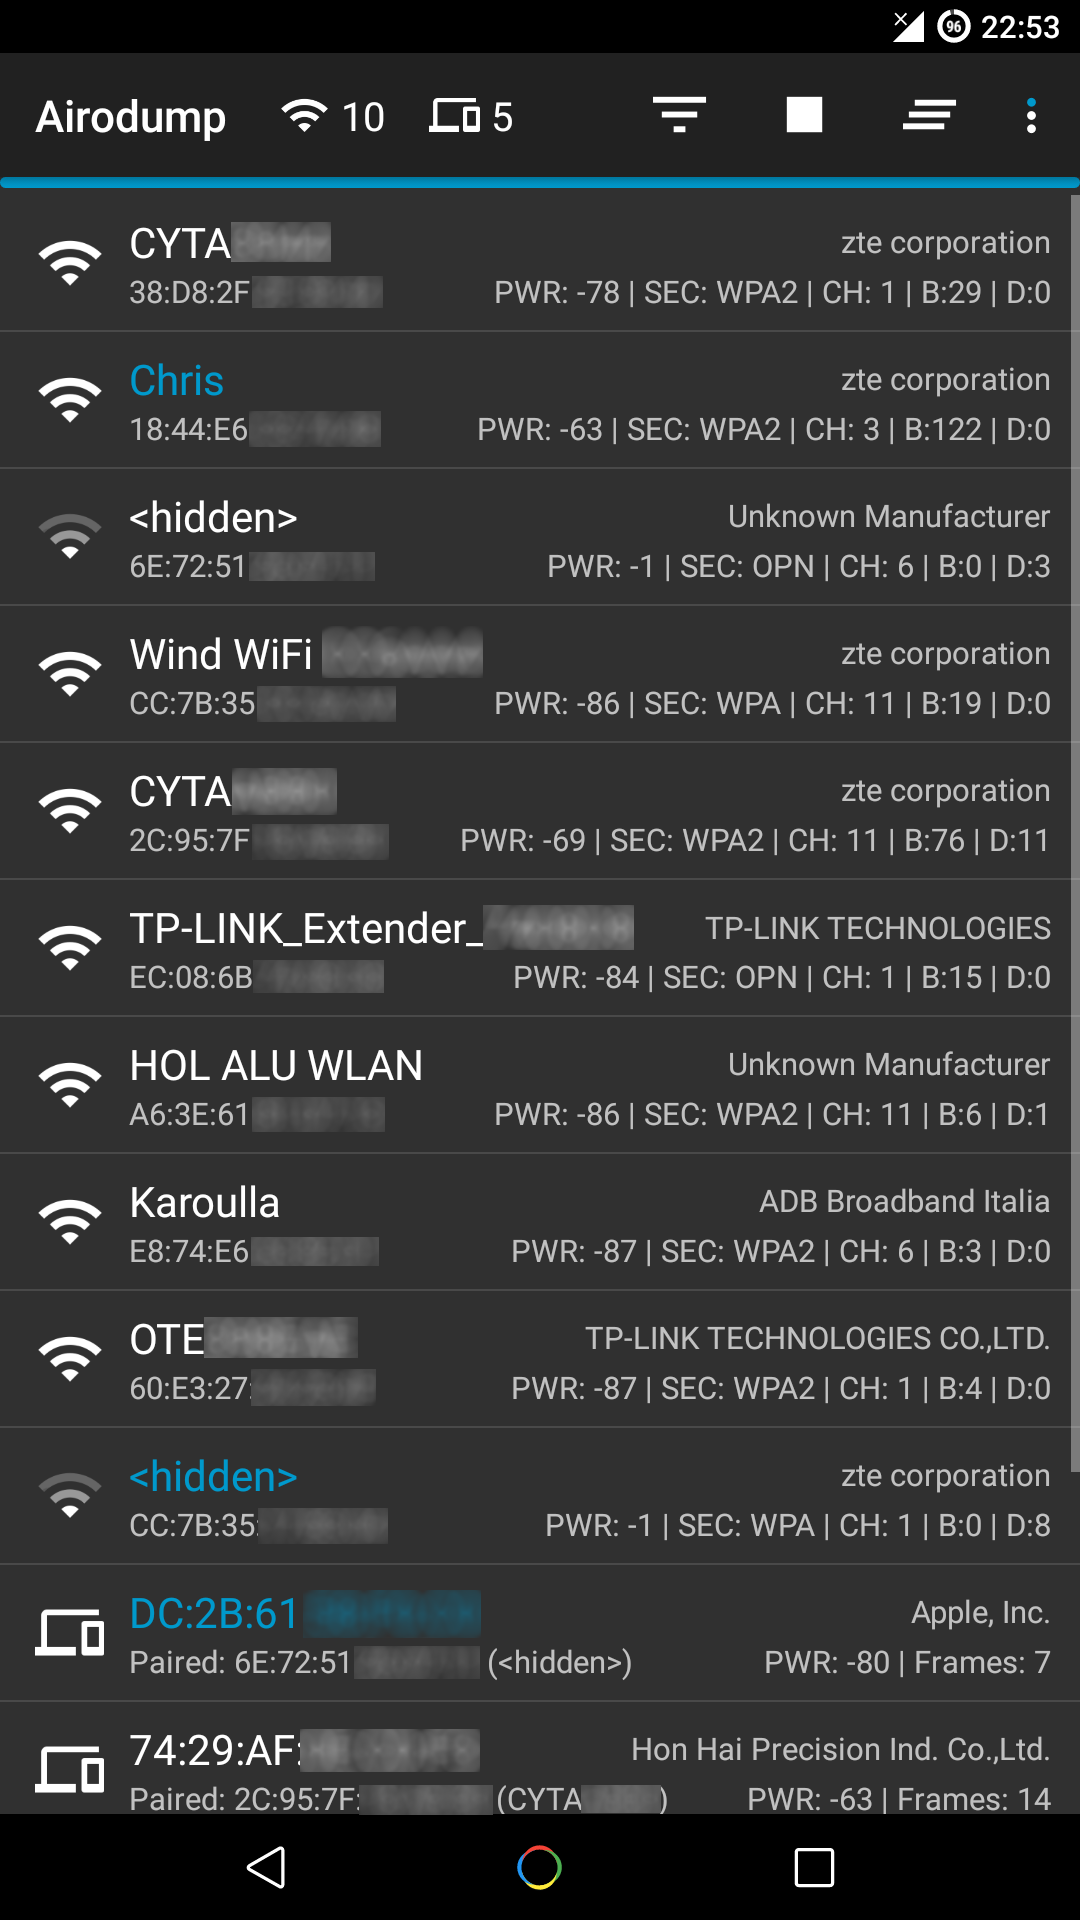 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android

 ptswarm/reflutter
Flutter Reverse Engineering Framework
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 androbugs/androbugs_framework
AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…
