

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
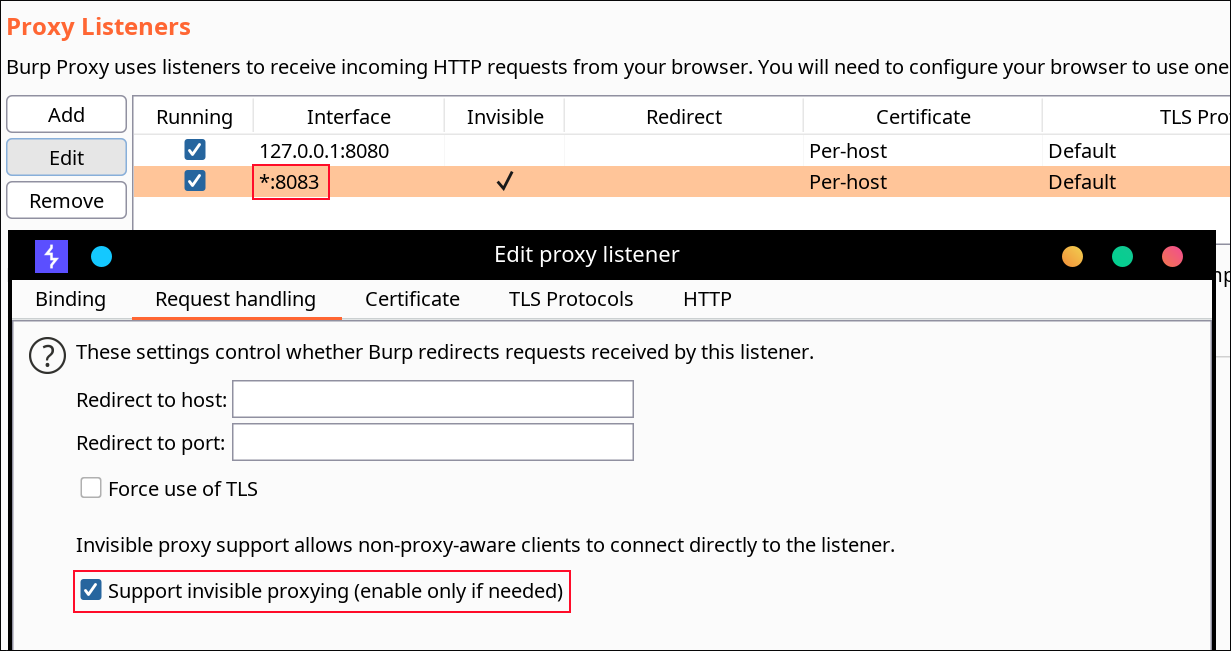 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
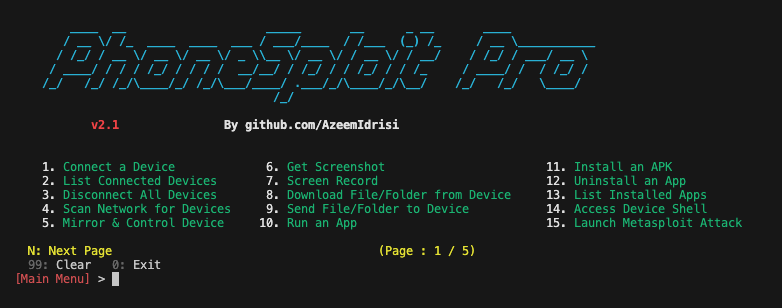 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 techupdate24/capacitor-flaw-cve-2026-103922
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 xiaobailovesstirring/cve-2025-48595-exploit
CVE-2025-48595 Android Framework Integer Overflow PoC - 优化版
 fevar54/cve-2025-48595-android-framework-integer-overflow-
PoC de CVE-2025-48595: desbordamiento de entero en multiples ubicaciones del Framework de Android.
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
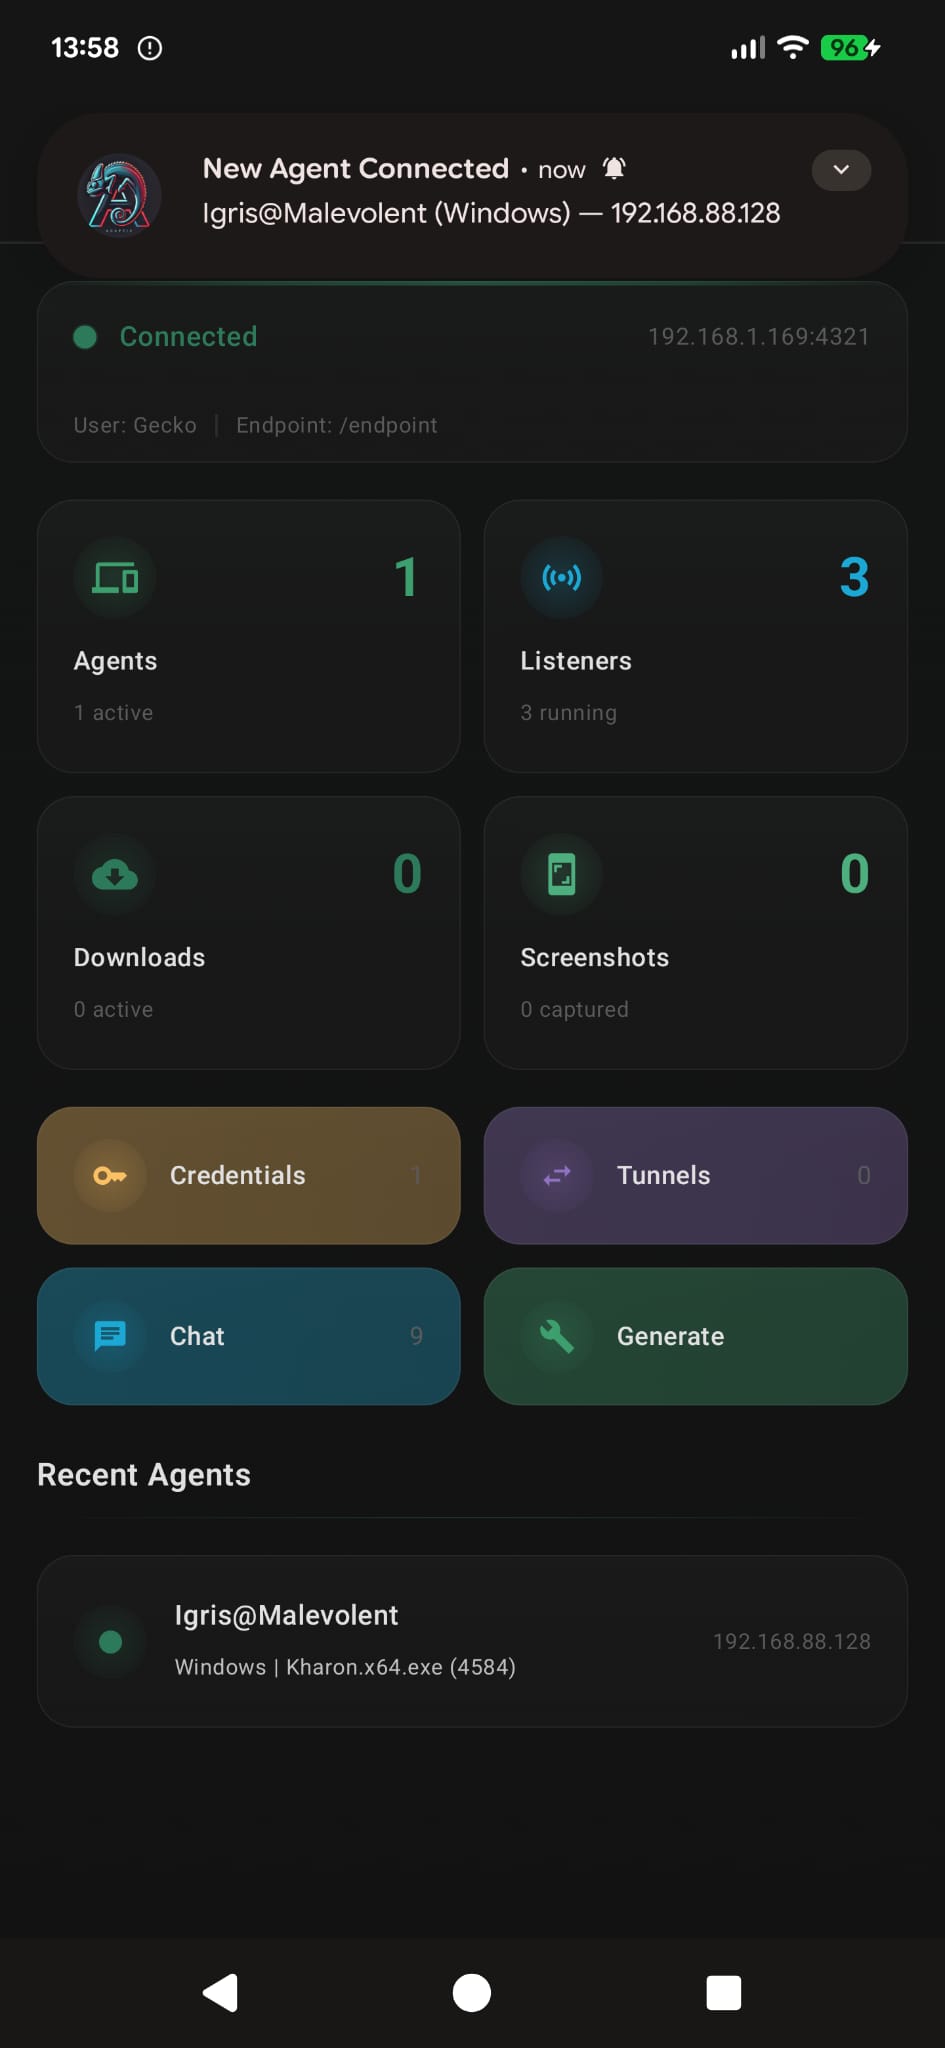 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 entysec/ghost
Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 pazhanivelmani/frameworks_base_android_6.0.1_r22_cve-2018-9338
Android 6.0.1 framework base repository containing the CVE-2018-9338 vulnerability for analysis and exploitation research.