
CVE-2024-23700-C2-Server
 kaitokidc500/cve-2024-23700-c2-server
Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
android-securitycommand-and-controldata-exfiltration+9
kaitokidc500/cve-2024-23700-c2-serverSource code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
 tinnci/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 gitamans/zygoteexploitdemo
Educational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android
 chengfeng30121/cve-2024-31317-poc
针对Android系统的CVE-2024-31317漏洞的概念验证脚本集合
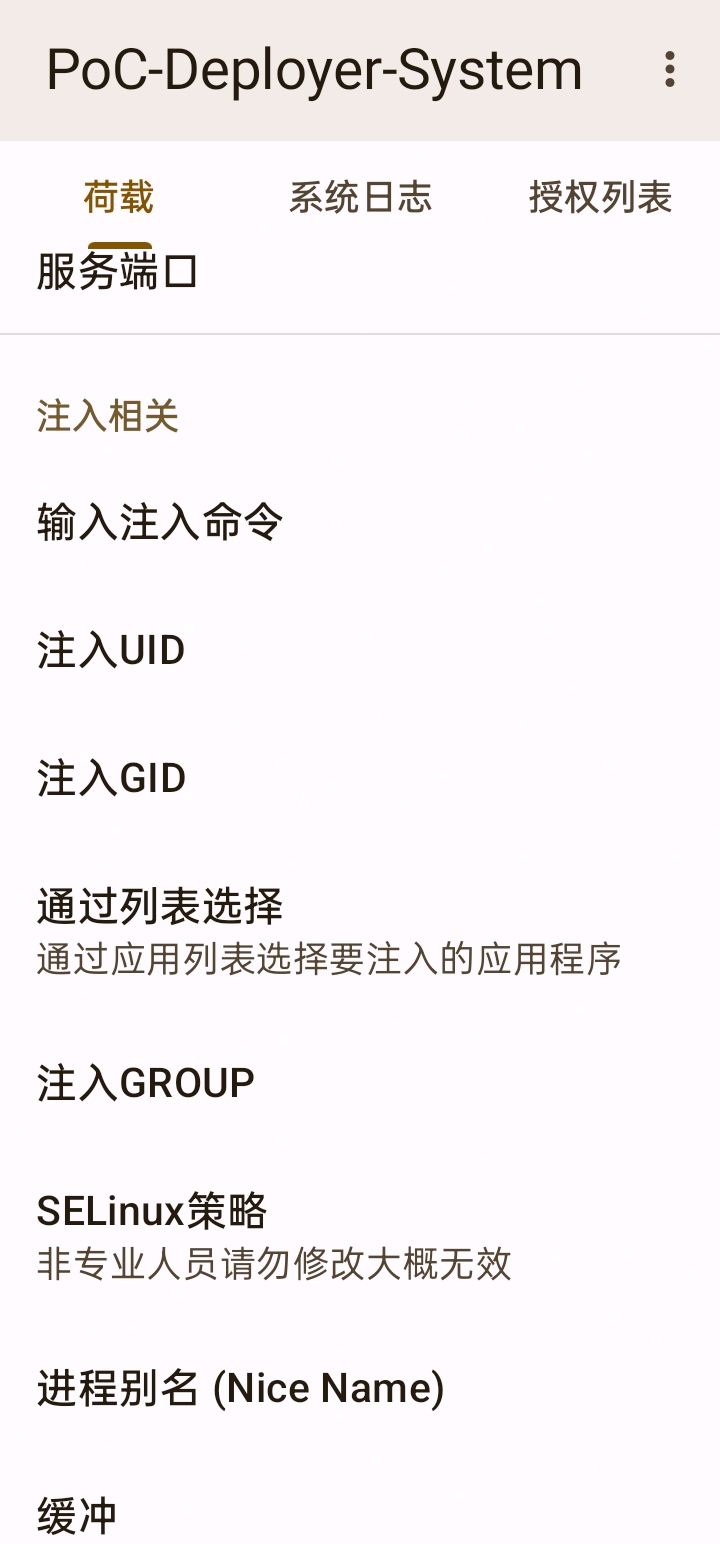 wqry085/poc-deployer-system
Quick tool for utilizing CVE-2024-31317 on Android
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…
 fcy10012/cve-2024-31317-deployer
CVE-2024-31317 Android Zygote命令注入漏洞研究与部署工具 | Android 9-13 漏洞利用框架
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
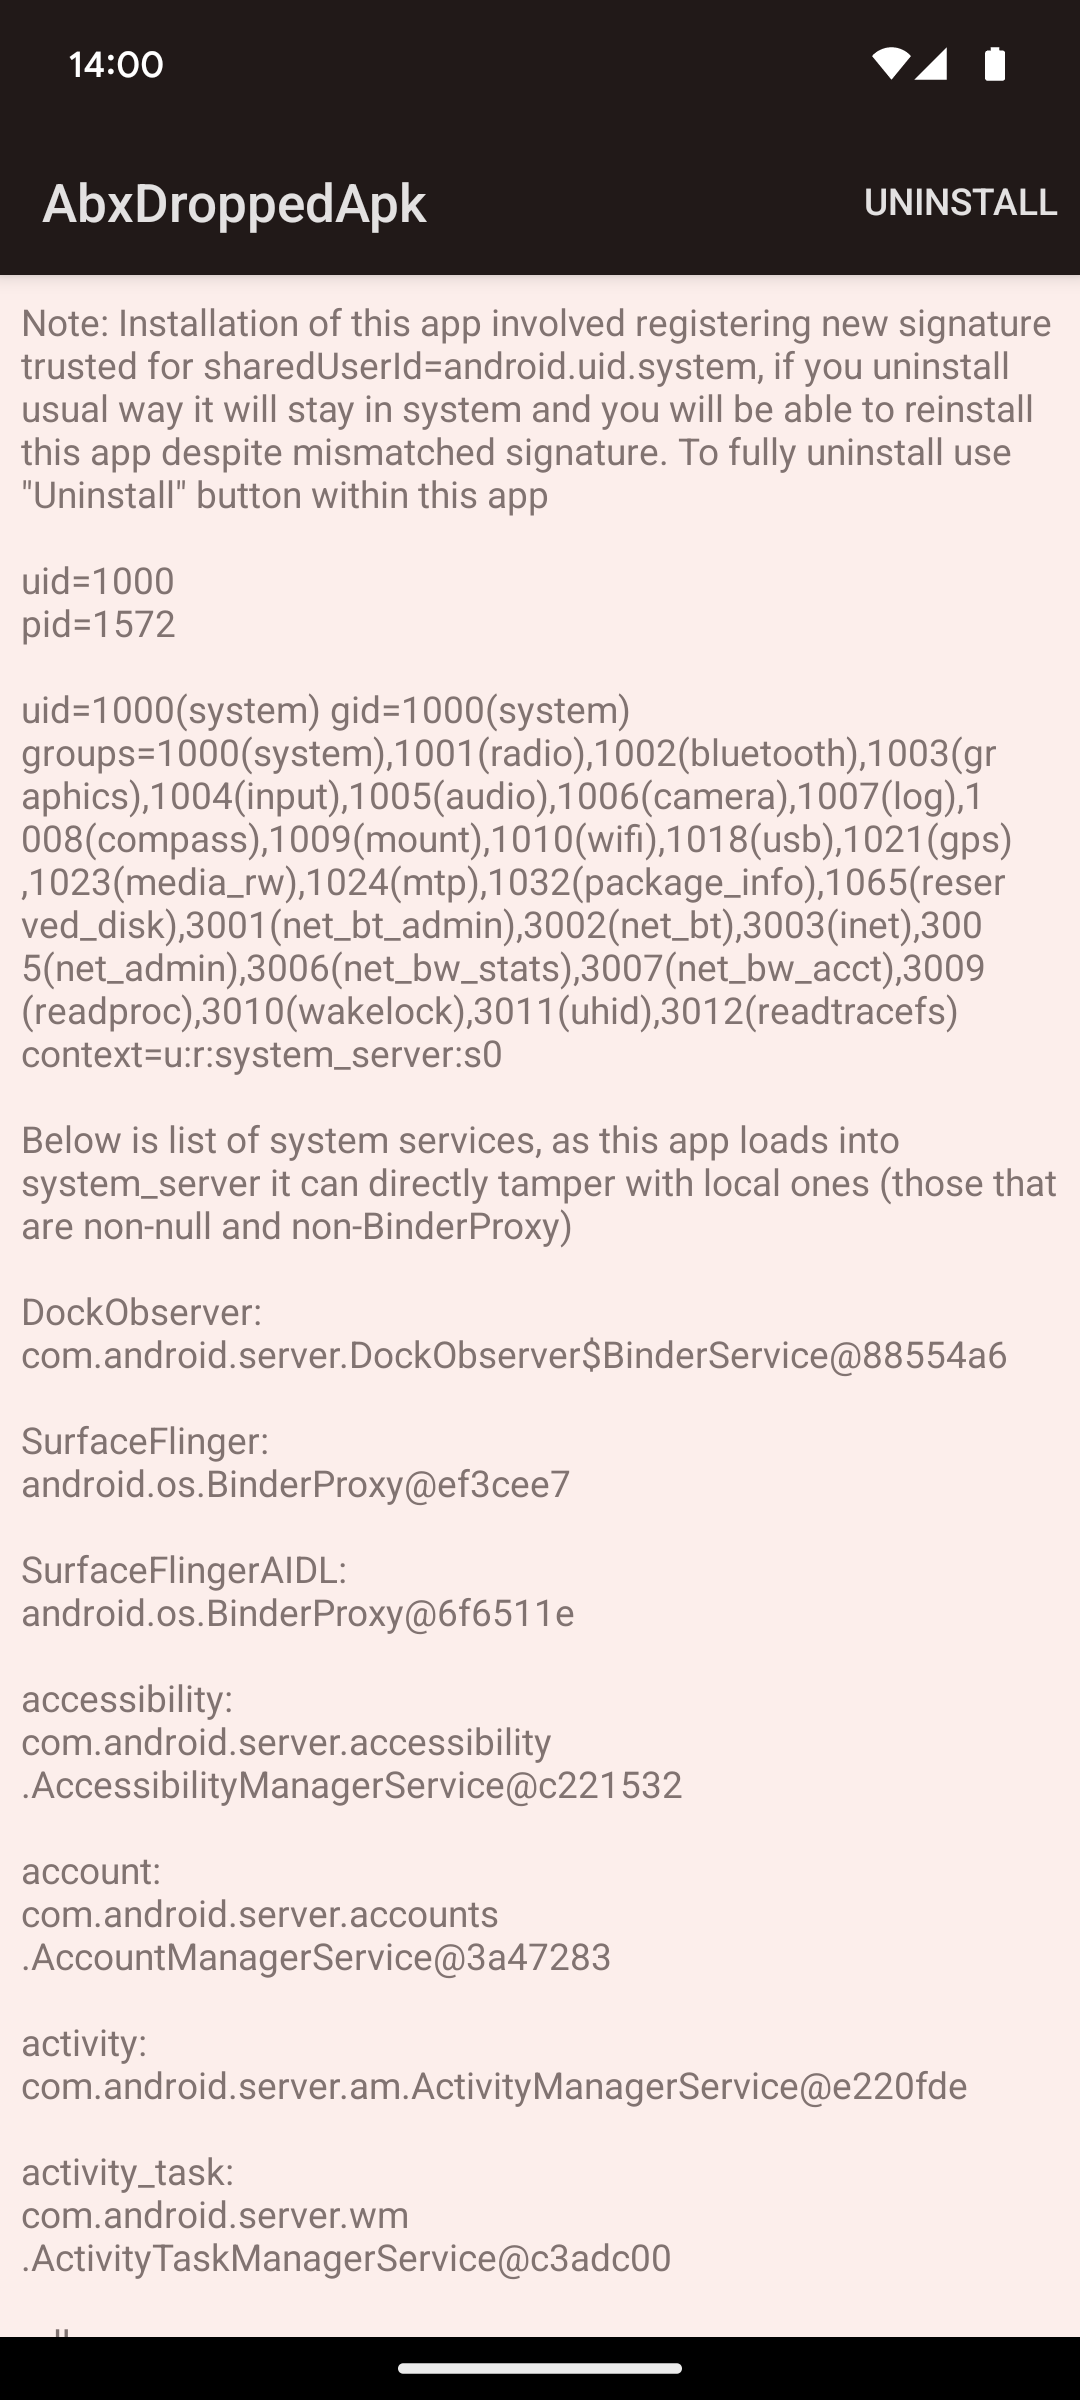 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 rifting/zygotroller
Remove Android profile owners/family link with CVE-2024-31317
 agg23/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 abbiy/cve-2024-36842-backdooring-oncord-android-sterio-
CVE-2024-36842, Creating Persistent Backdoor on Oncord+ android/ios car infotaiment using malicious script!
 absholi7ly/poc-for-cve-2024-7014-exploit
Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
 thebl4ckph4nt0m/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13. This repo demonstrates how to exploit…
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…