
Awesome-Hacking-Resources
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
ai-securityctfcurated-resources+9
17.5k
vitalysim/awesome-hacking-resourcesA collection of hacking / penetration testing resources to make you better!
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
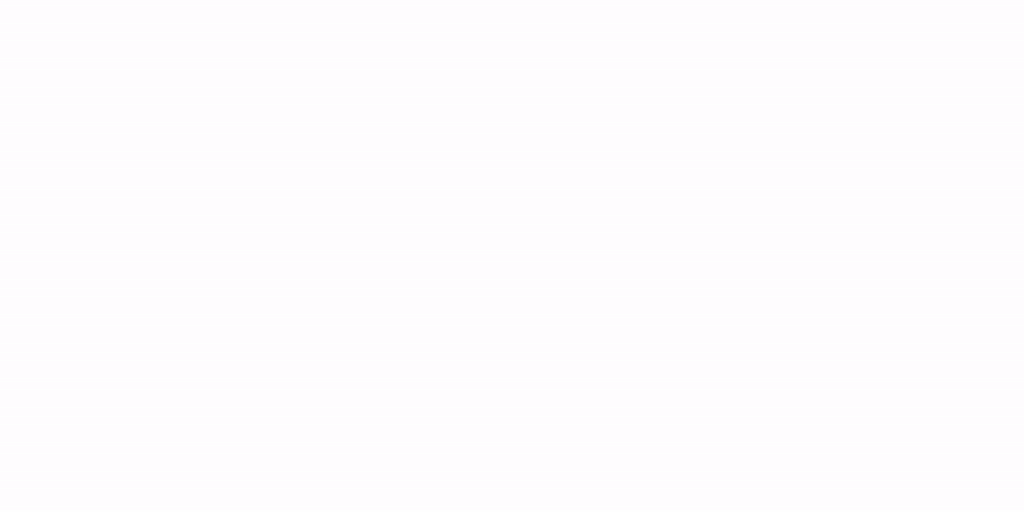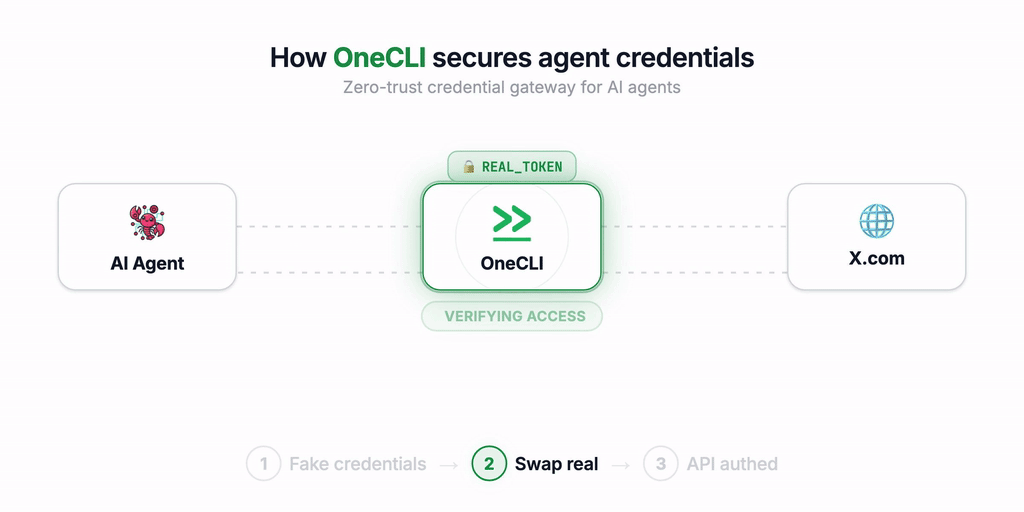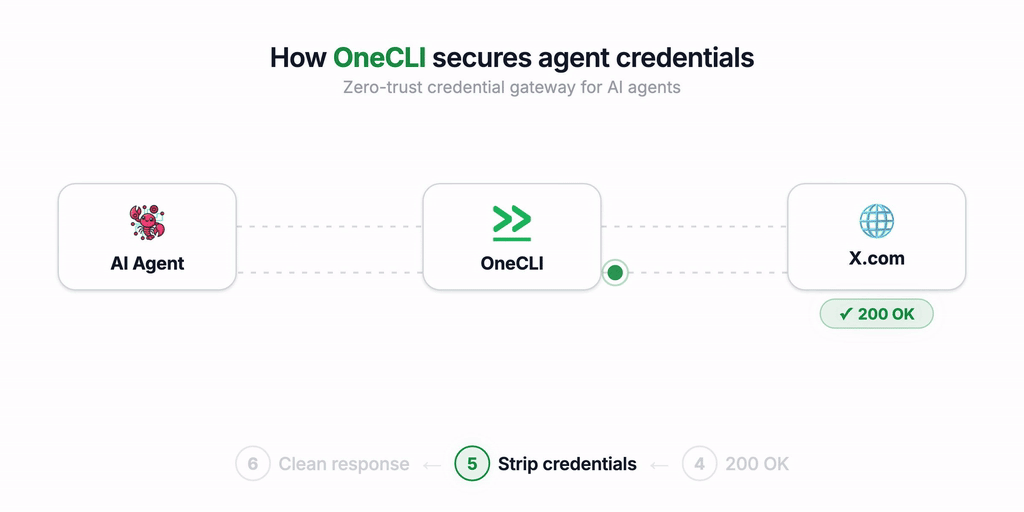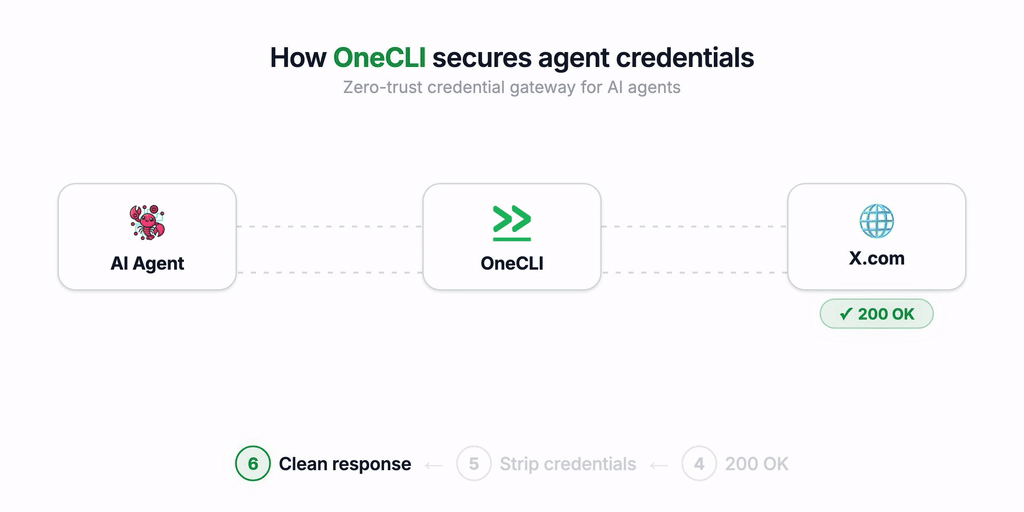 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 tmylla/awesome-llm4cybersecurity
Curated systematic literature review of 756+ papers on LLM applications in cybersecurity, covering threat intelligence, vulnerability detection,…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
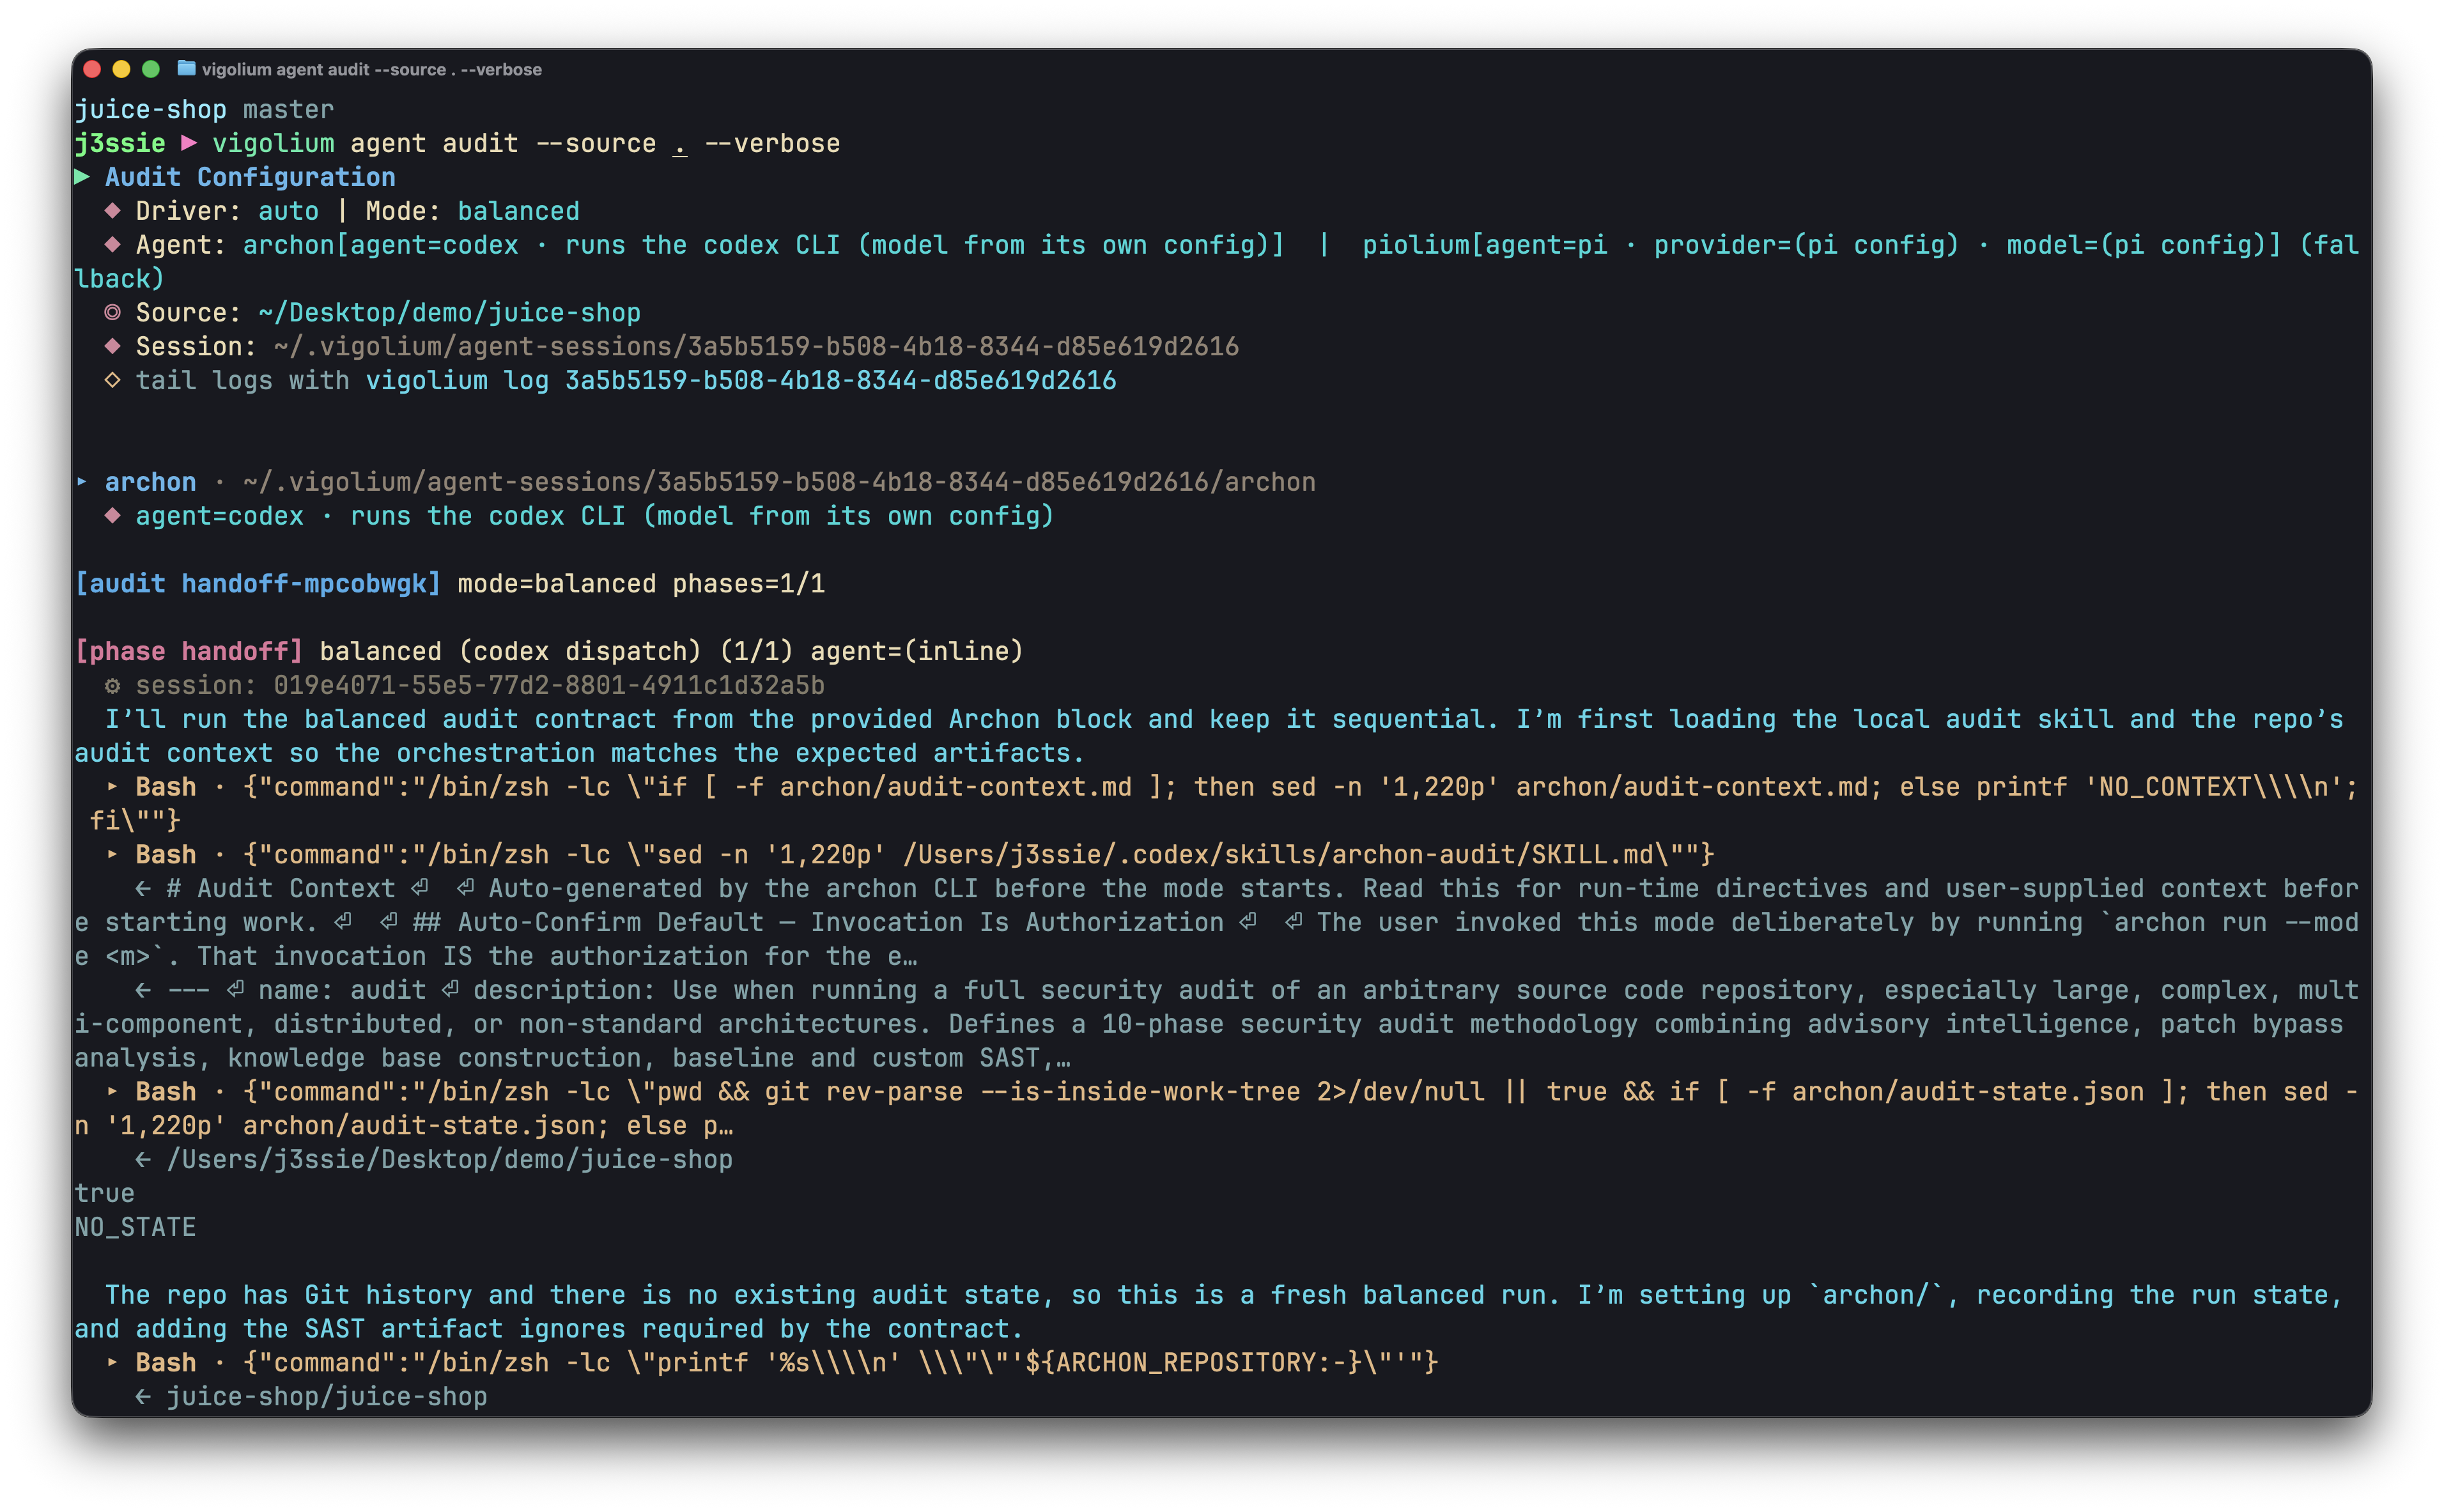 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
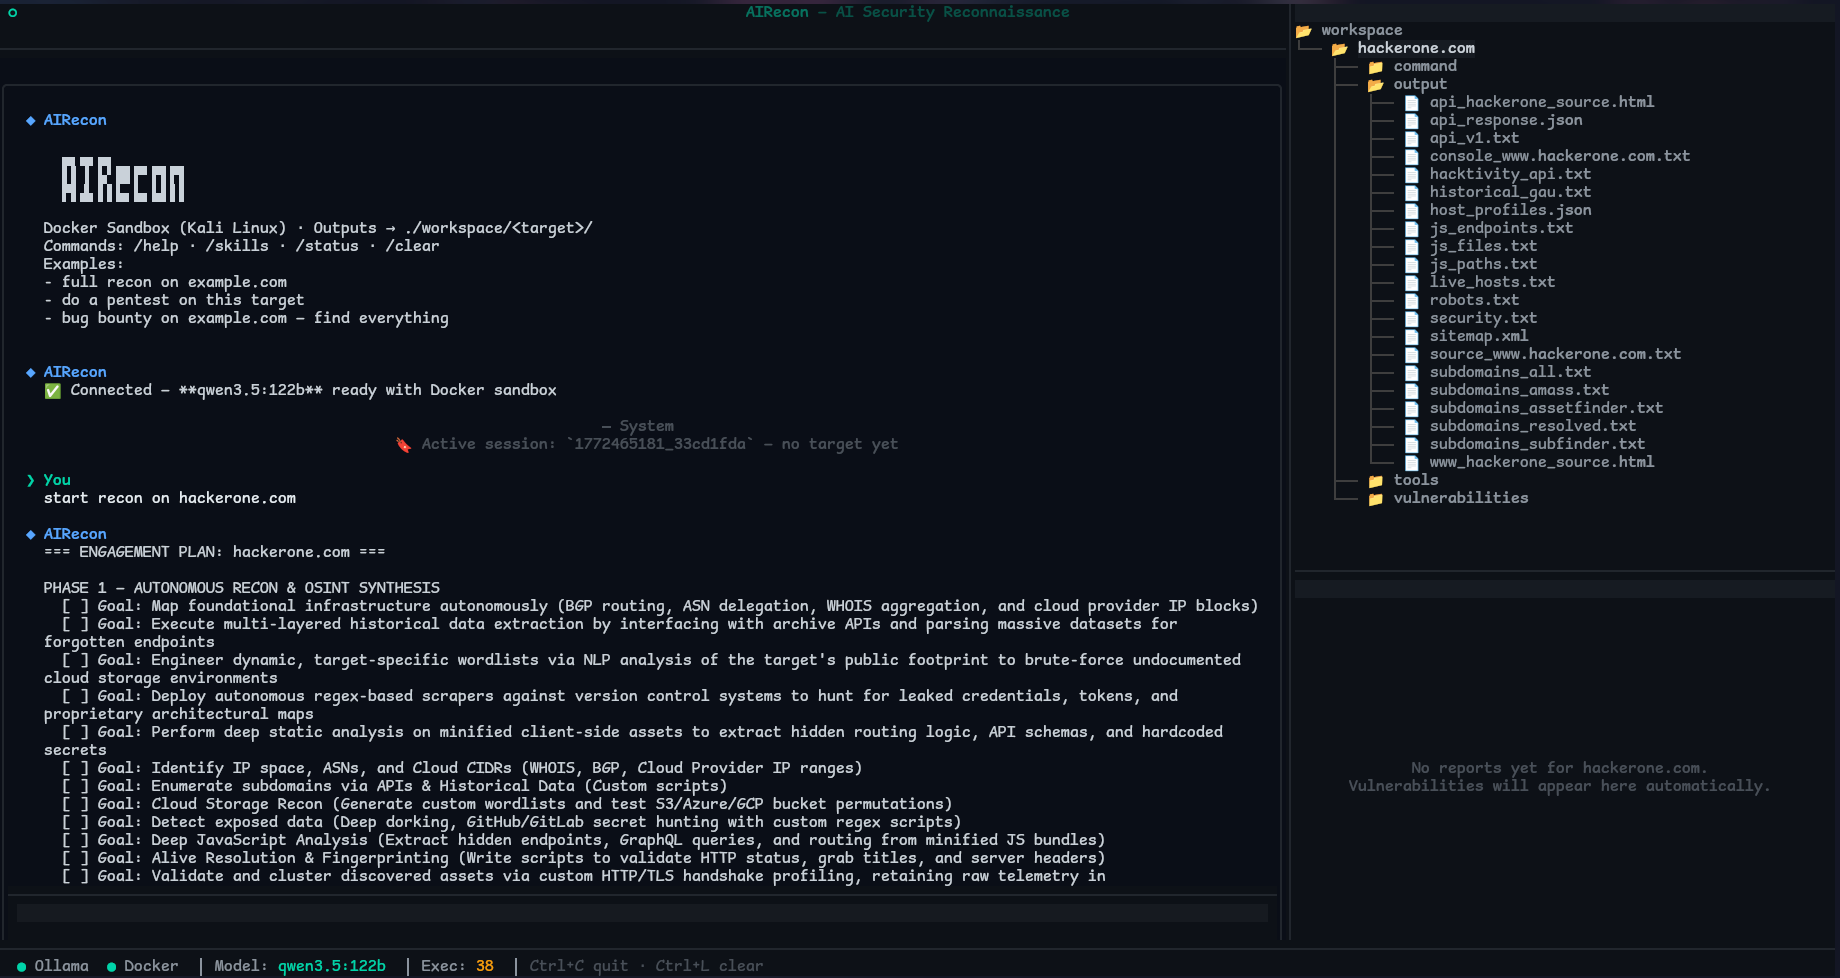 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.