Awesome-LLMs-for-Vulnerability-Detection

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

Technical webinars on reverse engineering, malware analysis, and software protection.

Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…

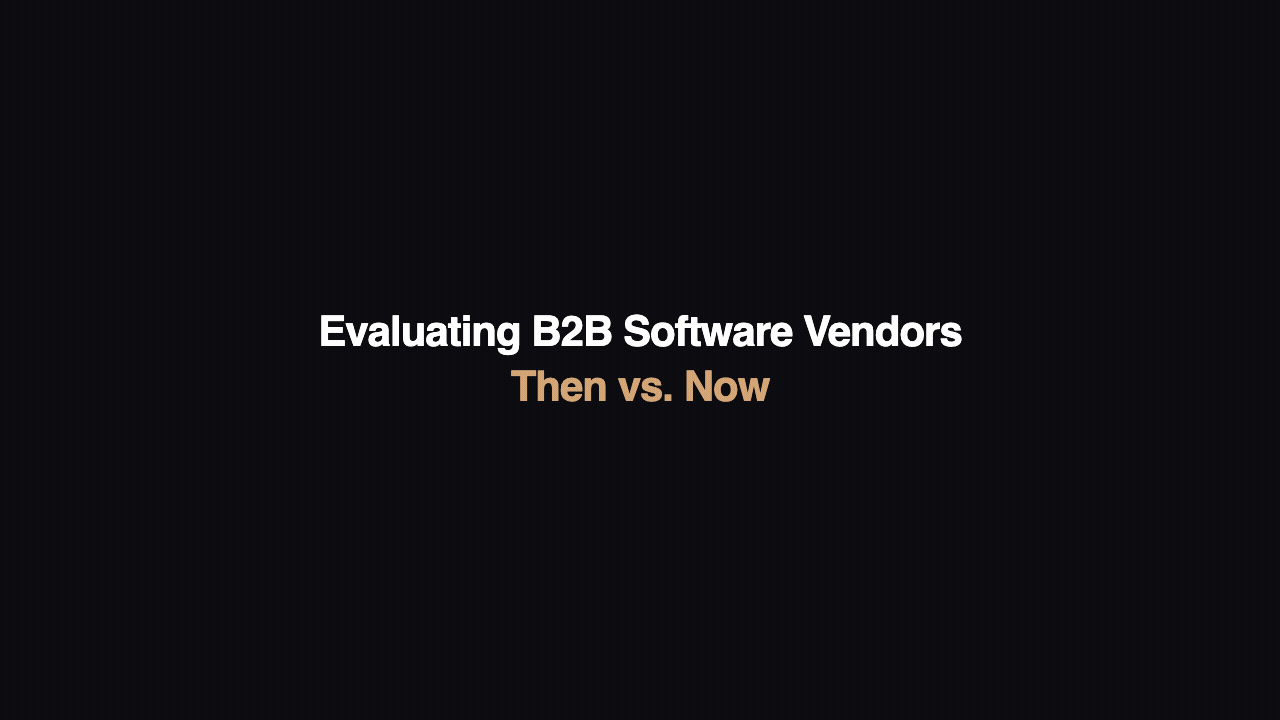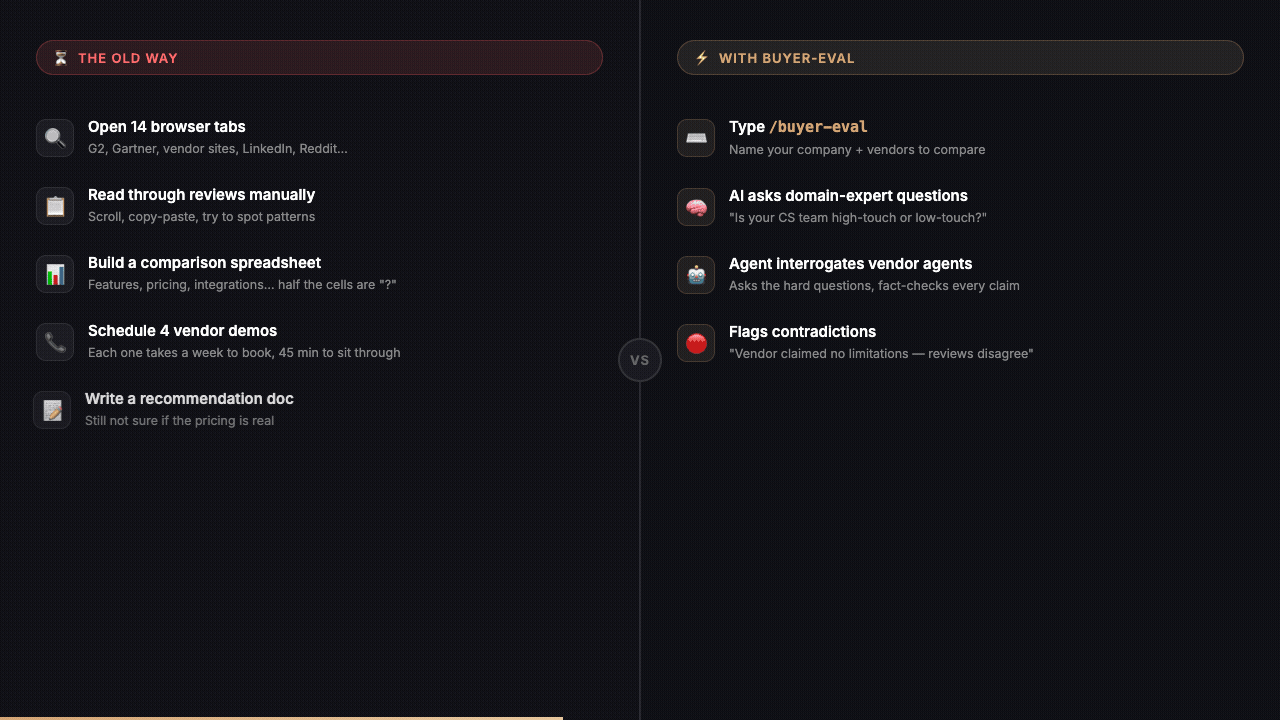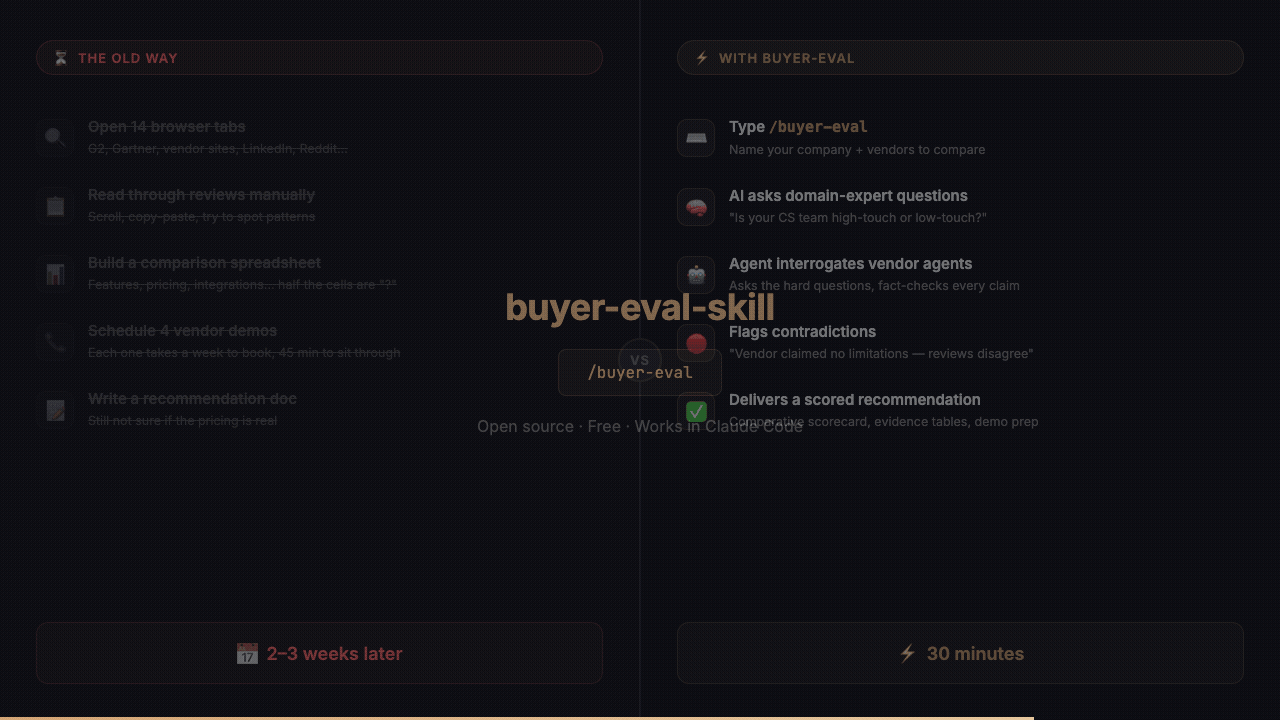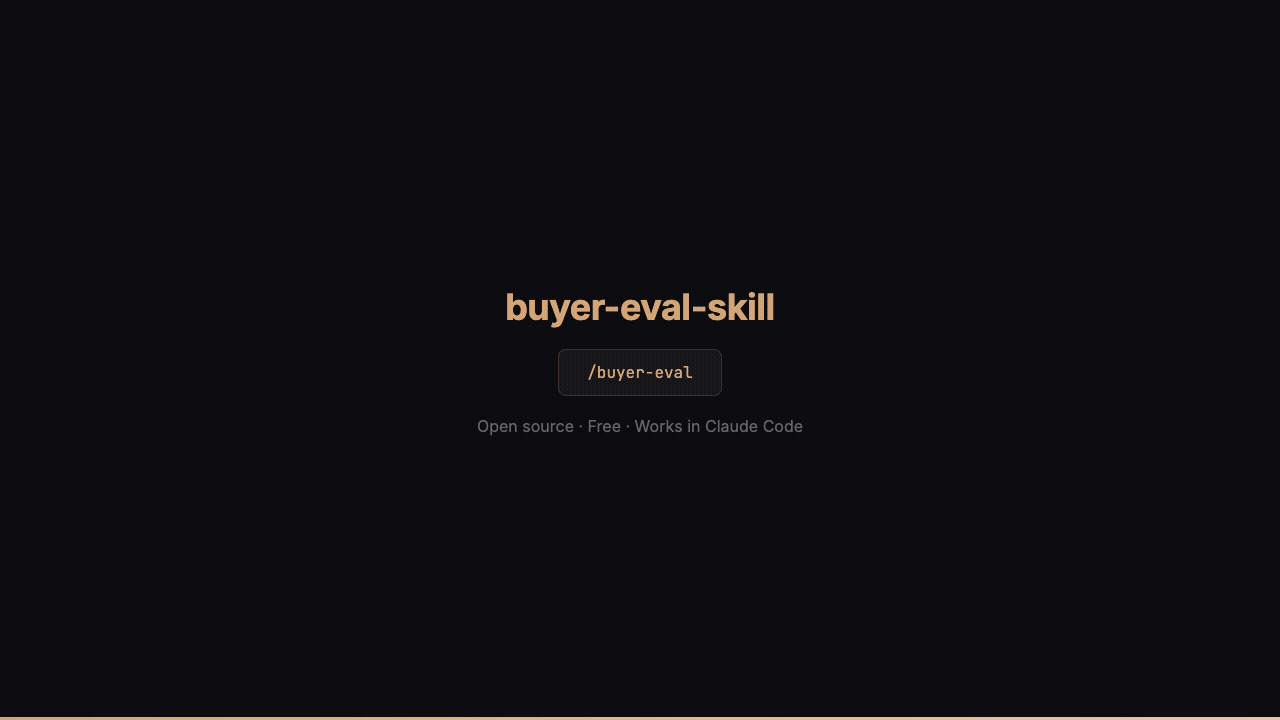
B2B software vendor evaluation skill for Claude Code — domain-expert questions, vendor AI agent conversations, evidence-based scoring

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…

Kernel-enforced authority and runtime security for Linux systems, autonomous software, and AI agents.

AI-driven endpoint governance platform that monitors software usage, applies deterministic policy-based risk classification, and generates structured…

Ensemble framework for software vulnerability detection and repair using multiple large language models, with consensus analysis and evaluation tools…

agent runtime security - zero trust, zero setup, zero latency agent sandboxing

The source files and tools needed to build the OWASP Cornucopia decks in various languages

Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…

Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…

Threat intelligence brief on CVE-2026-42208, a critical pre-auth SQL injection in BerriAI LiteLLM exploited within 36 hours of disclosure. Covers…

AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…

Zero-retraining sanitization that reorders permutation-equivalent neural network units to destroy malware embedded via weight-steganography attacks…

GitHub Action that scans ML model files for malicious code and security vulnerabilities

Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…