
openrisk
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
ai-securitypenetration-testingutilities-frameworks+2
180
projectdiscovery/openriskopenrisk is a tool that generates a risk score based on the results of a Nuclei scan.
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
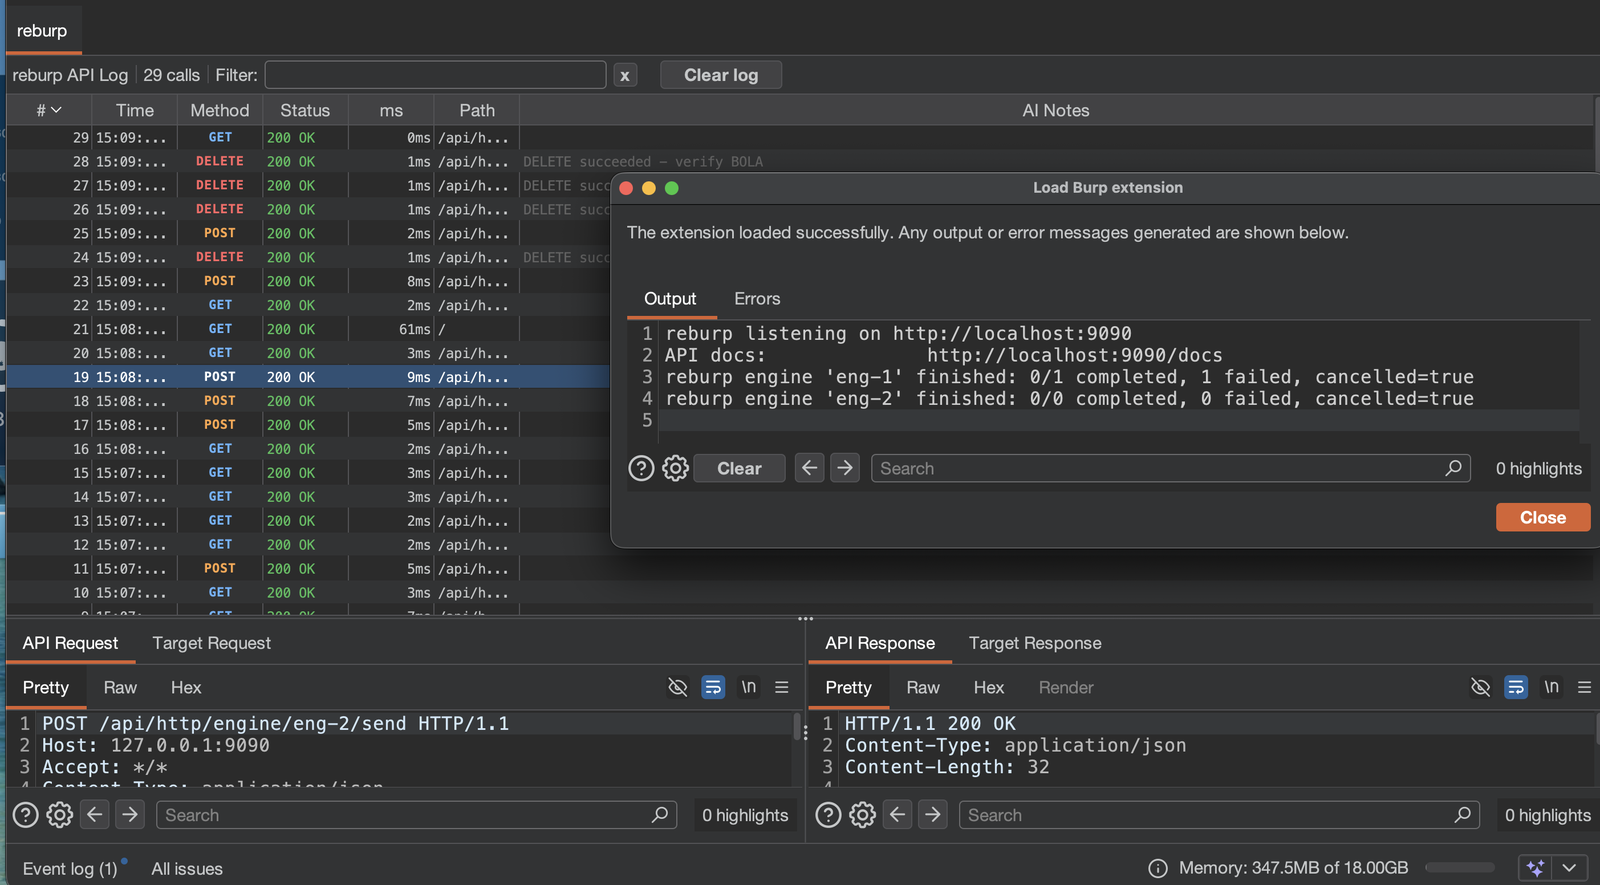 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
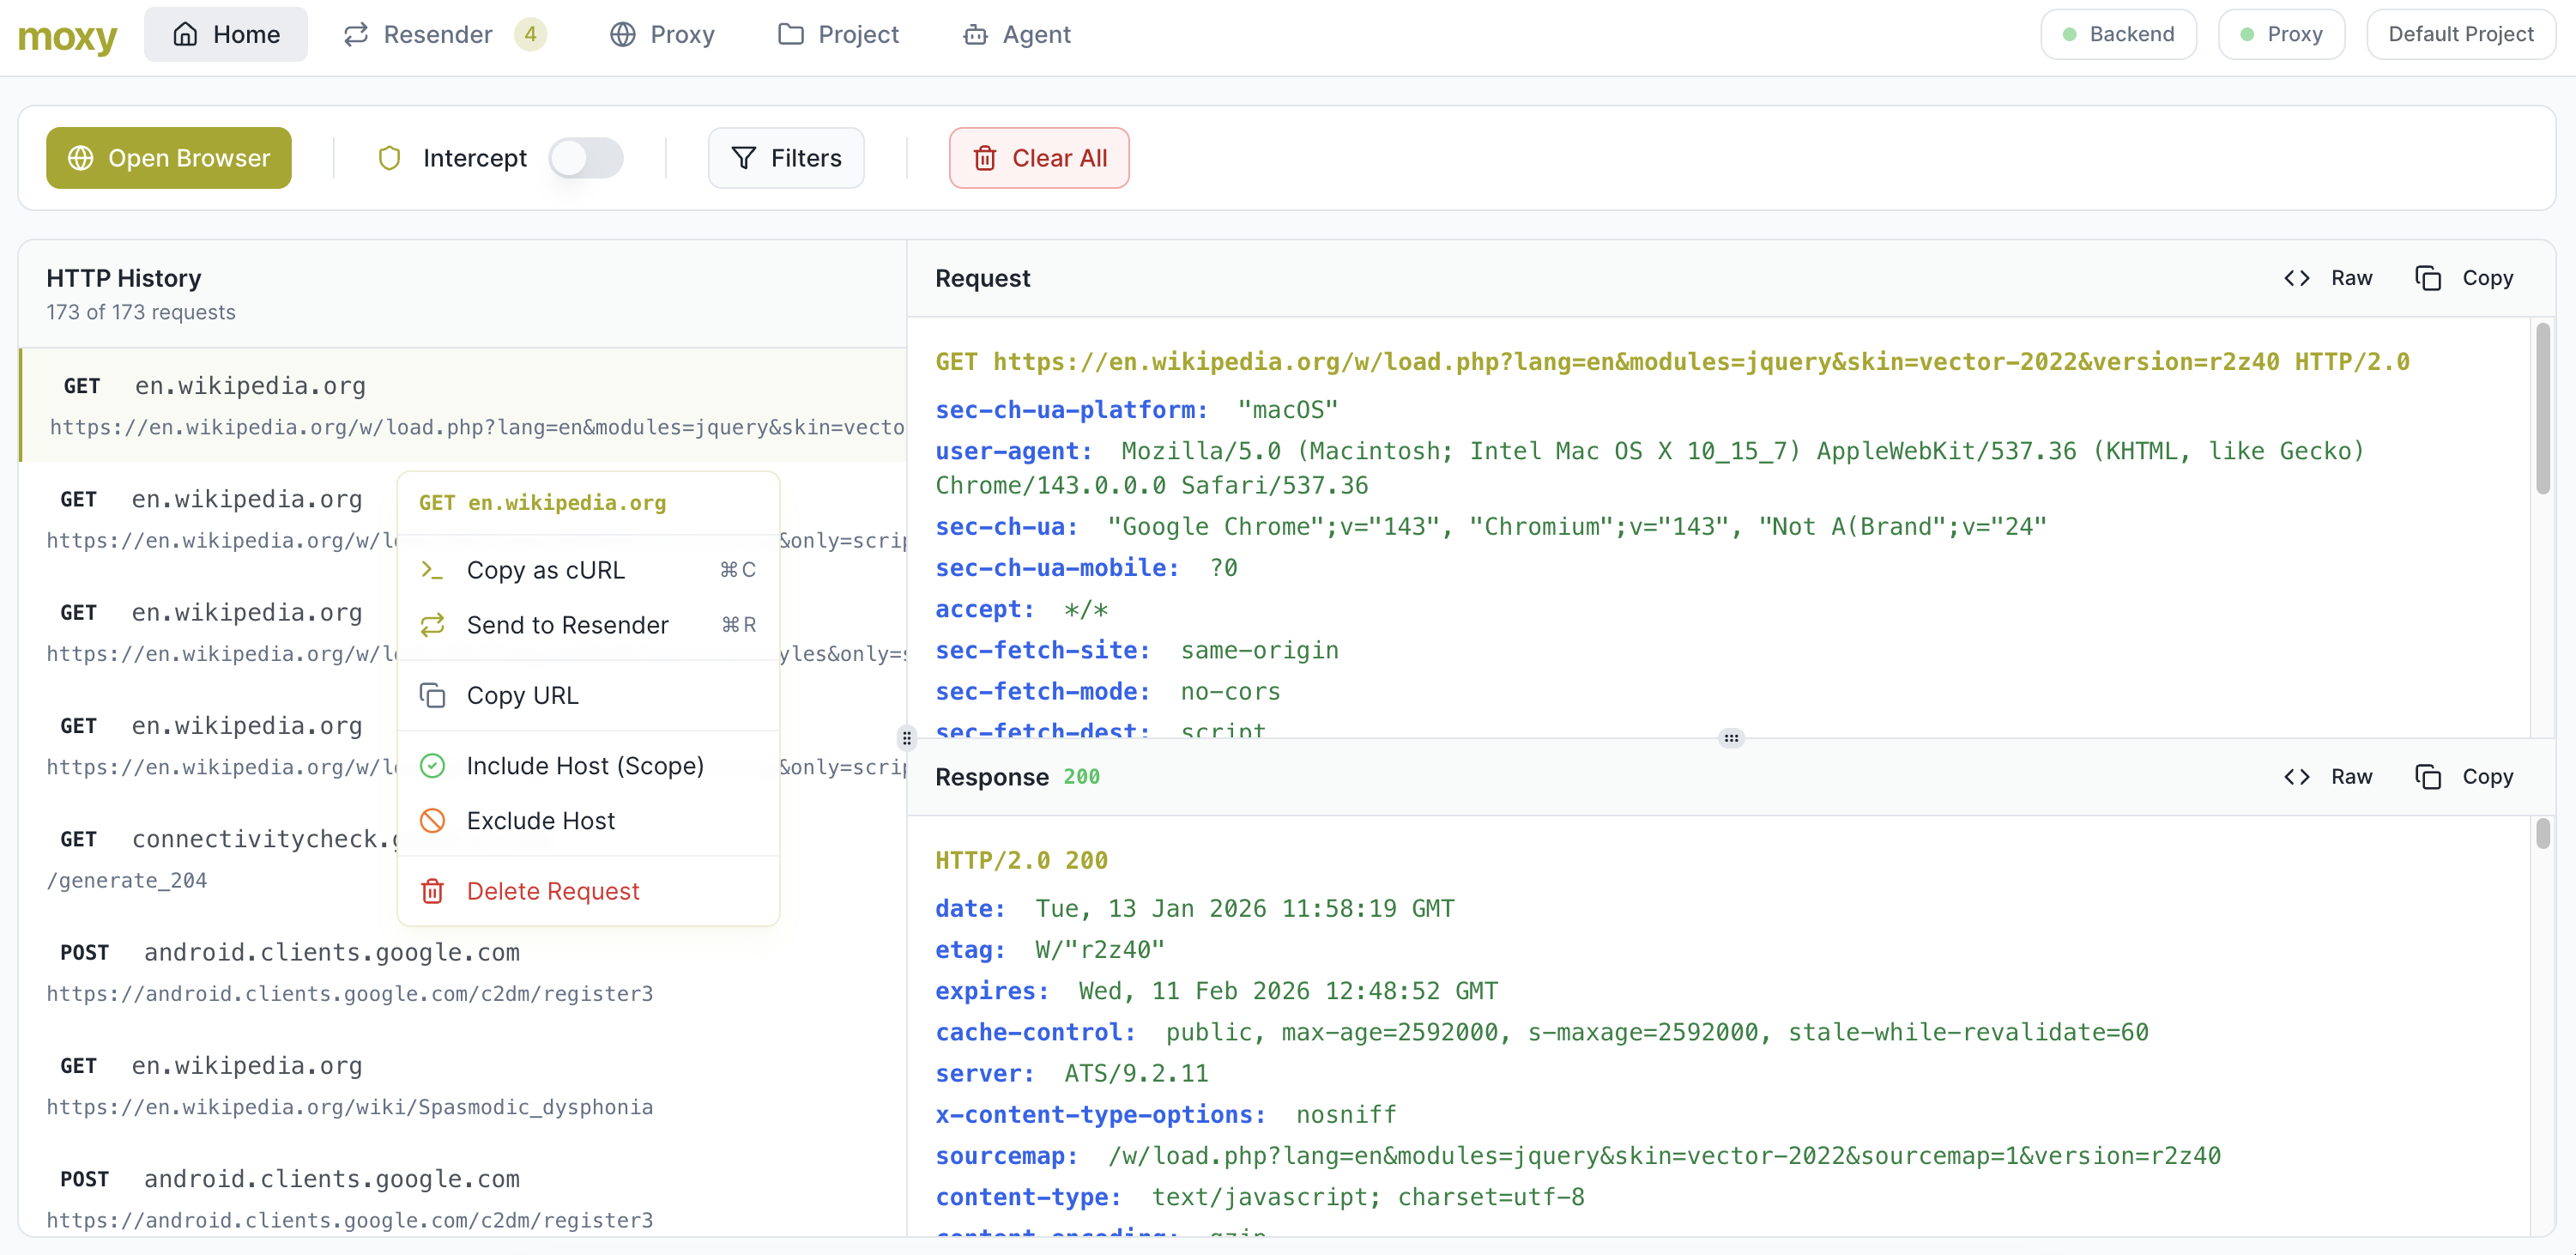 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 trailofbits/slither-mcp
MCP server for Slither static analysis of Solidity smart contracts
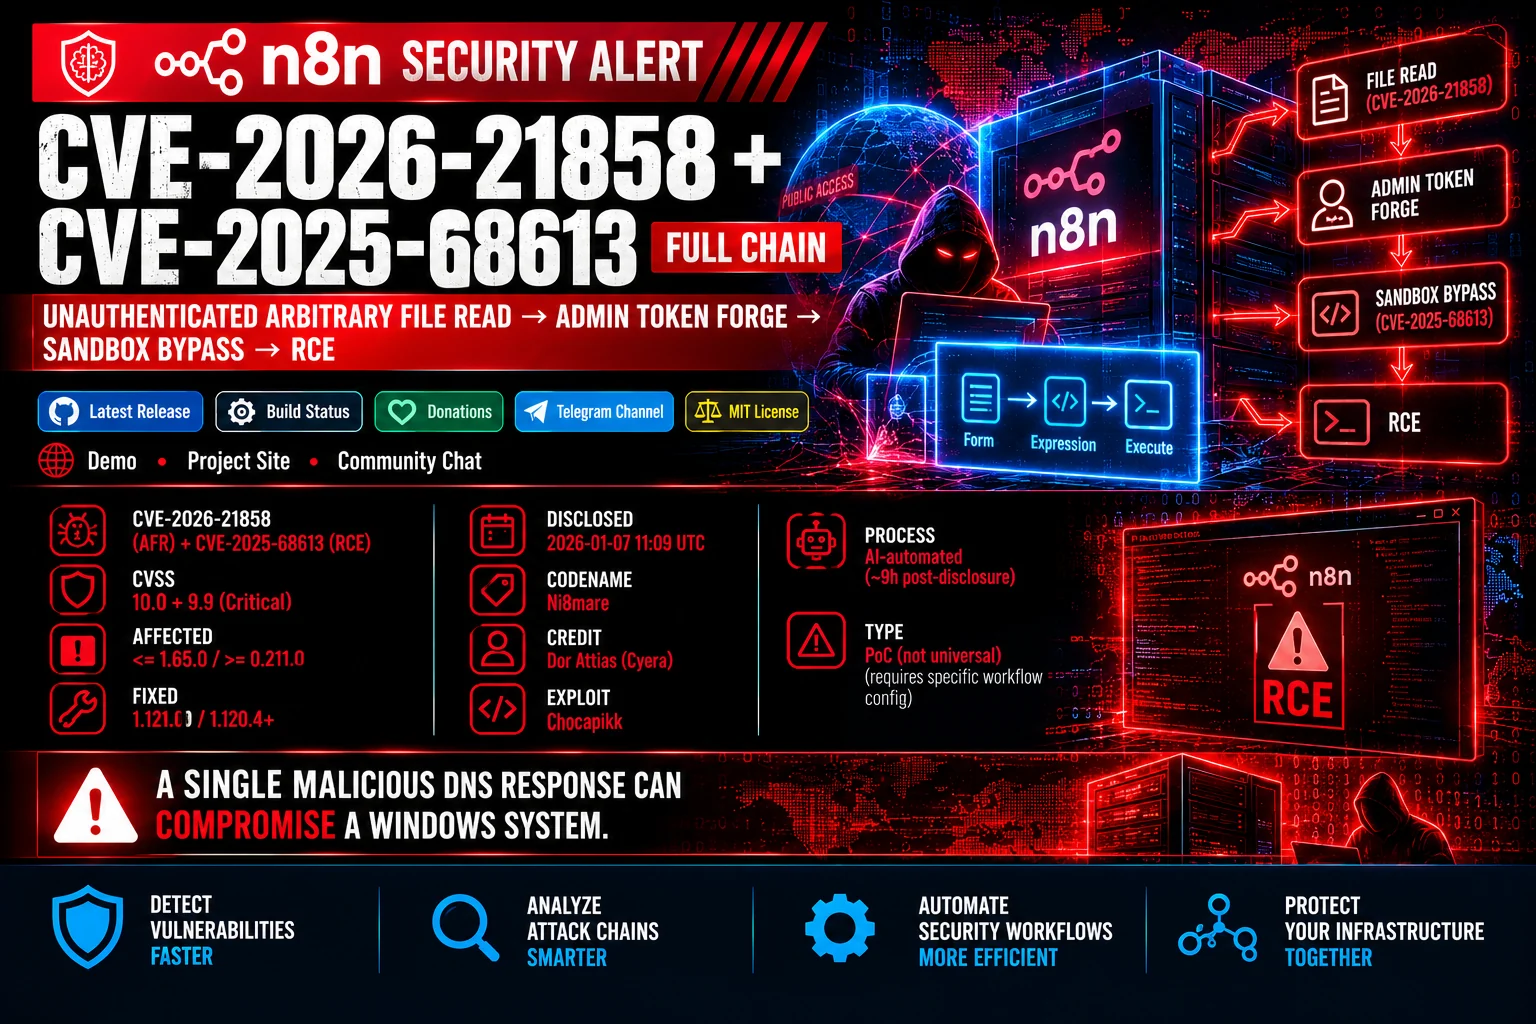 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
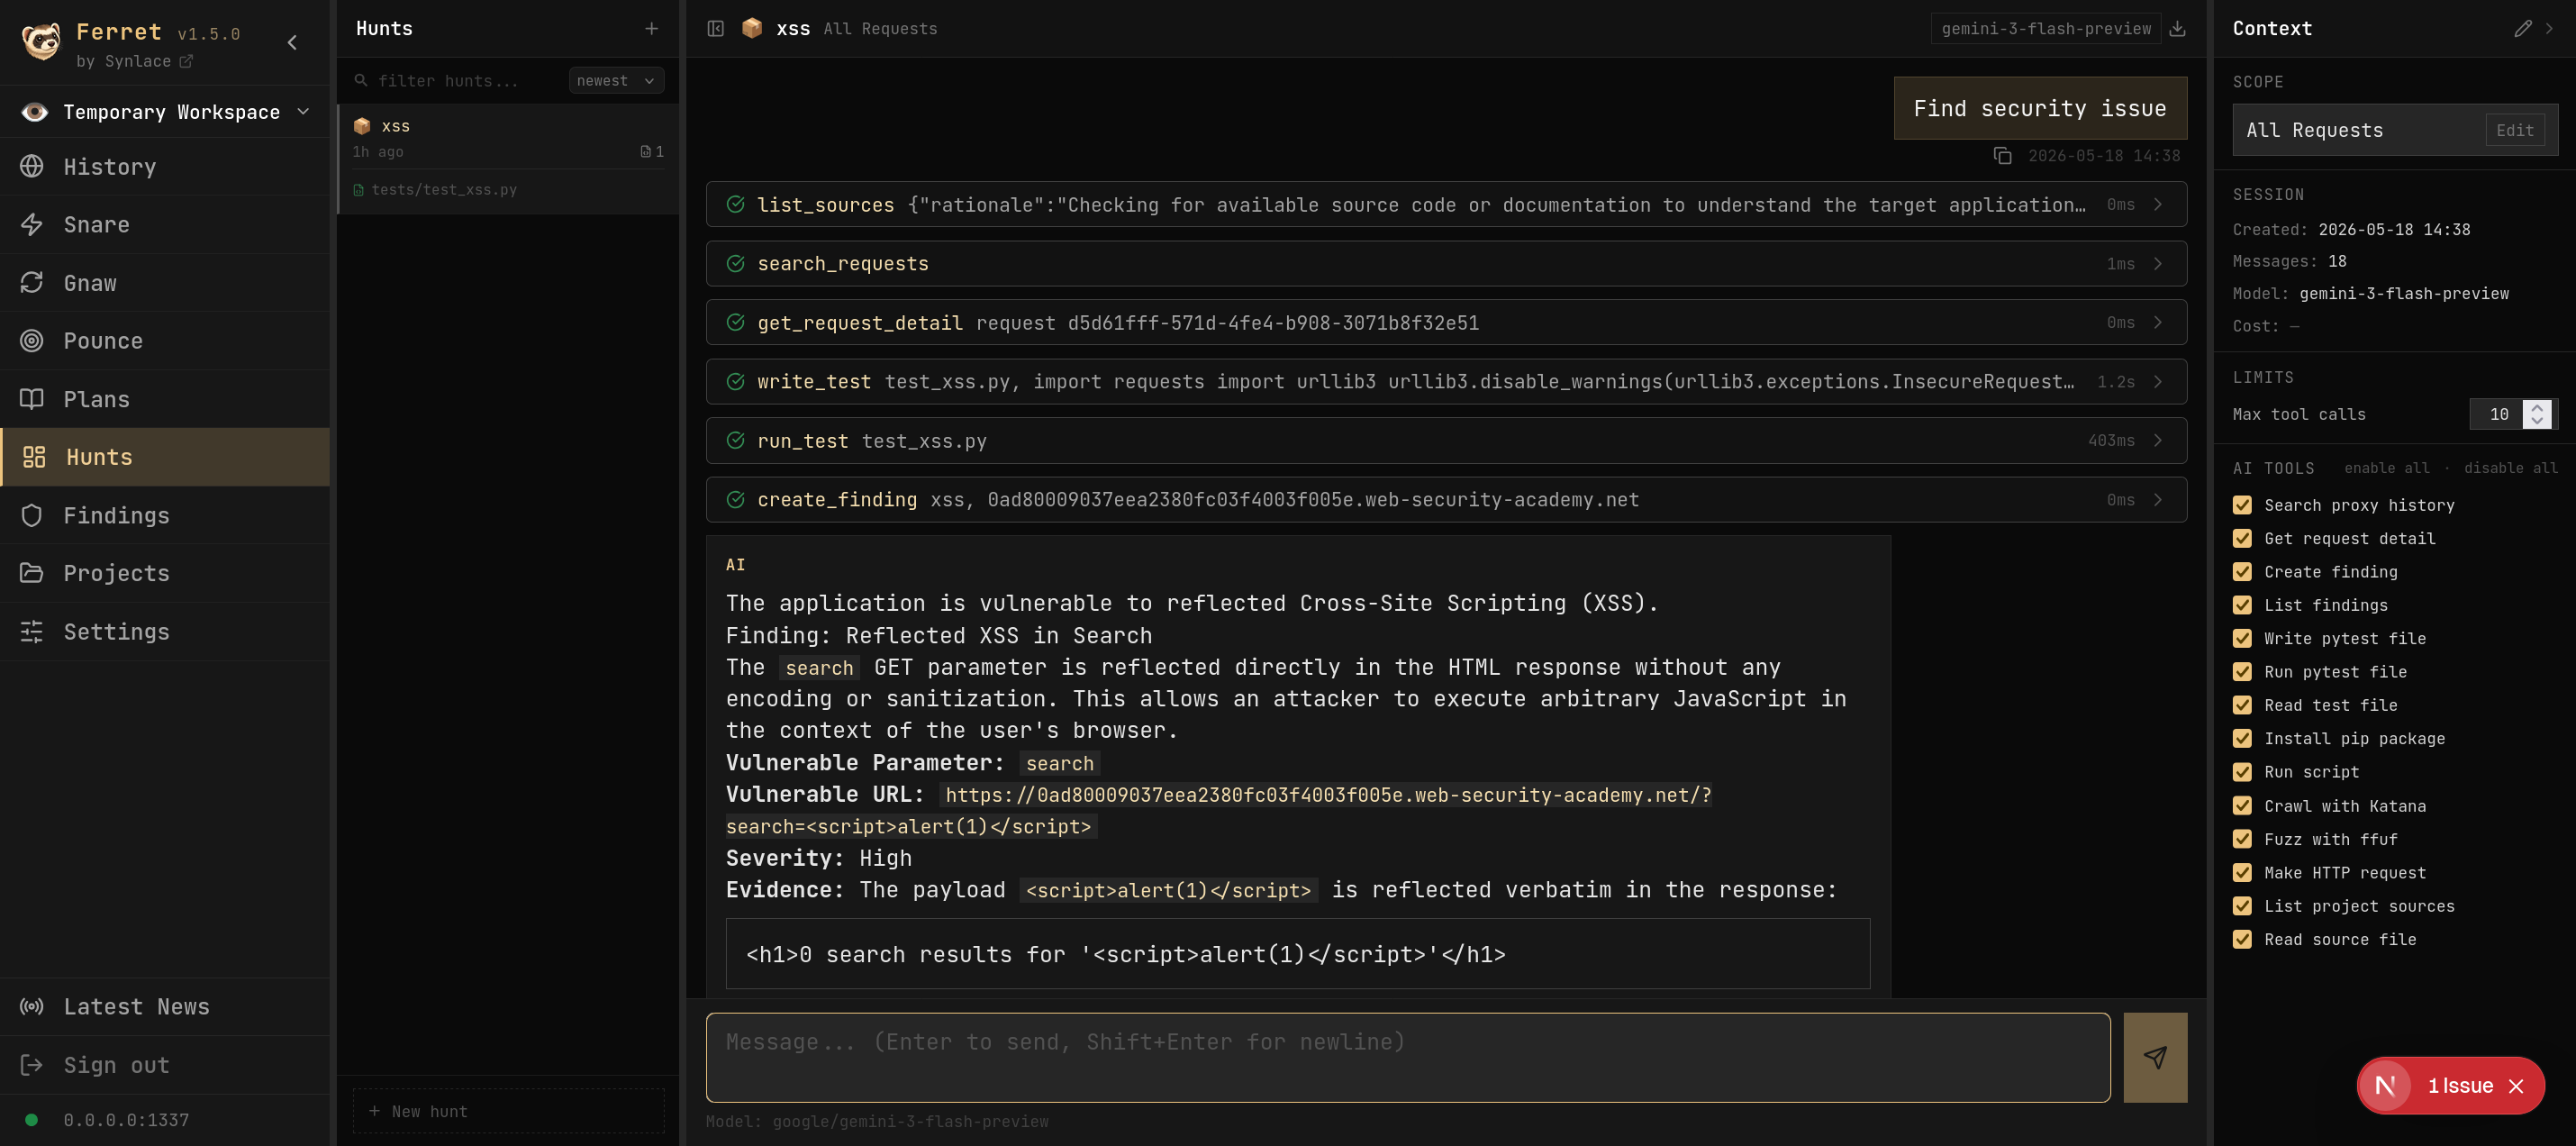 synlace/ferret
The collaborative web app pentest suite
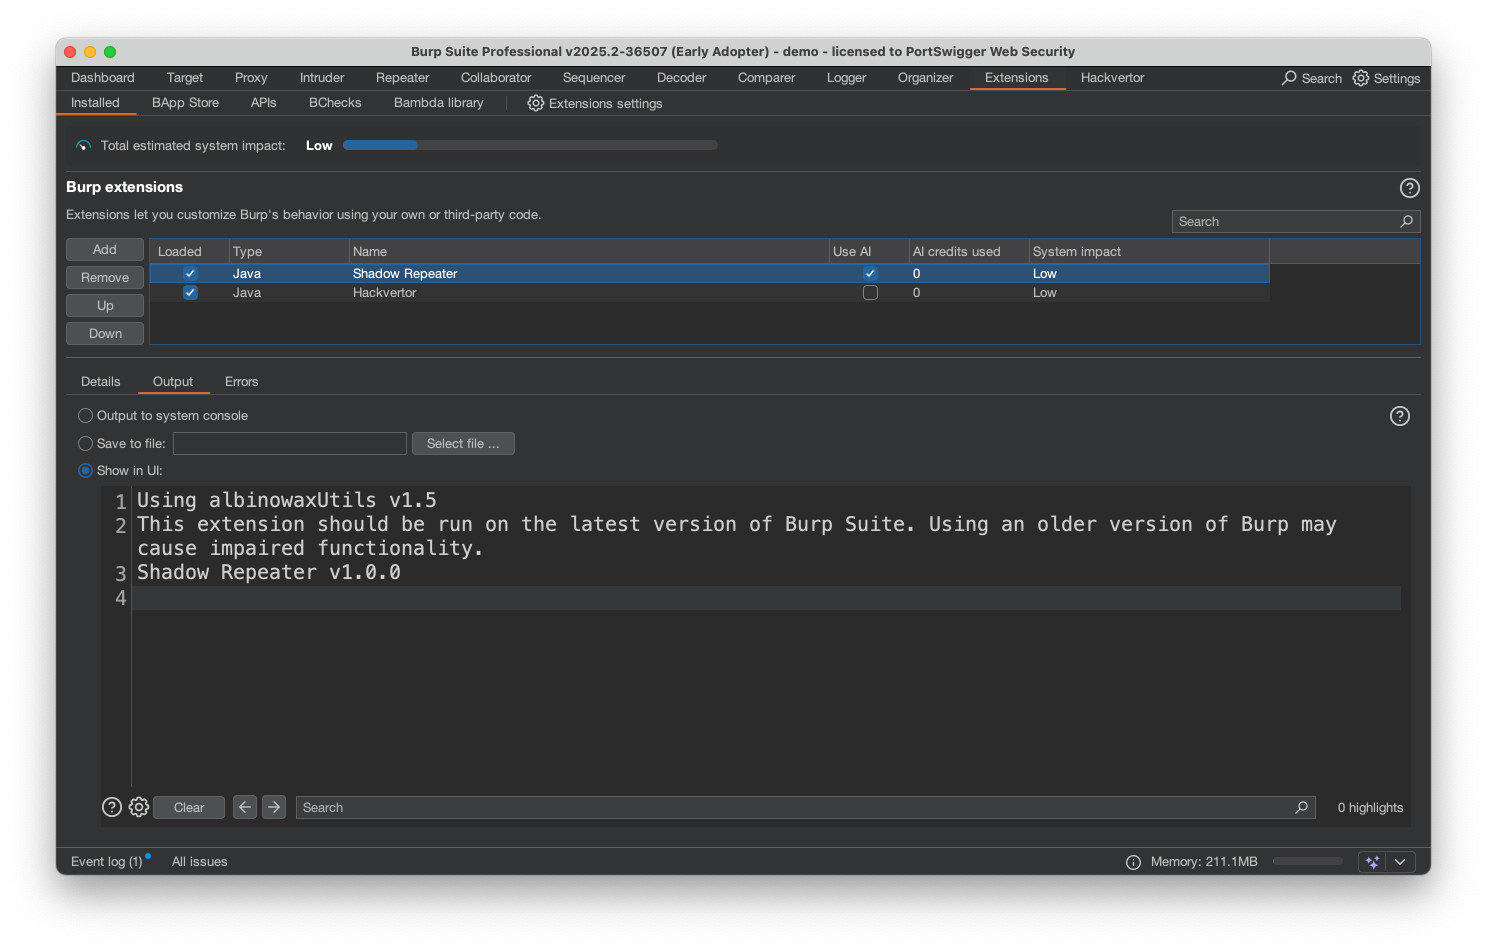 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
 infobyte/ai-pentest-agent
Standalone autonomous AI pentest agent with a plan→act→judge loop, generic skills, destructive-action gate, and swappable LLM providers, plus a…
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…