
openrisk
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
ai-securitypenetration-testingutilities-frameworks+2
projectdiscovery/openriskopenrisk is a tool that generates a risk score based on the results of a Nuclei scan.
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 berylliumsec/nebula
AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 kush-coder/autopilot-pentest-ai
Official Build & Verified Release | Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a…
 0sec-labs/0
The open-source AI security harness. Includes a web interface for code analysis, pentesting, vulnerability research, reverse engineering,…
 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 reconmap/reconmap
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…
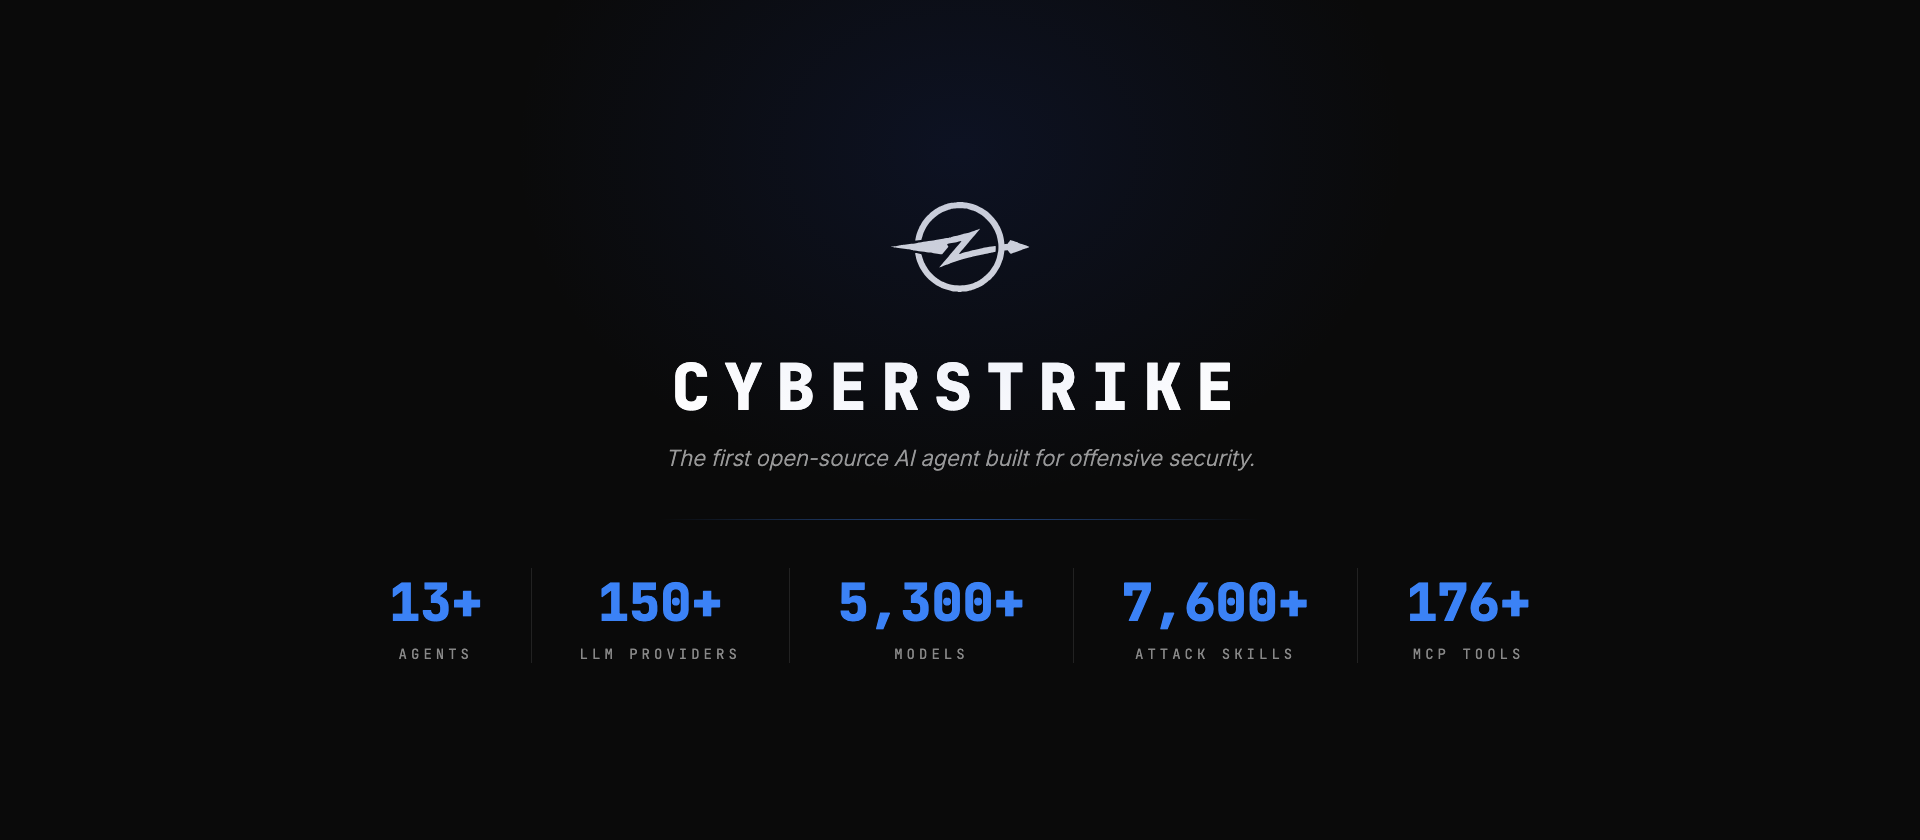 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
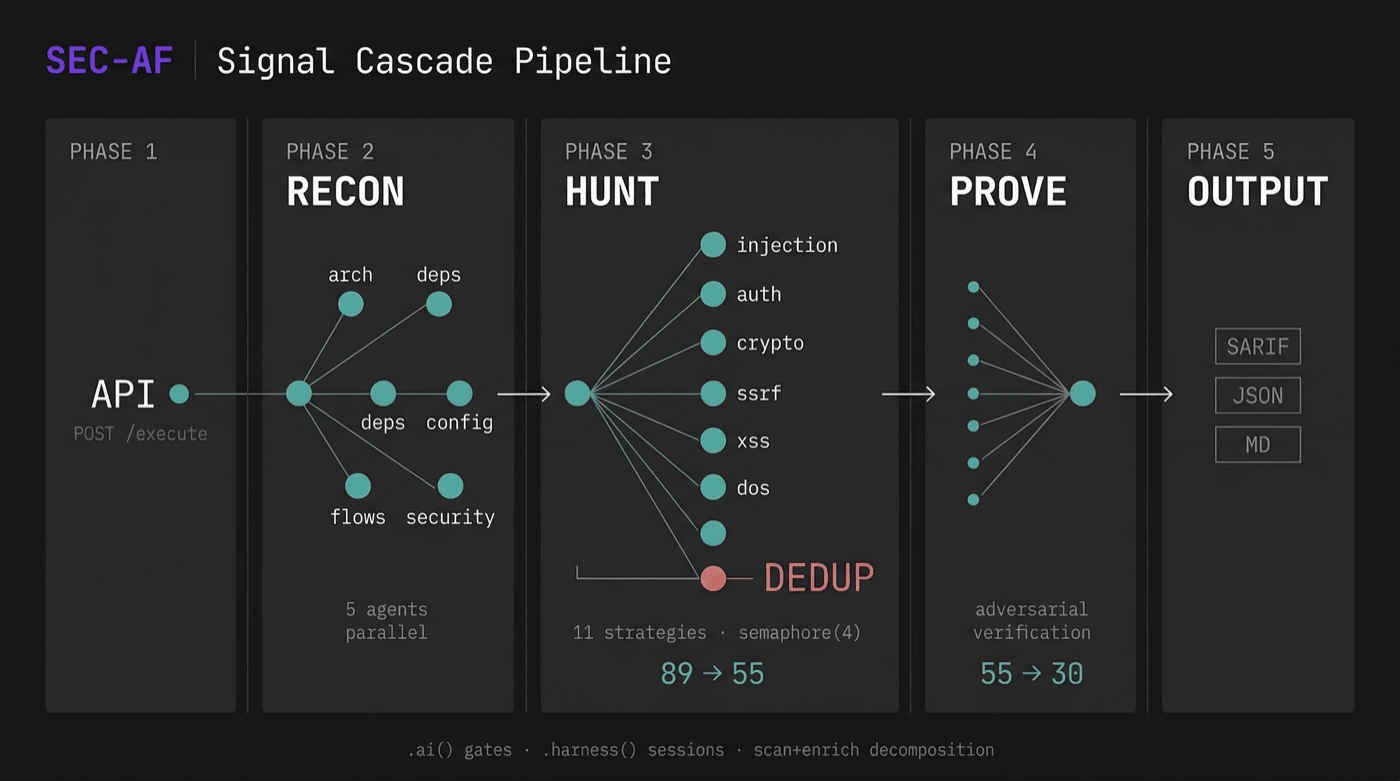 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
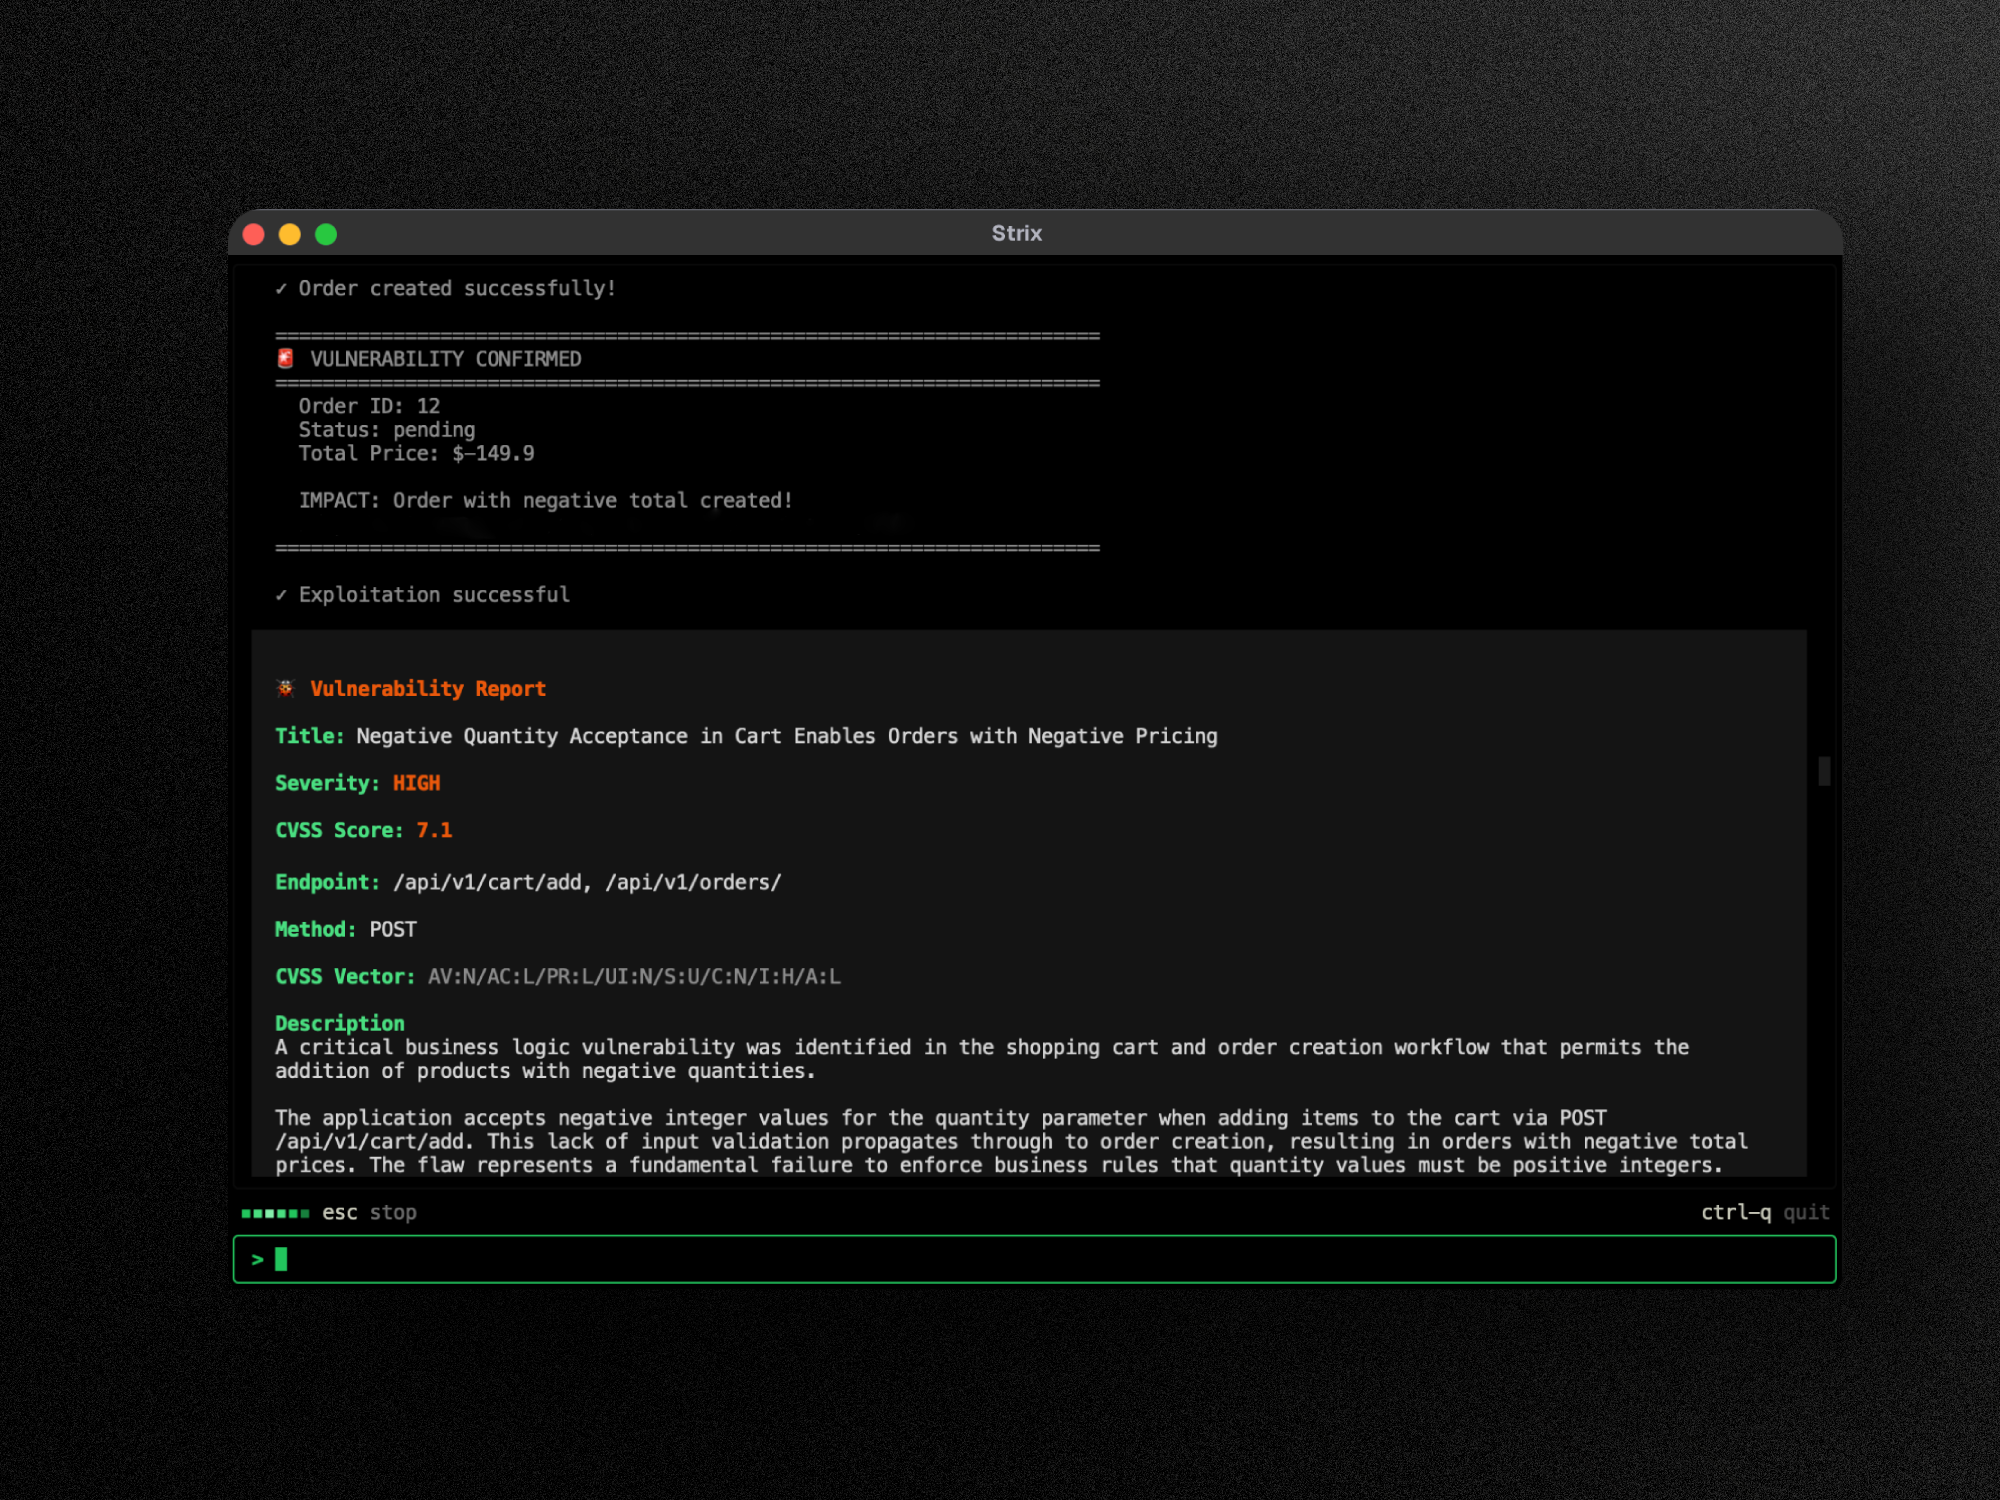 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
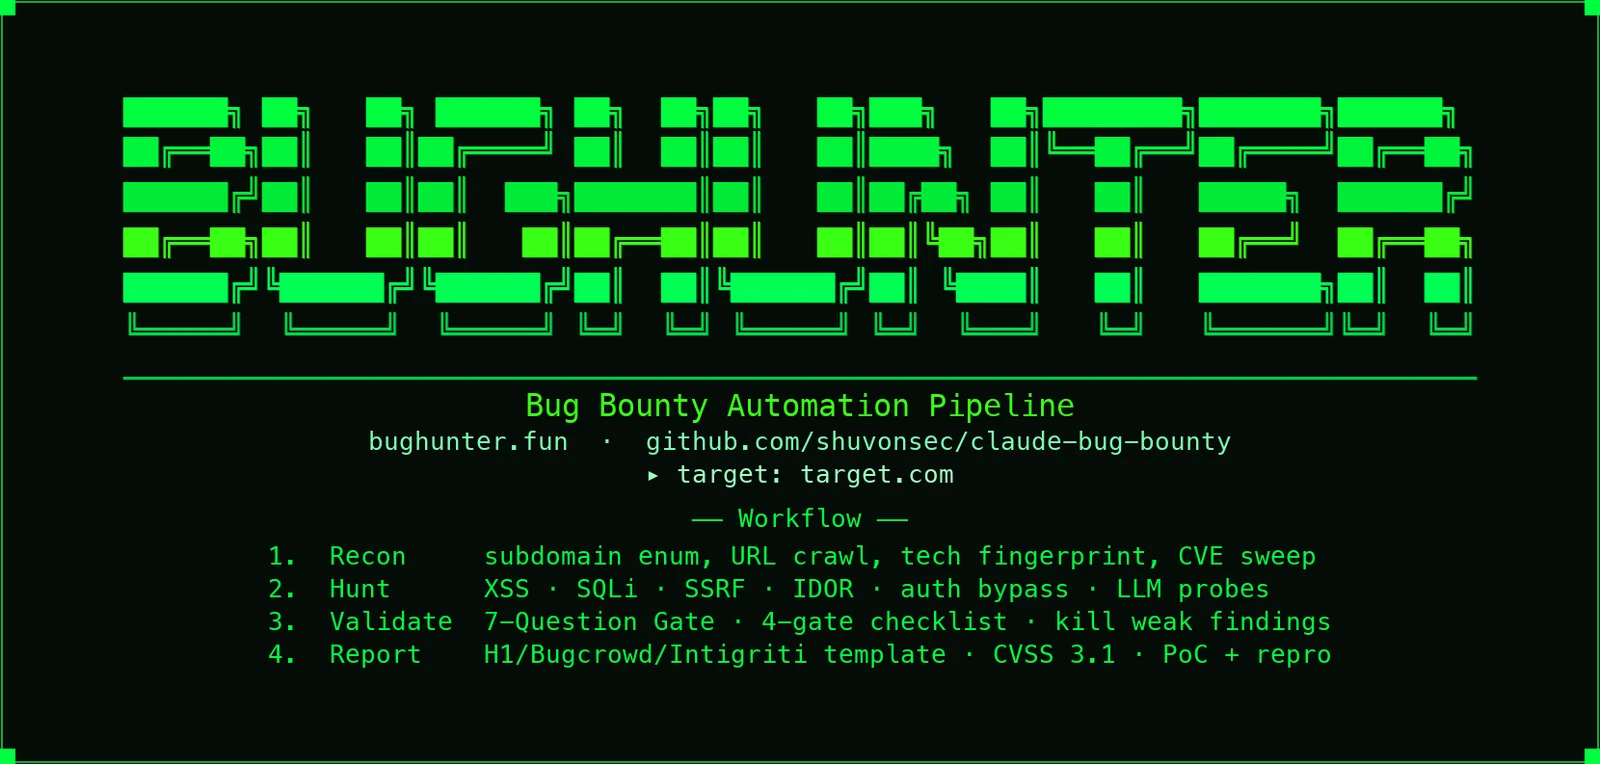 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.