

cve-intel
 fazmin/cve-intel
Local security intelligence for CVE triage — 31 tools, 25 sources, risk scores and an MCP server for AI agents, all in native Rust. Private by…
ai-securitydevsecopsincident-response+8
5
fazmin/cve-intelLocal security intelligence for CVE triage — 31 tools, 25 sources, risk scores and an MCP server for AI agents, all in native Rust. Private by…
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
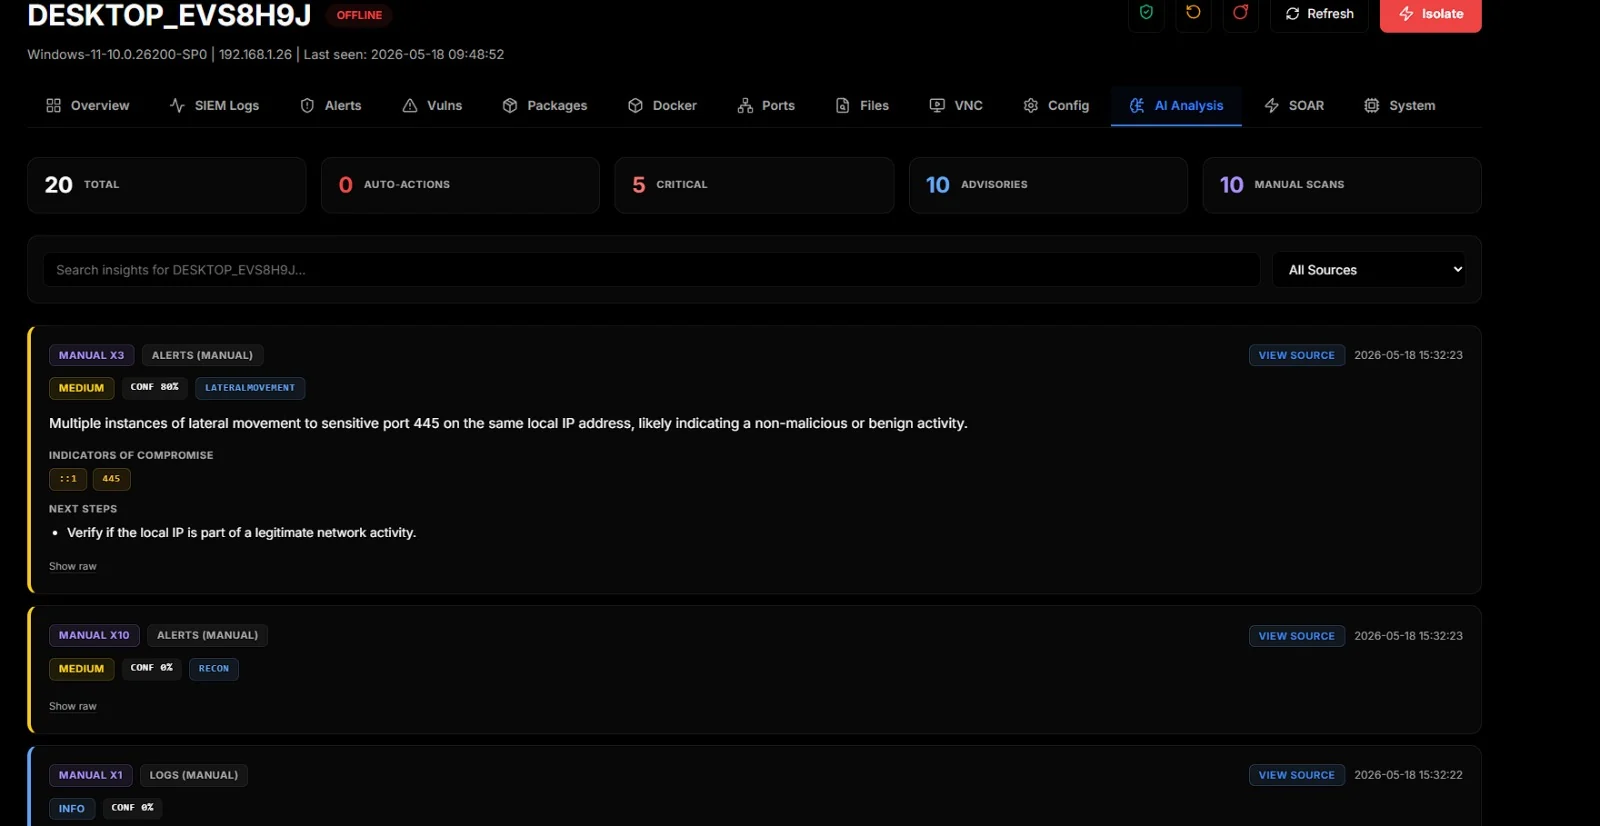 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 ololadeabiola03/aisecplus-week01-servicenow-ai-security-incident
Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
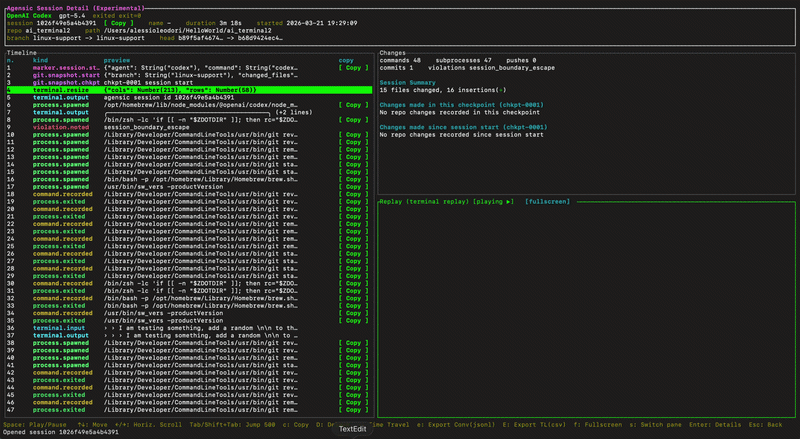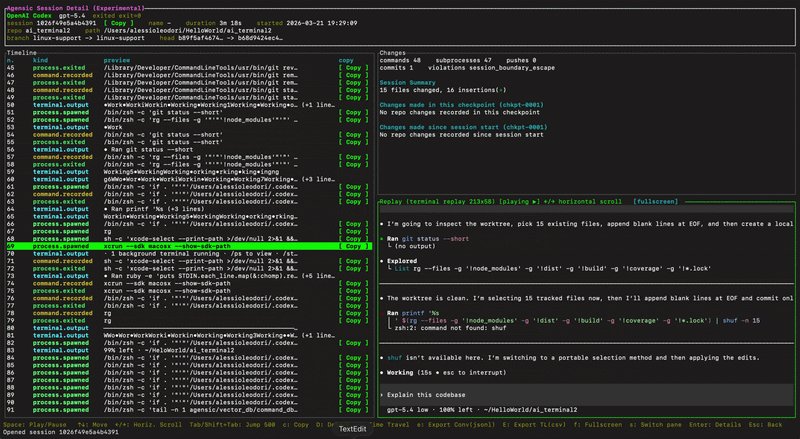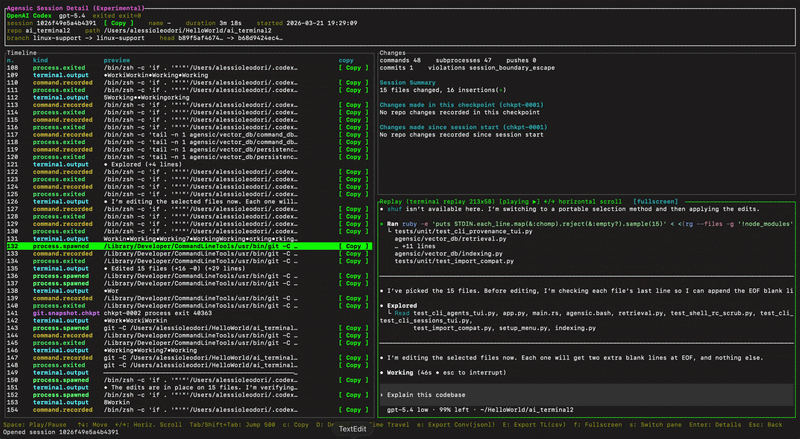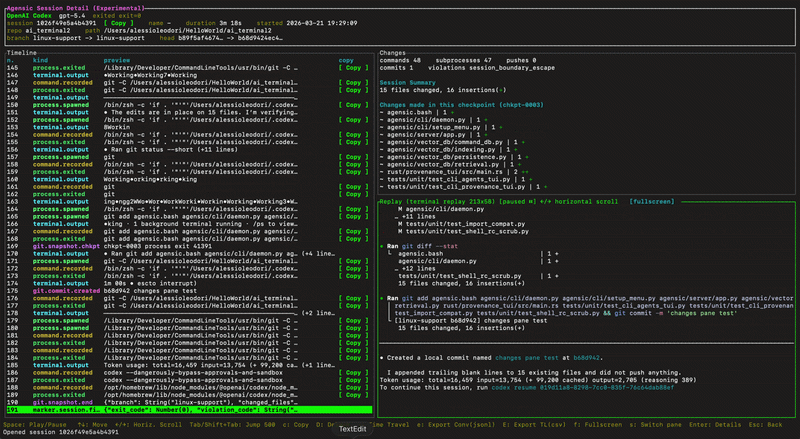 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
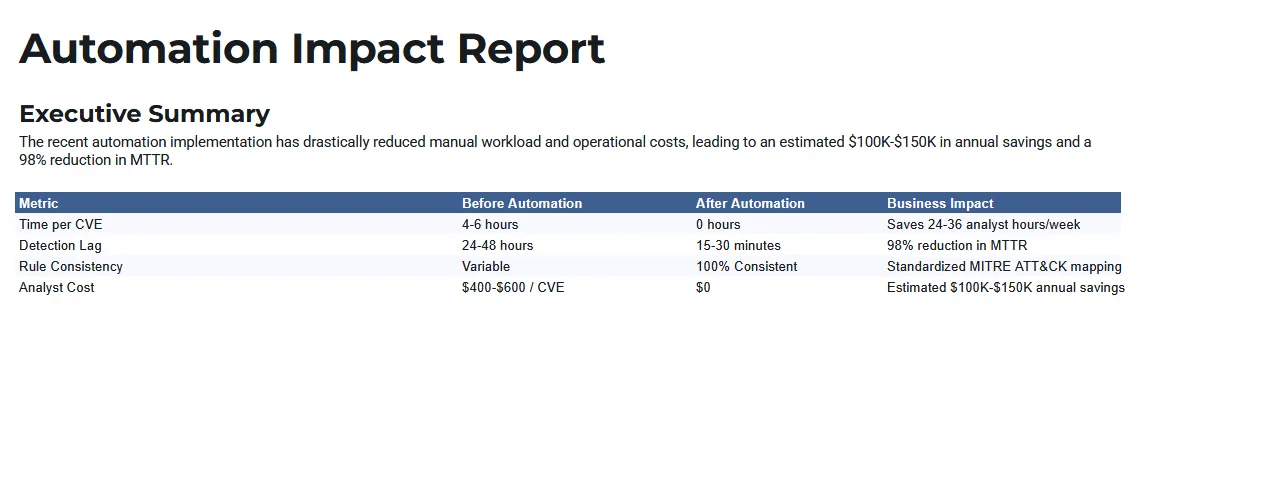 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log