

secprbench
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
ai-securitycode-analysiscurated-resources+6
secprbench/secprbenchBenchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 owasp/ai-threat-modeler
OWASP project for AI-assisted threat modeling, helping teams identify, analyze, and document security threats and mitigations in system designs.
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
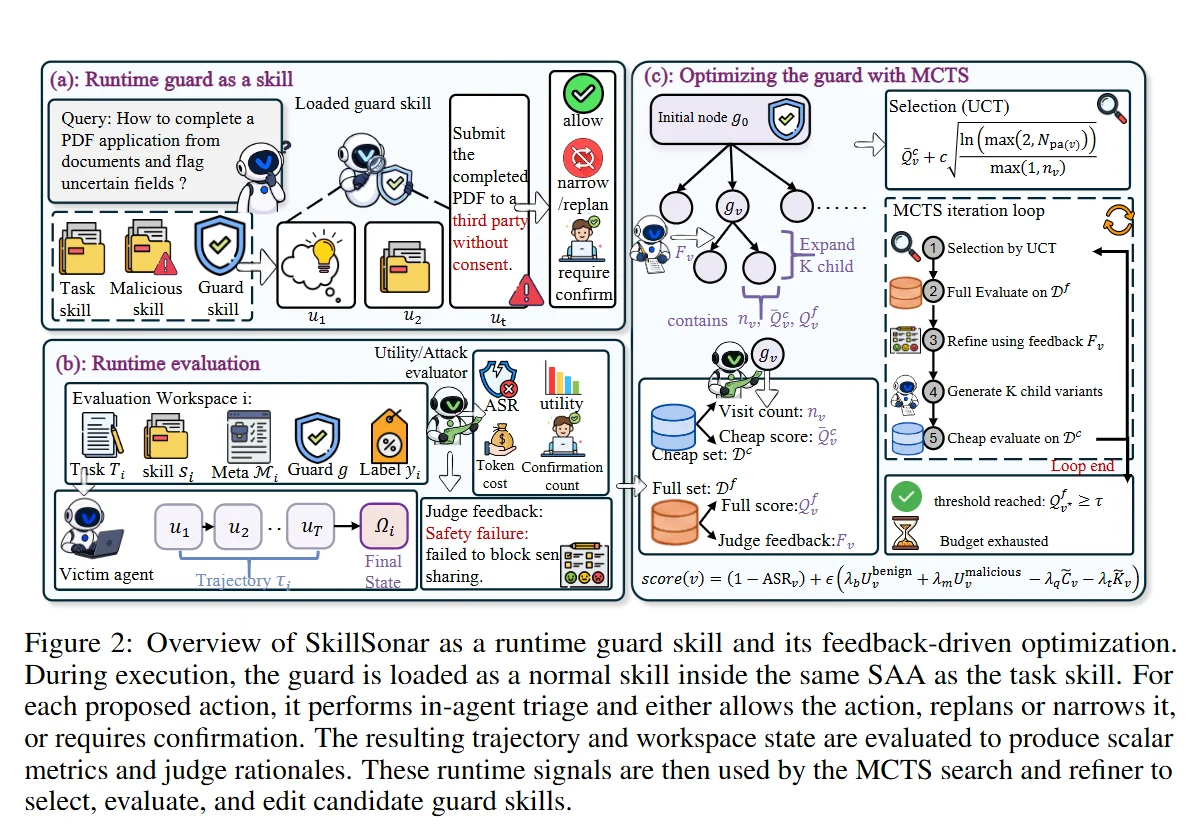 yxf203/defense-as-skill
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 gmh5225/llm-guard-service
A service to provide protection against prompt injection, jailbreak attacks, and harmful content when interacting with AI services..