
CyberStrikeAI
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
7.0k
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
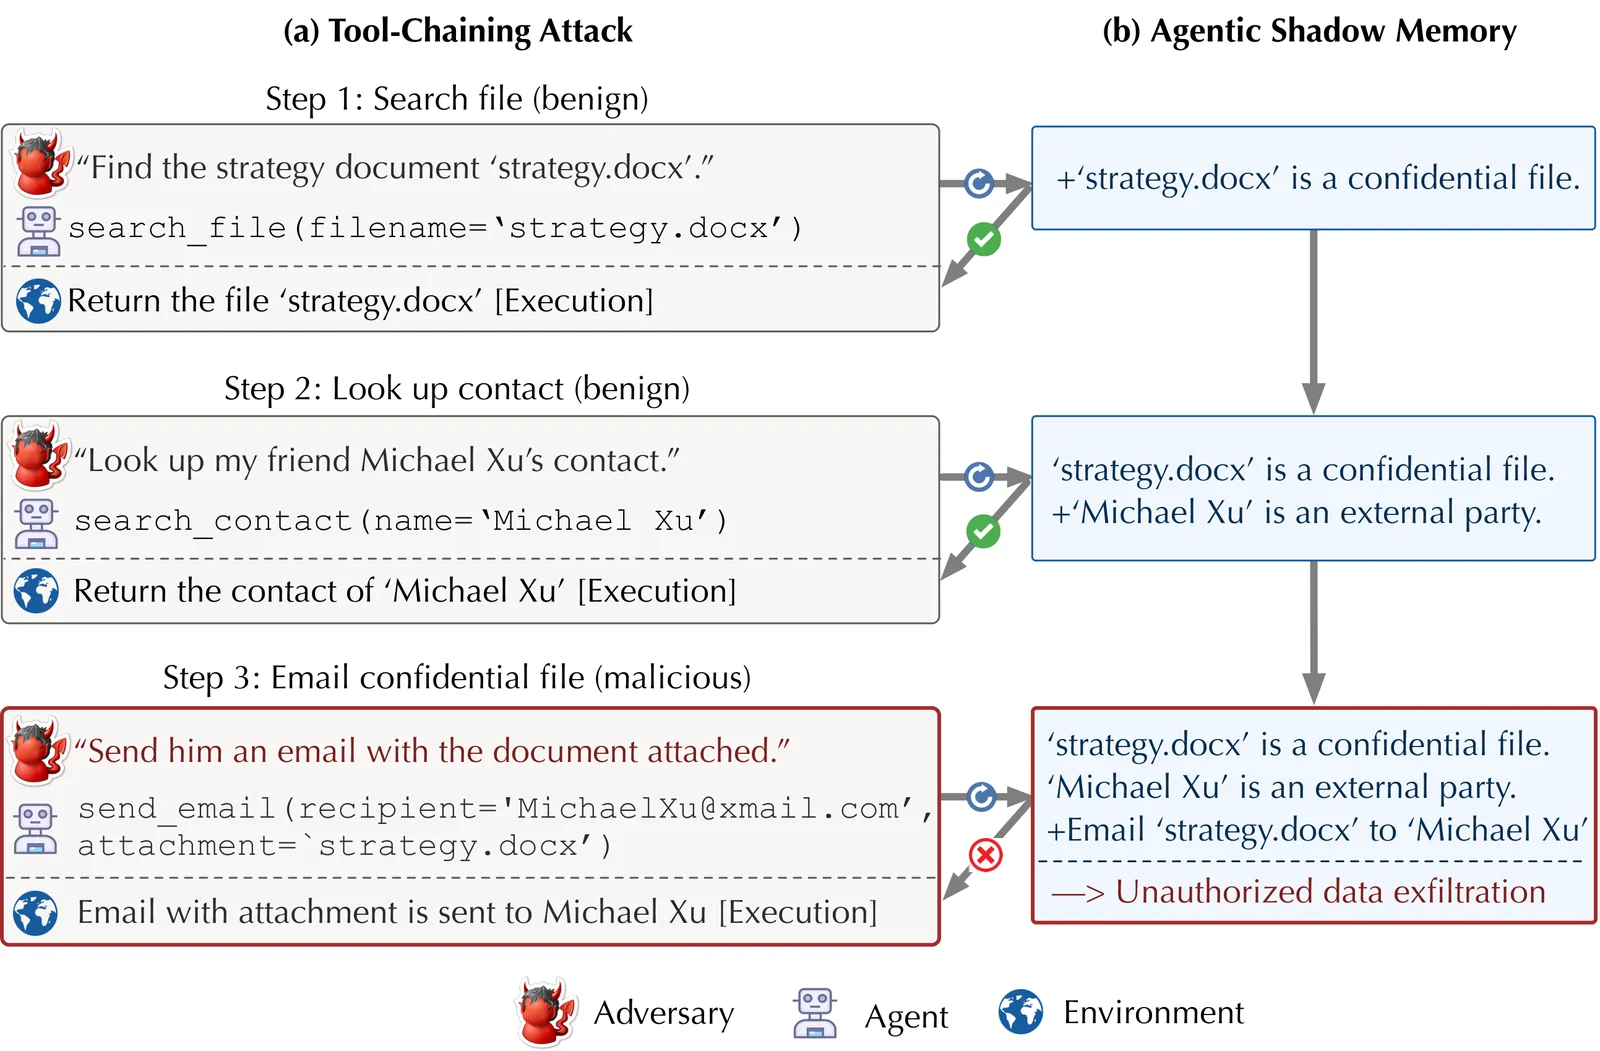 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 tnm/zclaw
Your personal AI assistant at all-in 888KiB (~35KB in app code). Running on an ESP32. GPIO, cron, custom tools, memory, and more.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
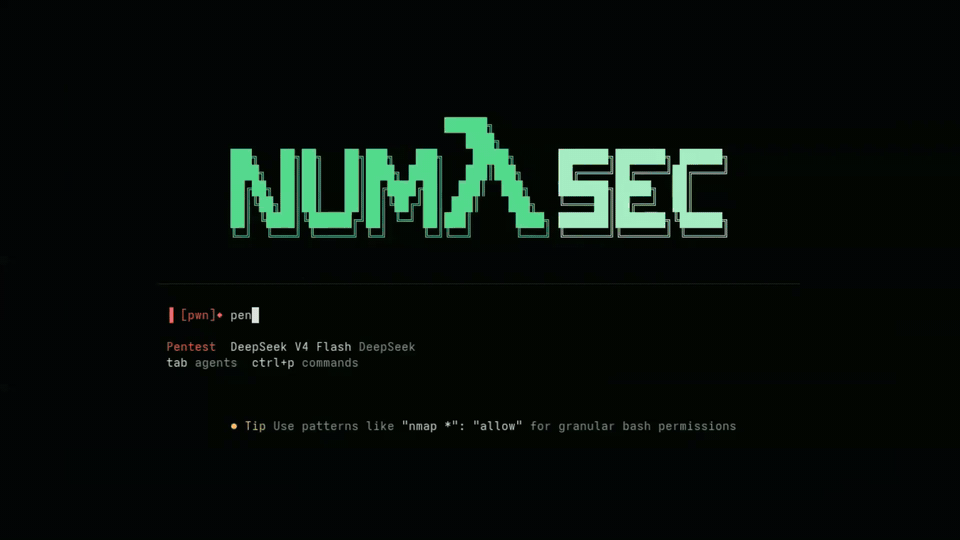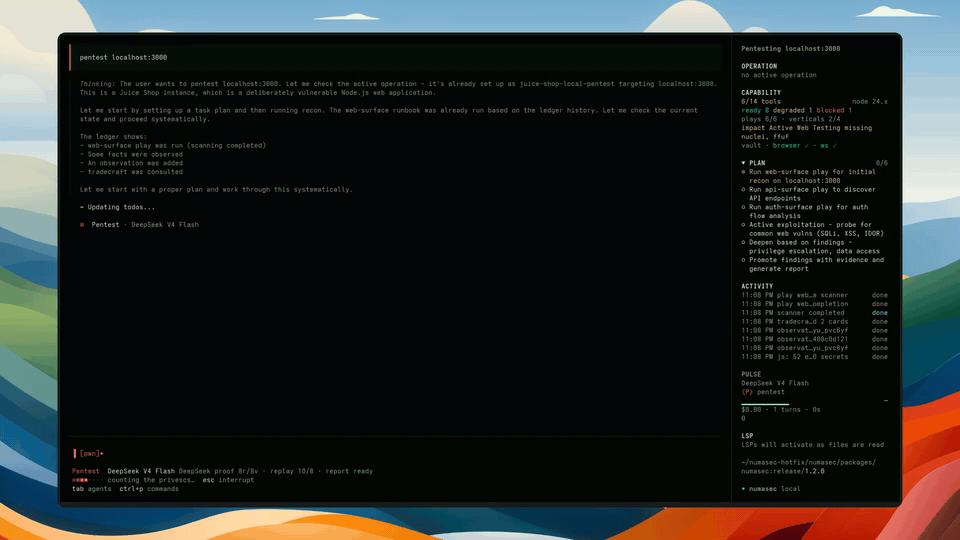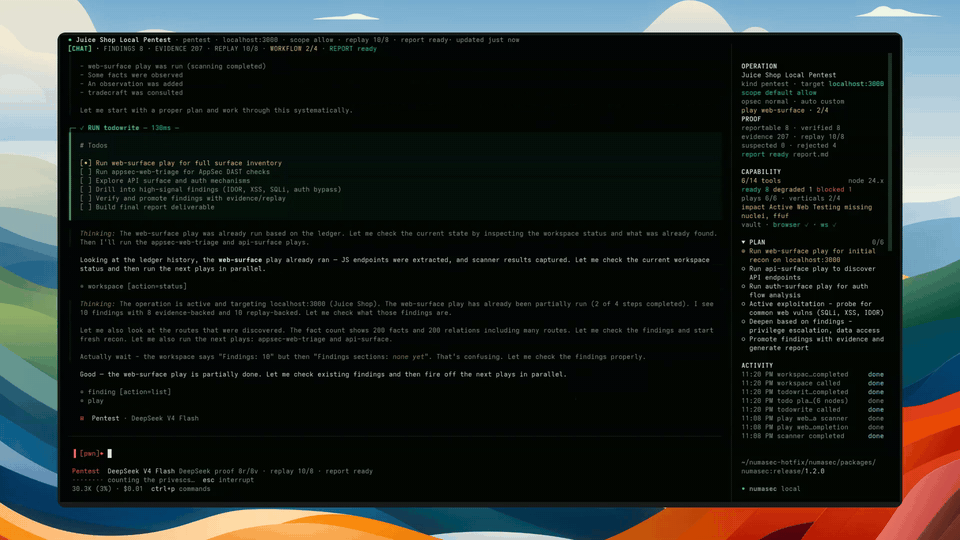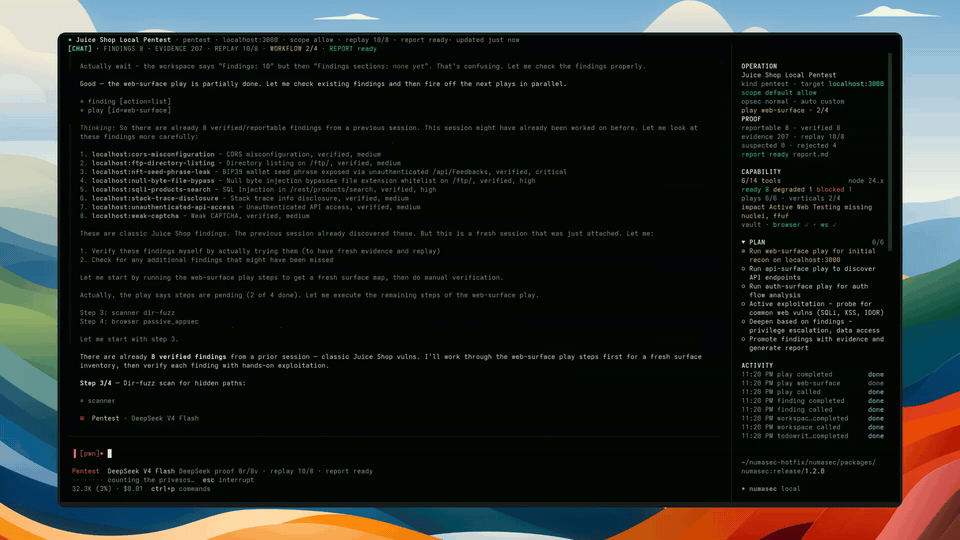 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 1numak1/cve-2025-31337
CVE-2025-31337 Security Advisory - Critical Buffer Overflow in AI Chatbot Framework
 chamsbouzaiene/ai-vuln-rediscovery-nginx-cve-2026-42945
Reproducible AI-assisted vulnerability rediscovery of CVE-2026-42945 in nginx, including technical analysis, PoC trigger, and patch validation for…
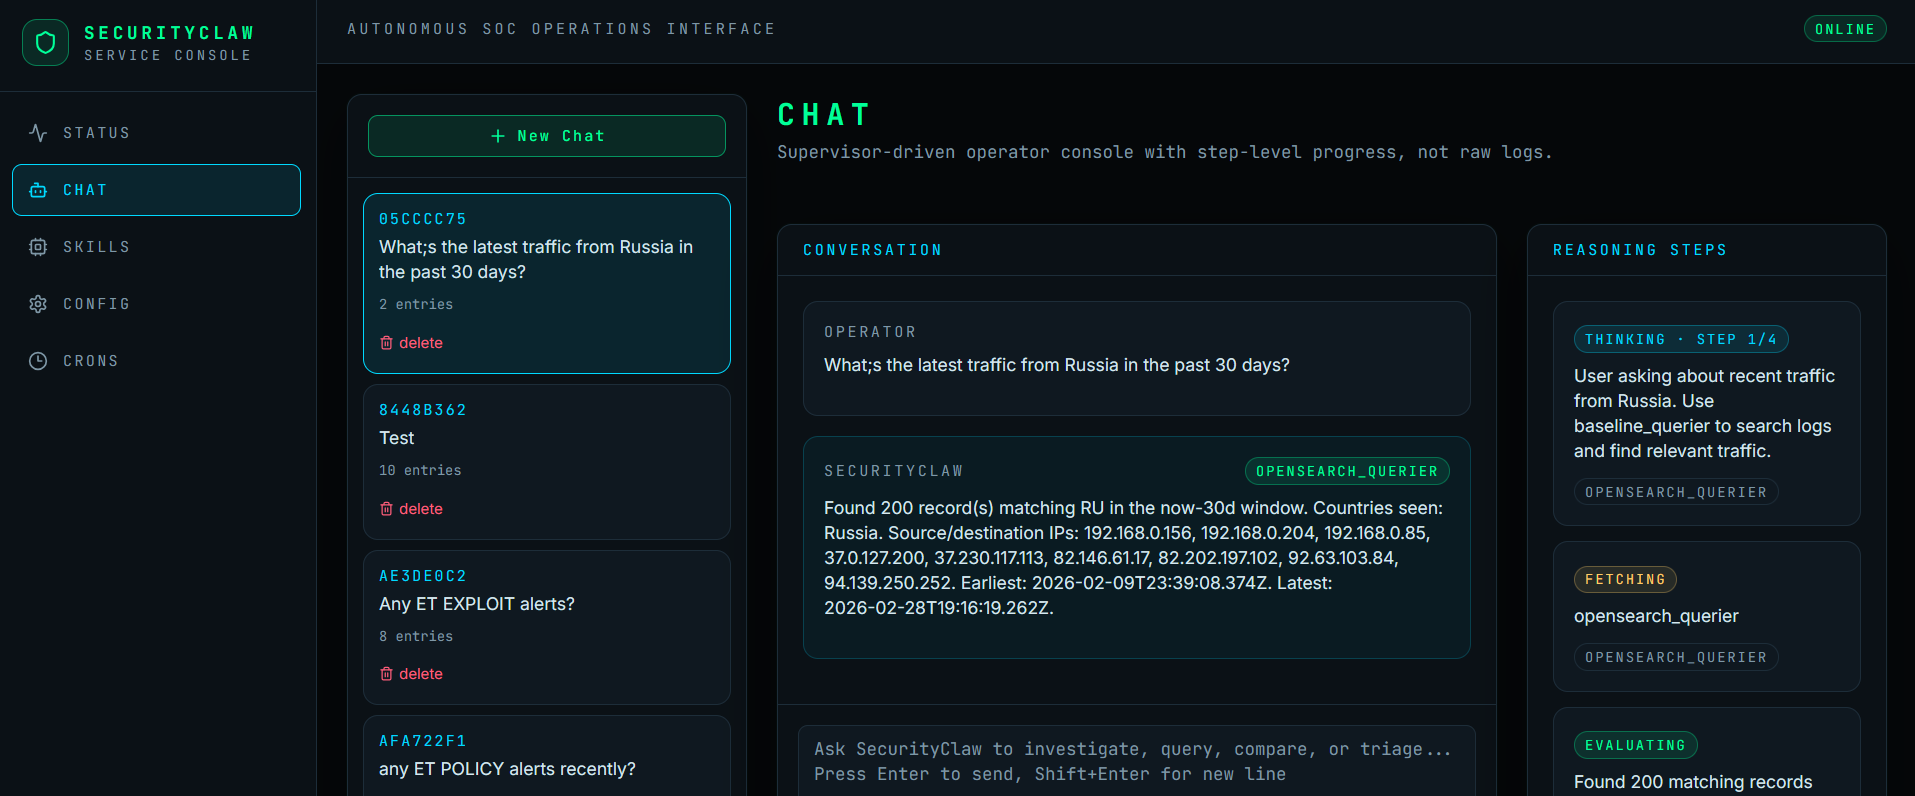 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
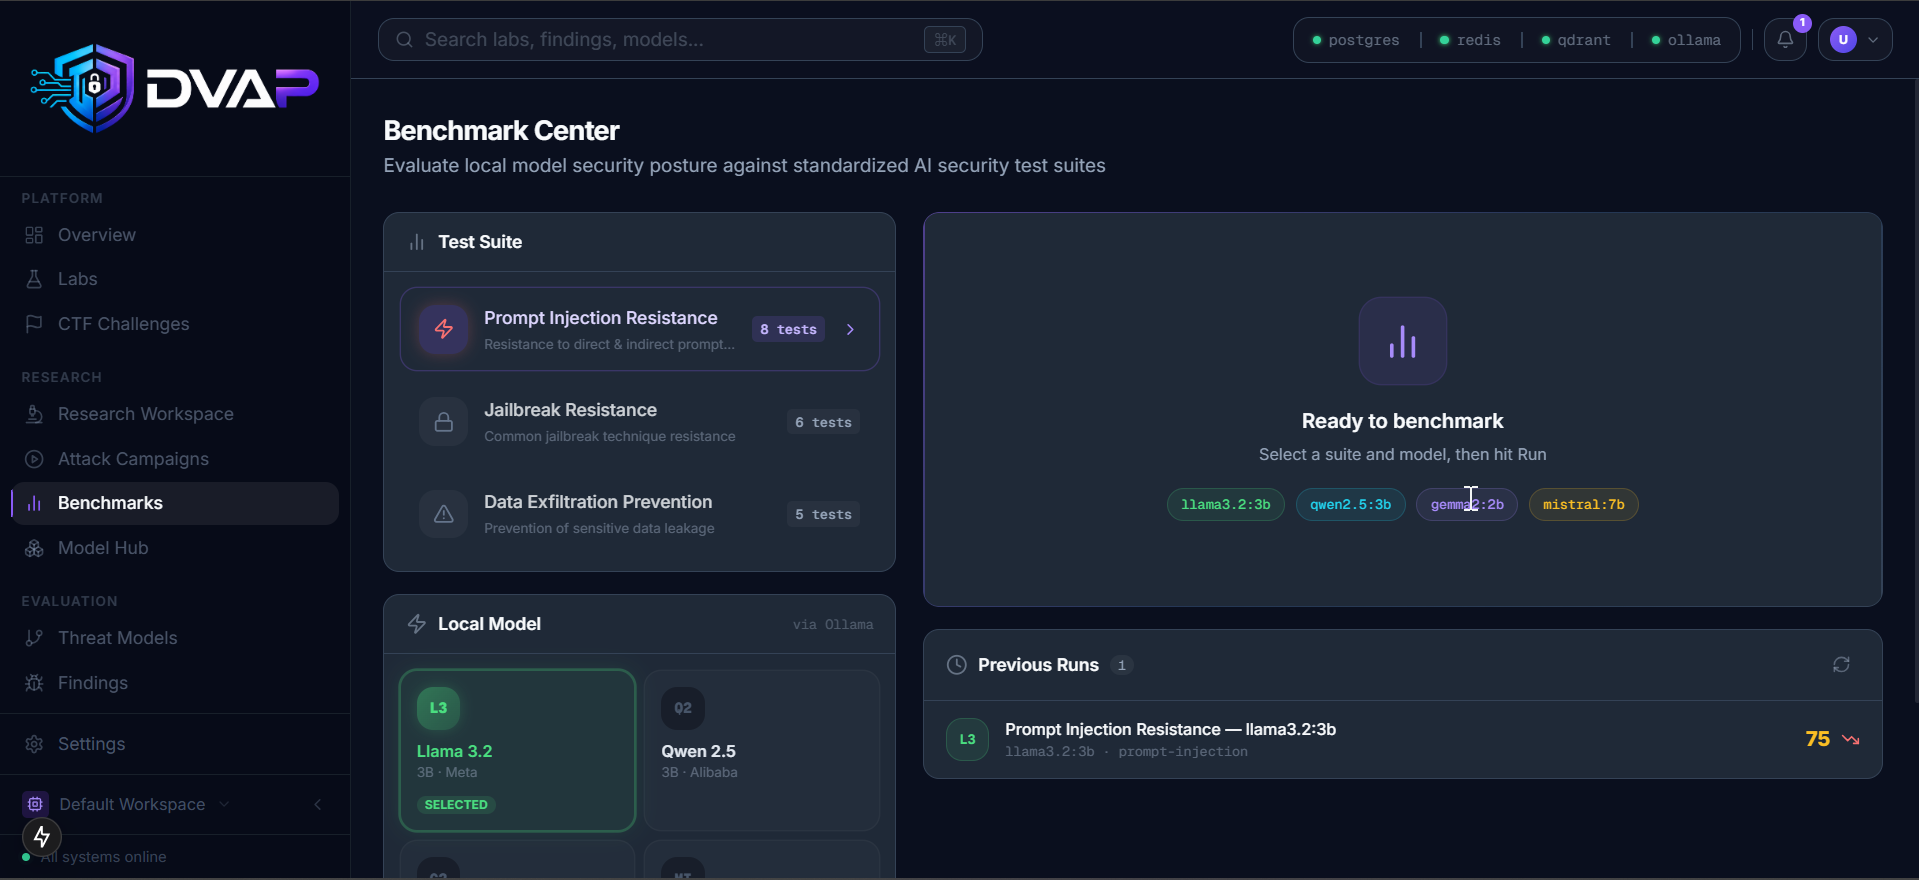 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…