

skills
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
ai-assisted-reversingcode-analysiscurated-resources+8
7.3k
trailofbits/skillsTrail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
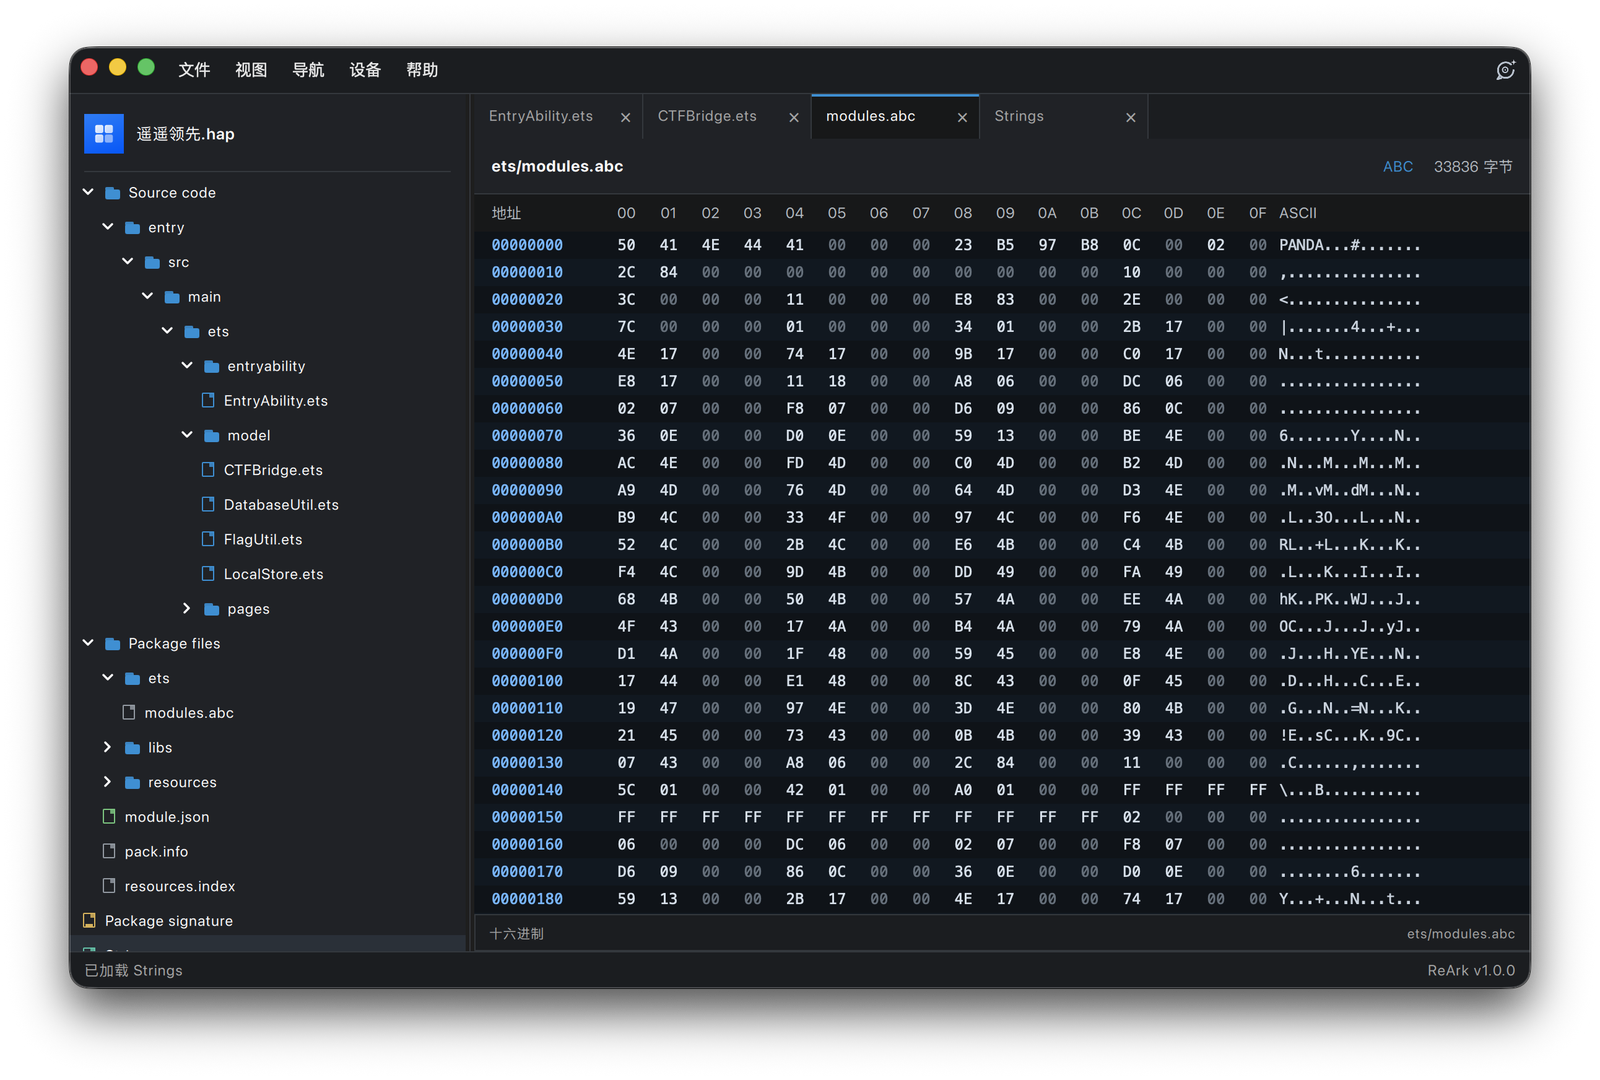 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
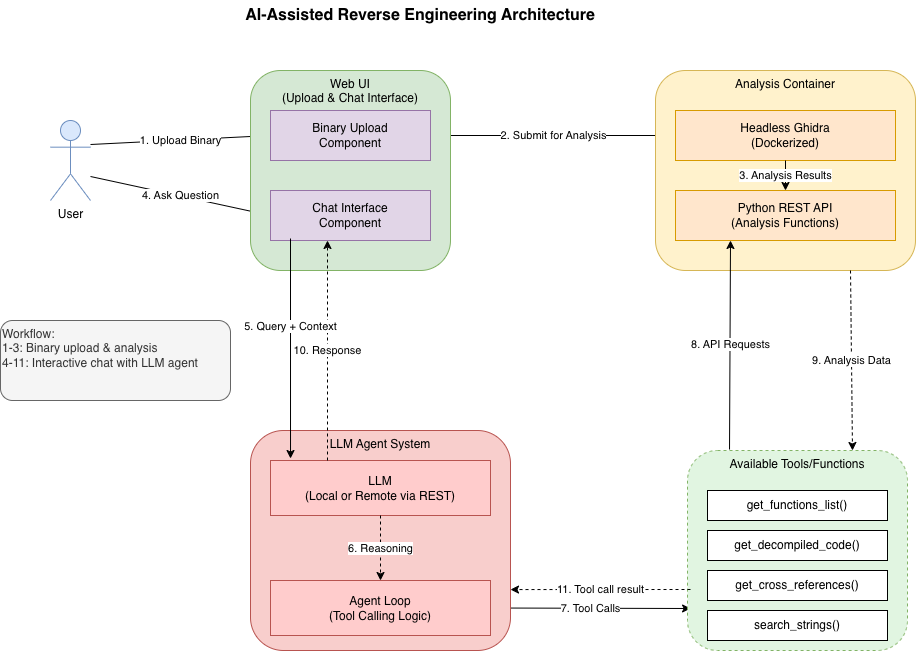 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
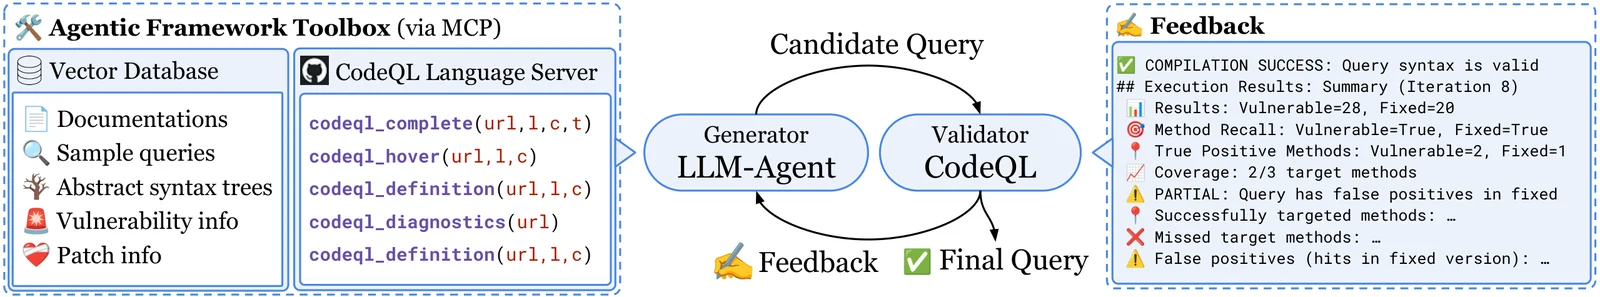 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
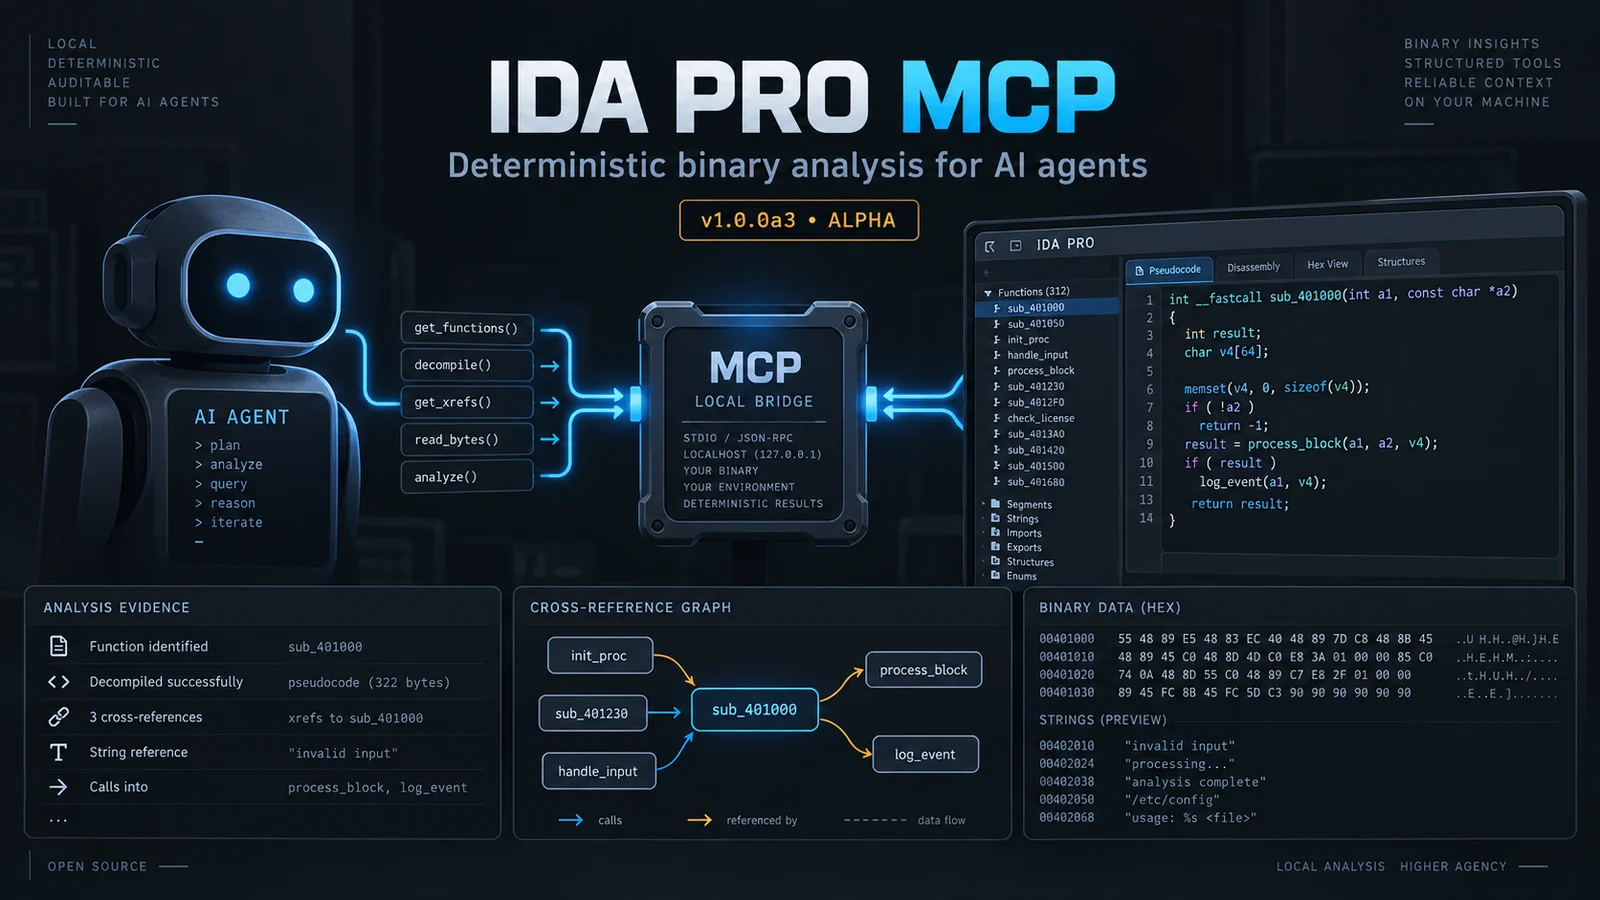 grecandrei/ida-pro-mcp
Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.