
LIEF
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
ai-assisted-reversingandroid-securitybinary-analysis+12
5.6k
lief-project/liefCross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
 0xdea/oneiromancer
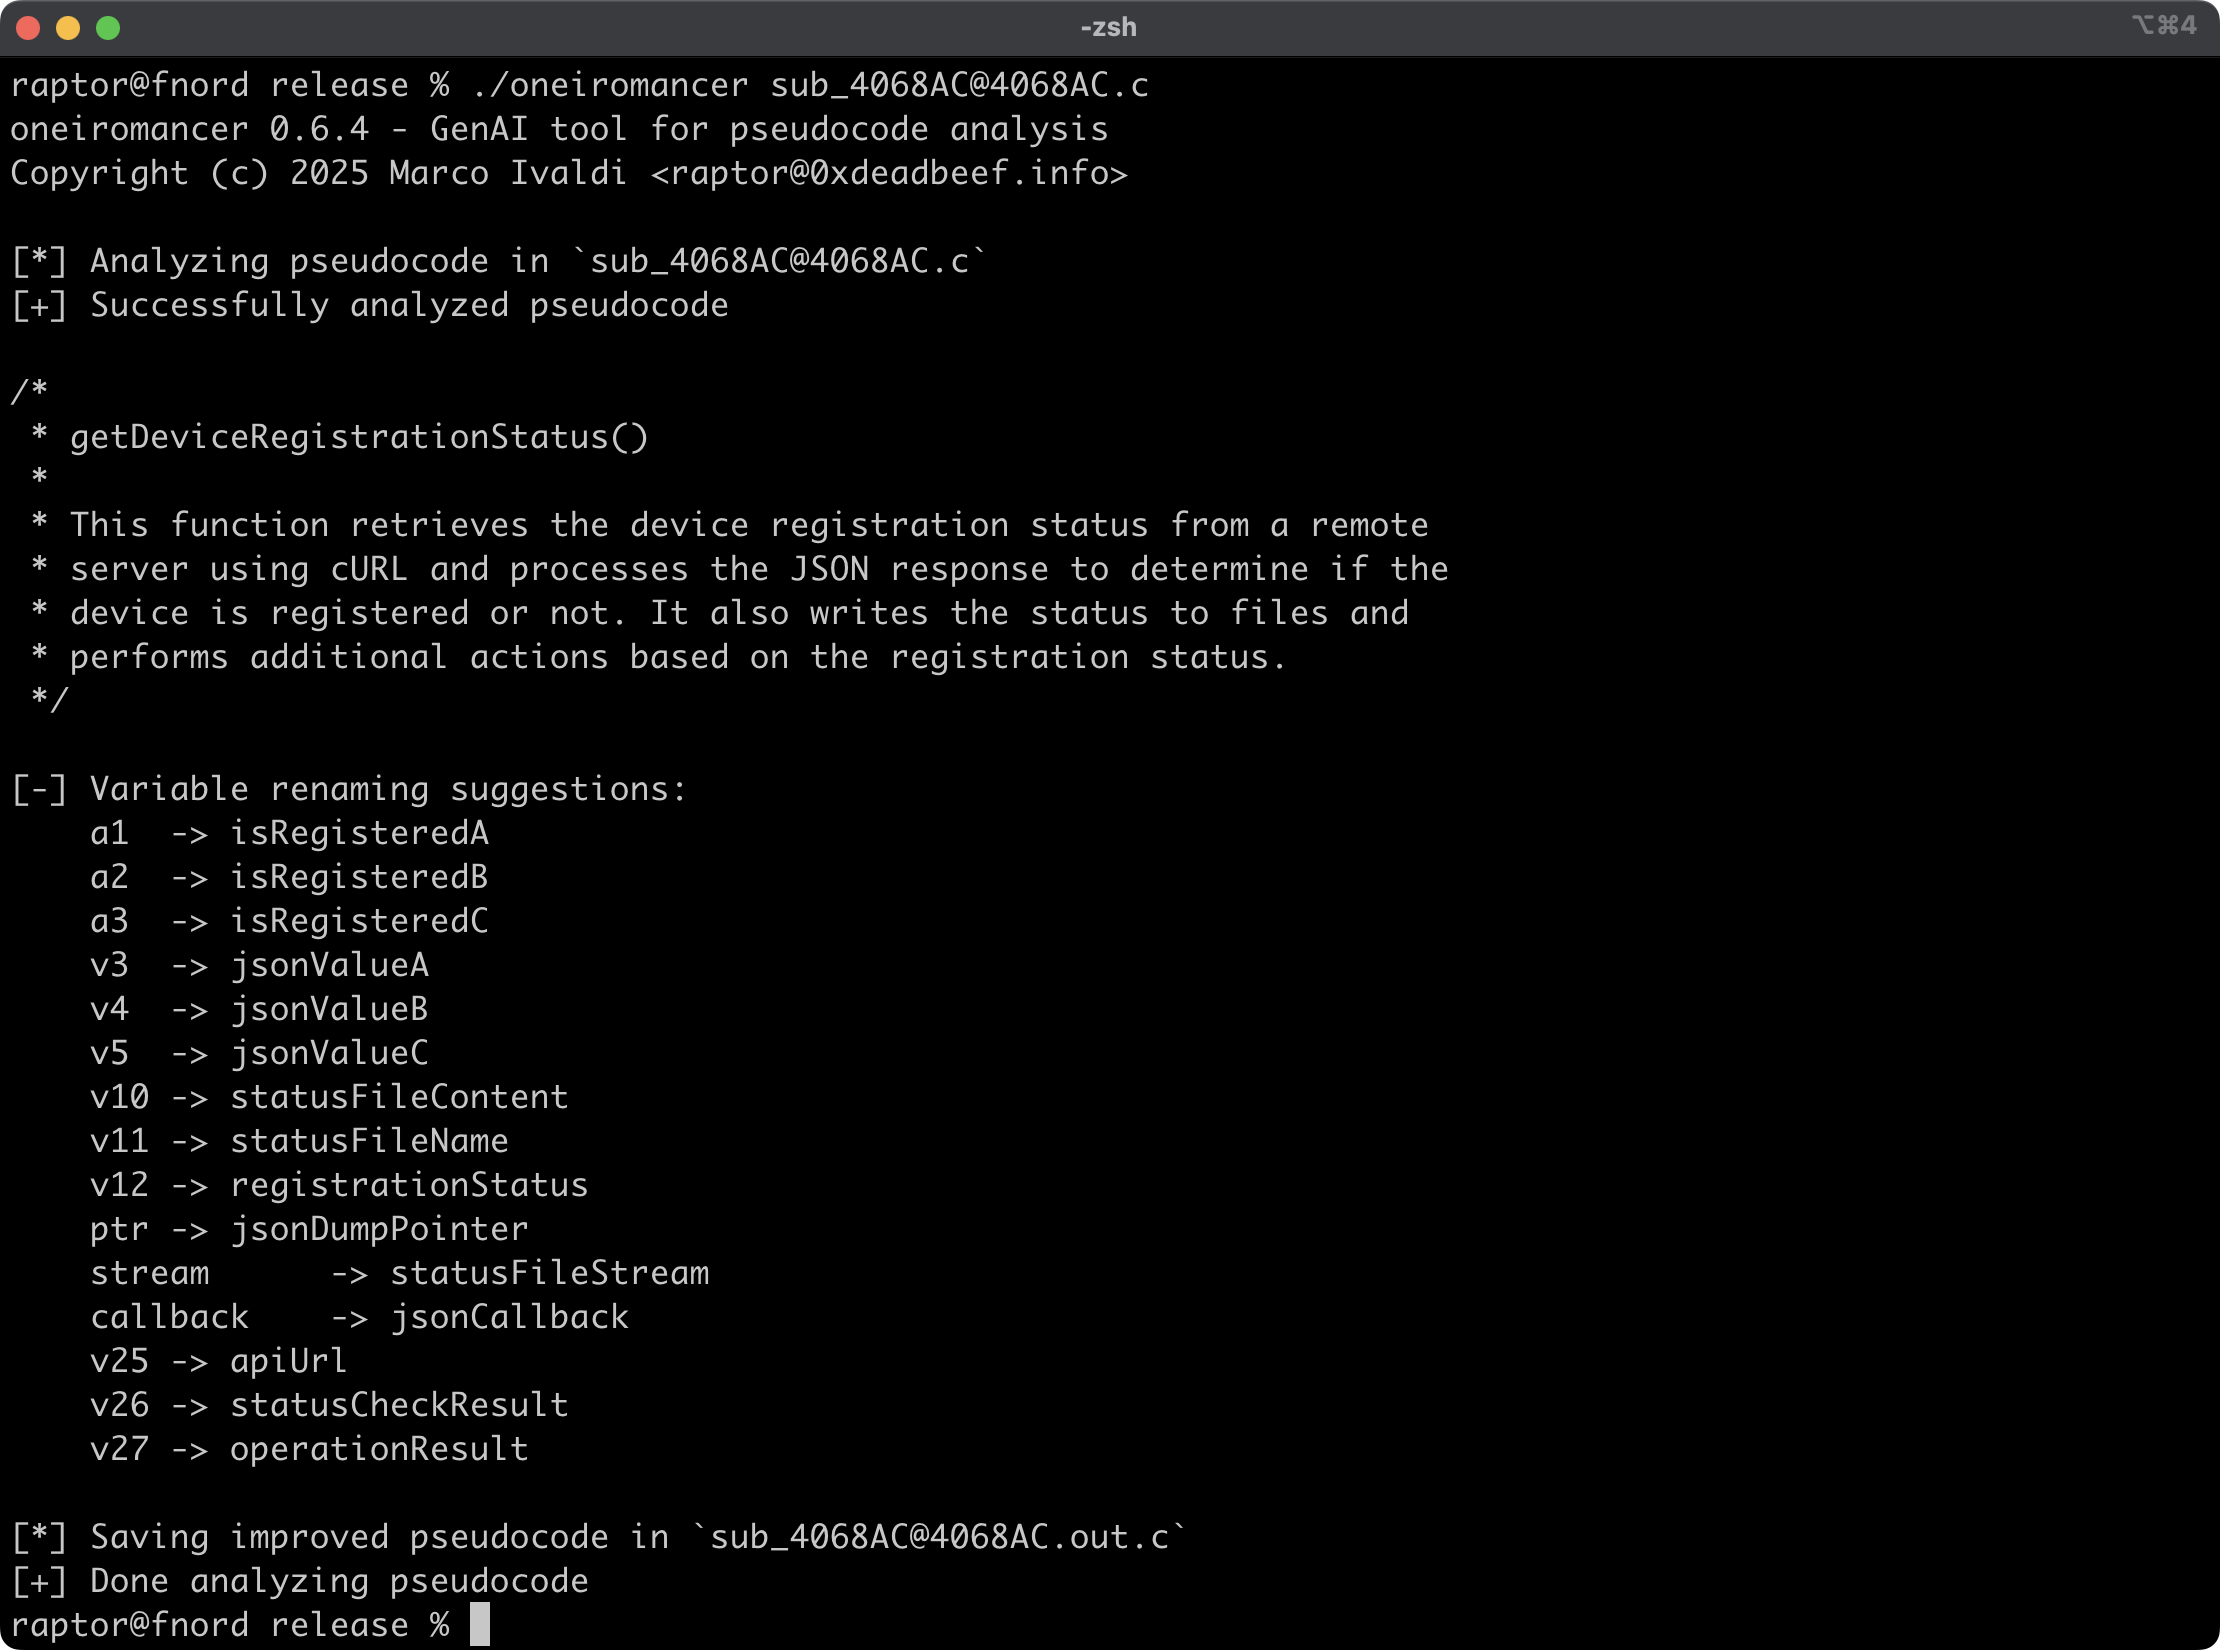
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
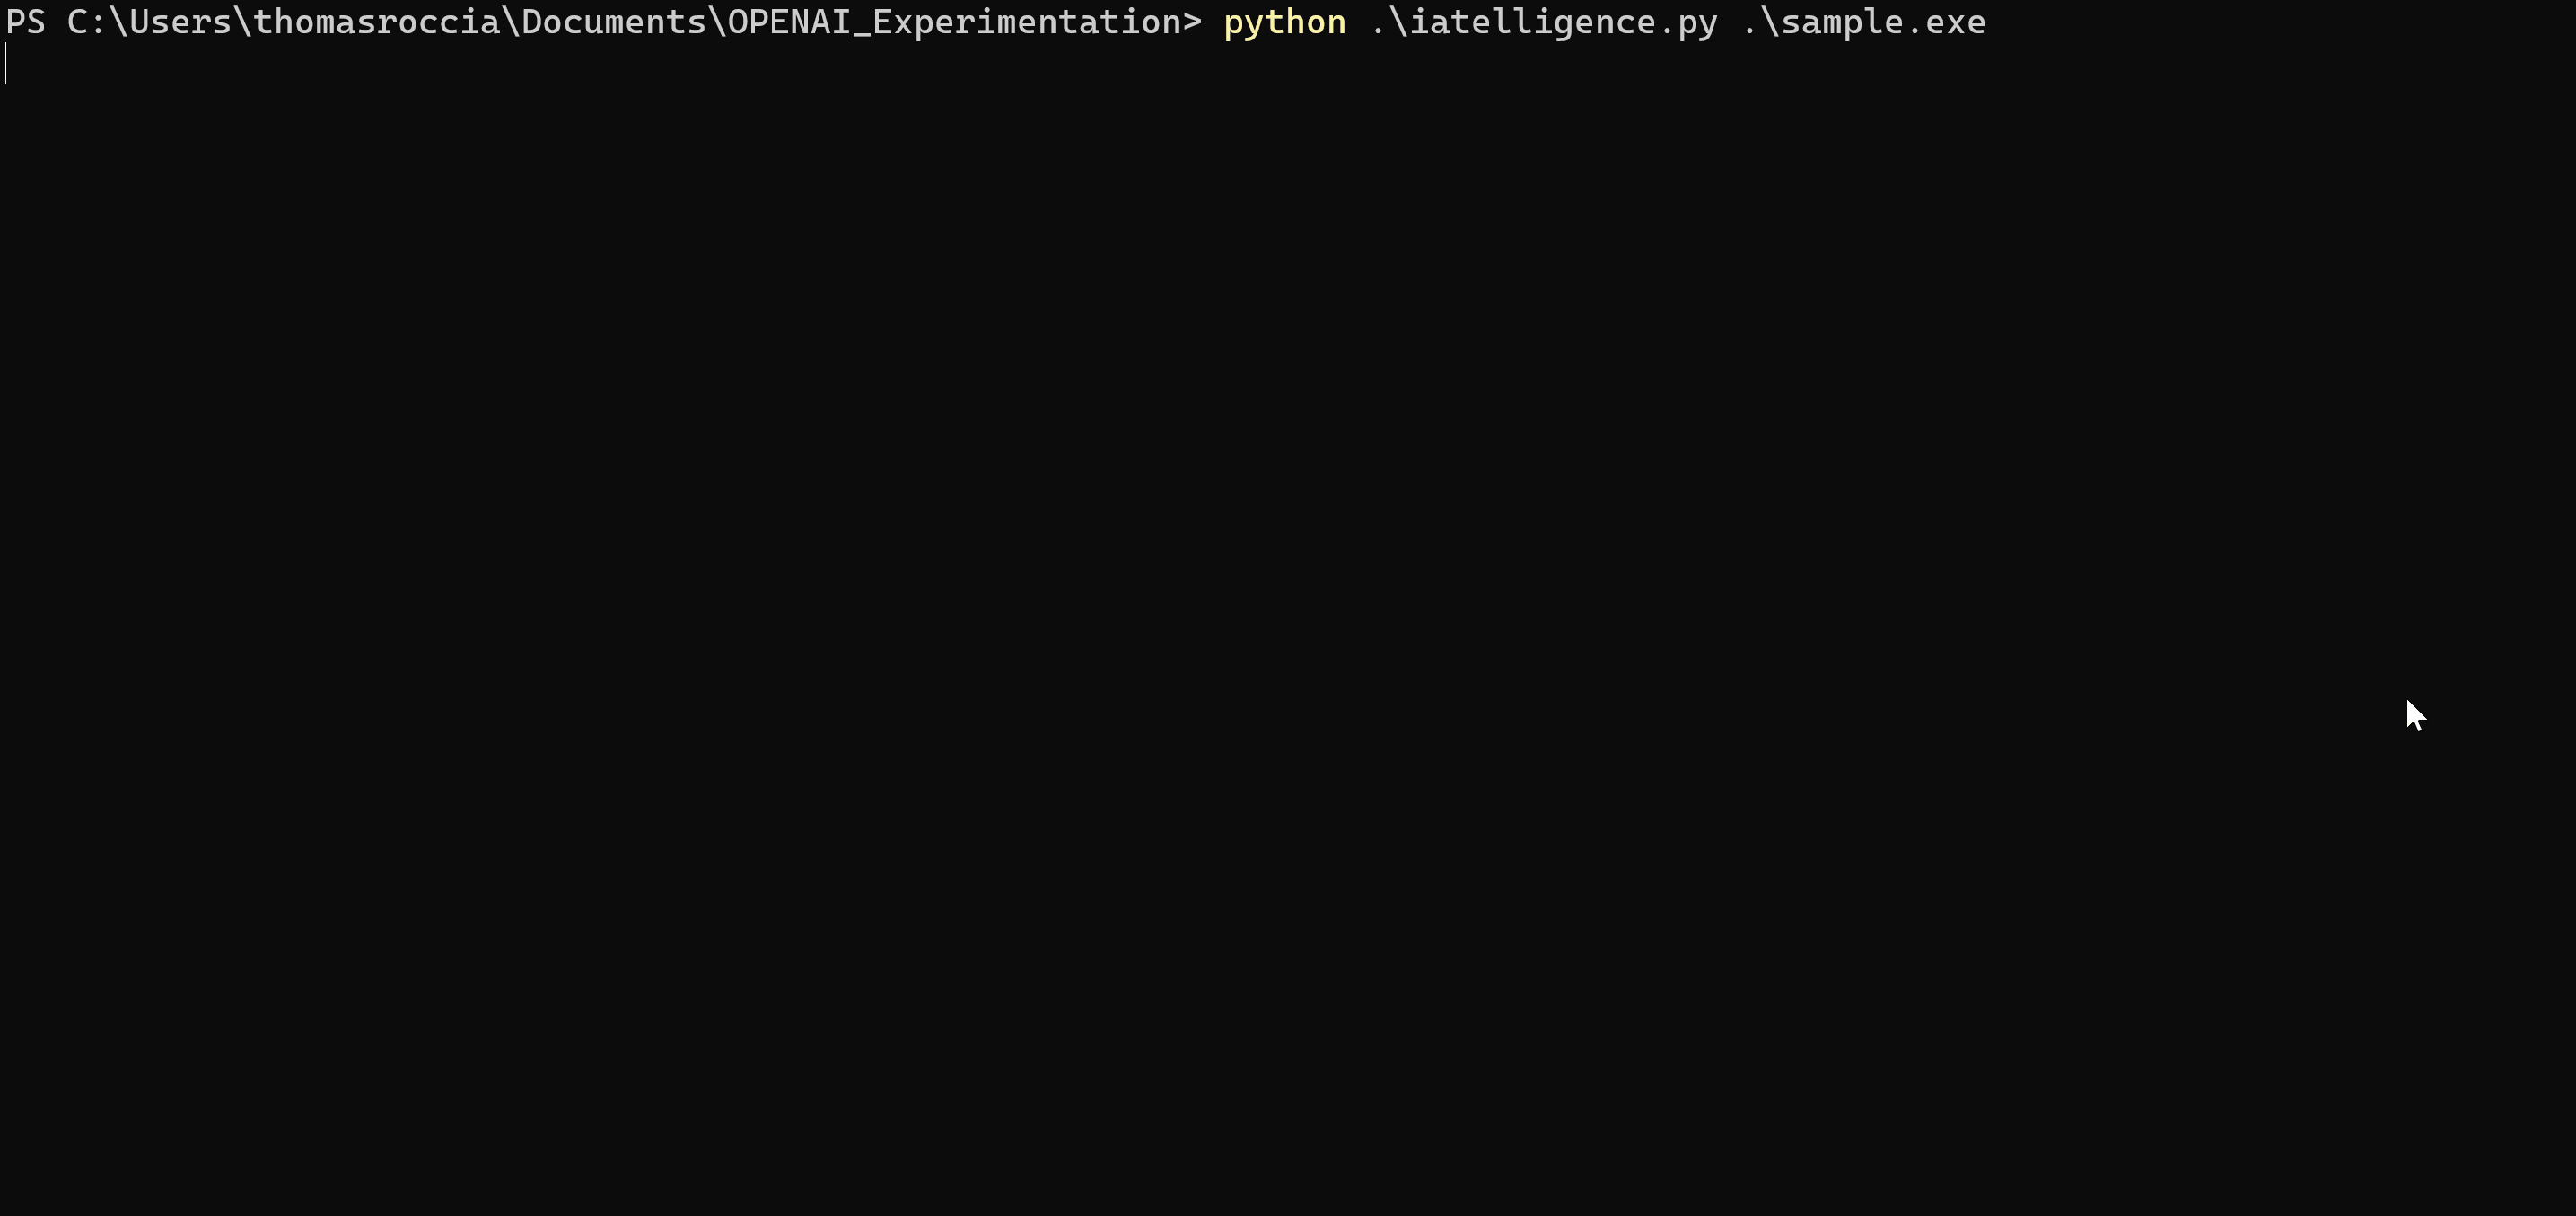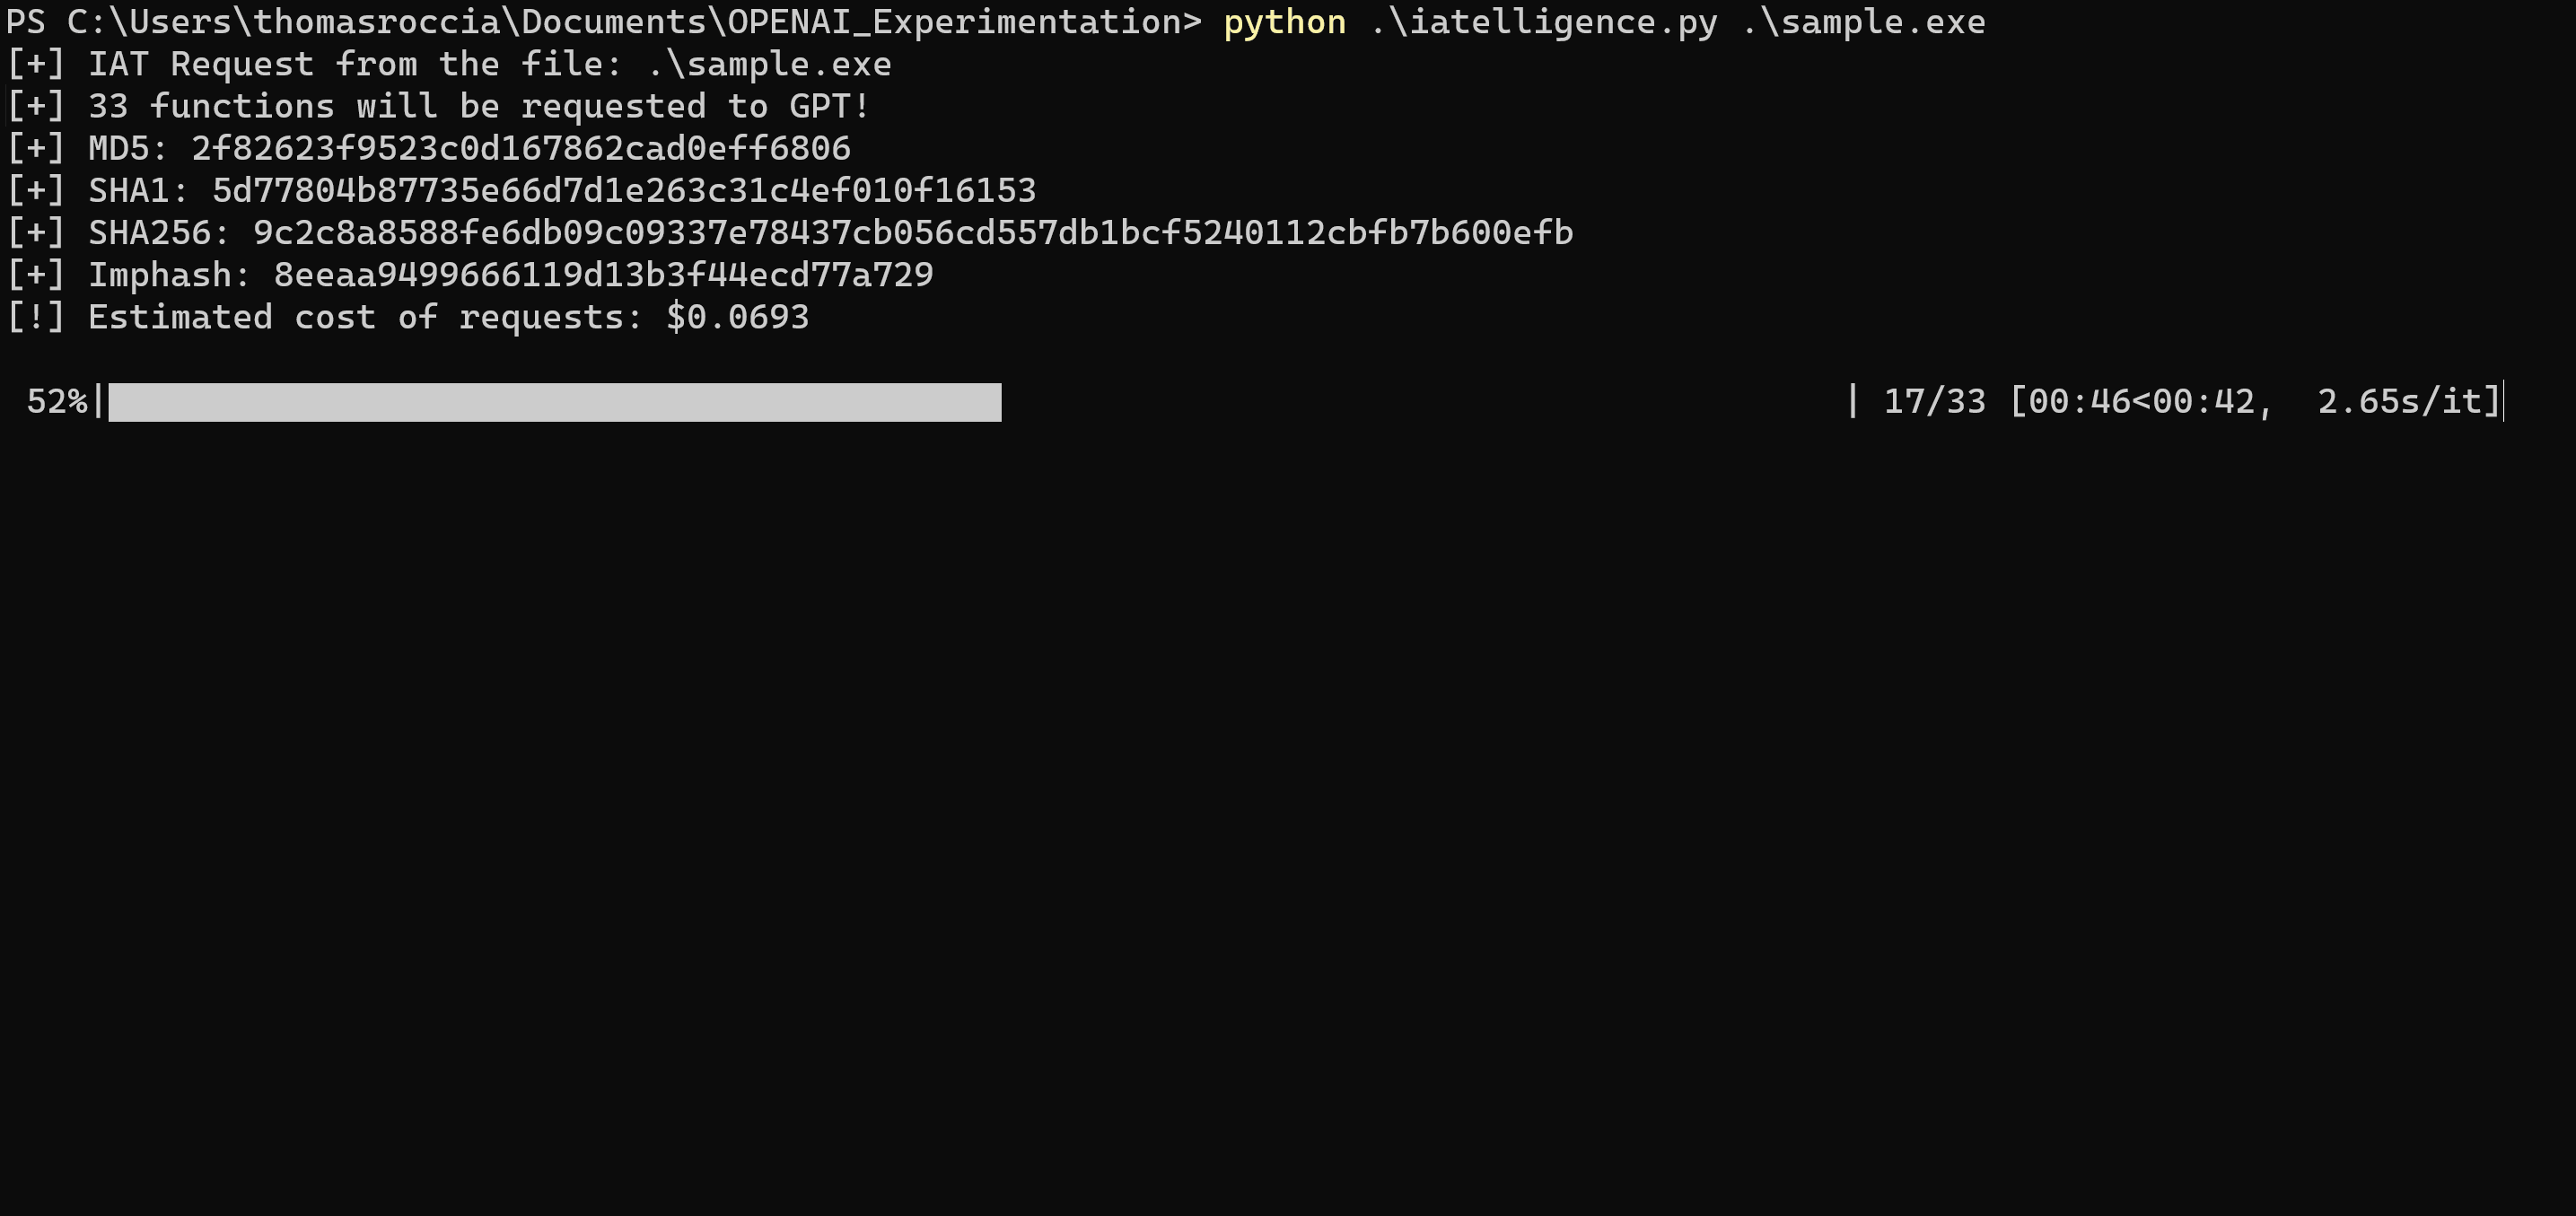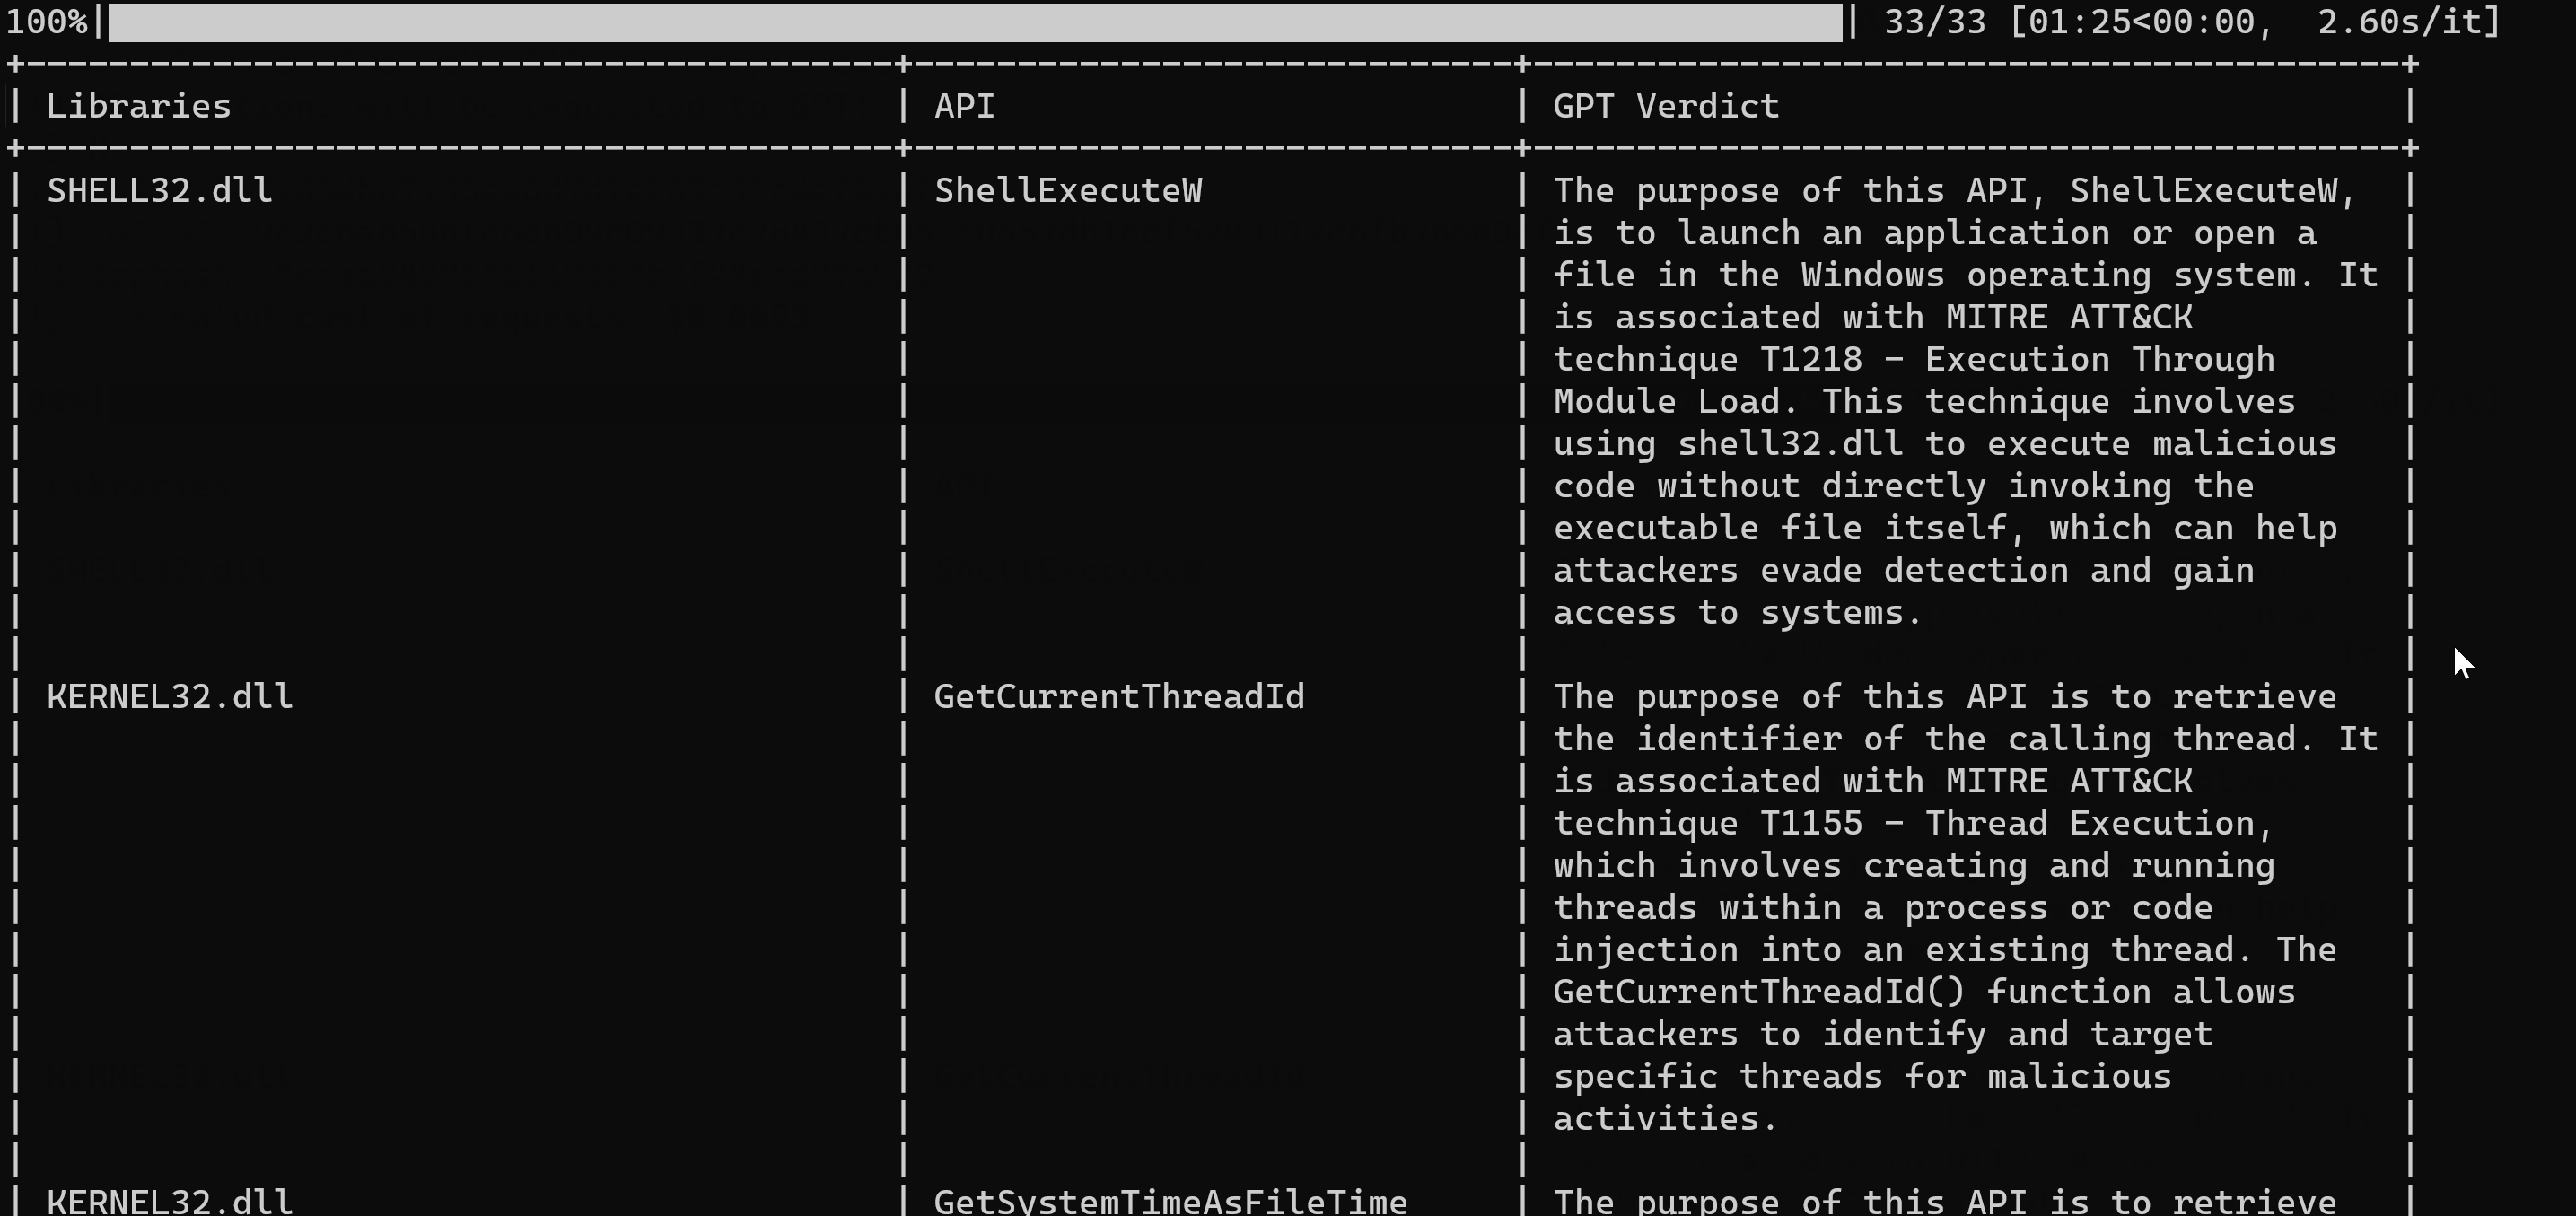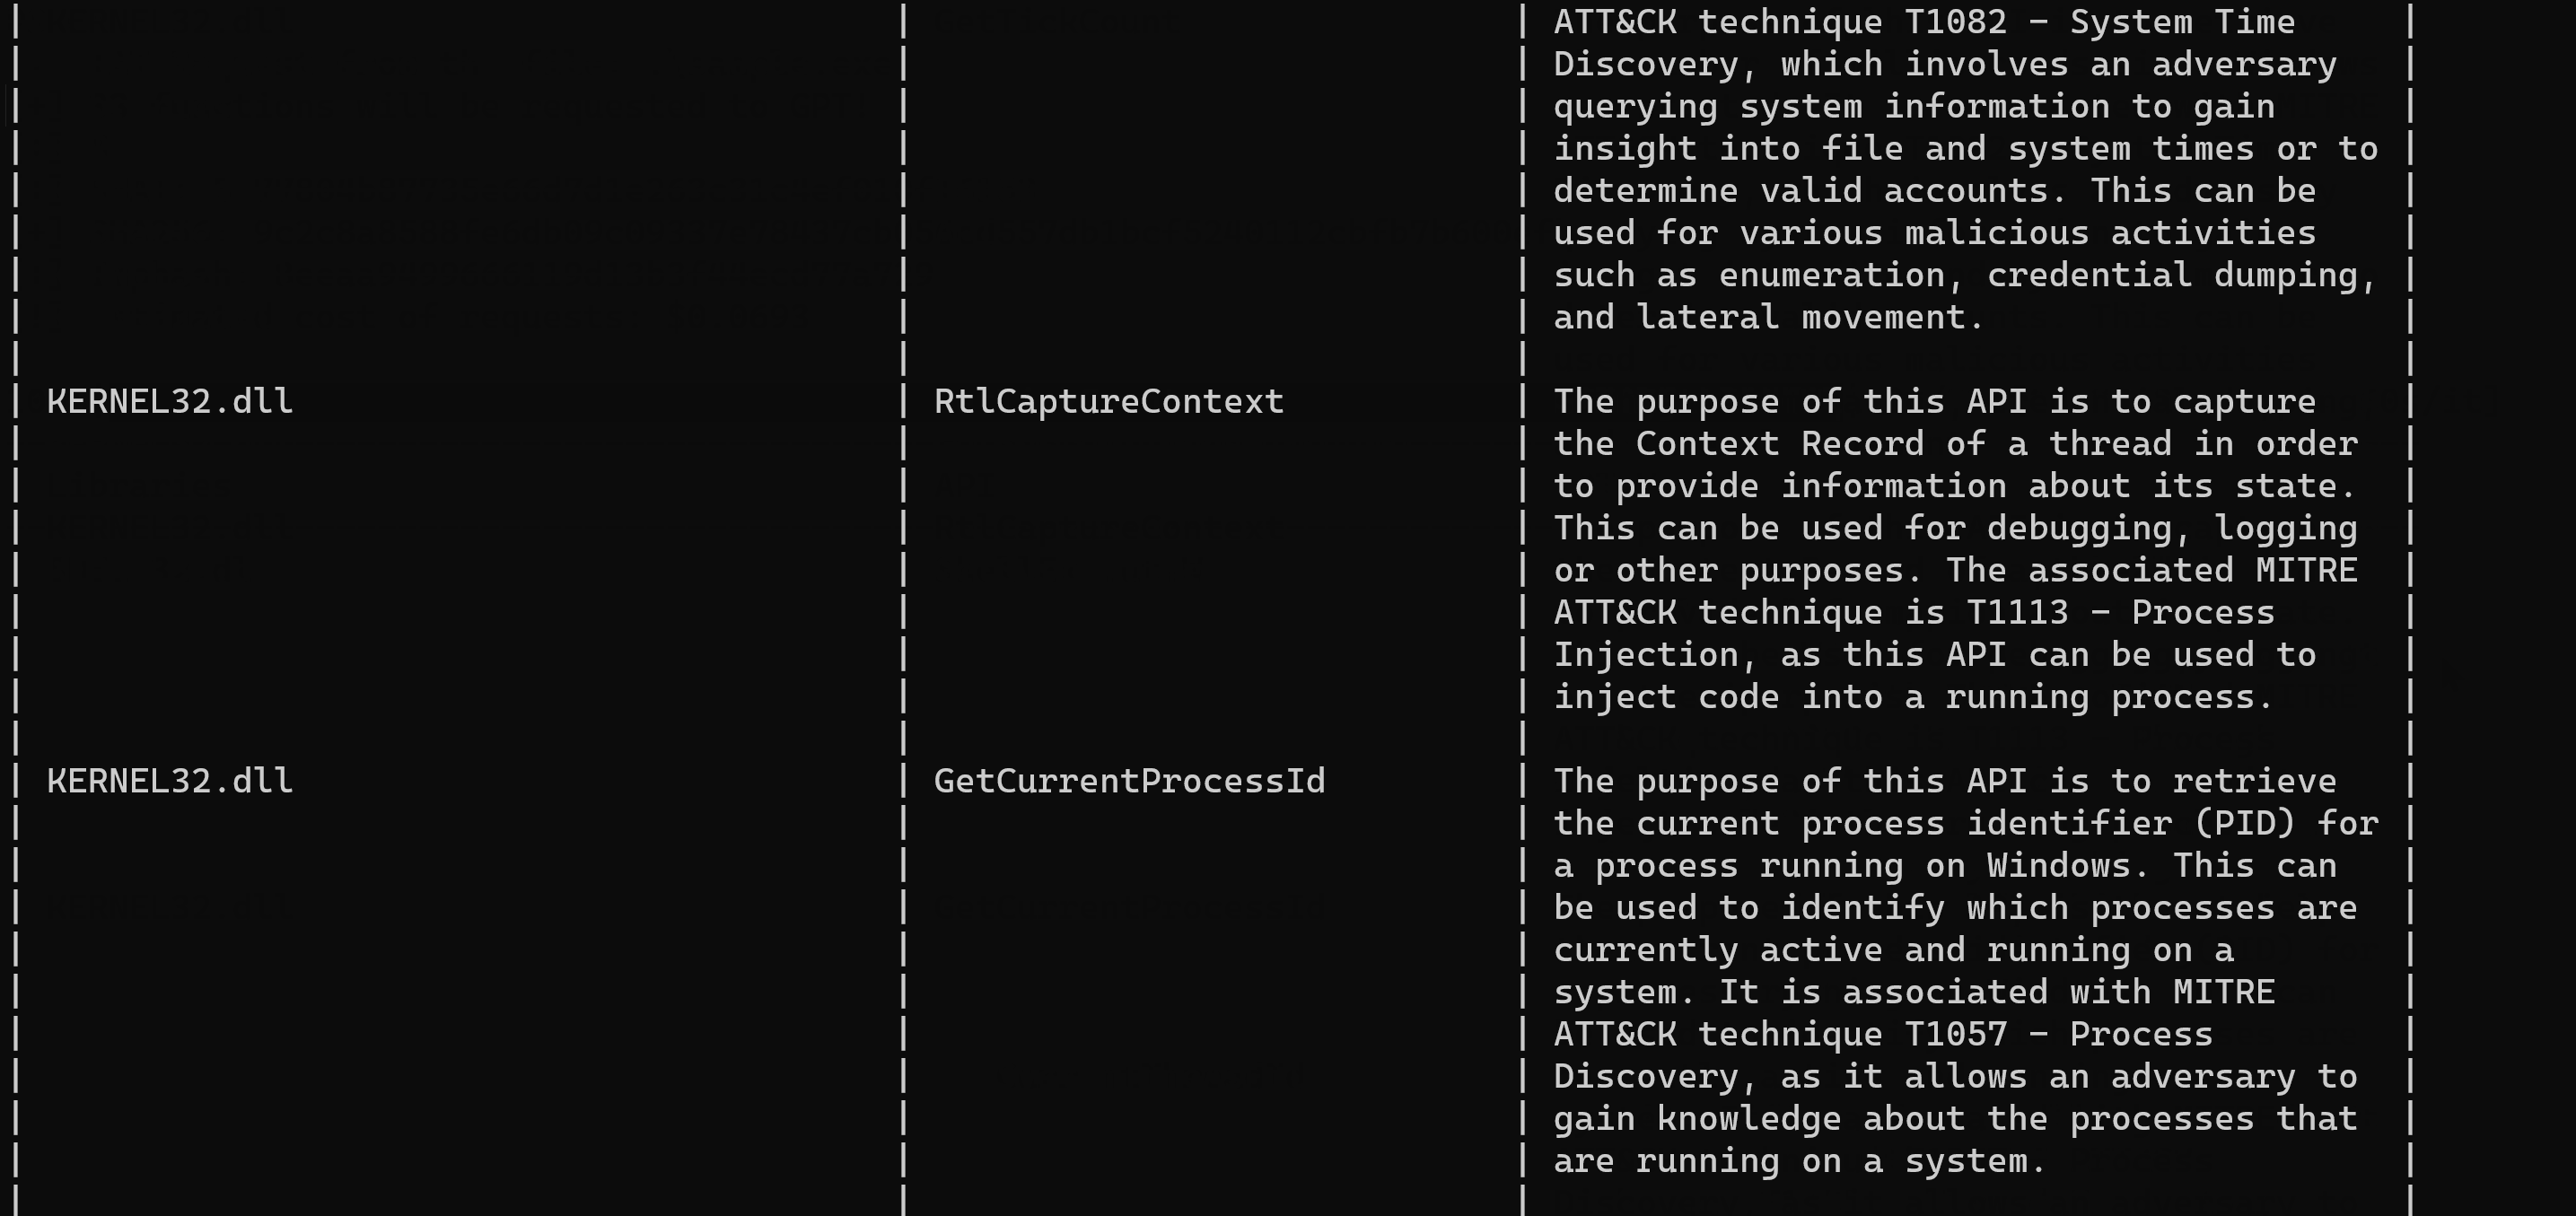 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 miscusi-peek/cheatengine-mcp-bridge
Connect Cursor, Copilot & Claude AI directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 akamai/cve-2025-60719-afd.sys
Proof-of-concept and root-cause analysis of CVE-2025-60719, a use-after-free vulnerability in Windows afd.sys leading to local privilege escalation,…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
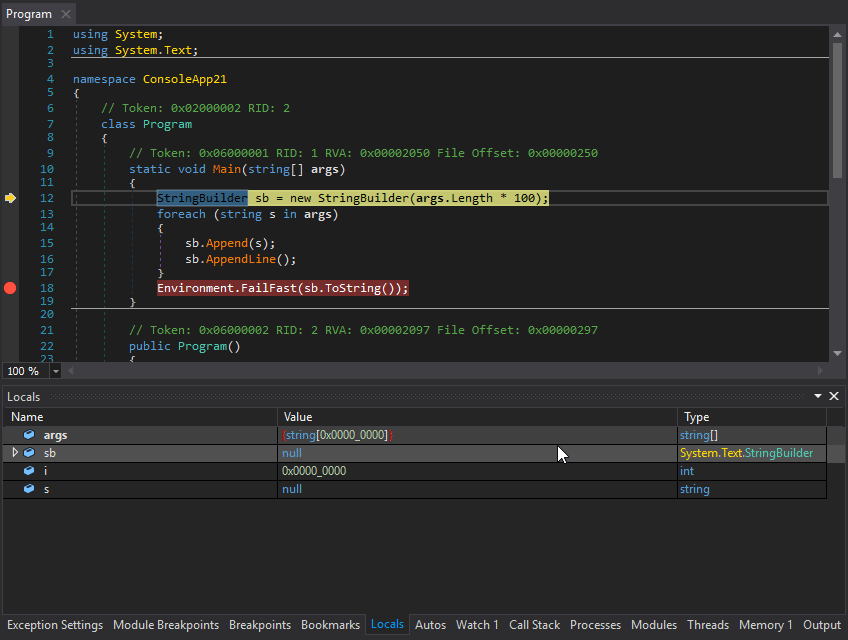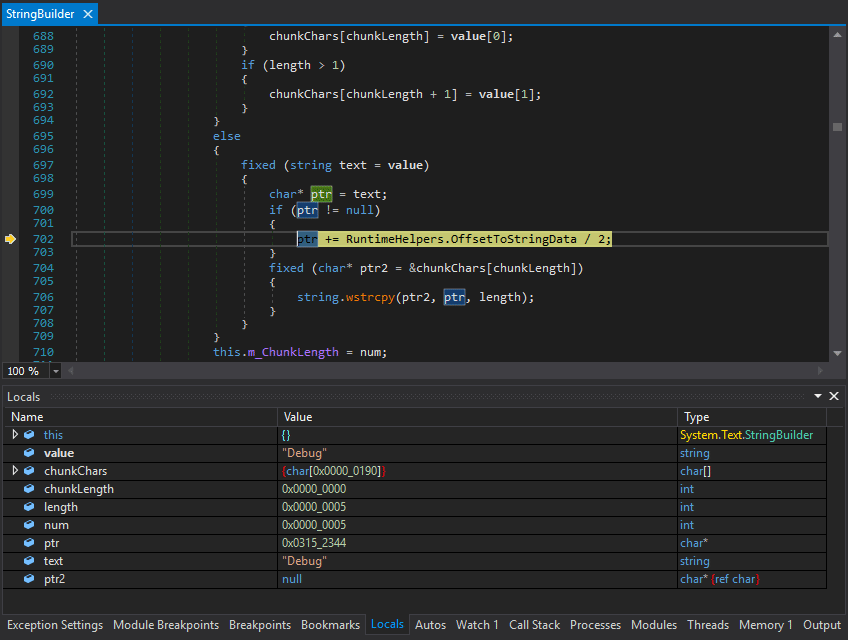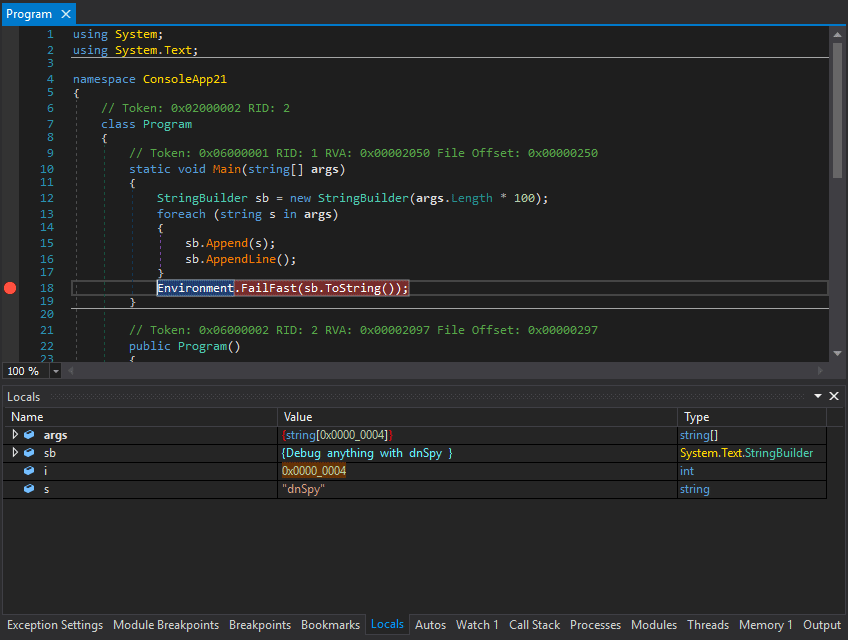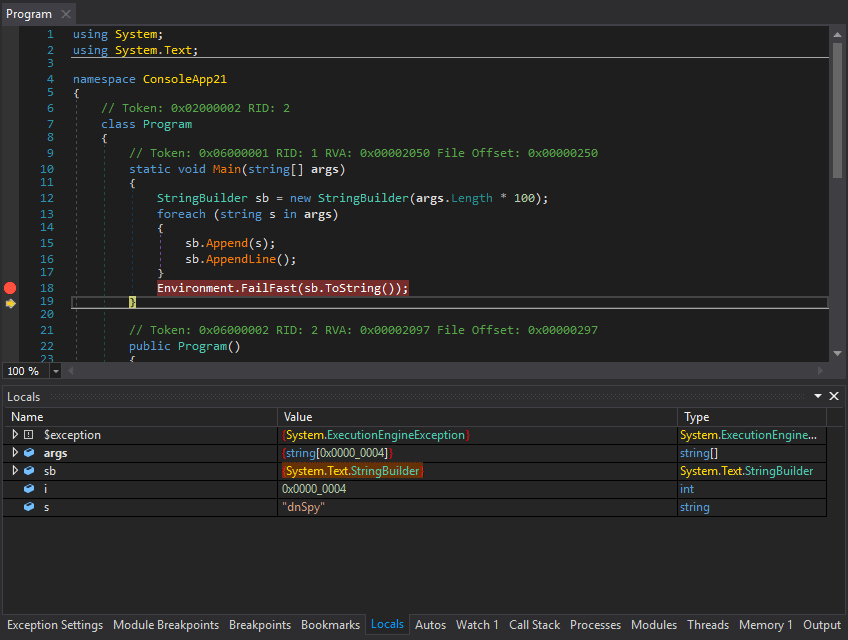 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
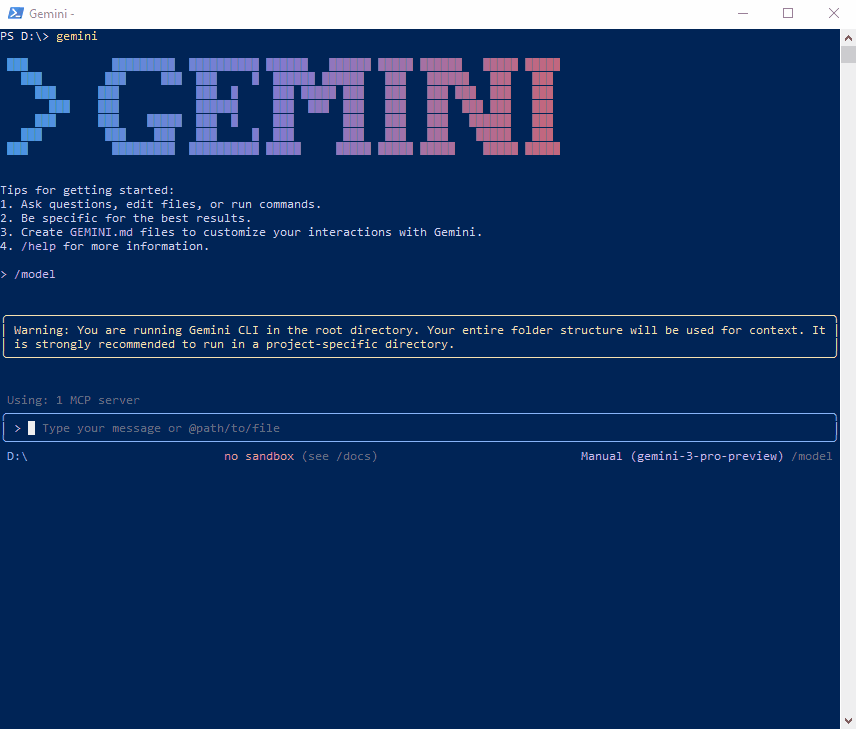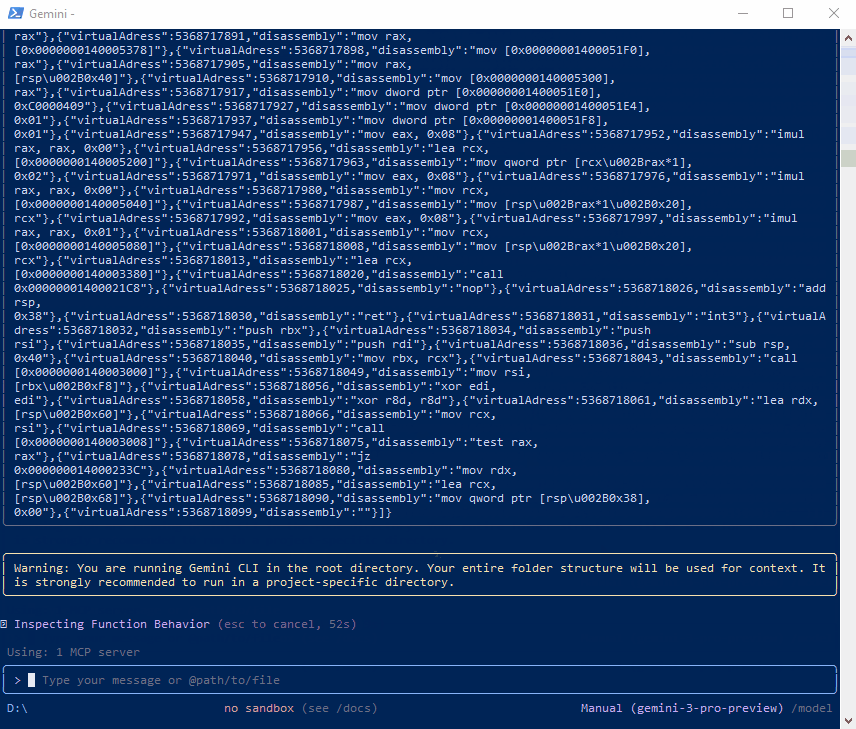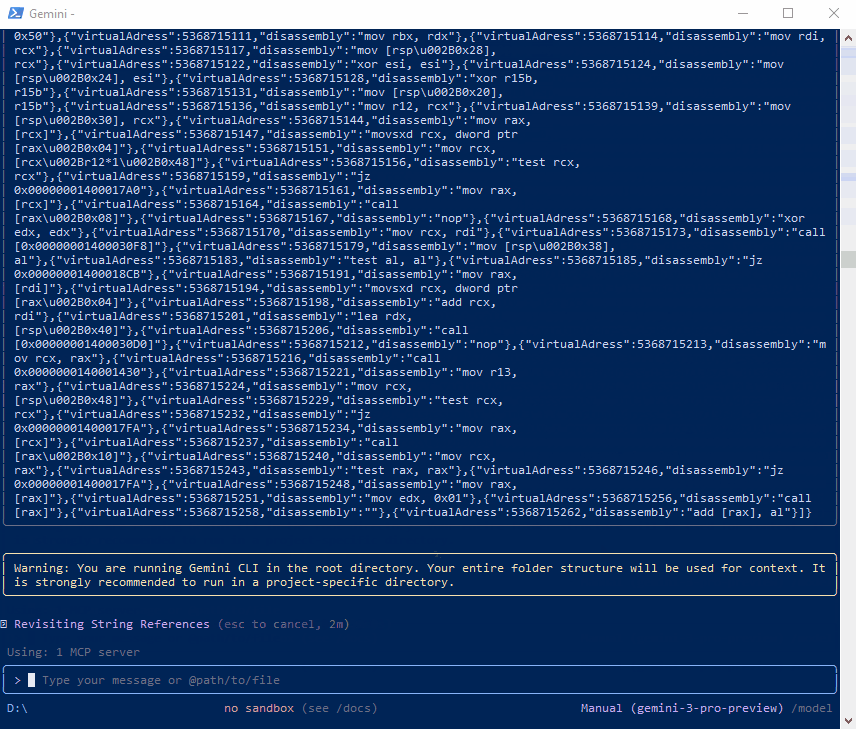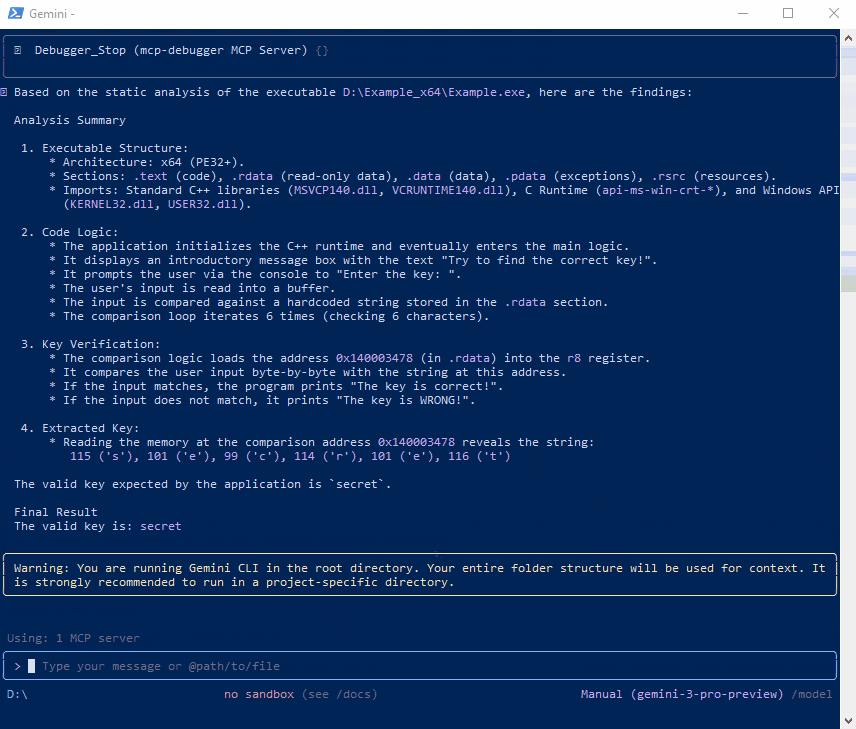 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
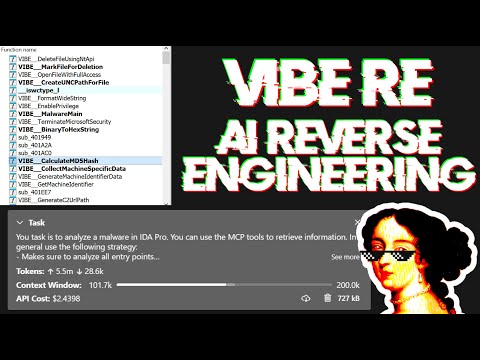 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 ant4g0nist/lisa.py
LLDB MCP Integration + other helpful commands
 lt-asset/resym
For our CCS24 paper 🏆 "ReSym: Harnessing LLMs to Recover Variable and Data Structure Symbols from Stripped Binaries" by Danning Xie, Zhuo Zhang, Nan…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.