

unidbg
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
ai-assisted-reversingandroid-securitybinary-analysis+5
5.3k15h 53m ago
zhkl0228/unidbgAllows you to emulate an Android native library, and an experimental iOS emulation
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 nighthawkk/jnisleuth-mcp
Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)

 lauriewired/malimite
iOS and macOS Decompiler
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
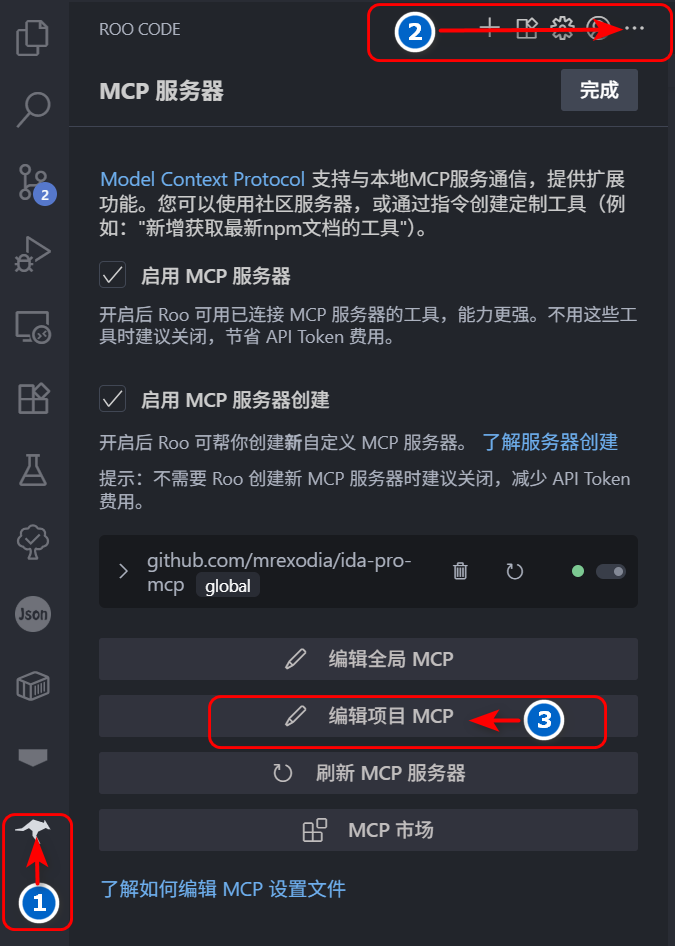 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…