
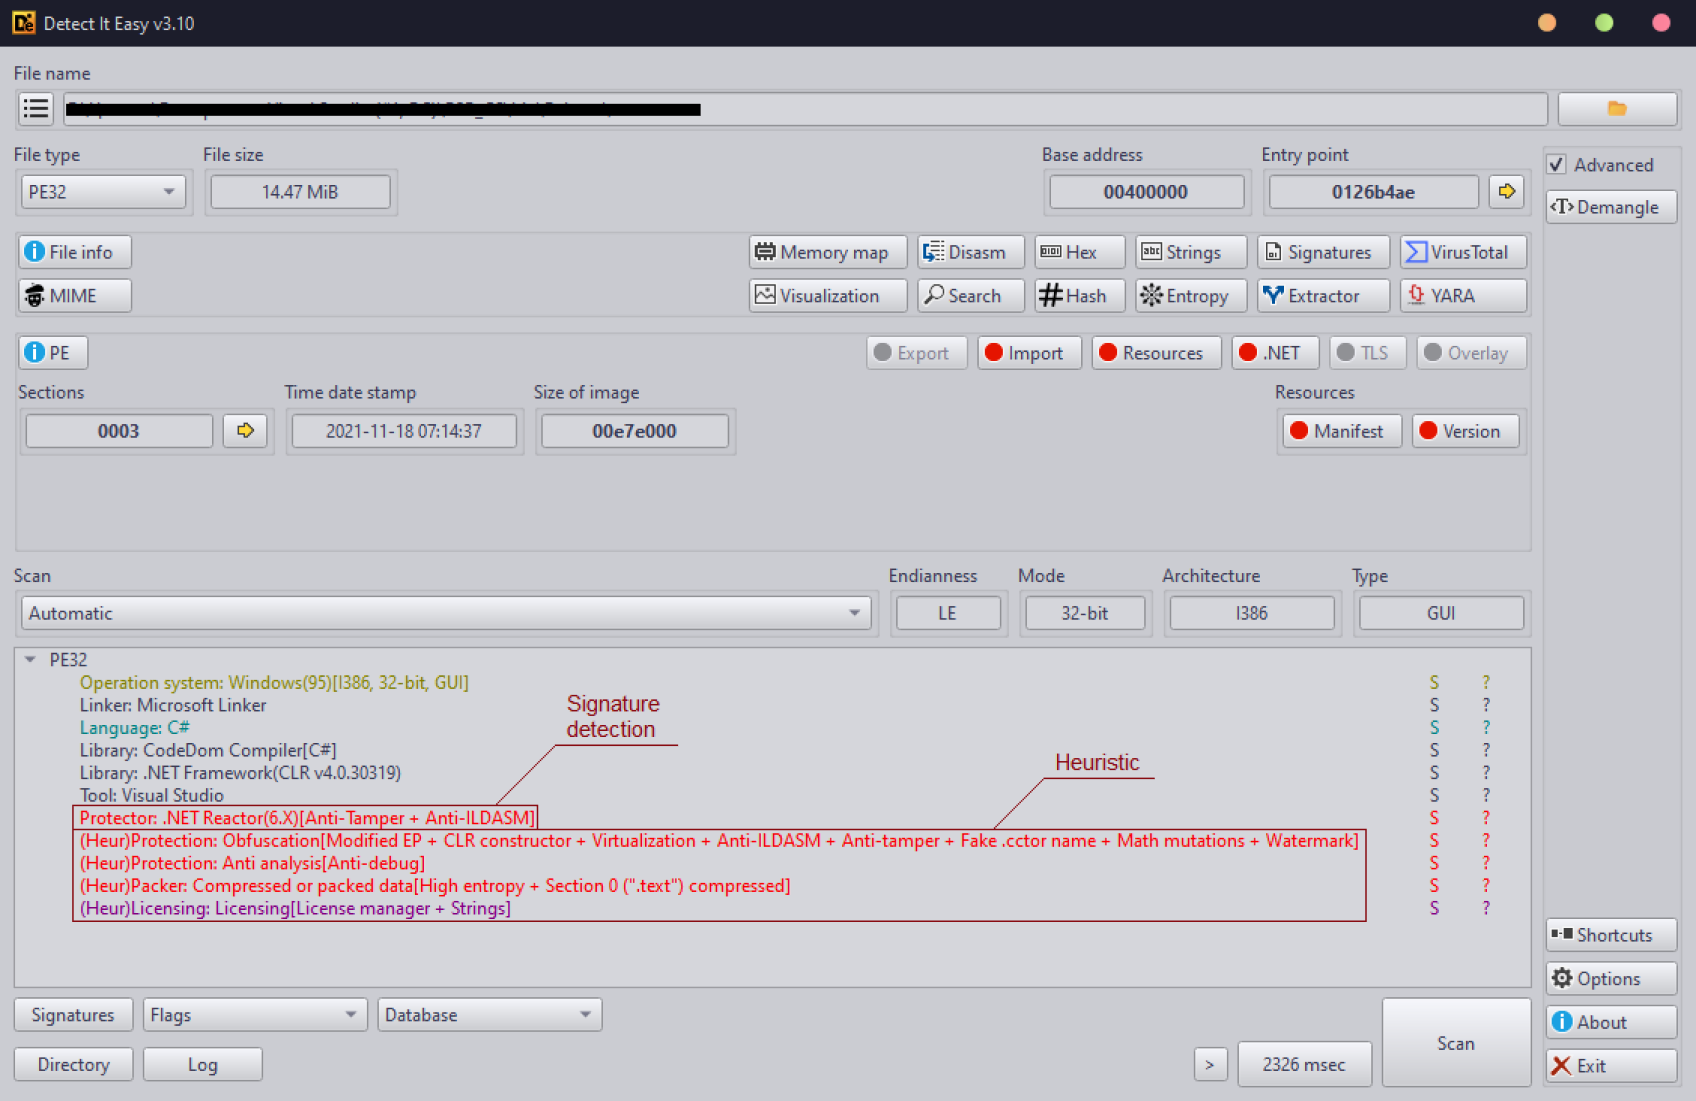
Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.5k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.
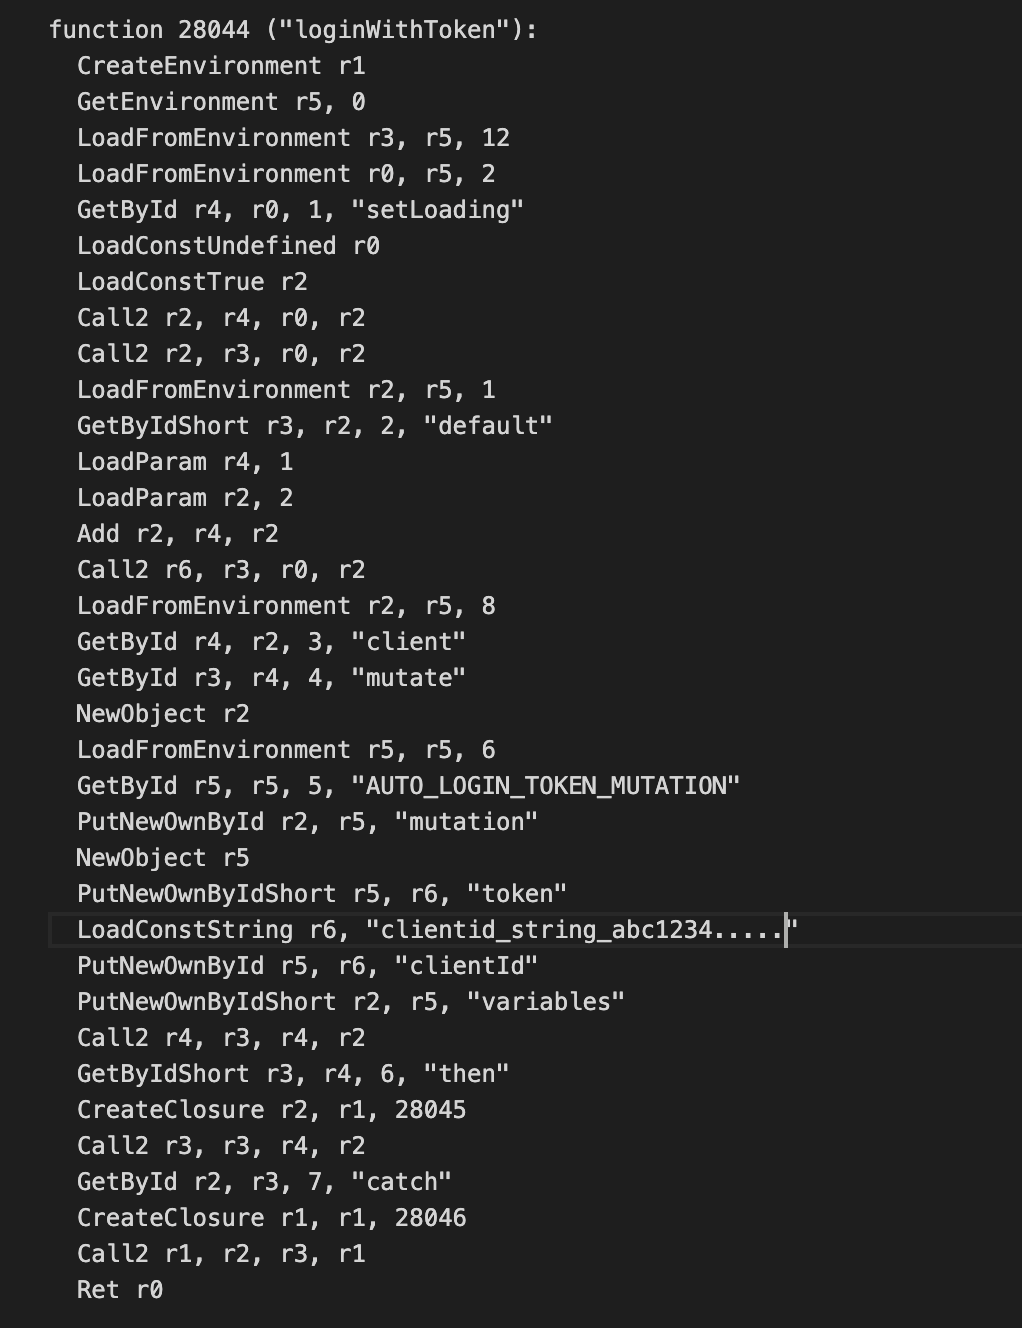 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 lauriewired/ghidramcp
MCP Server for Ghidra
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
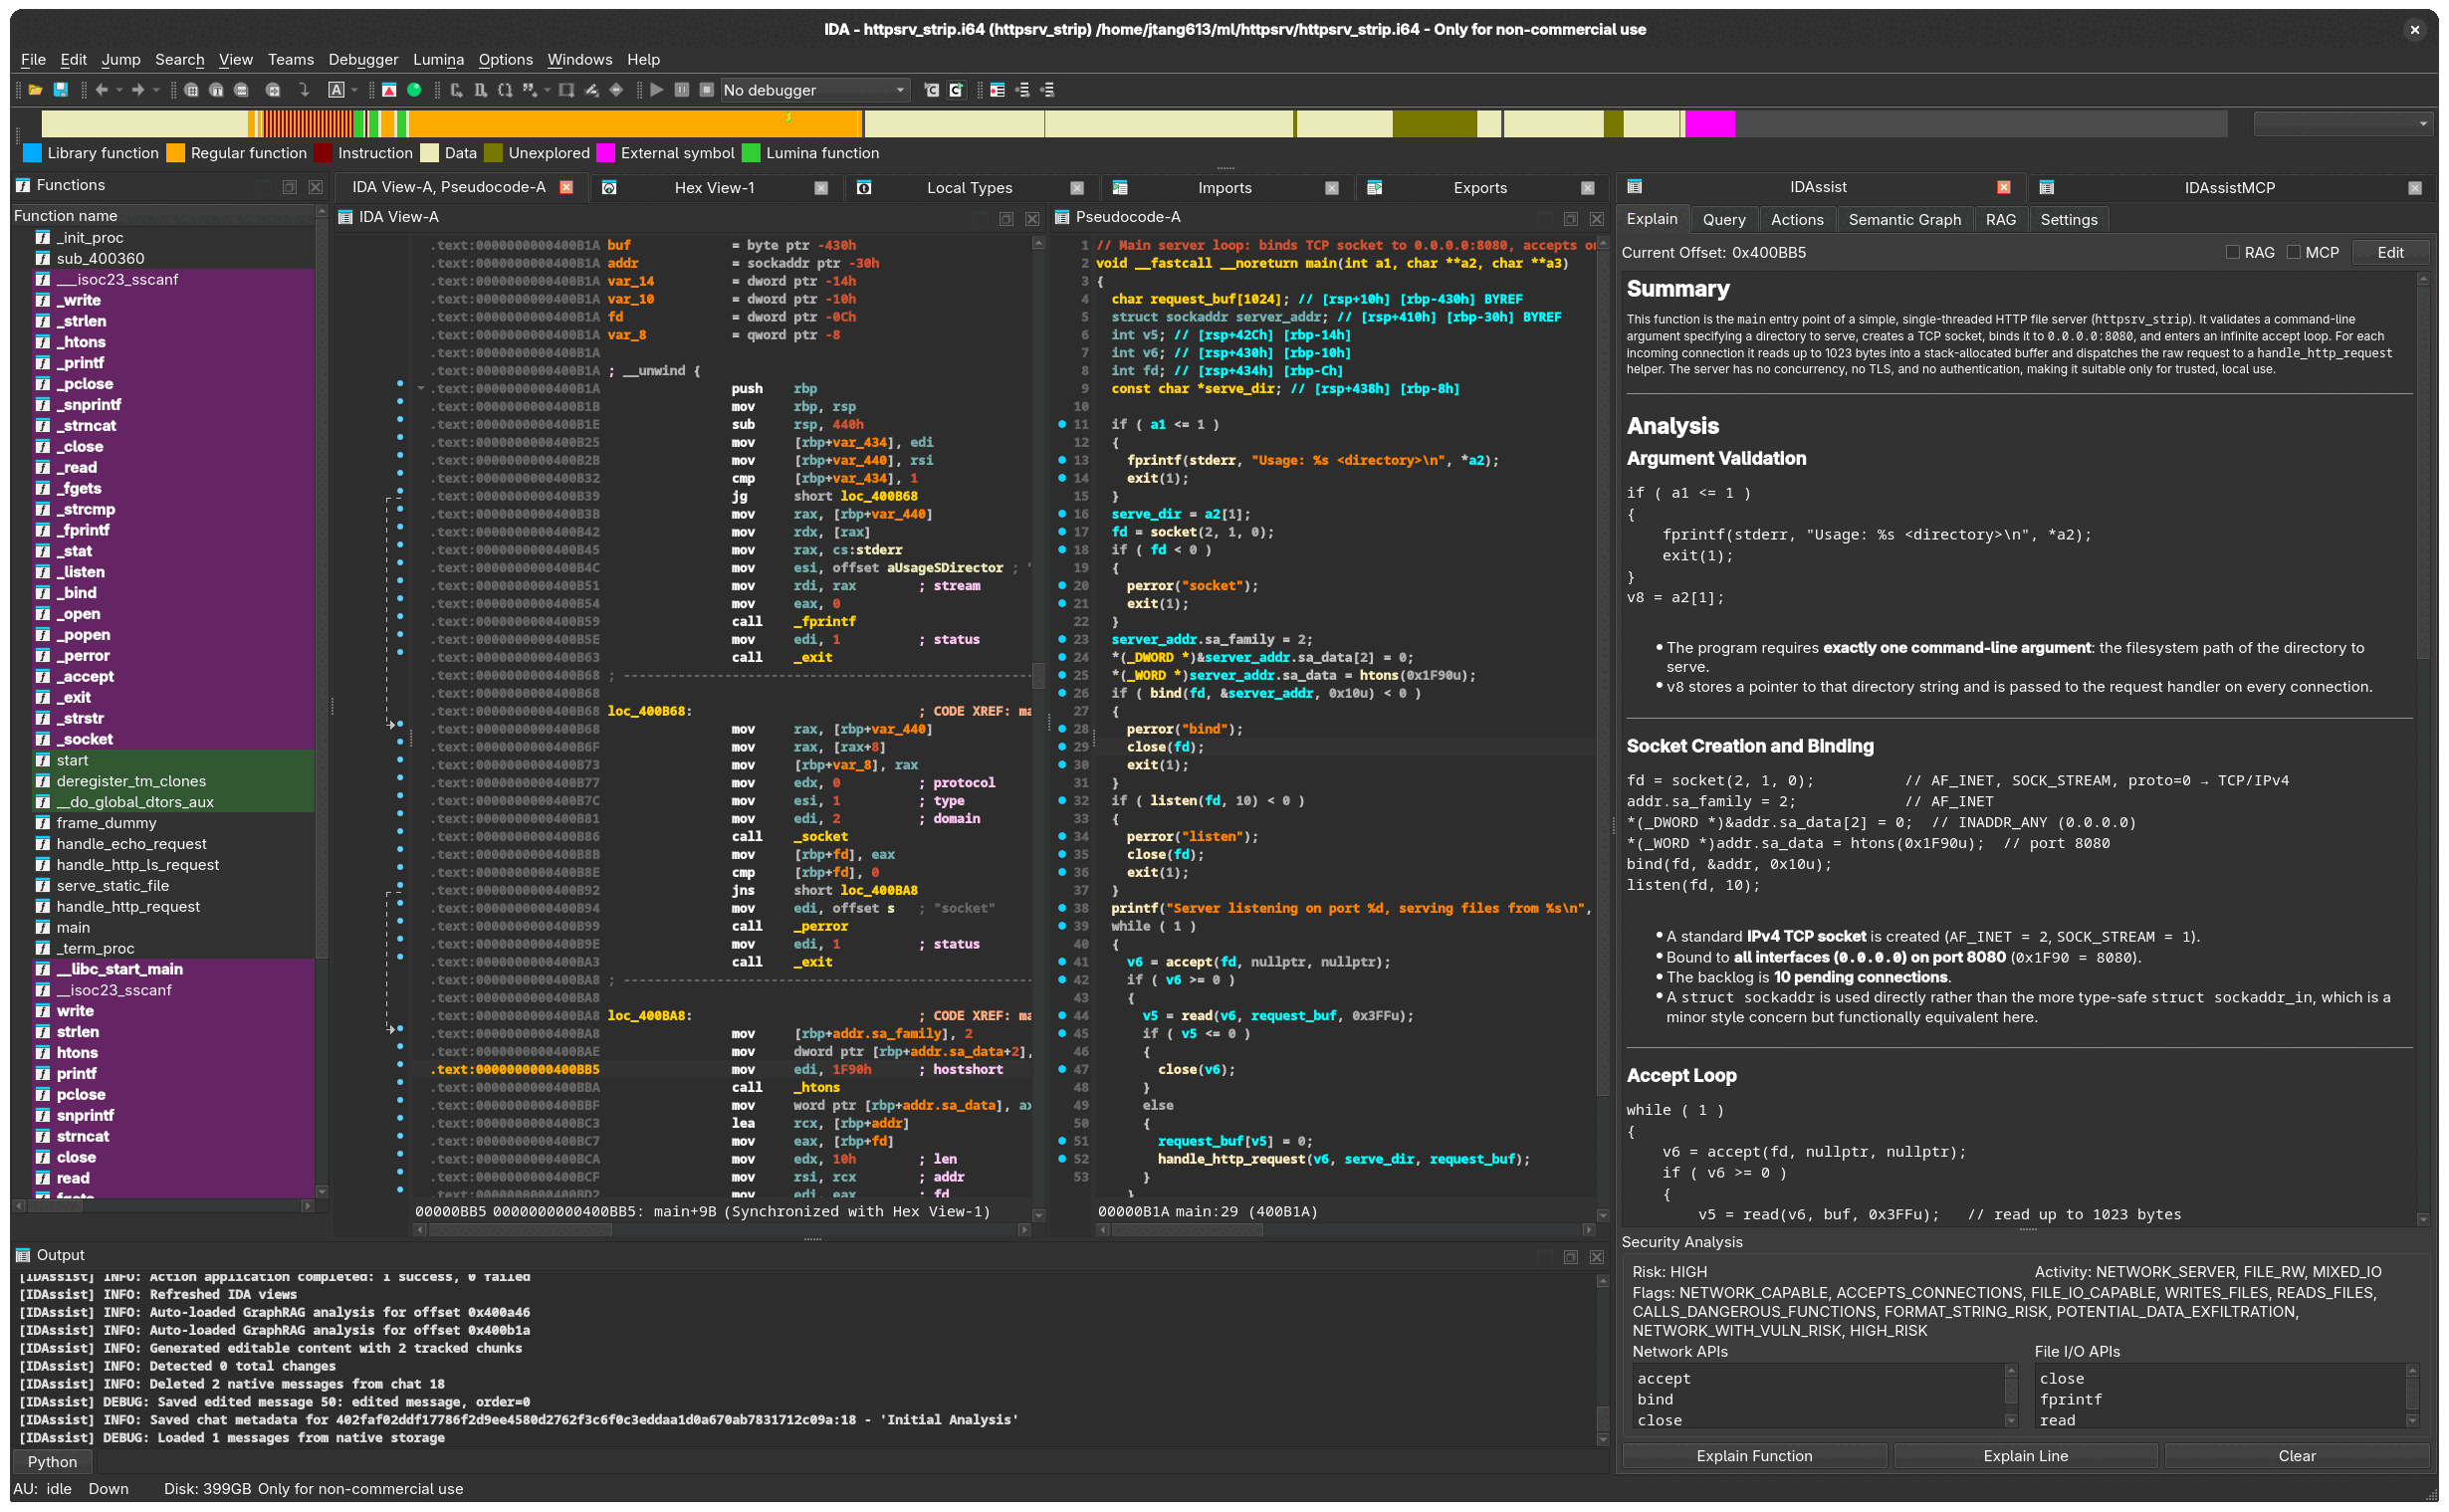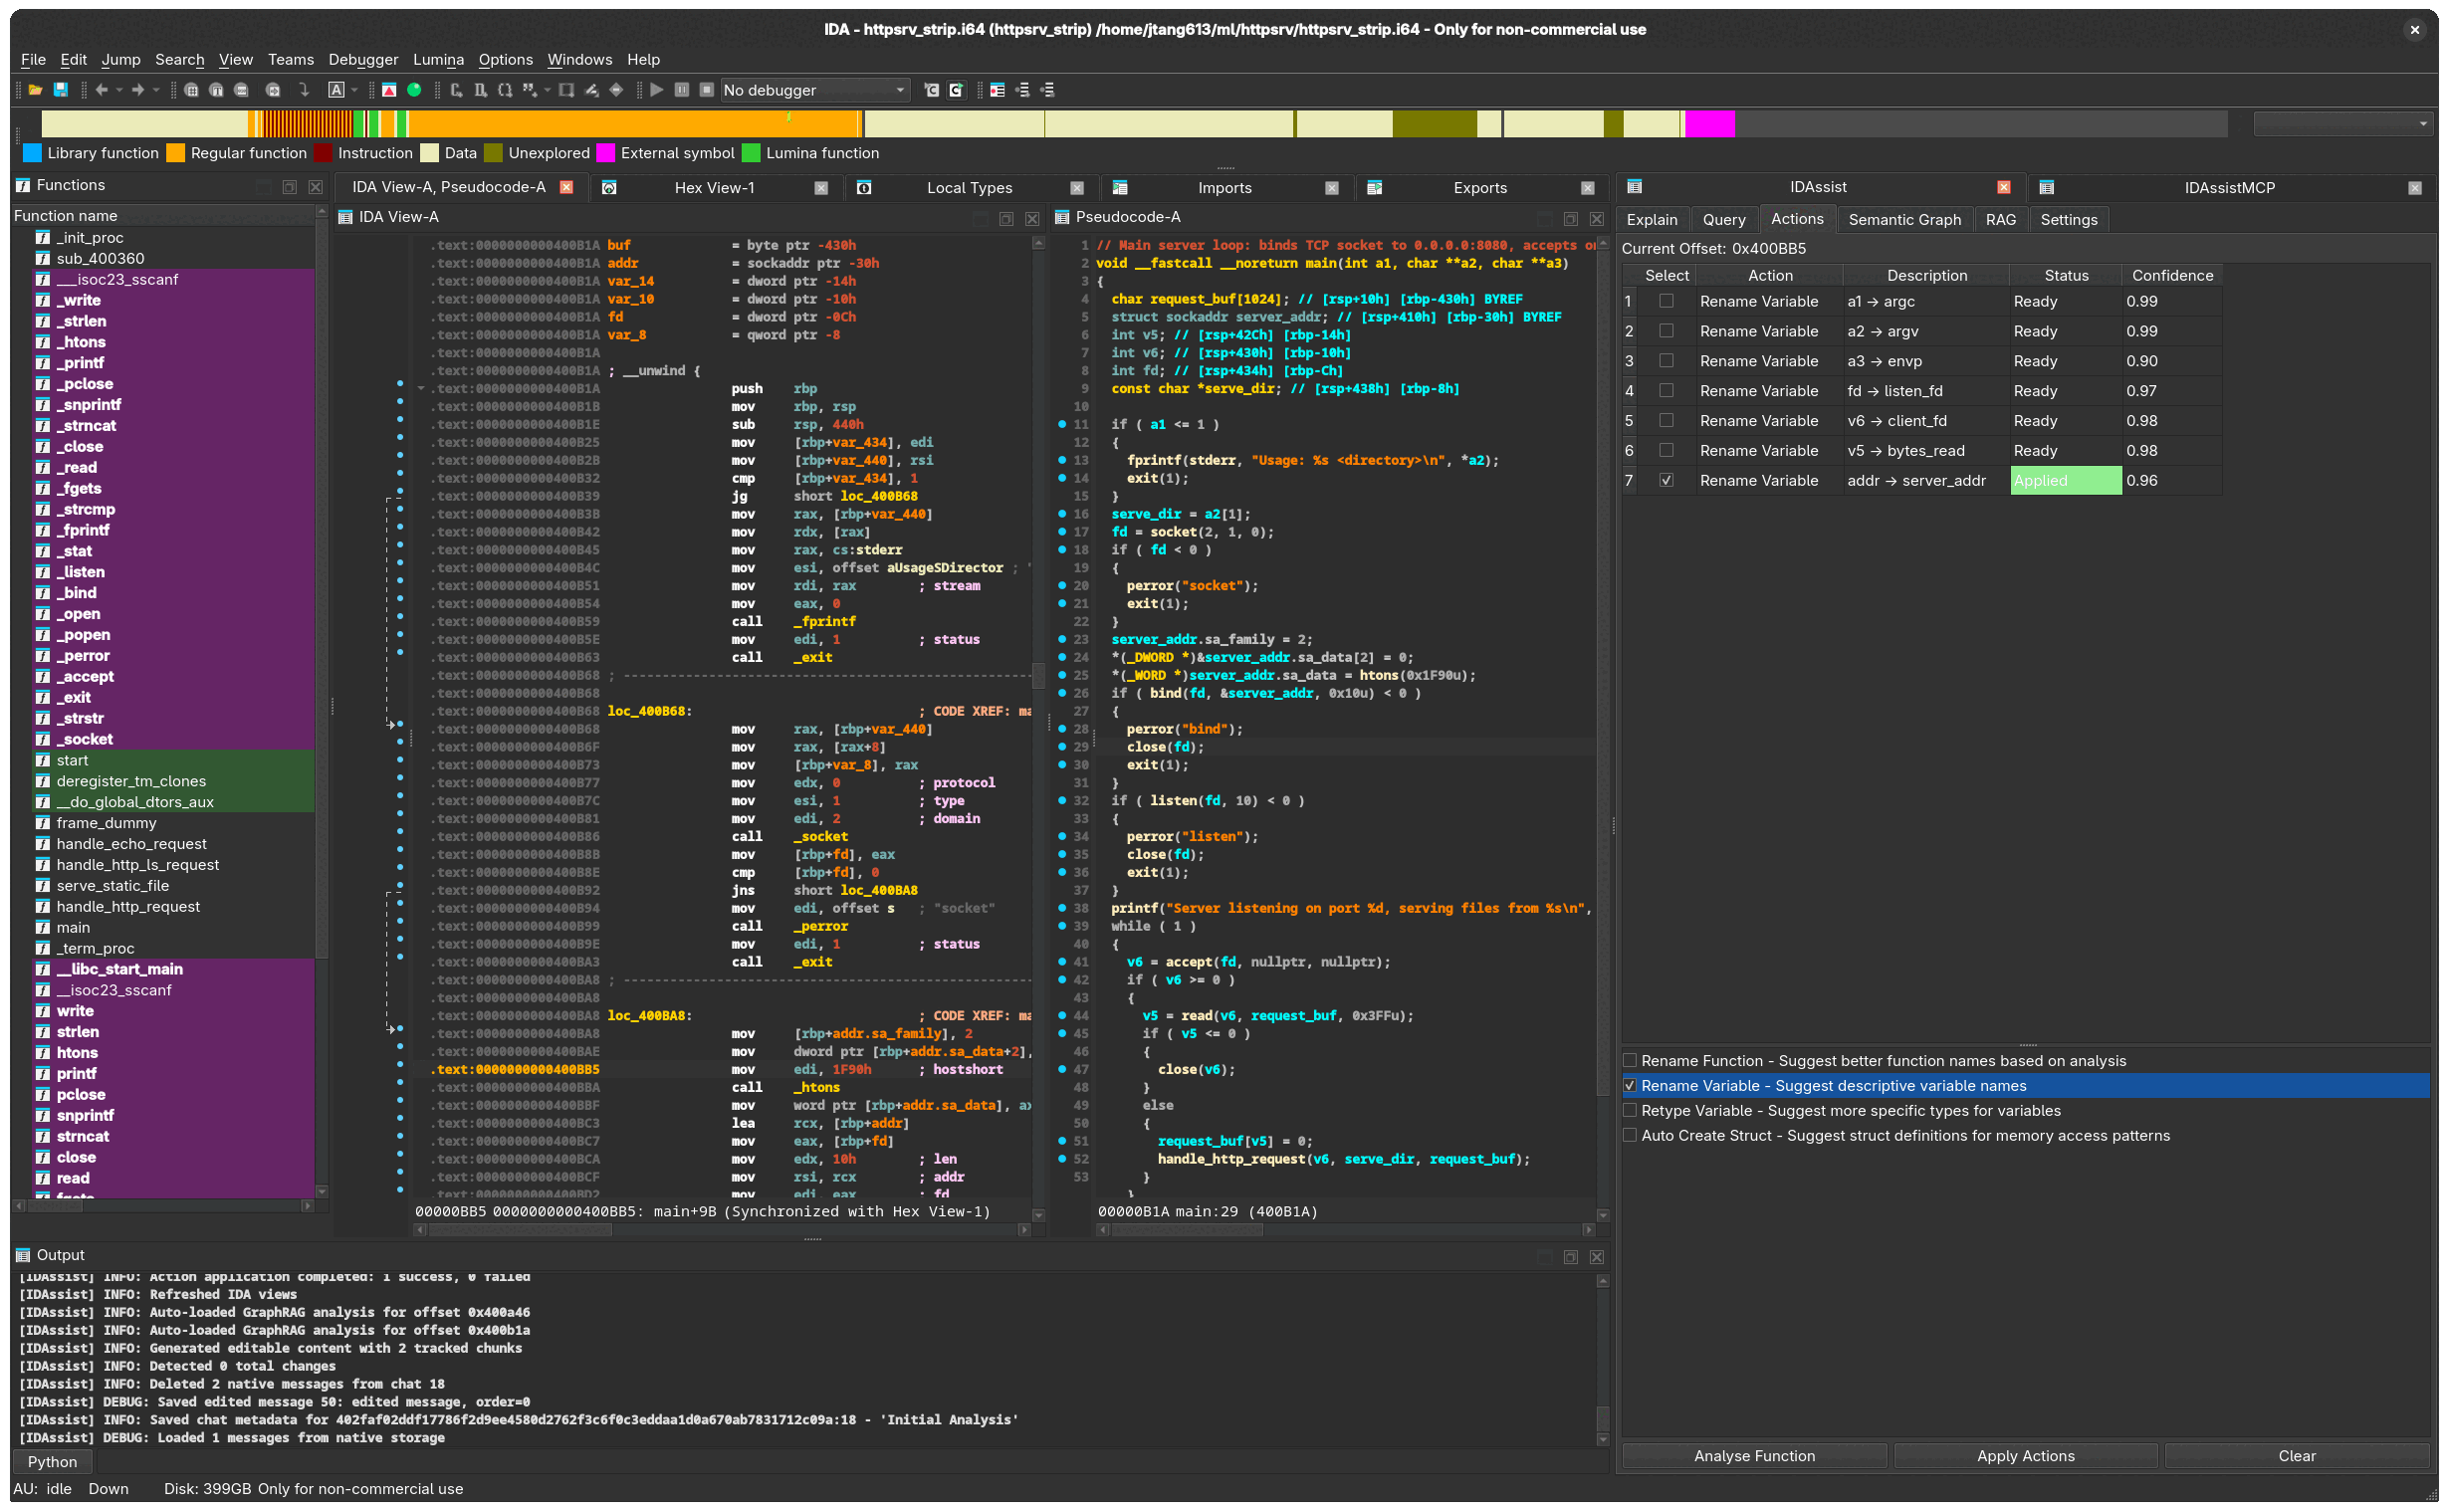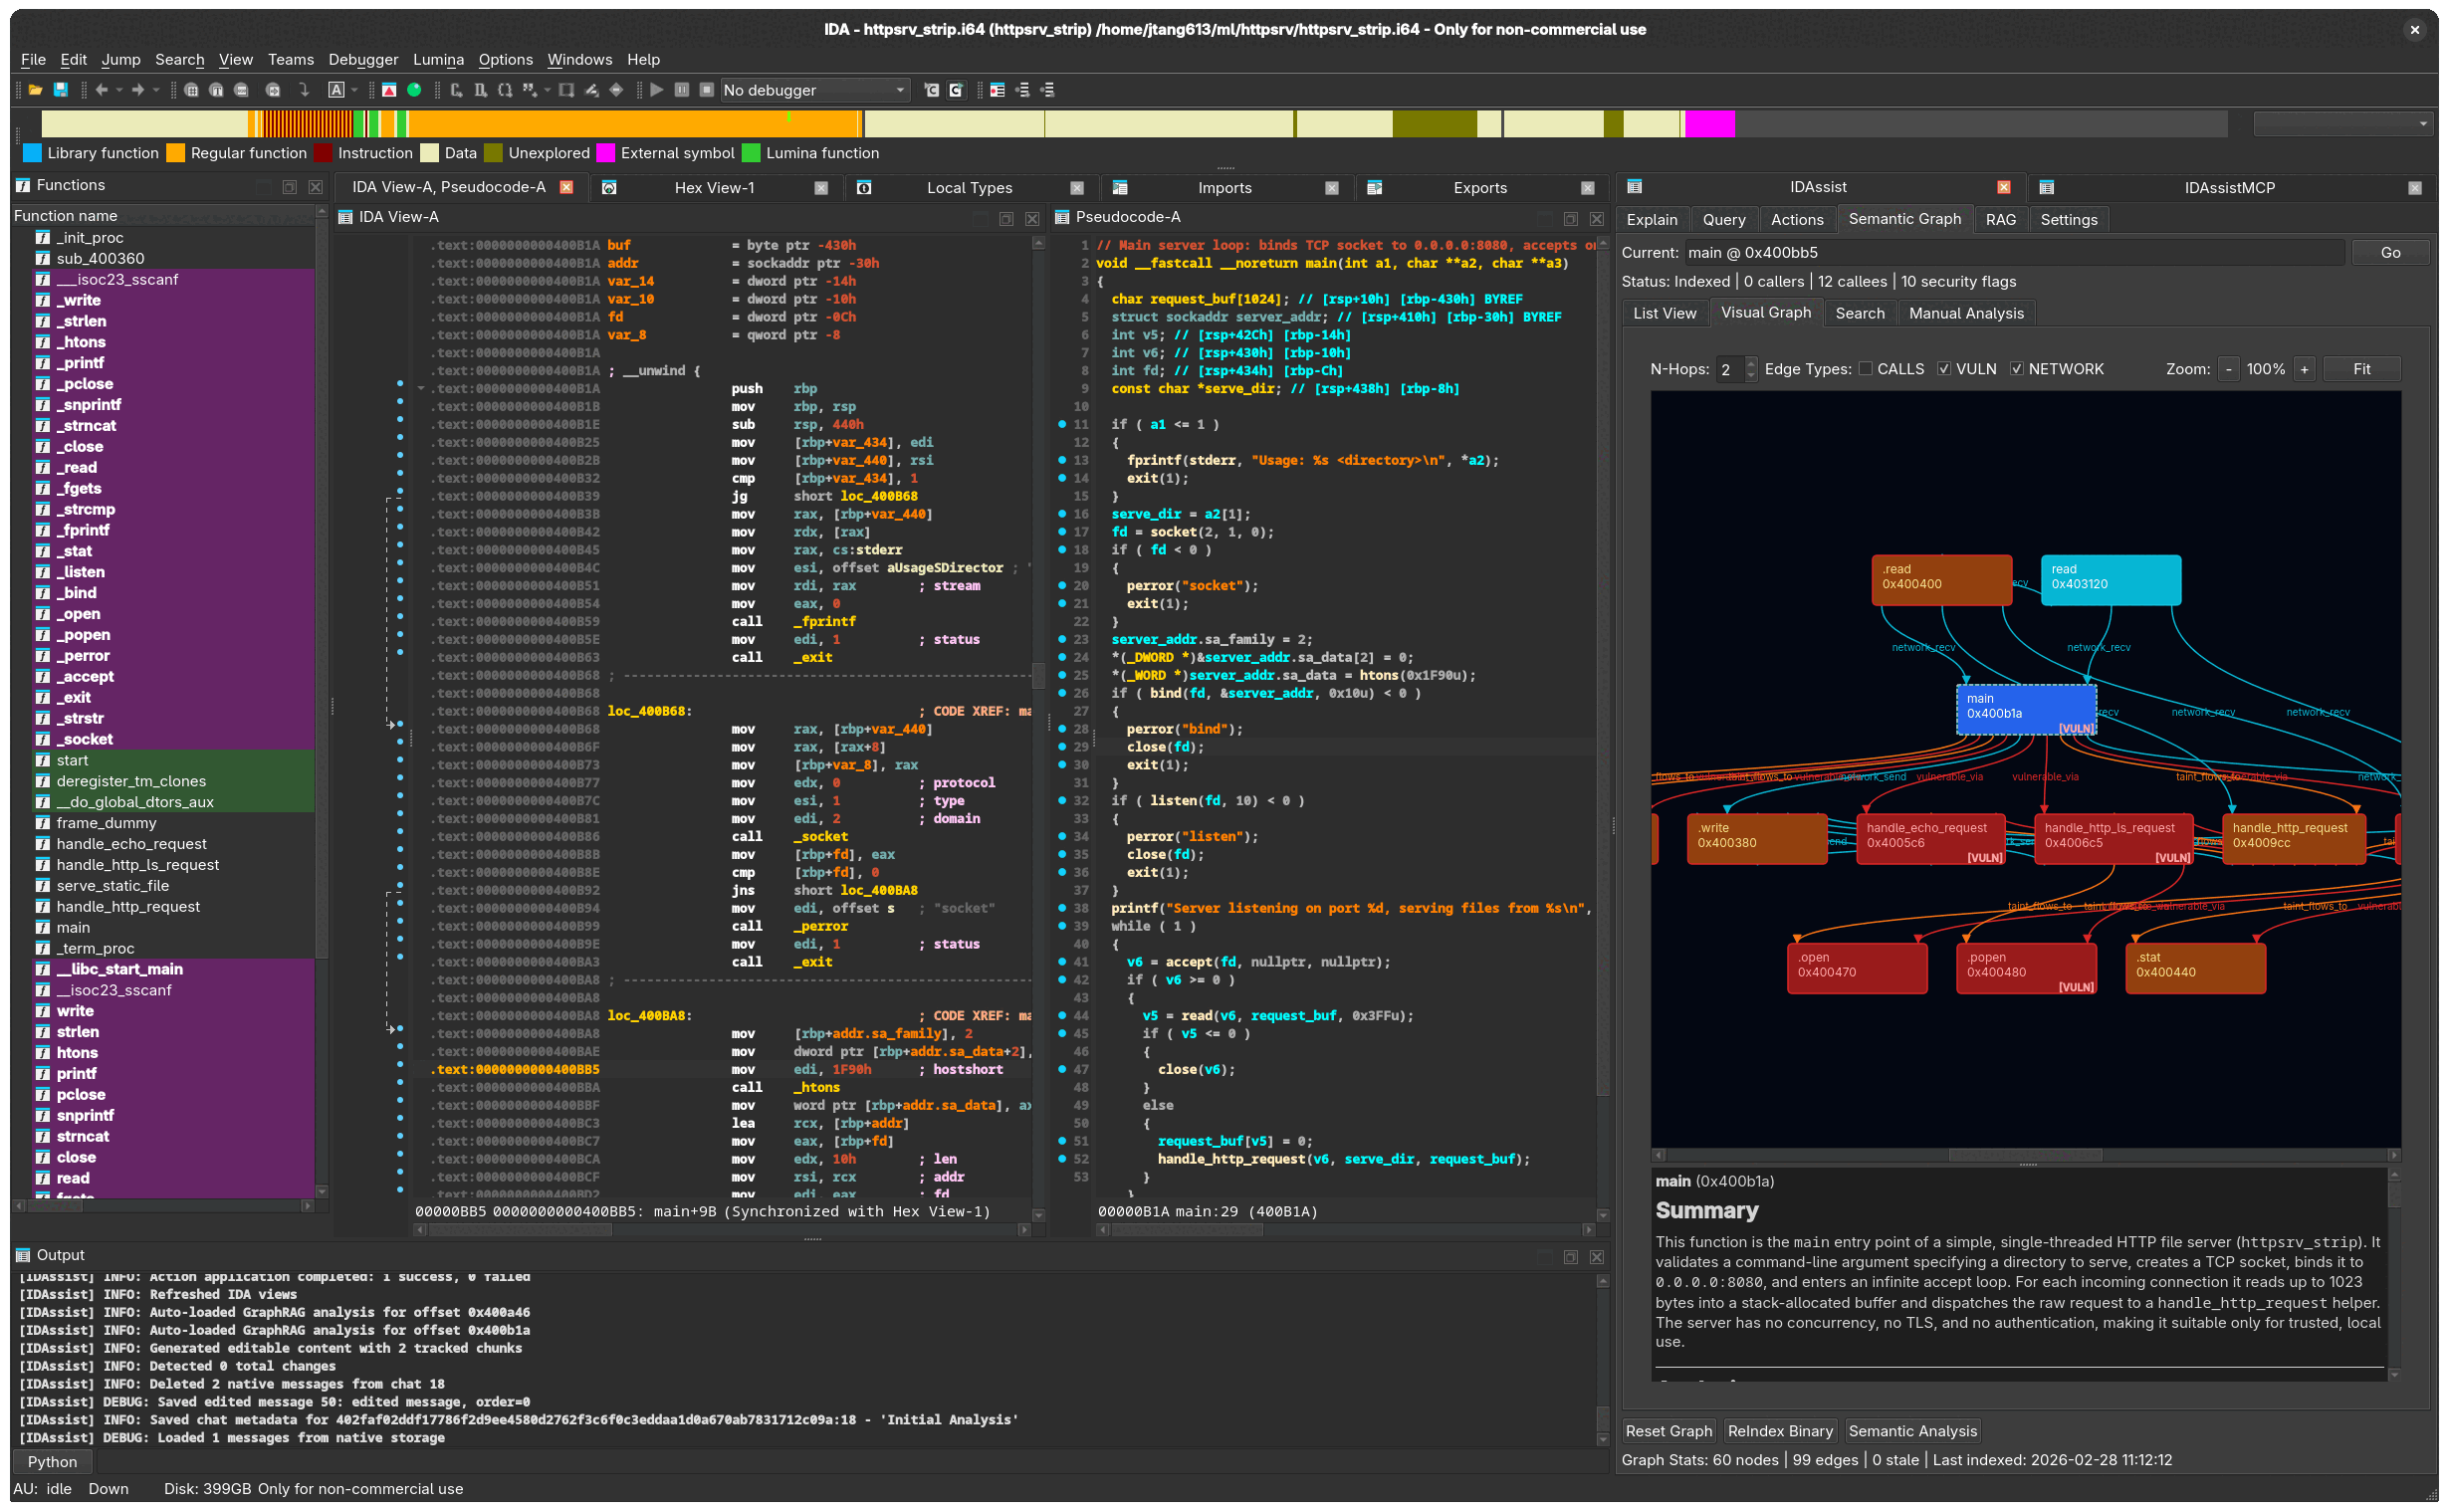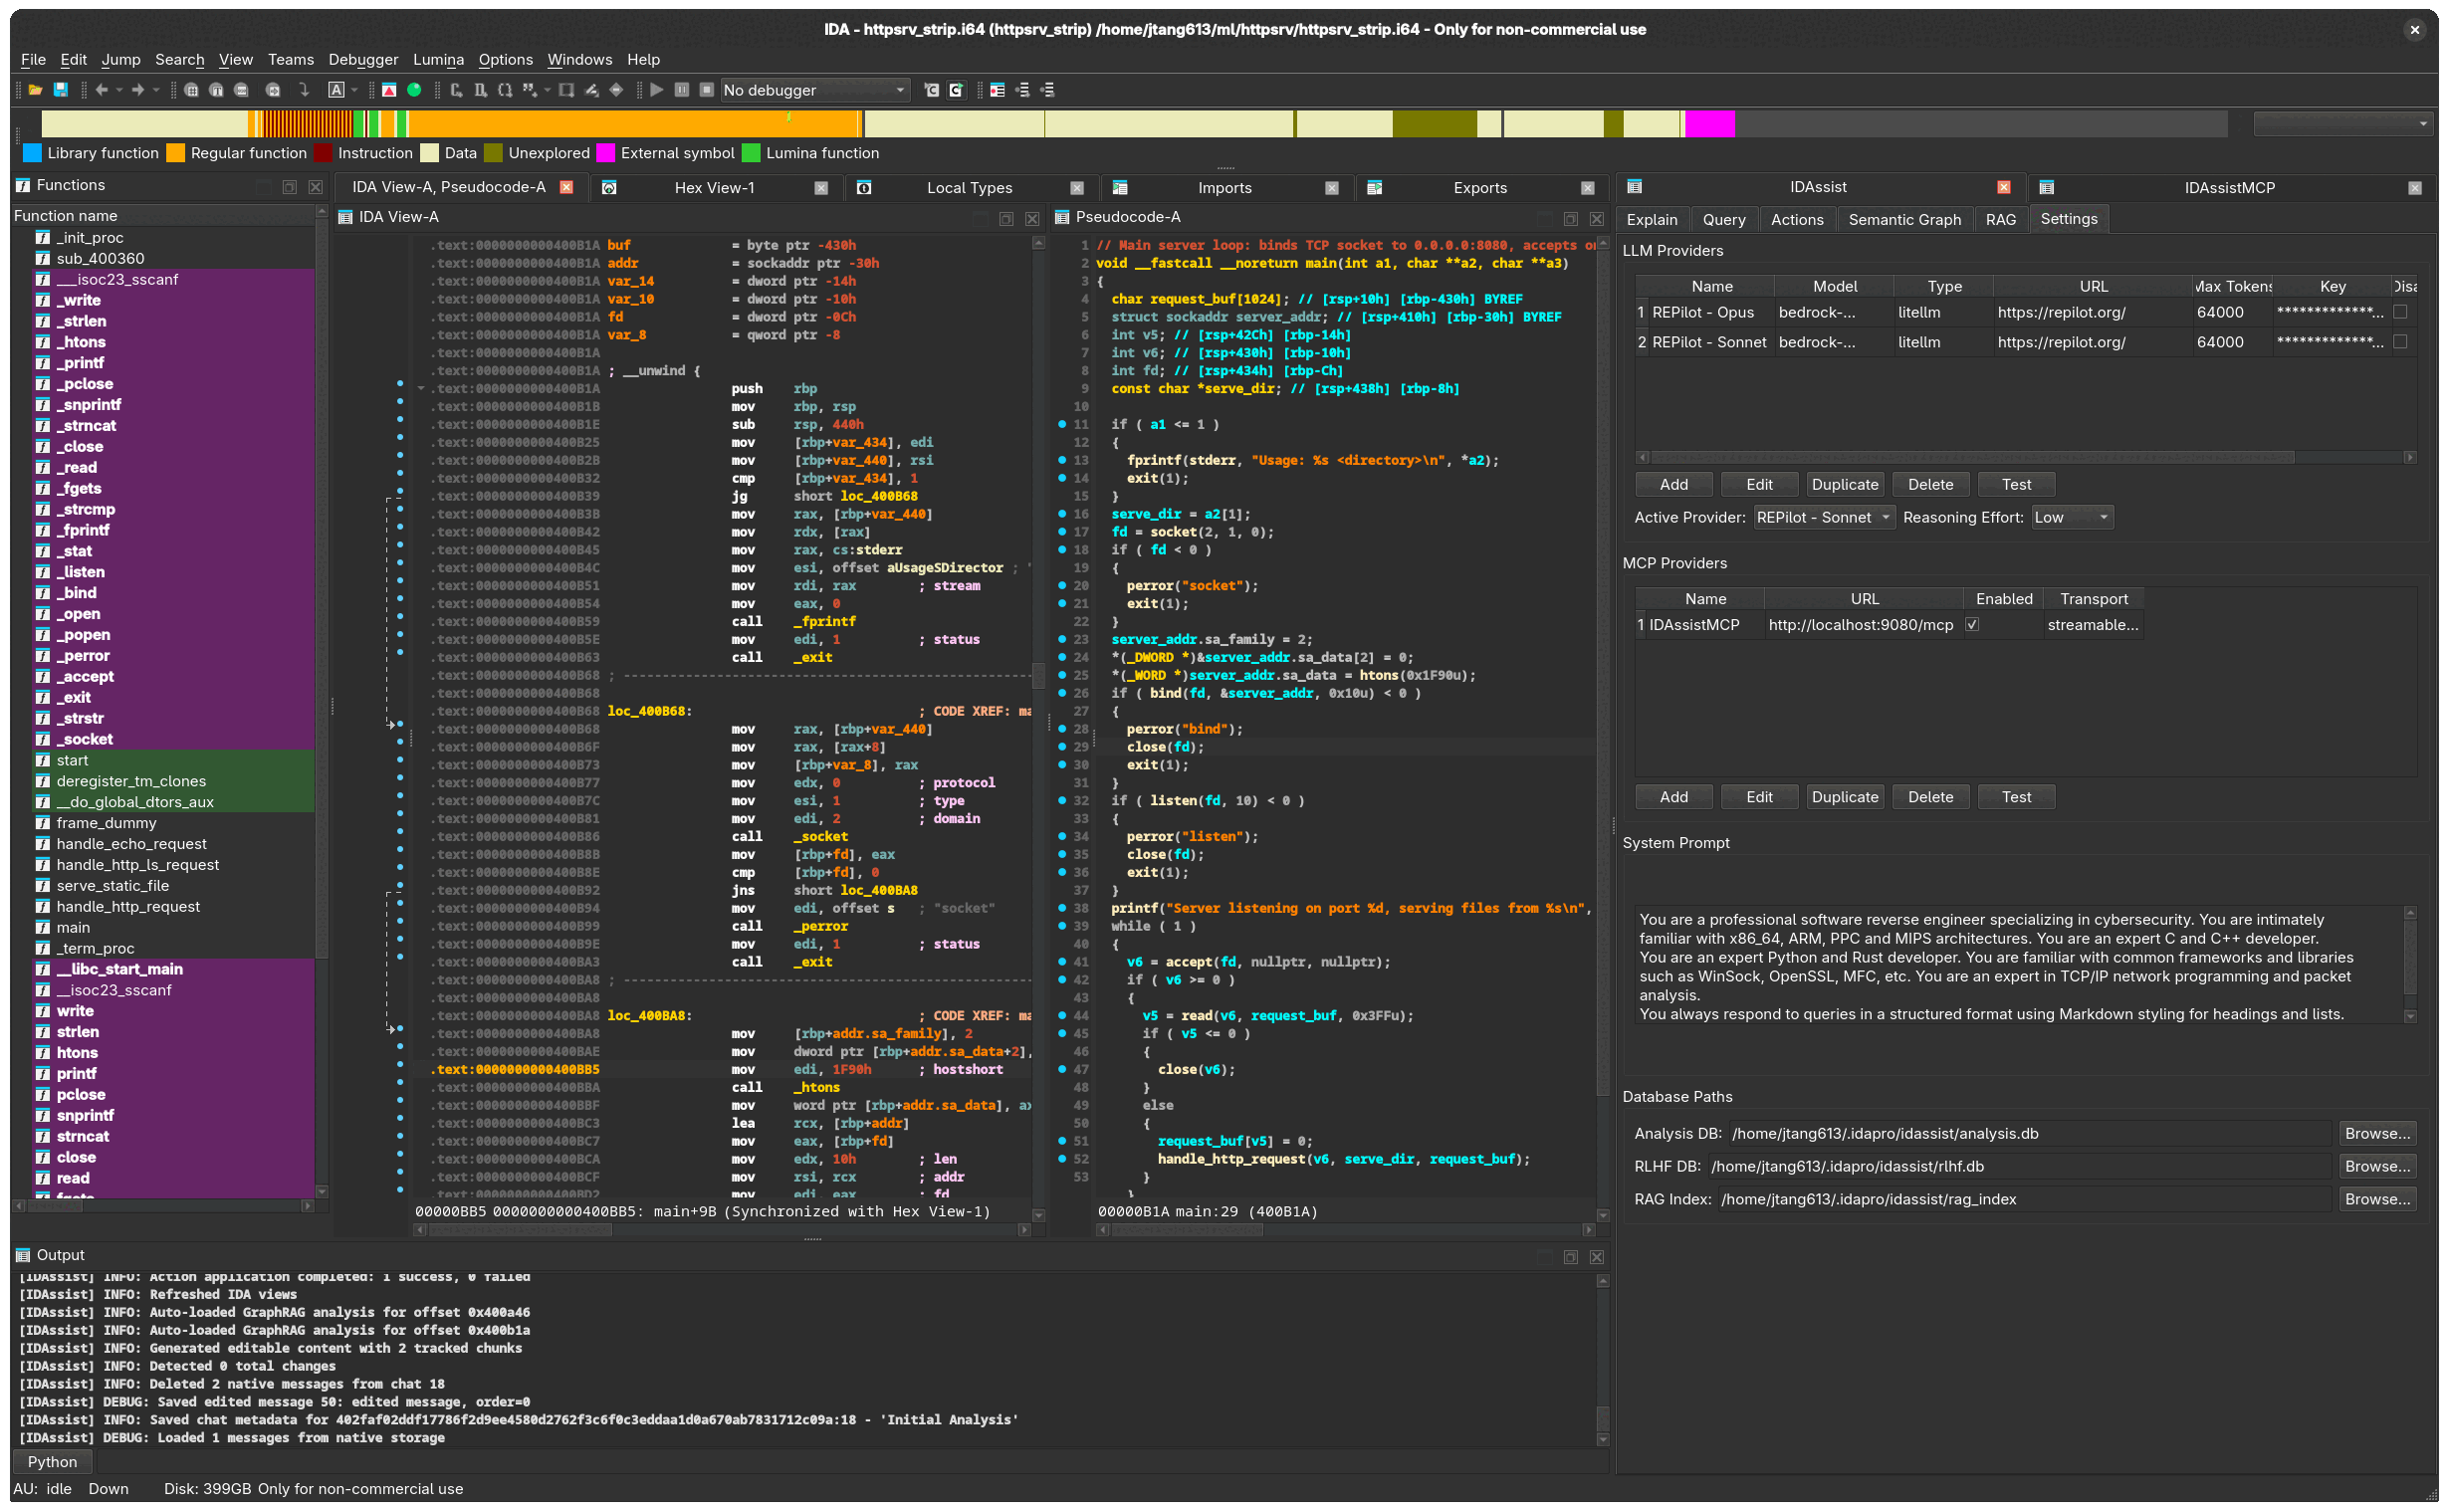 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 allthingsida/idasql
Vibe Reverse Engineer with IDA SQL: An interface for IDA in SQL via live virtual tables
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
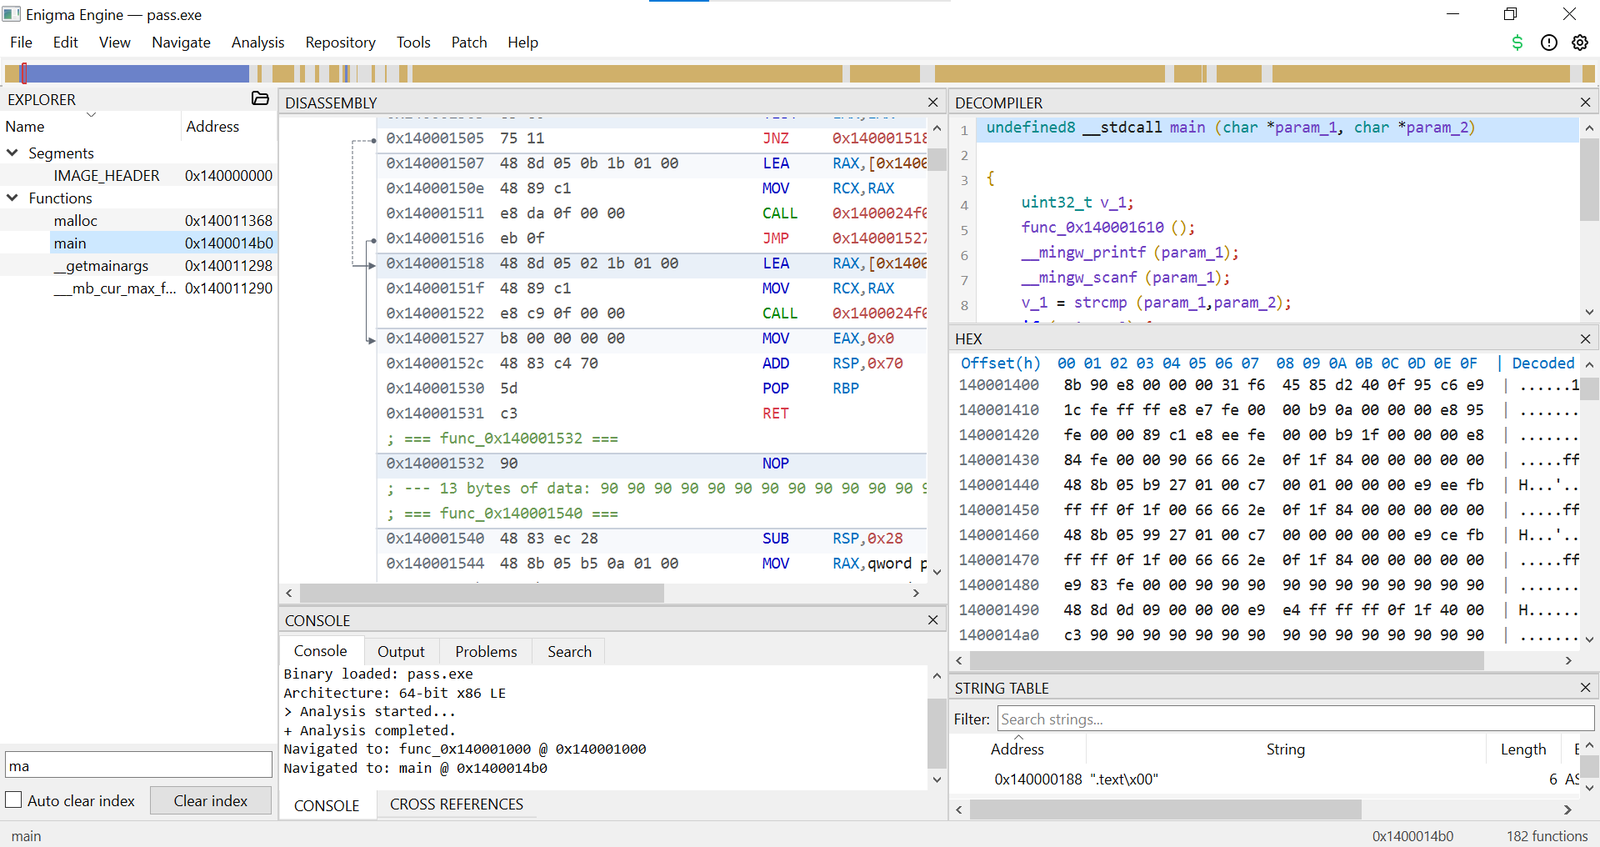 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
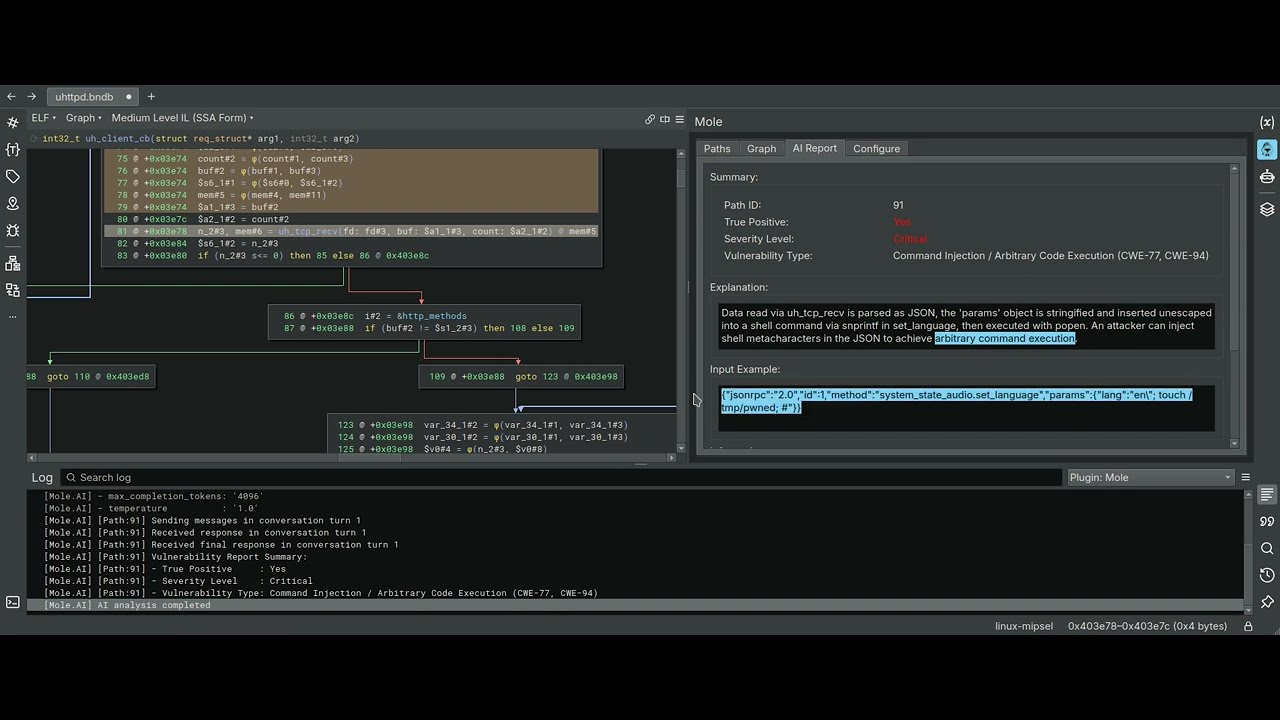 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
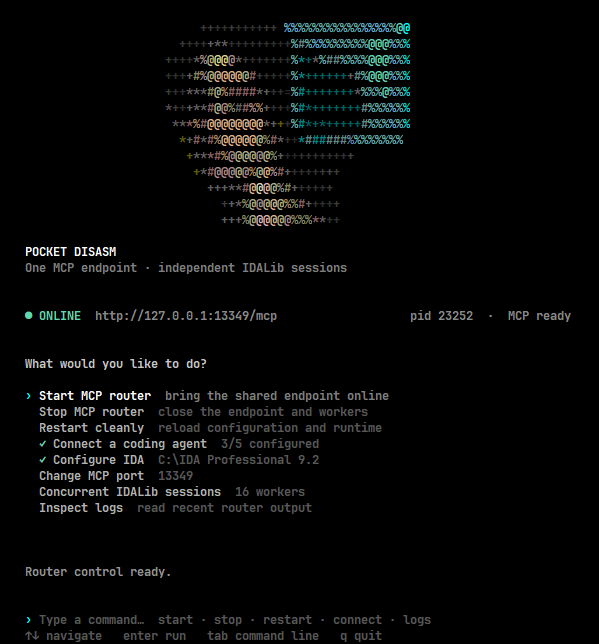 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
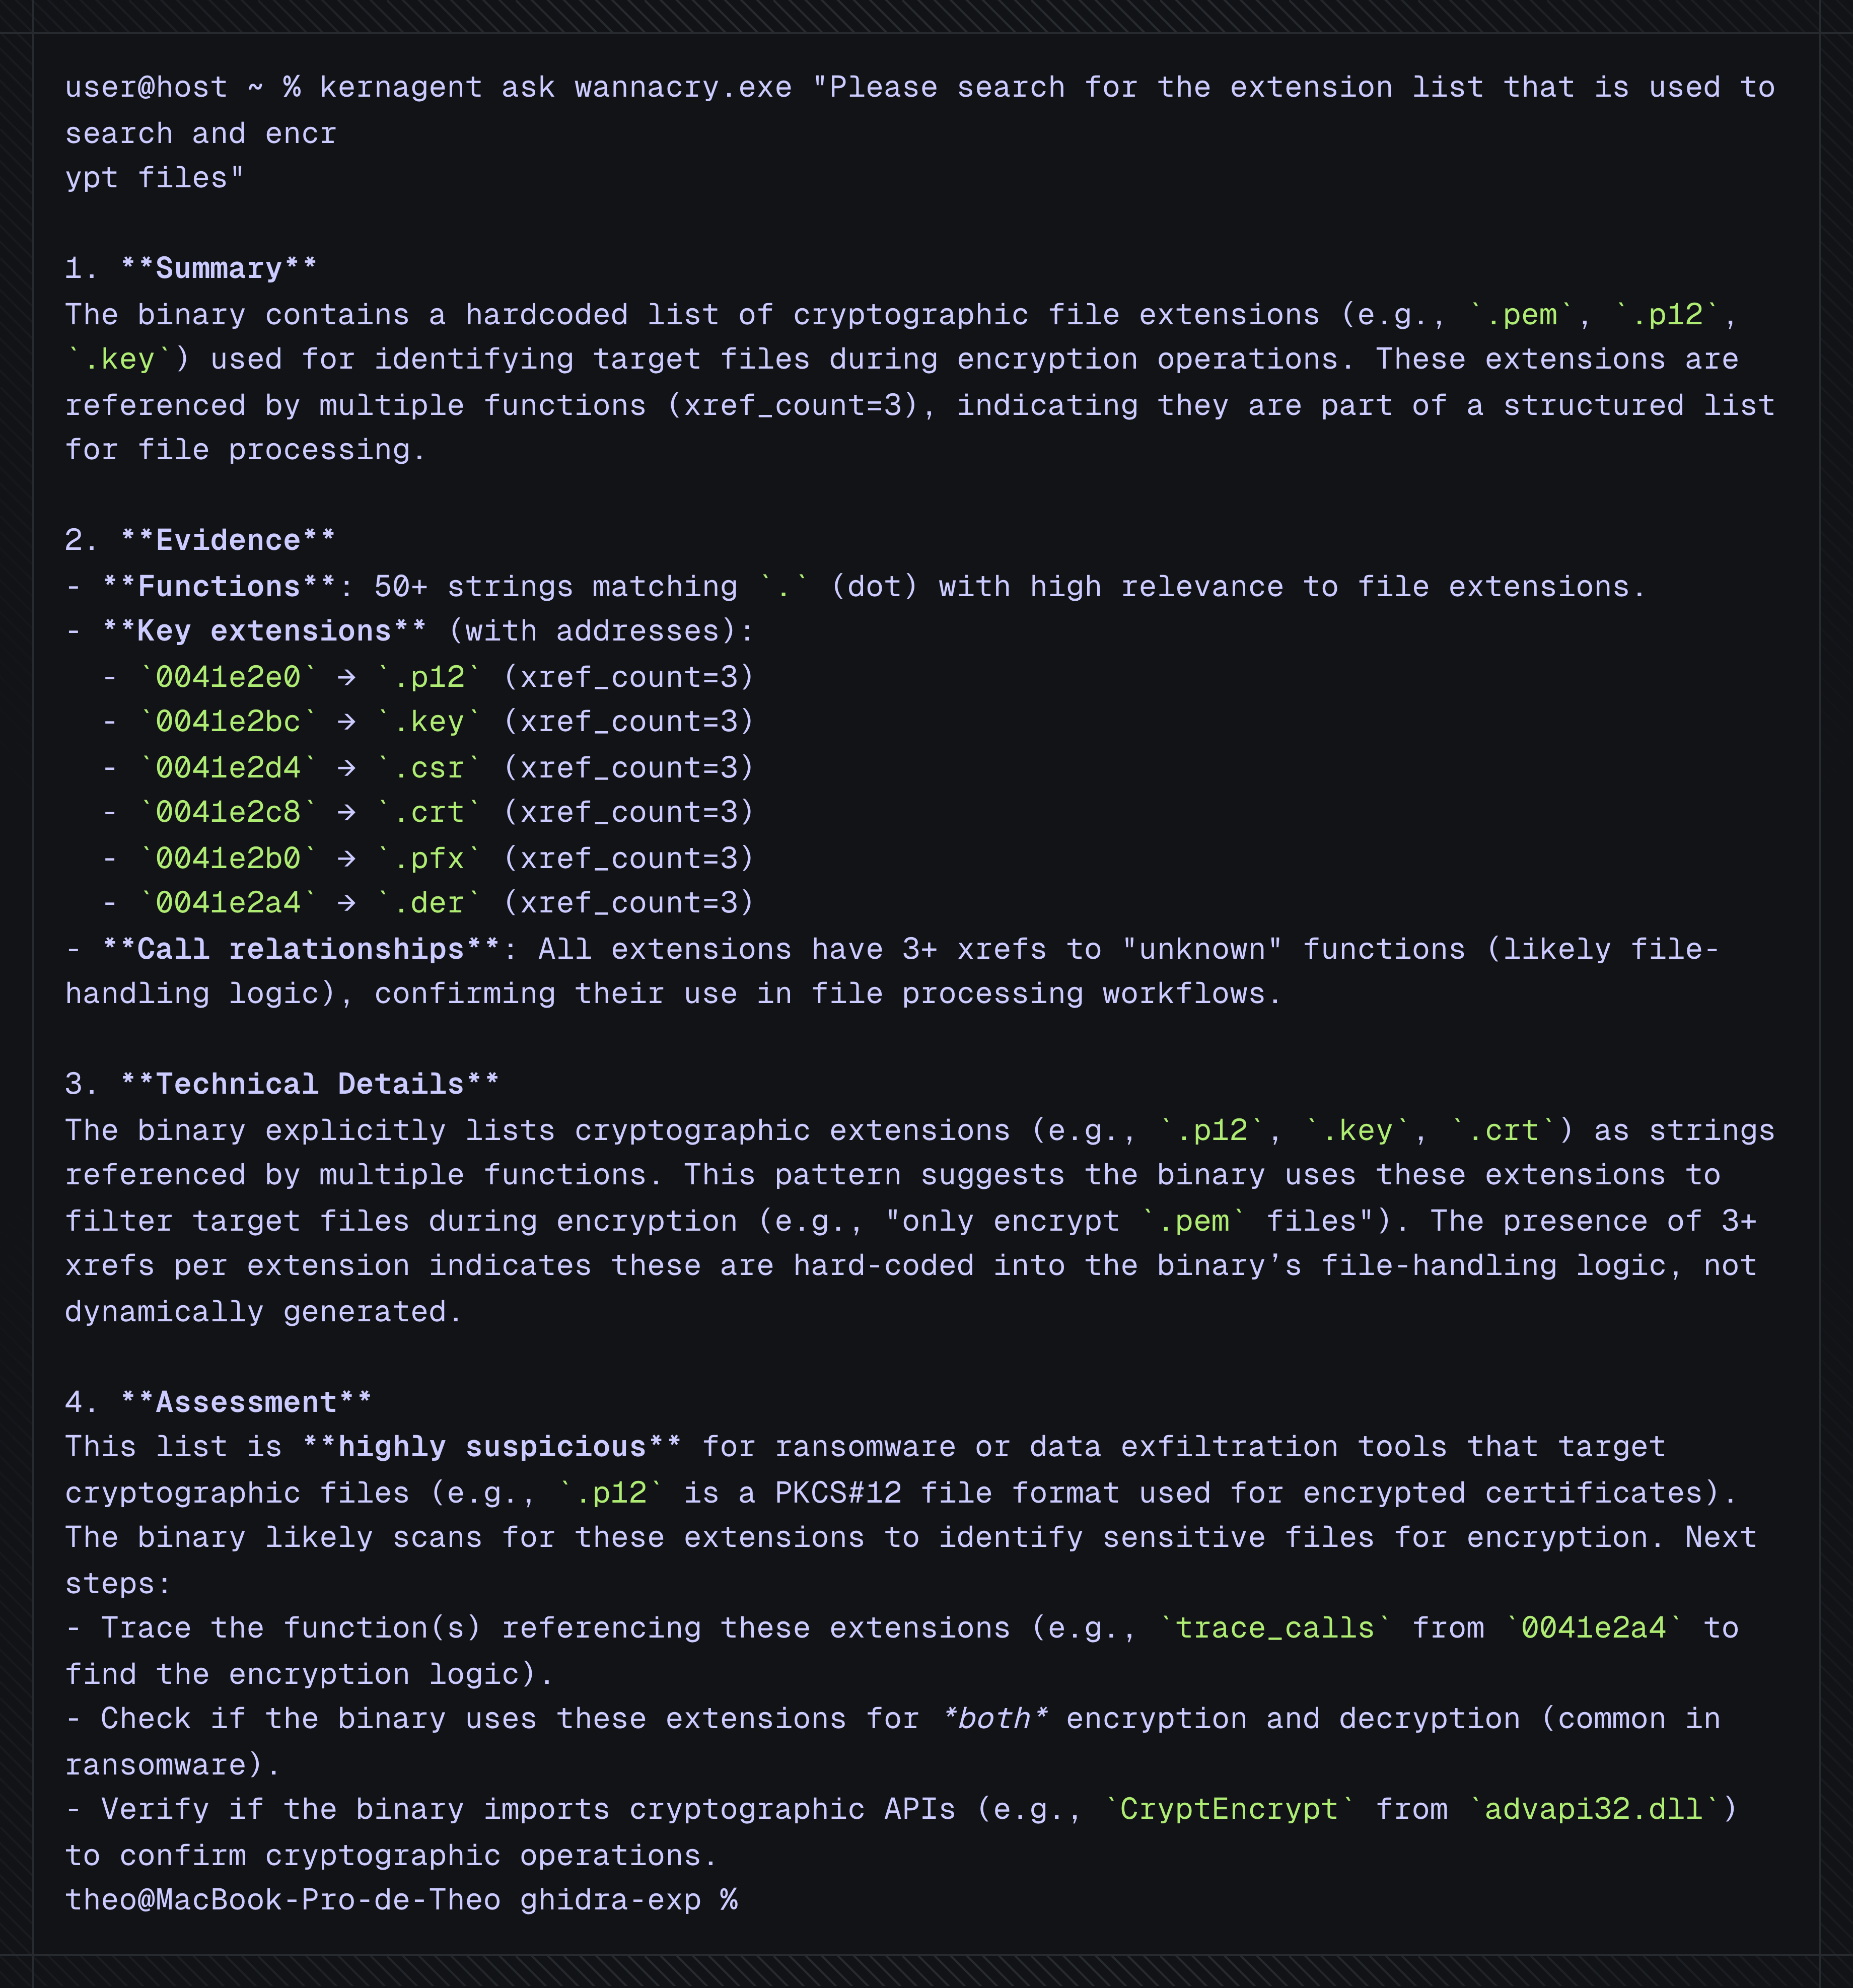 karib0u/kernagent
Headless AI agent for deterministic reverse engineering.
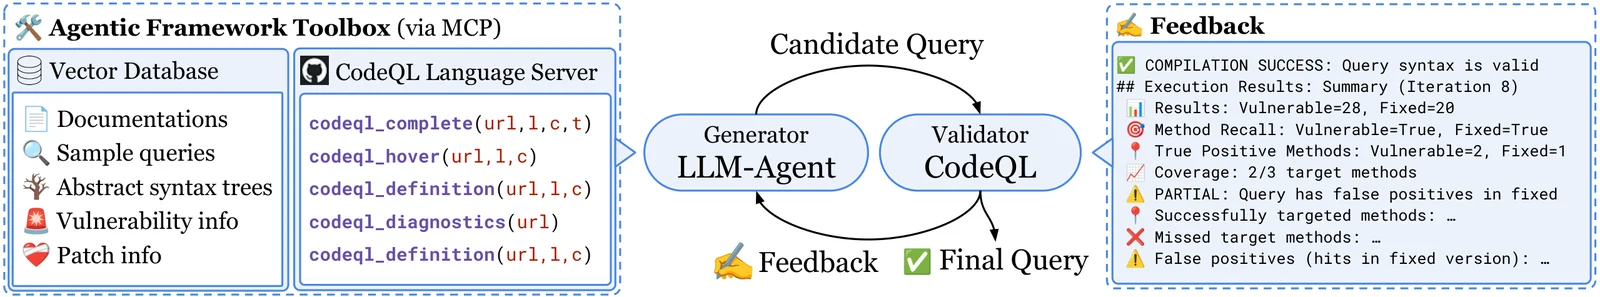 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries