CVE-2025-60719-AFD.SYS

Proof-of-concept and root-cause analysis of CVE-2025-60719, a use-after-free vulnerability in Windows afd.sys leading to local privilege escalation,…

Proof-of-concept and root-cause analysis of CVE-2025-60719, a use-after-free vulnerability in Windows afd.sys leading to local privilege escalation,…

AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.

UNIX-like reverse engineering framework and command-line toolset.

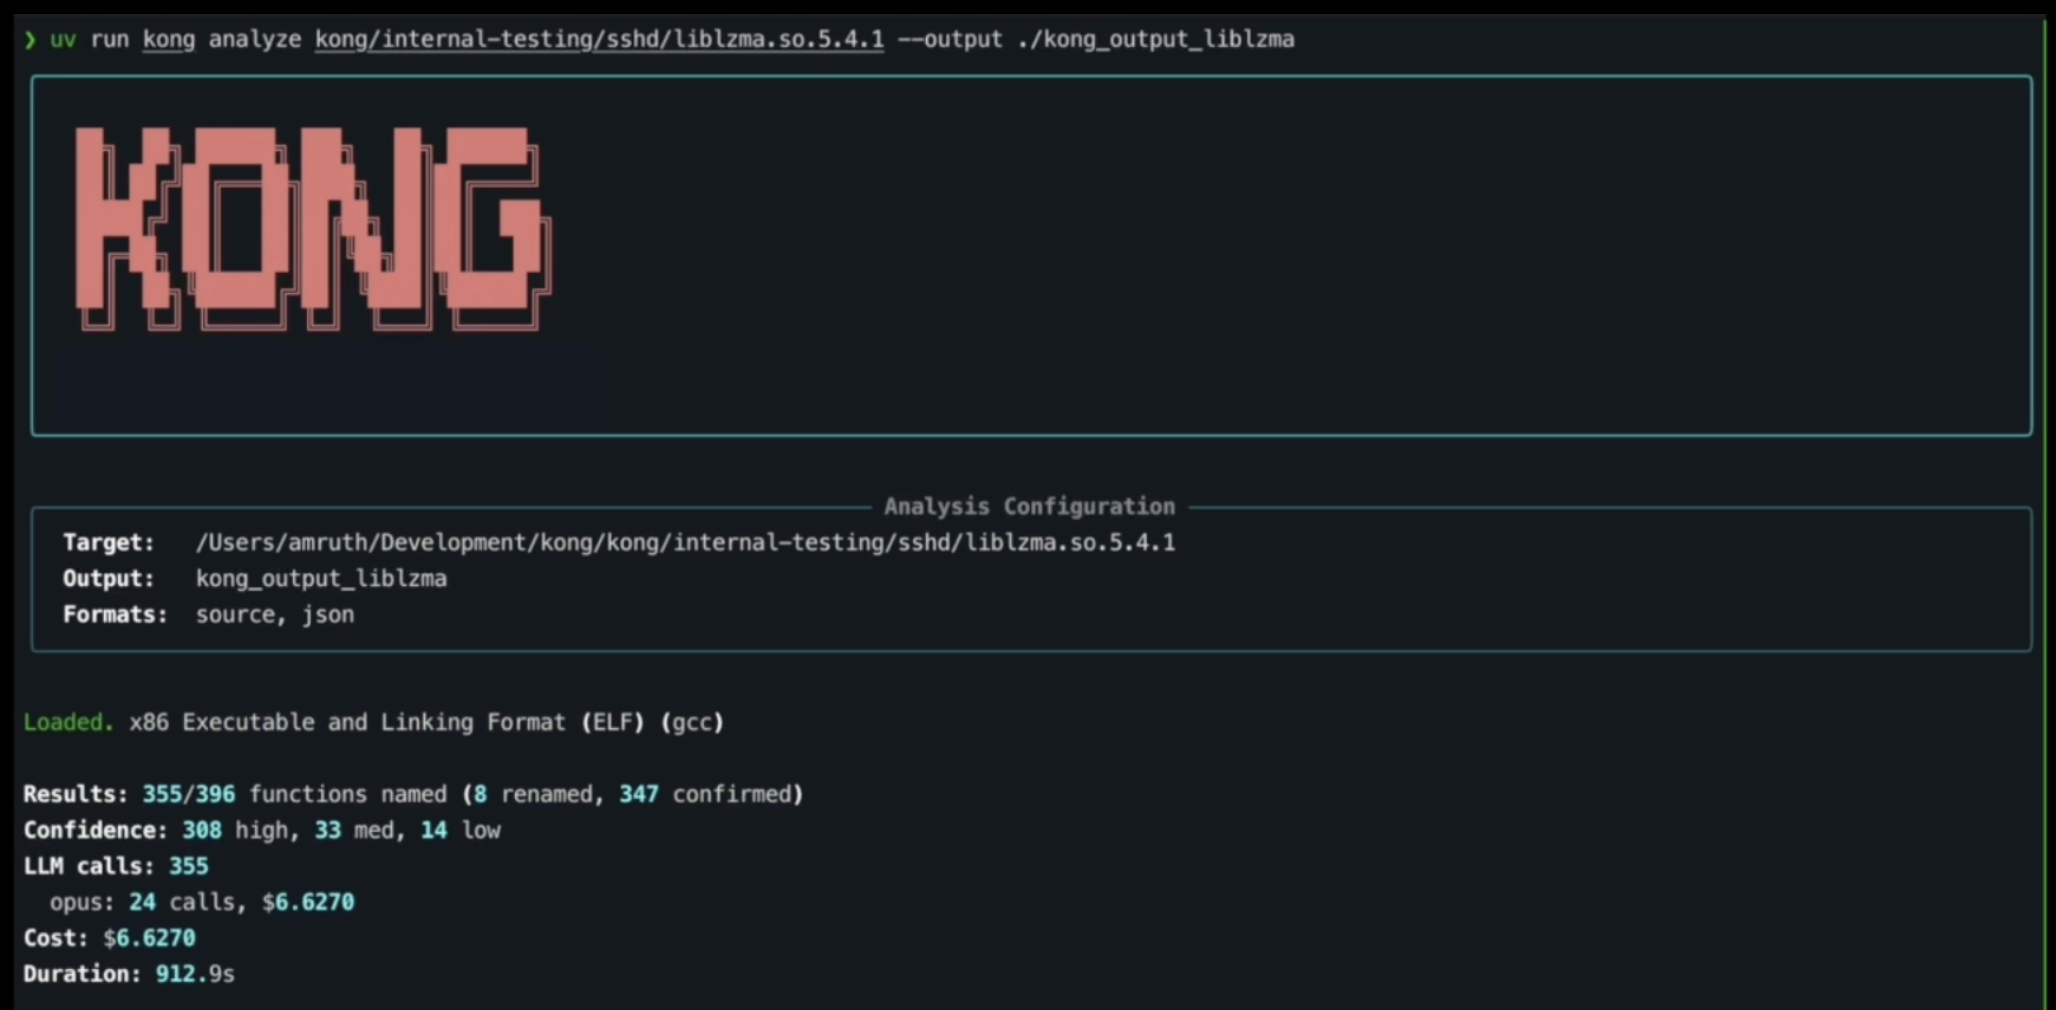
Reconstruct and validate C/C++ code from compiled programs with AI.

Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…

Vulnerability detection framework by Binarly's REsearch team

LLDB MCP Integration + other helpful commands

The world's first agentic reverse engineer.

Python Command-Line Ghidra MCP

Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.

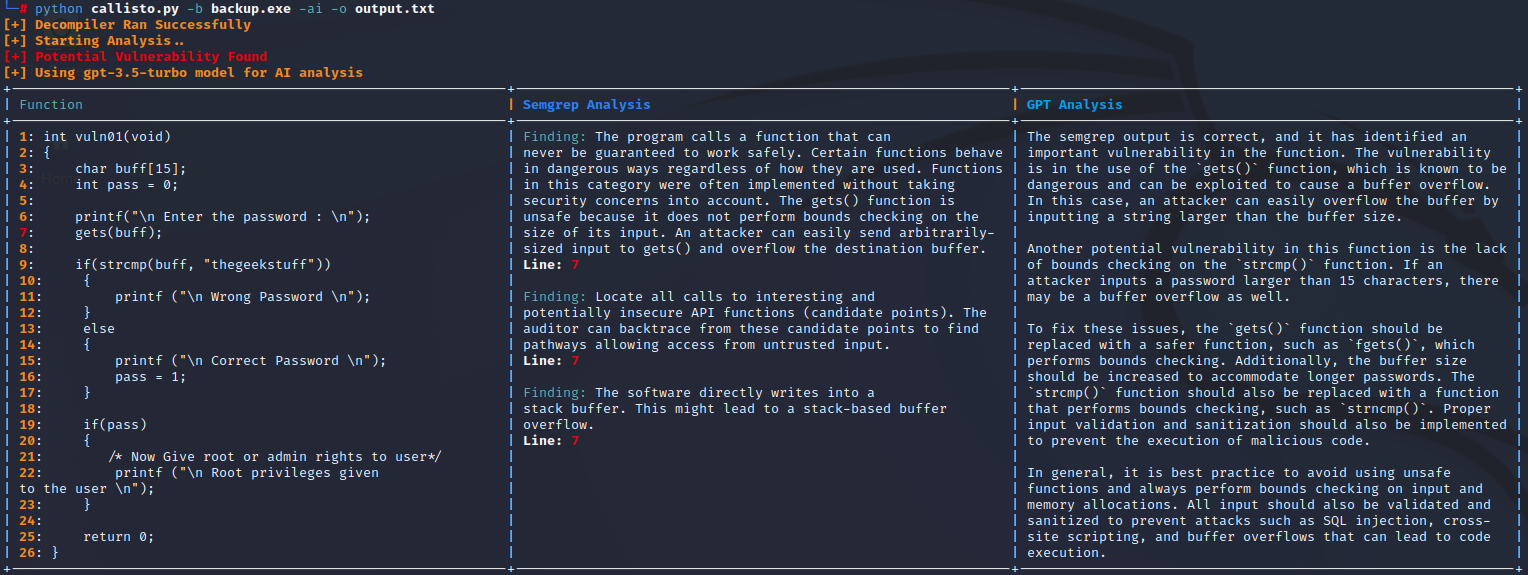
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…

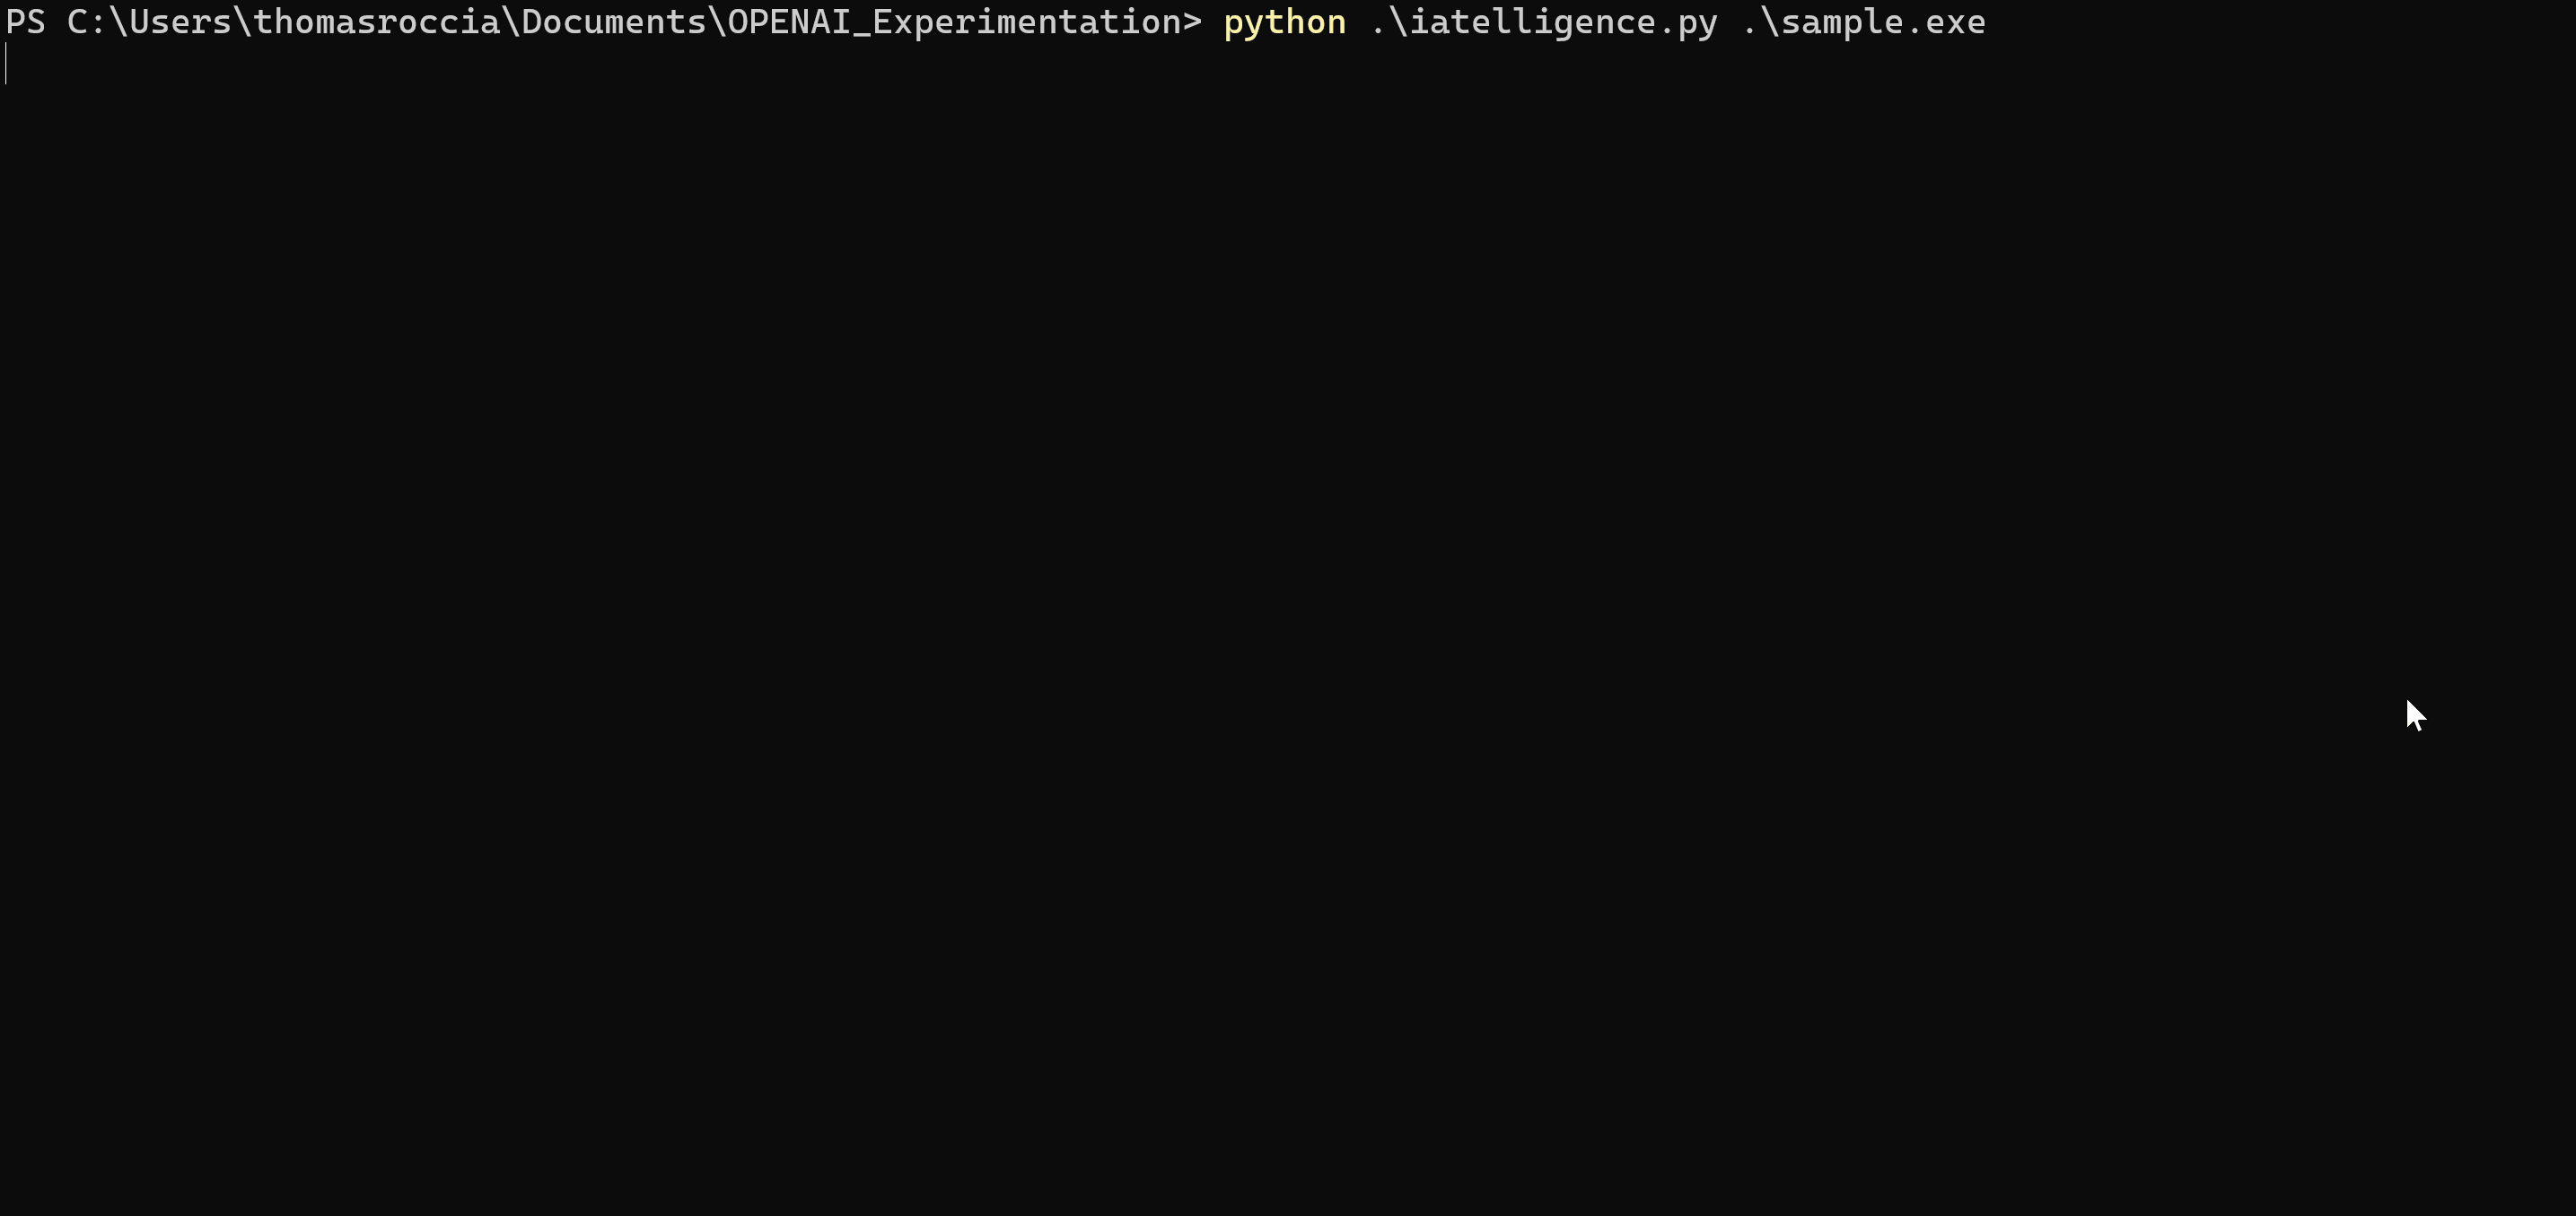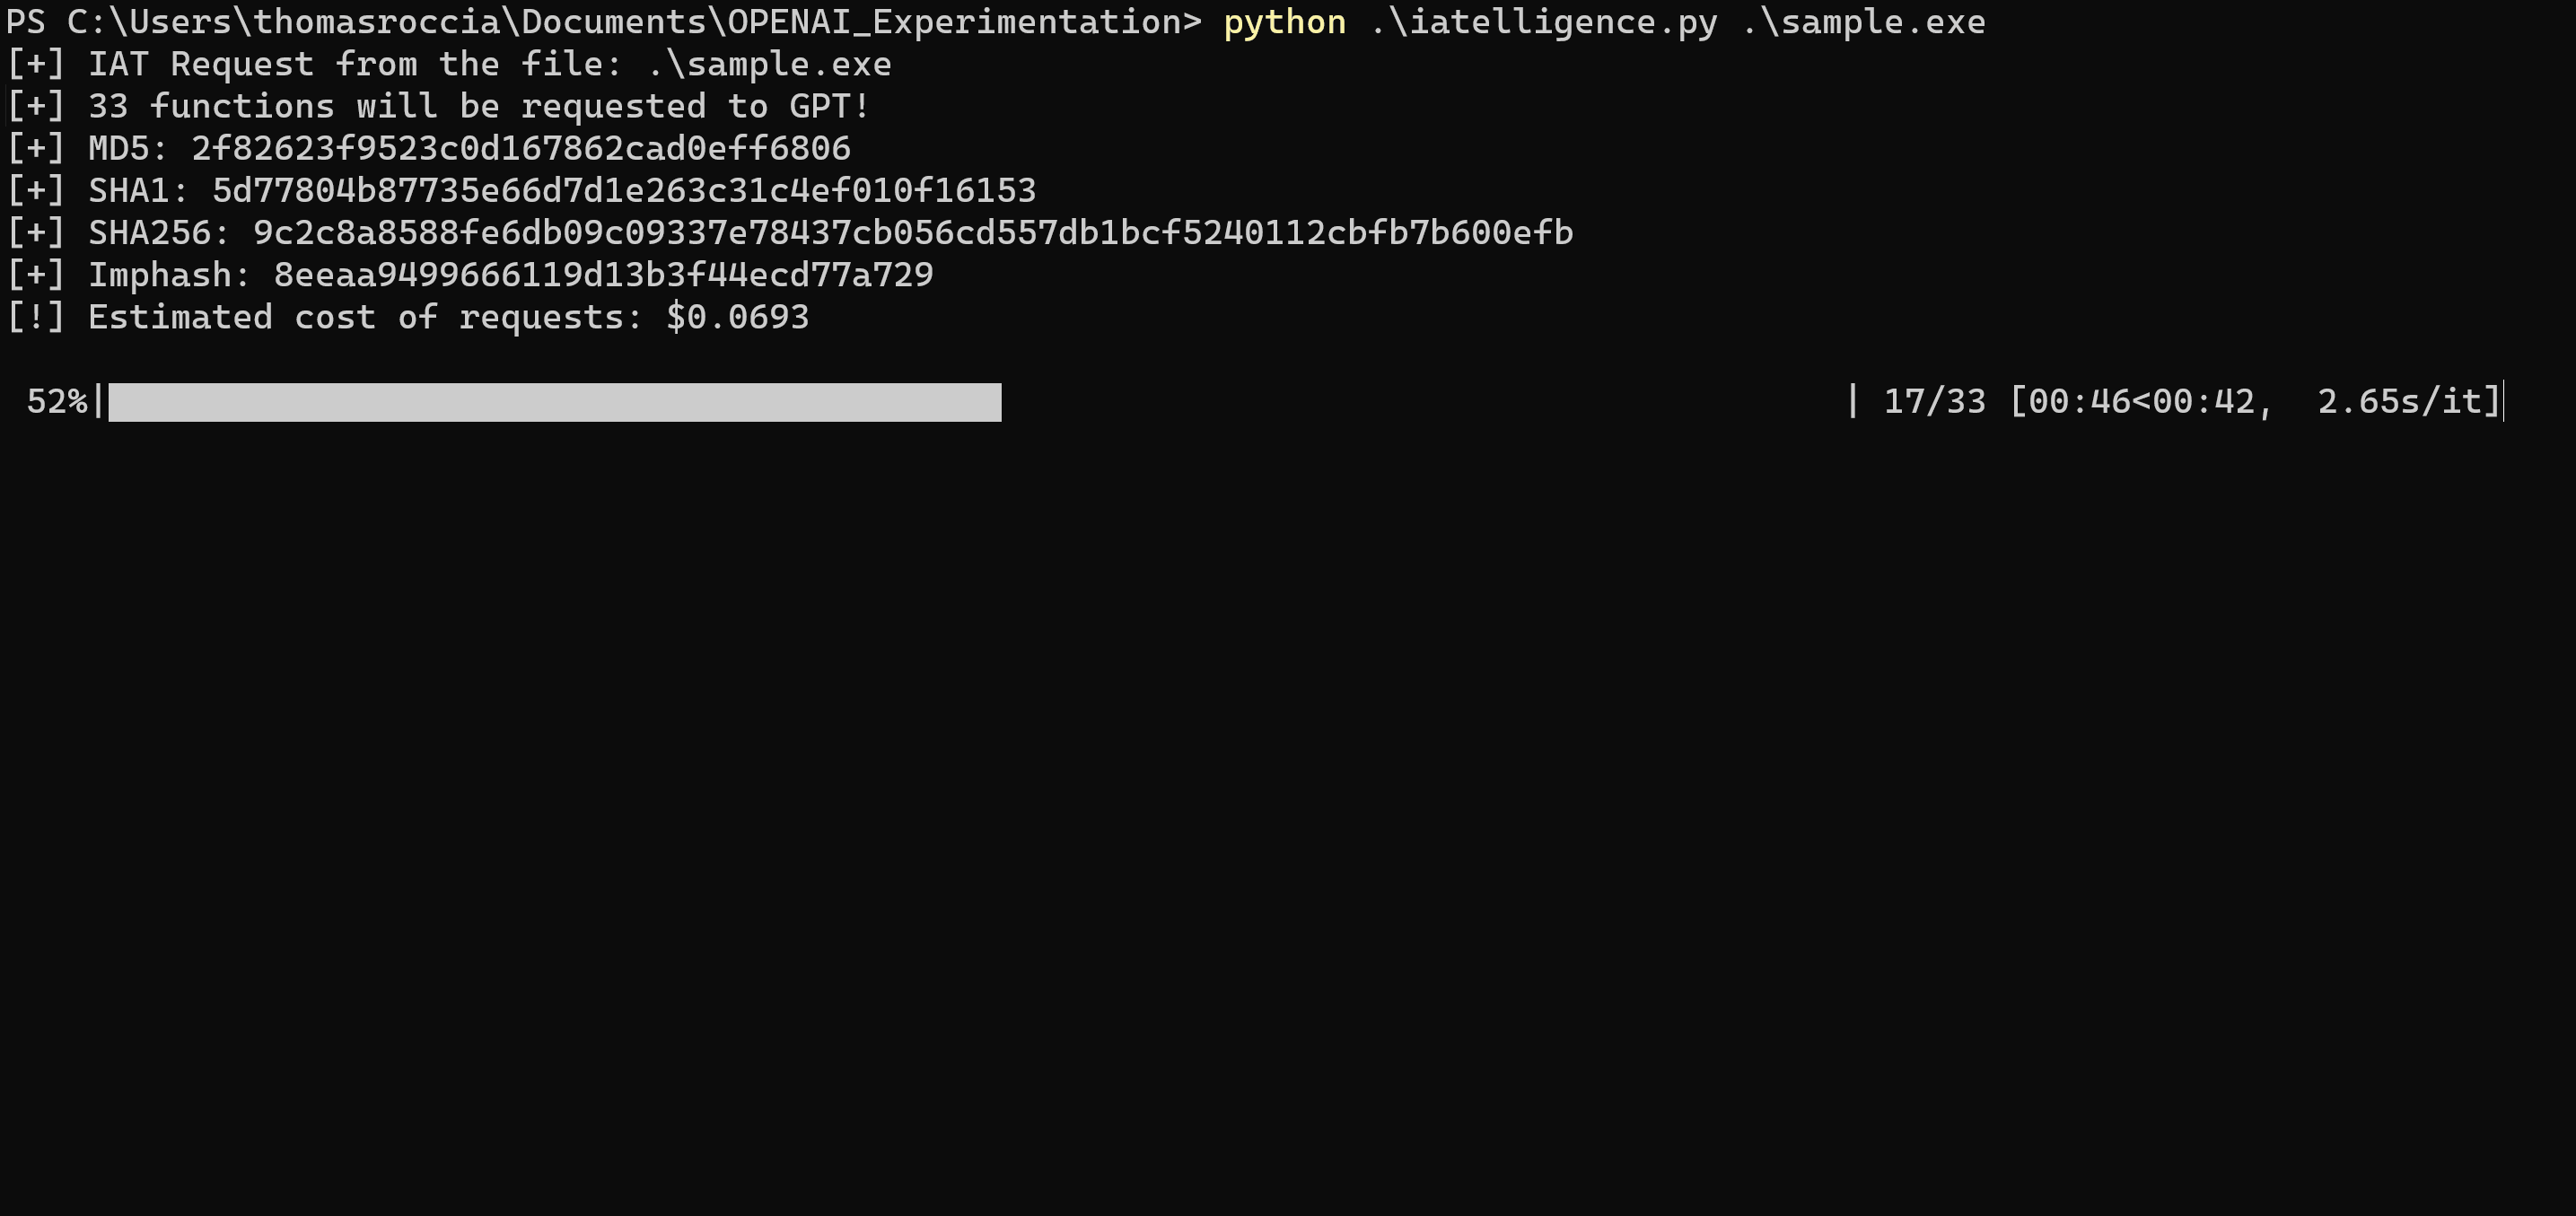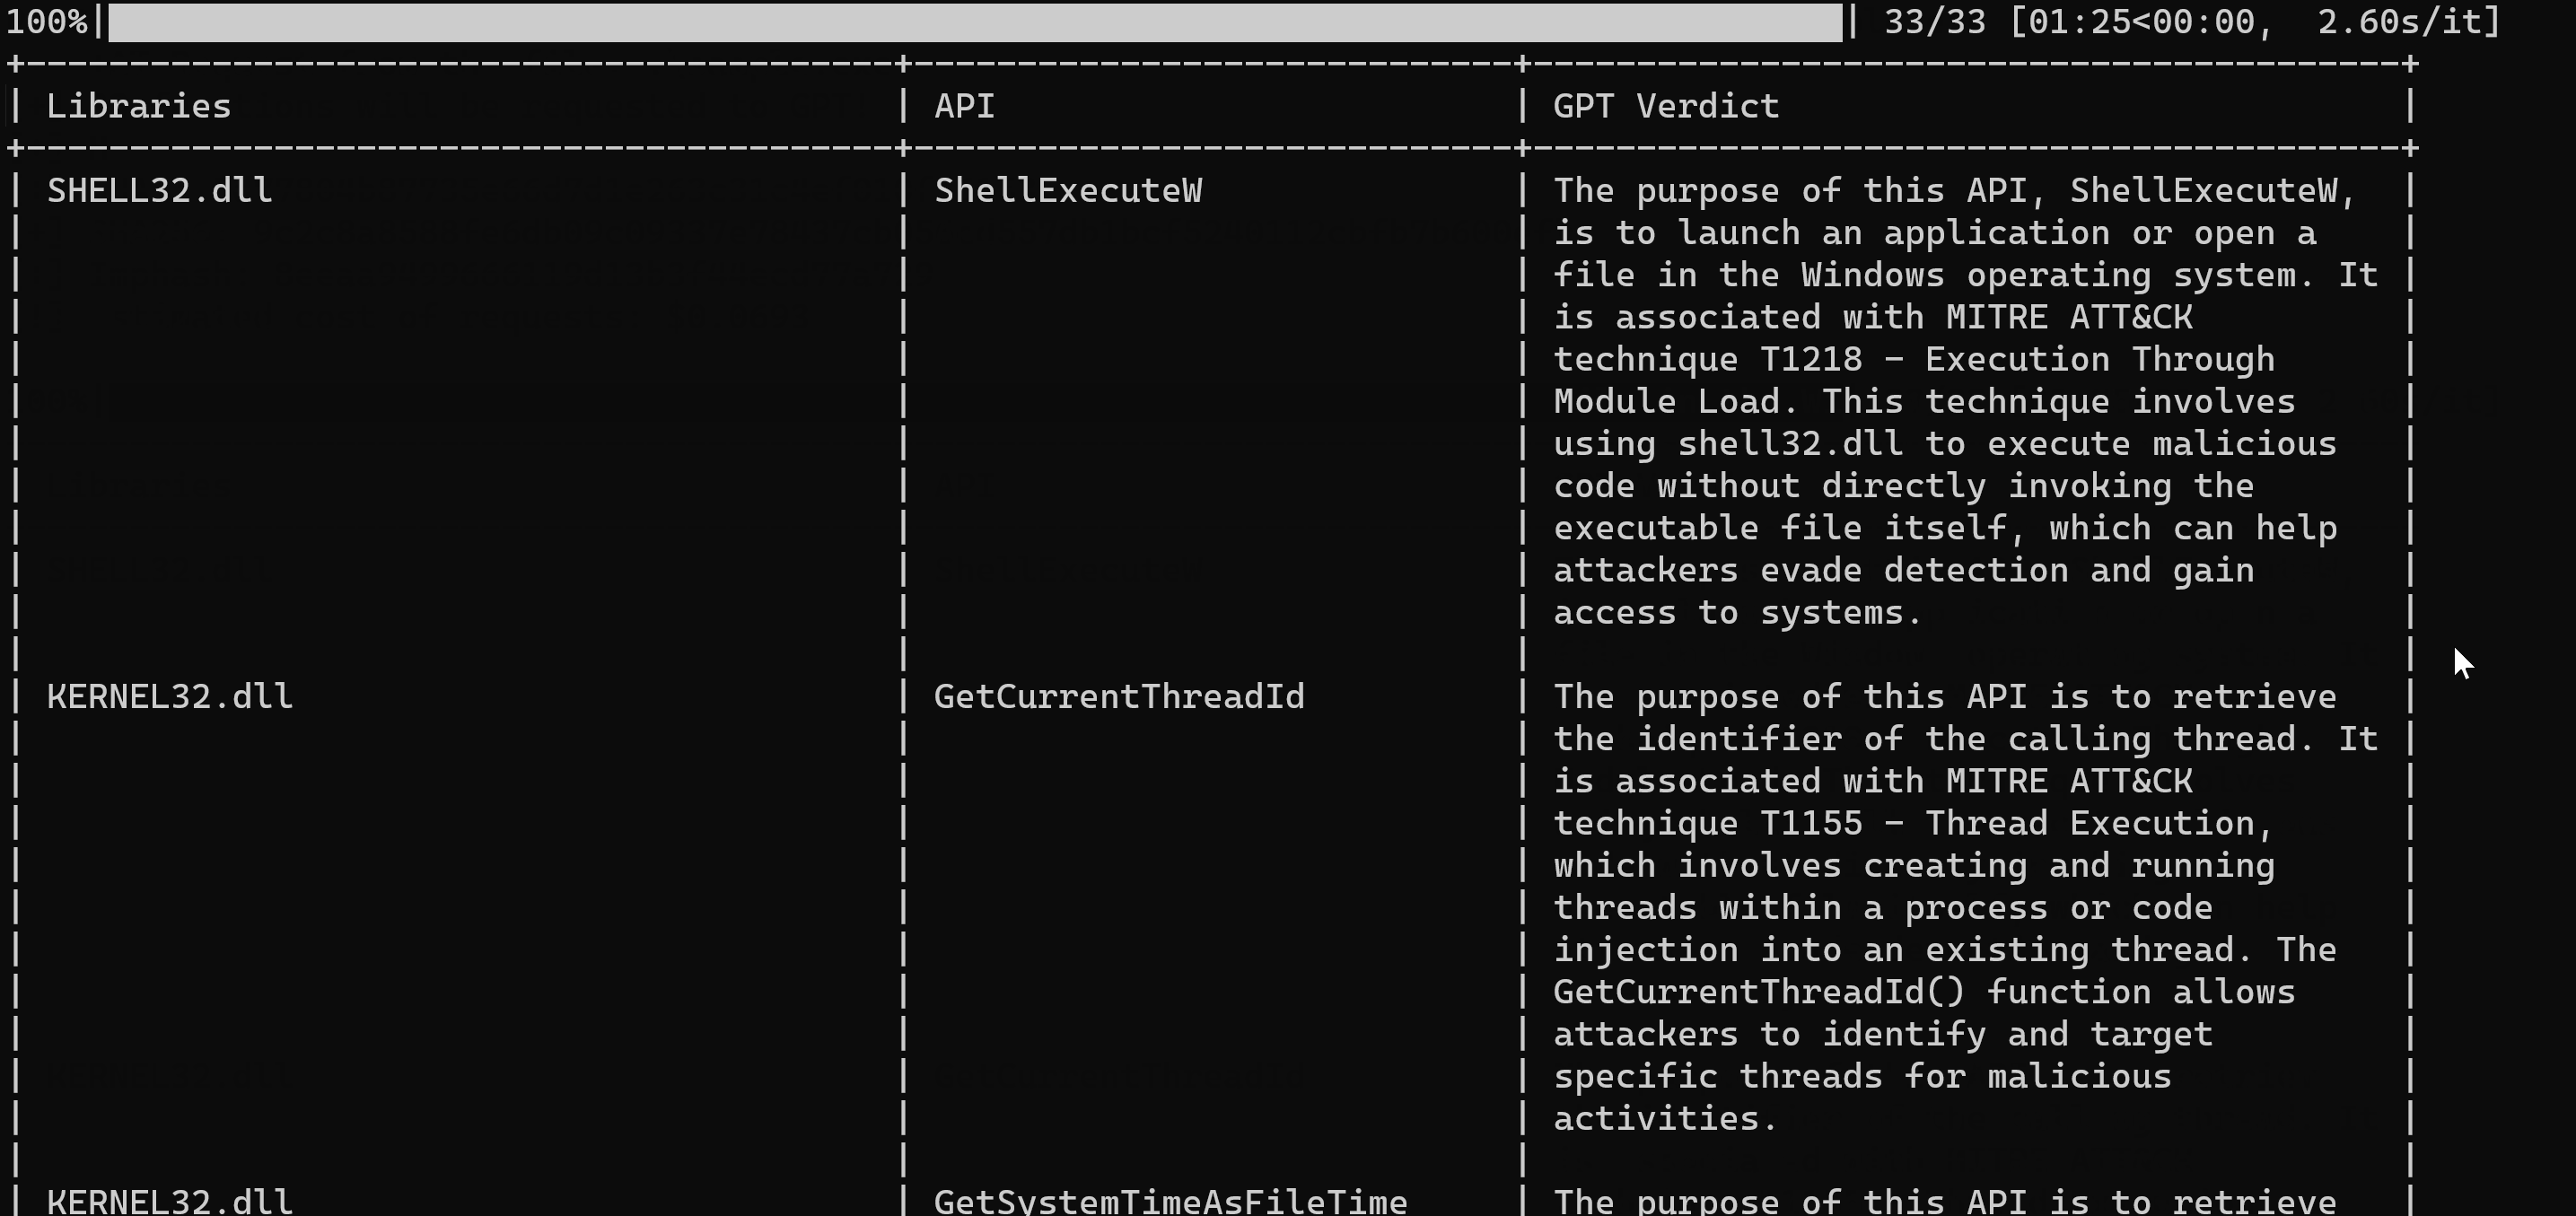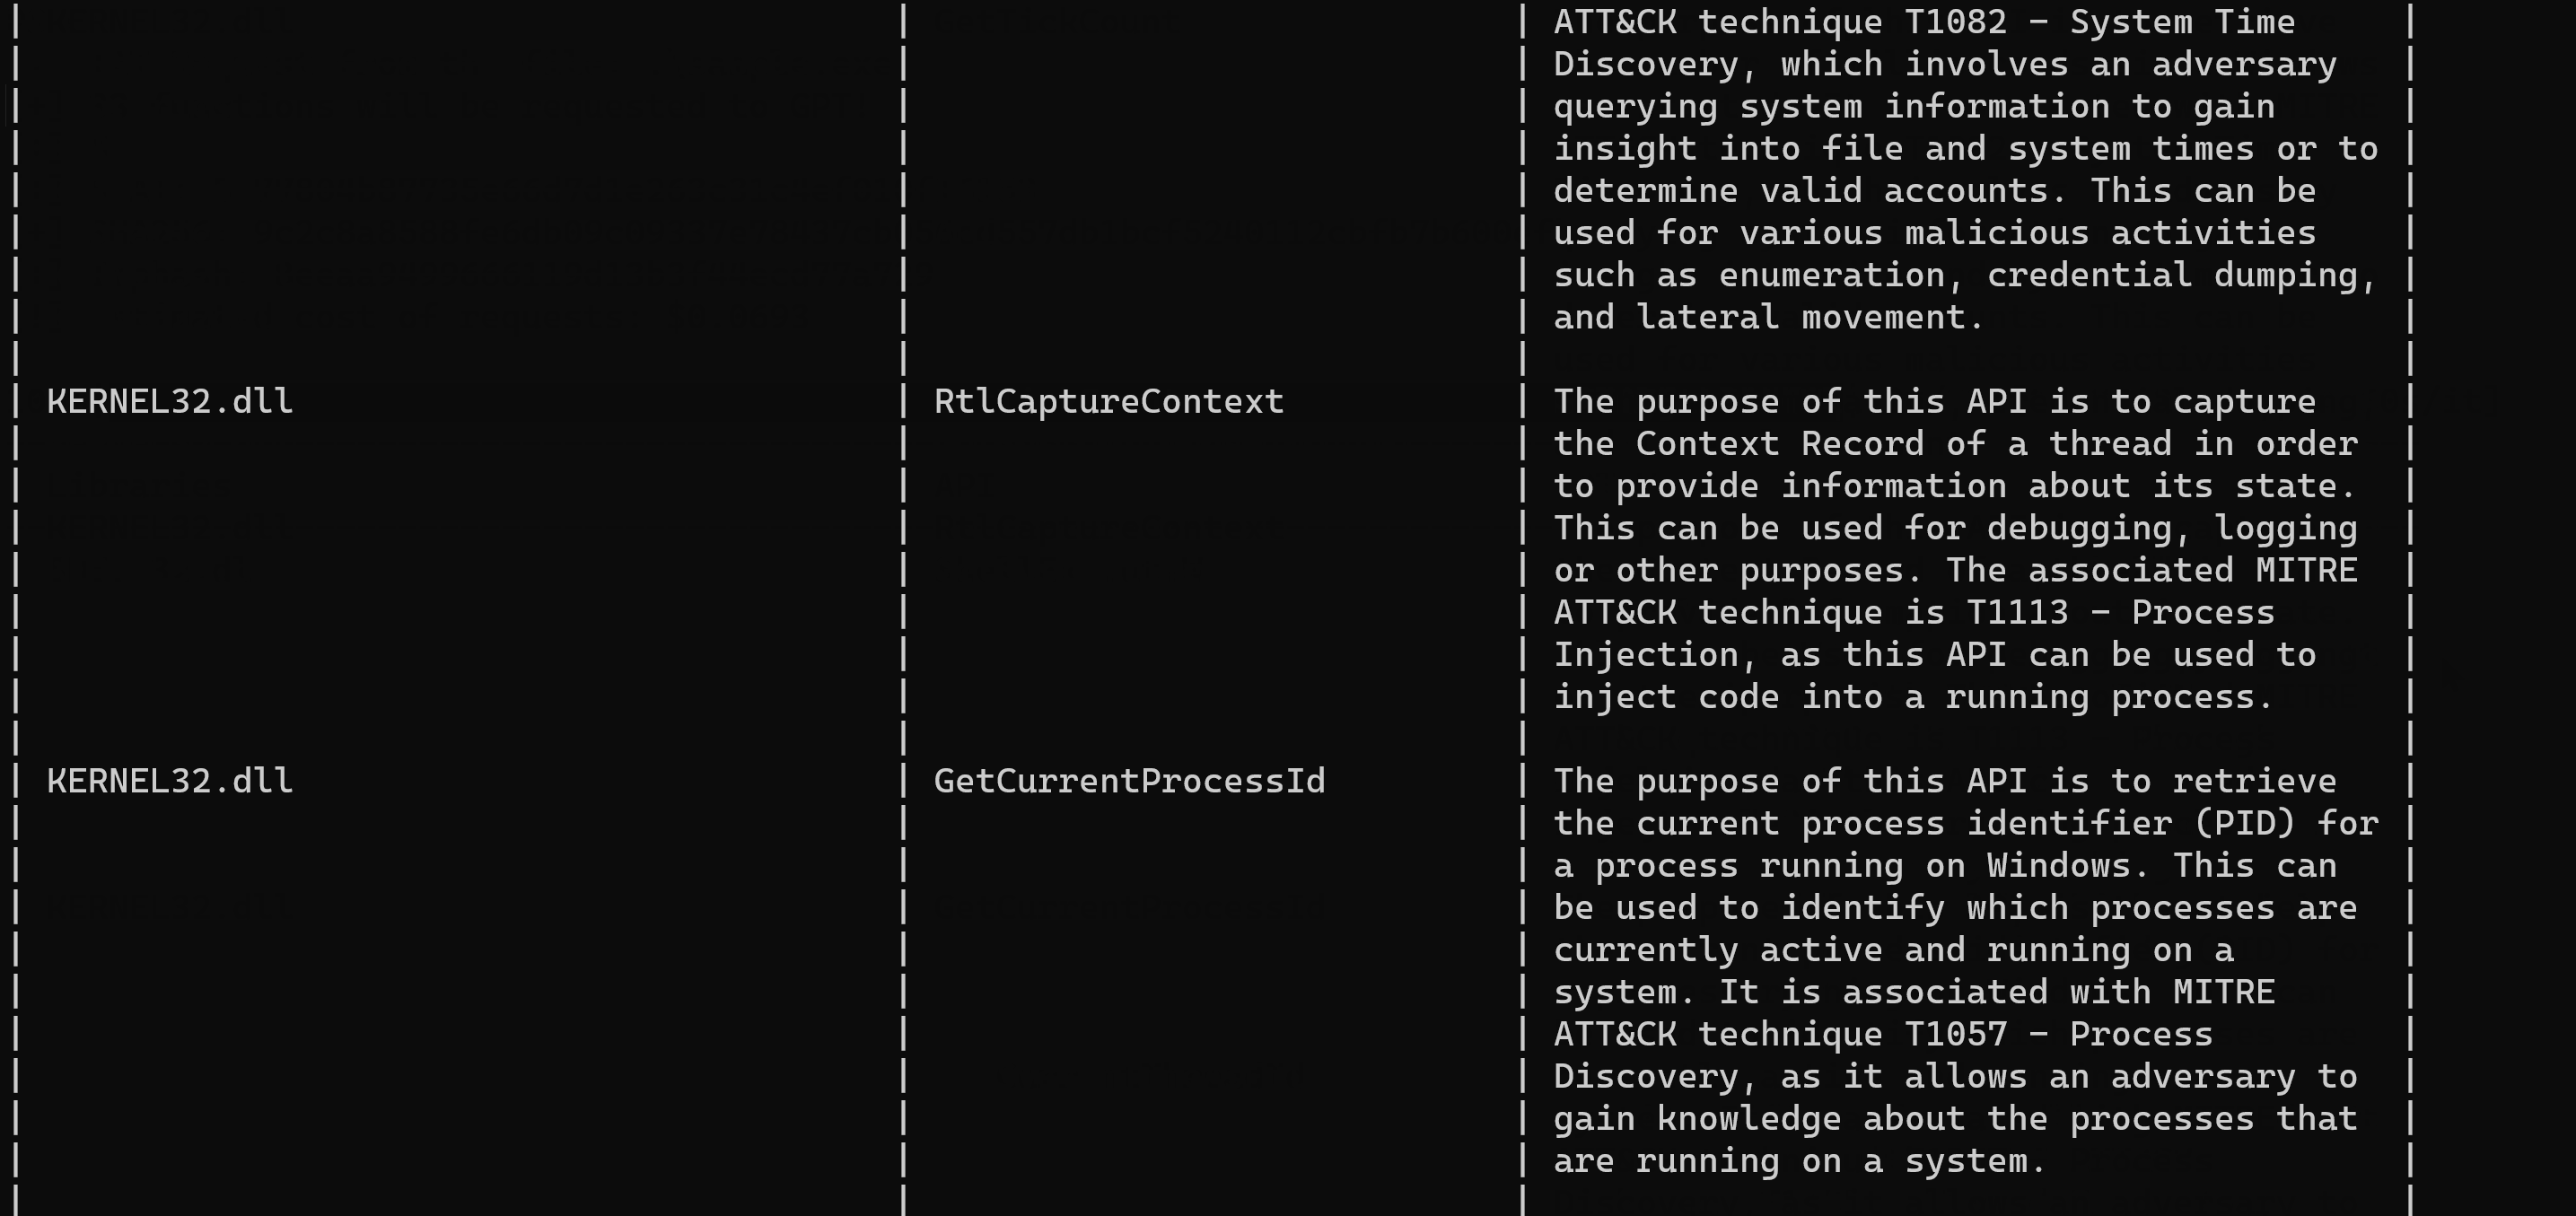
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

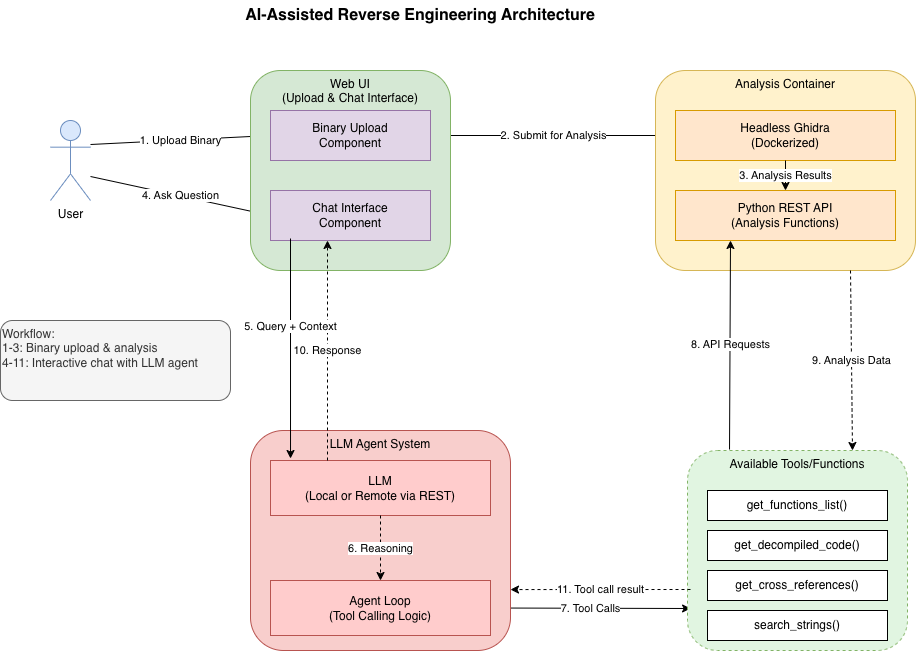
AI-Assisted Reverse Engineering with Ghidra

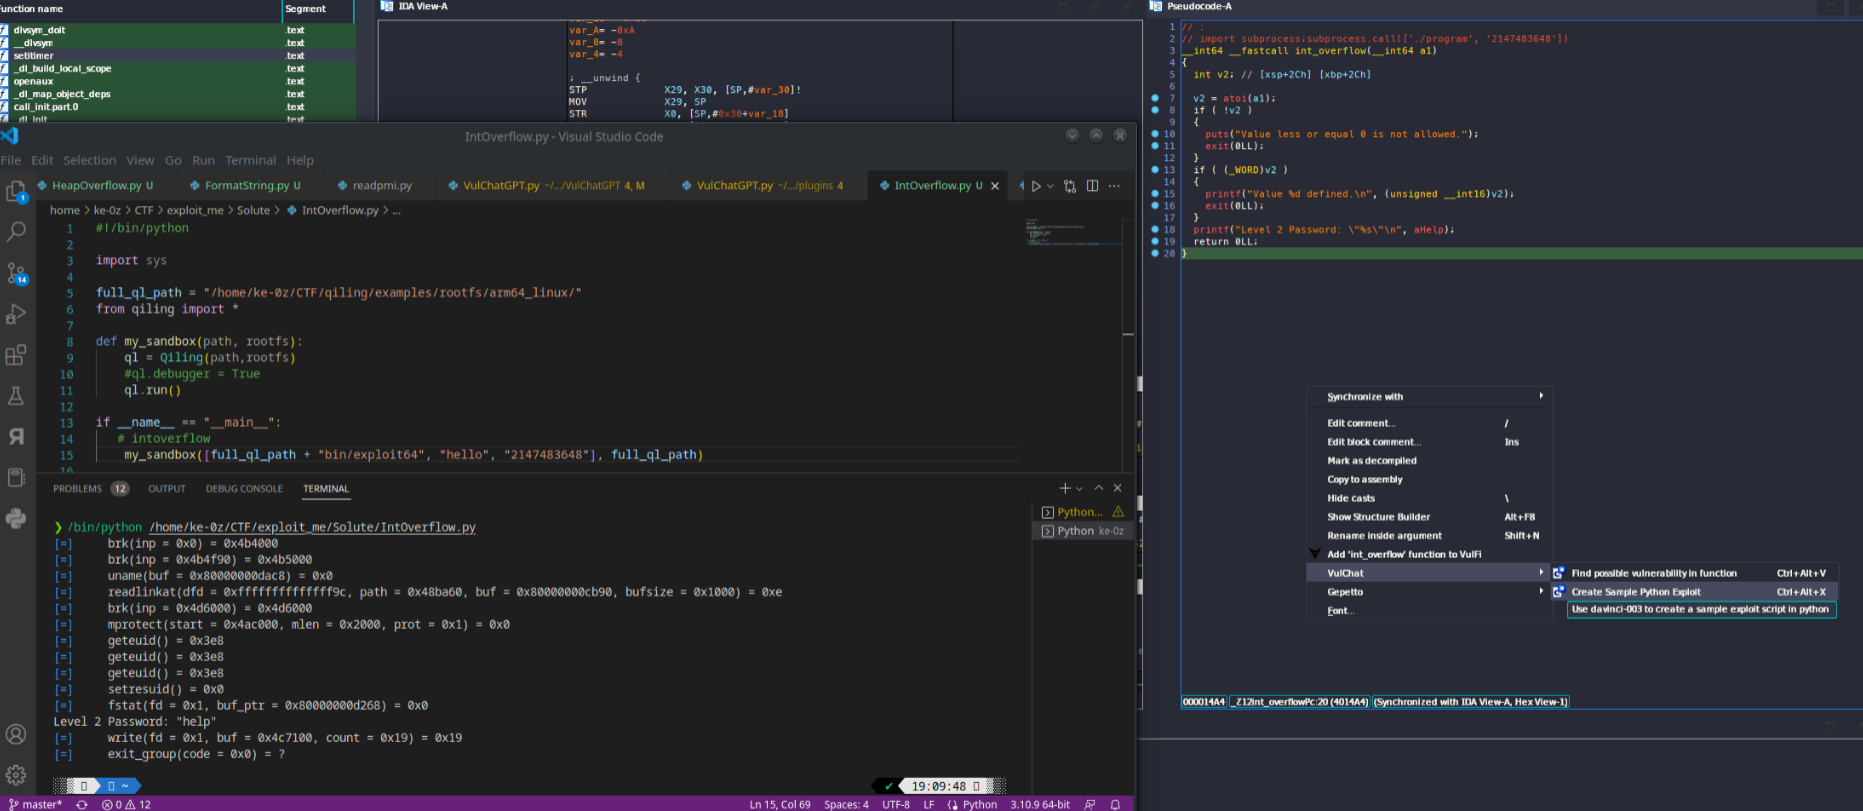
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries

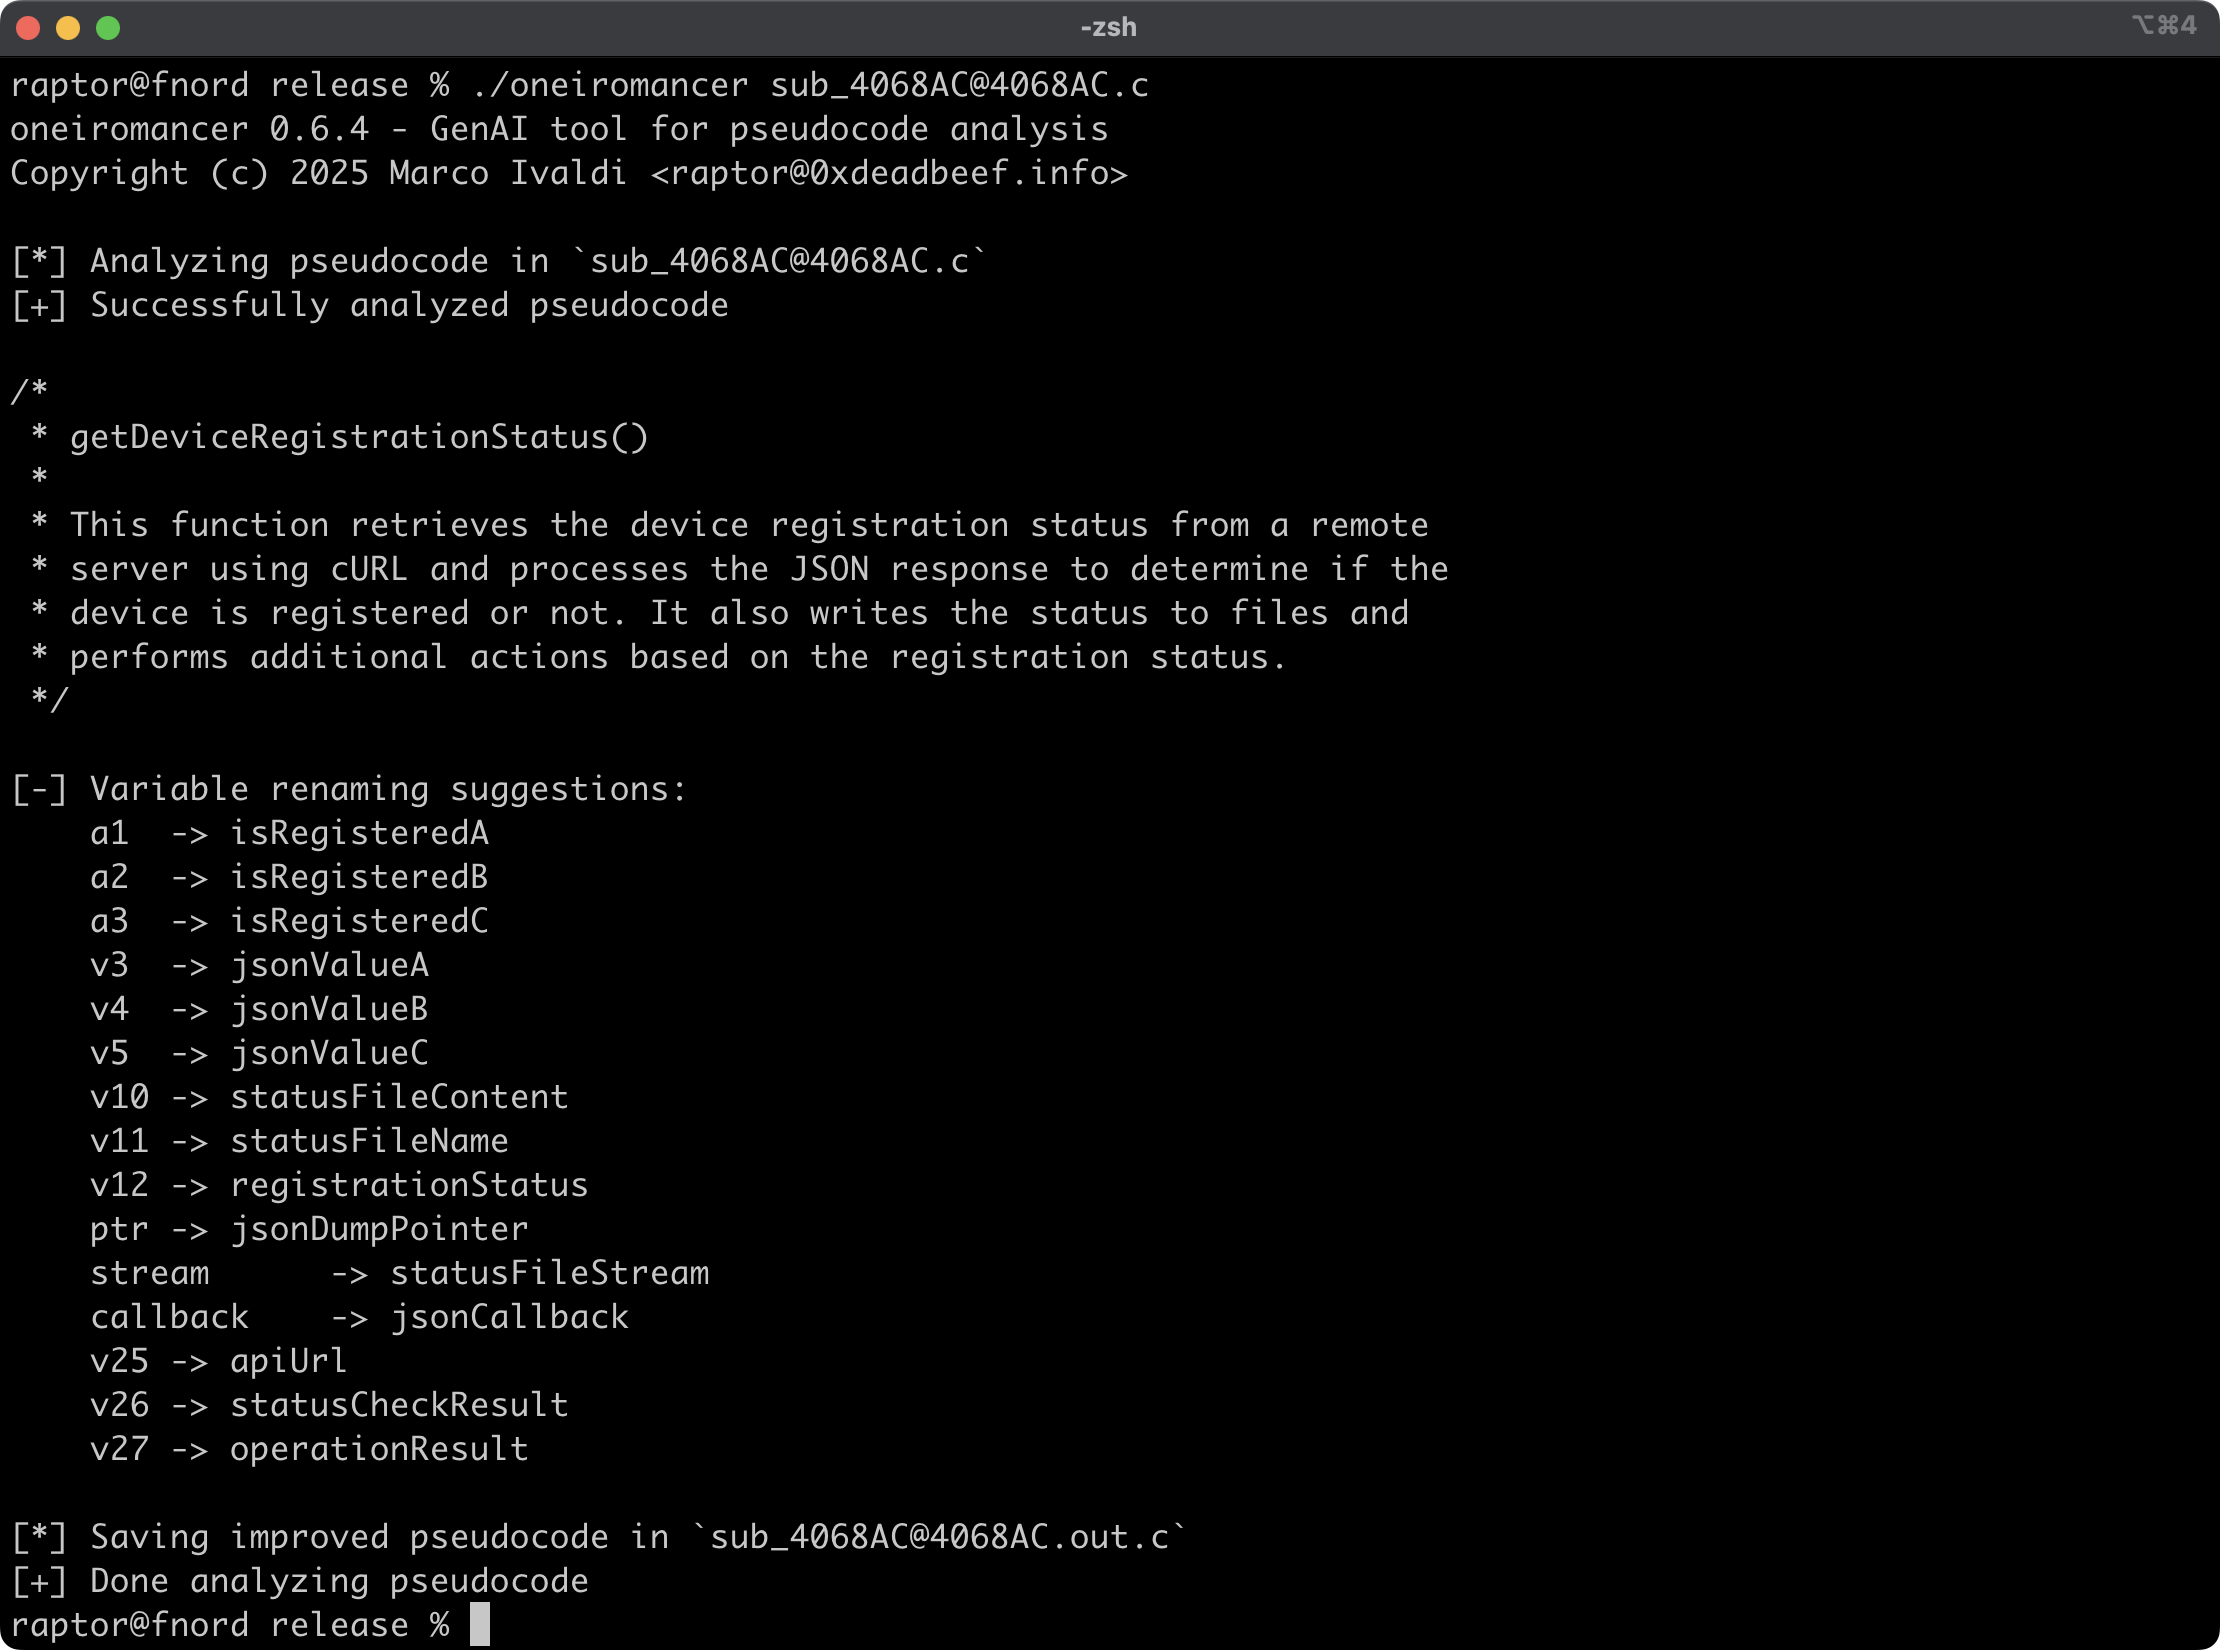
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.

A lightweight hex editor and decompiler to solve your binary file analysis problems.

A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.

Output high level Pcode (PcodeAST) in Ghidra