

rea
 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
ai-assisted-reversingai-securitybinary-analysis+5
morluto/reaReverse engineer anything with agents, from app behavior down to native binaries.
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
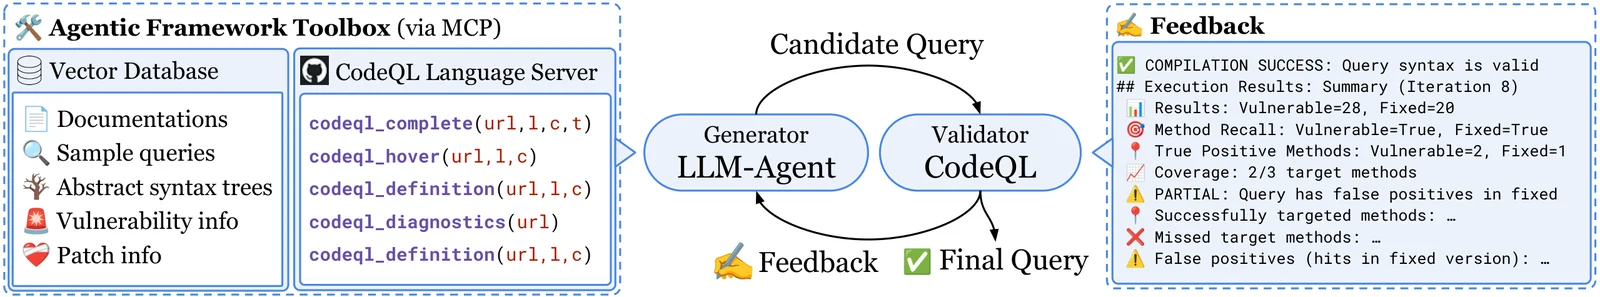 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
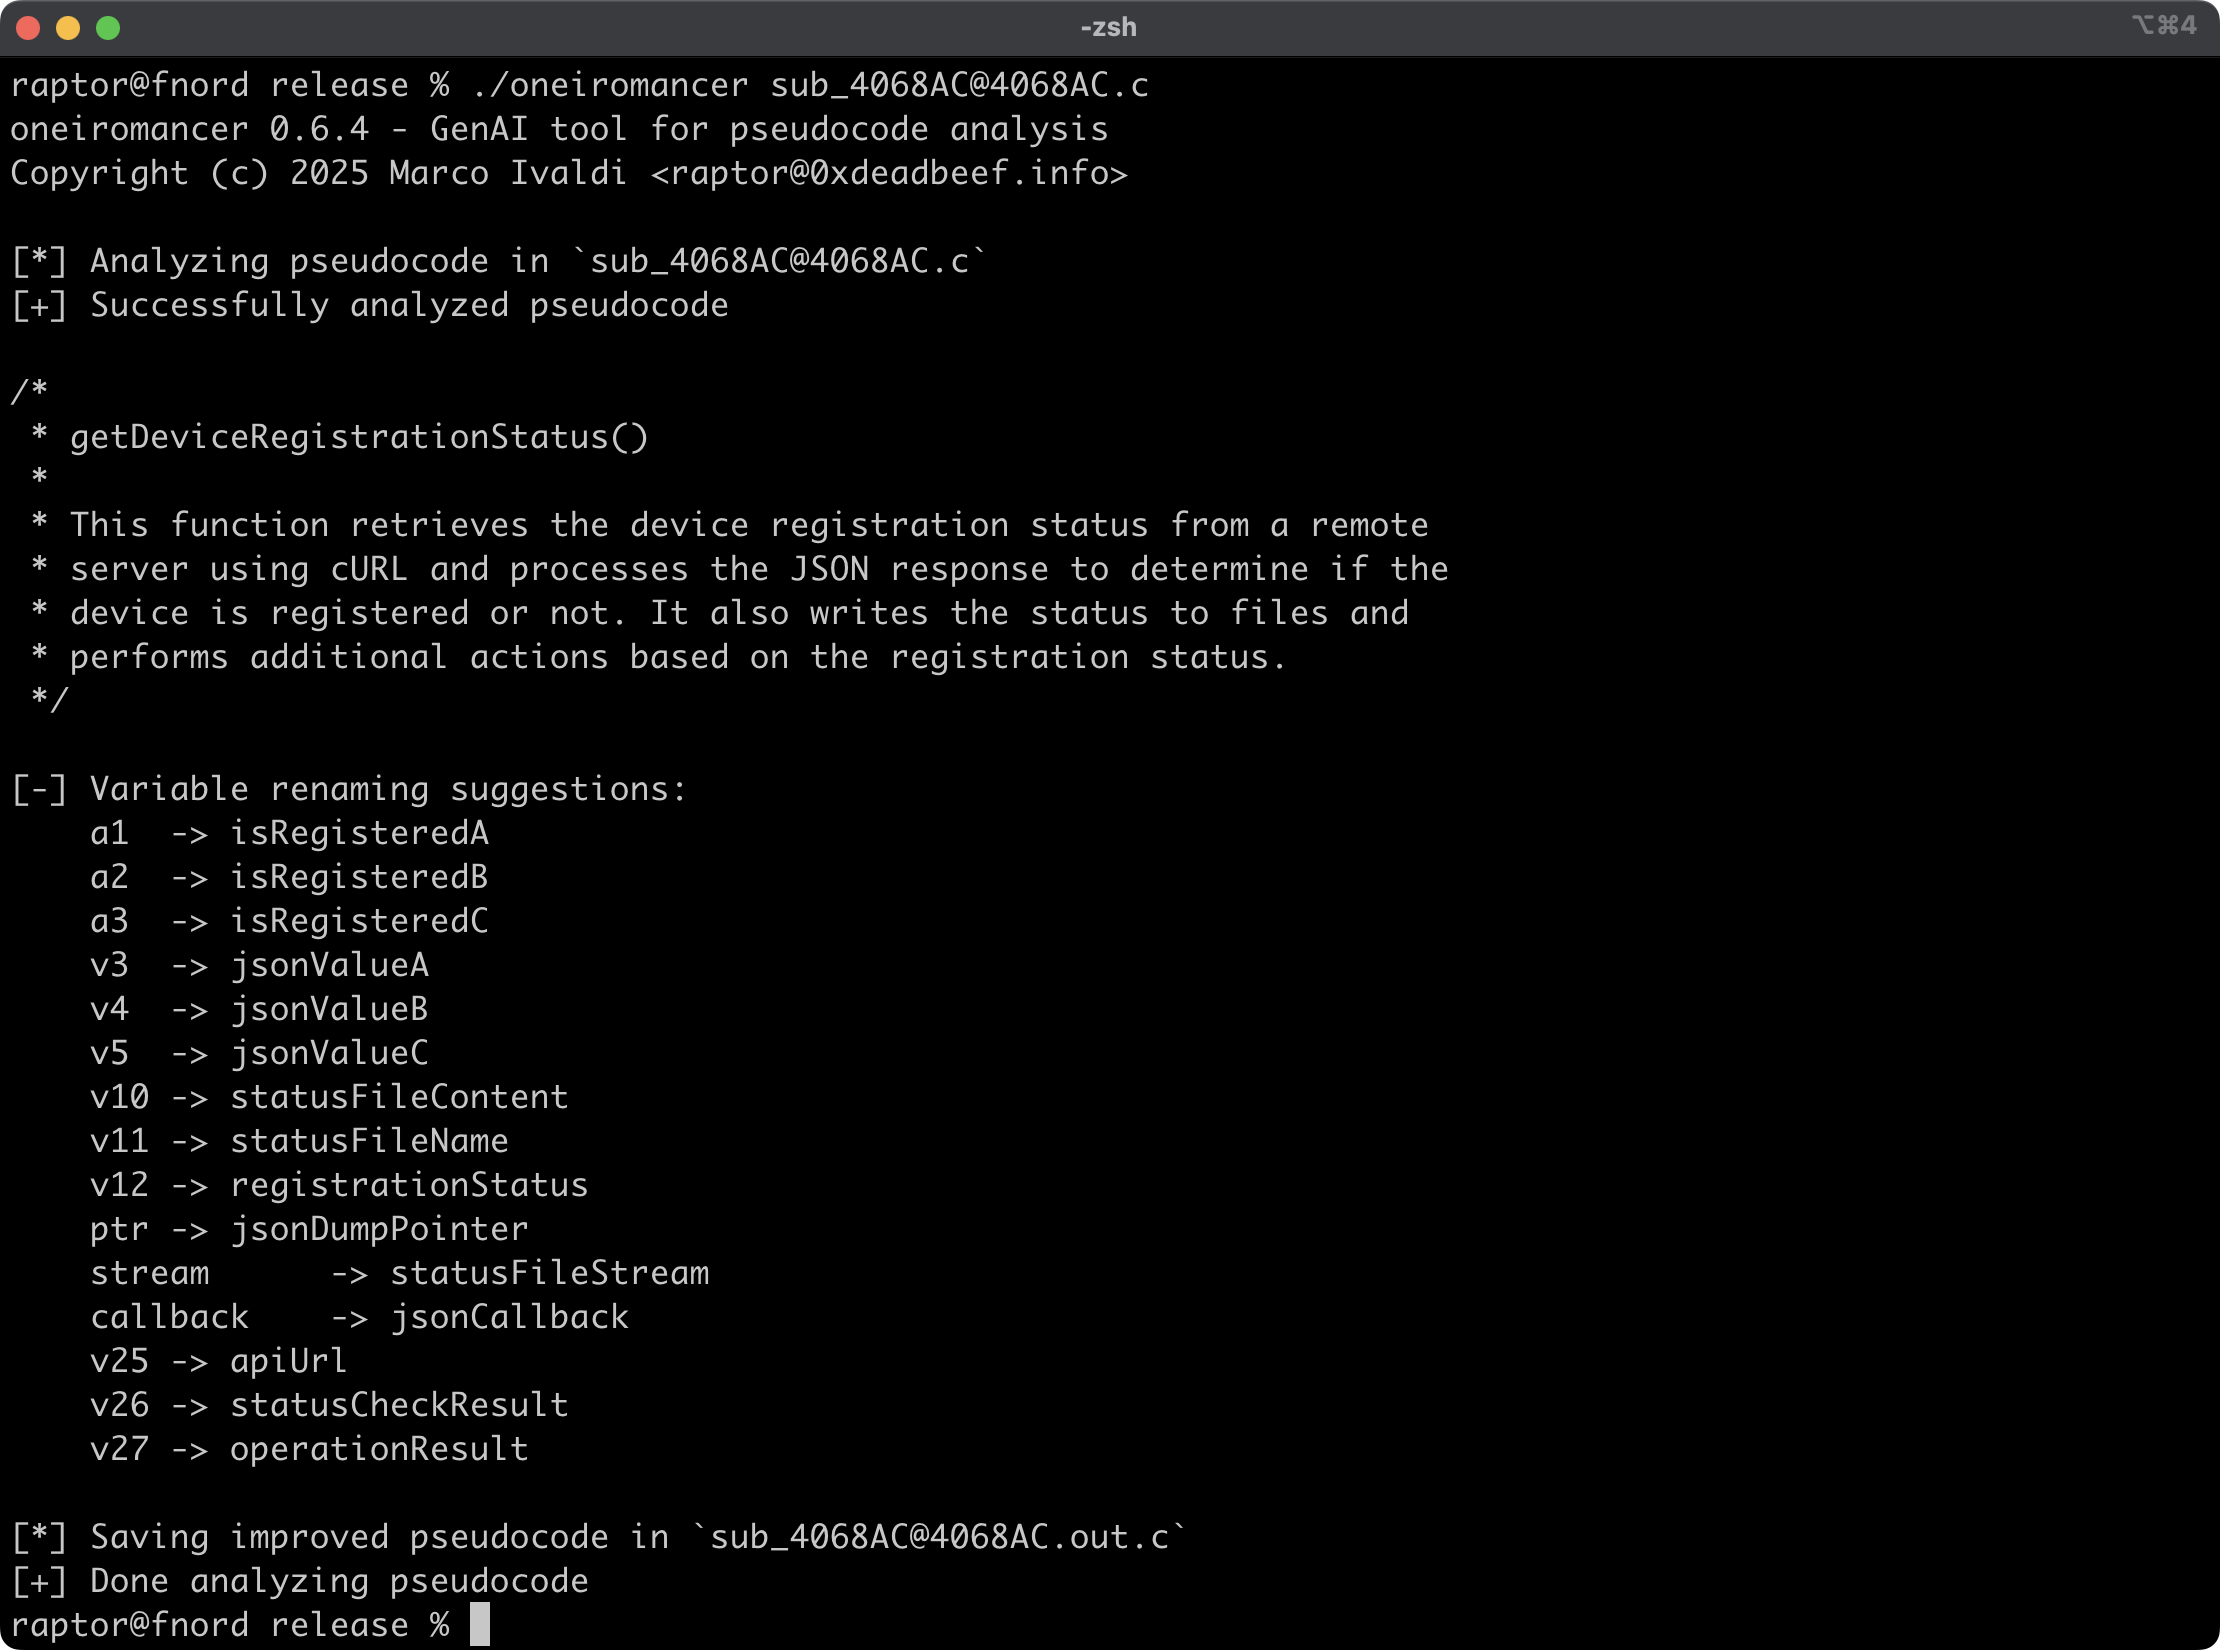 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 cosmosyi/autocontrol-arena
Automated framework for frontier AI safety evaluation that synthesizes executable, pressure-rich test environments to uncover latent risks in…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
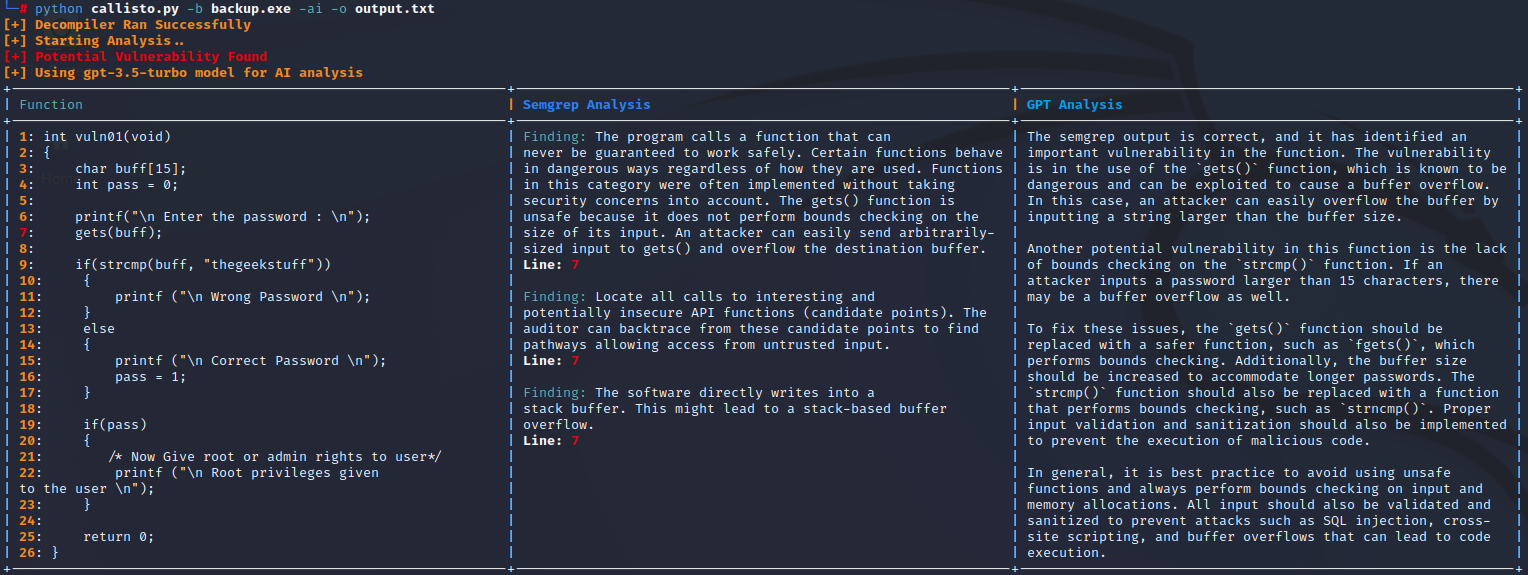 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…