

foolbox
 bethgelab/foolbox
A Python toolbox to create adversarial examples that fool neural networks in PyTorch, TensorFlow, and JAX
adversarial-attackai-securitymachine-learning+1
3.0k
bethgelab/foolboxA Python toolbox to create adversarial examples that fool neural networks in PyTorch, TensorFlow, and JAX
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 george0papasotiriou/cve-2026-23010-ccsds-telecommand-replay-without-sequence-number
PoC simulation of a critical CCSDS telecommand replay vulnerability in satellite command systems, demonstrating missing sequence-number validation…
 george0papasotiriou/cve-2026-22020-weak-seed-in-quantum-key-distribution-error-correction
Python PoC demonstrating CVE-2026-22020: exploitable weak seed in quantum key distribution privacy amplification, reducing final key entropy.
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 thuyimingli/backdoor-learning-resources
Curated list of backdoor learning papers, surveys, and toolboxes, organizing poisoning-based attacks and defenses in deep learning for researchers…
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
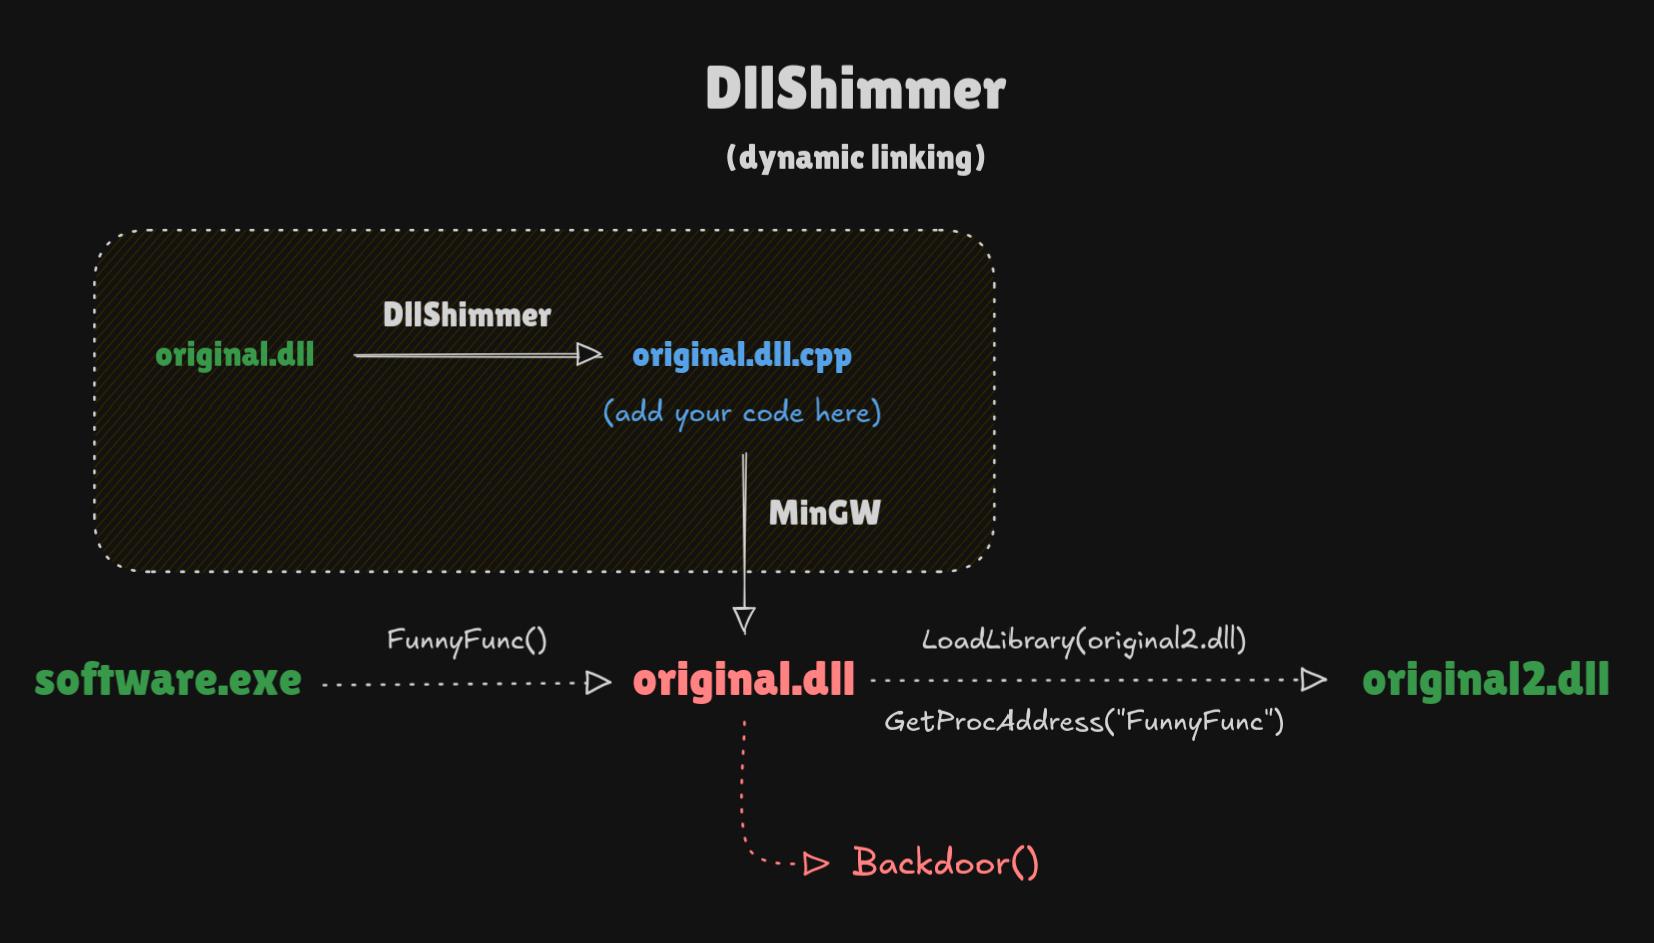 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
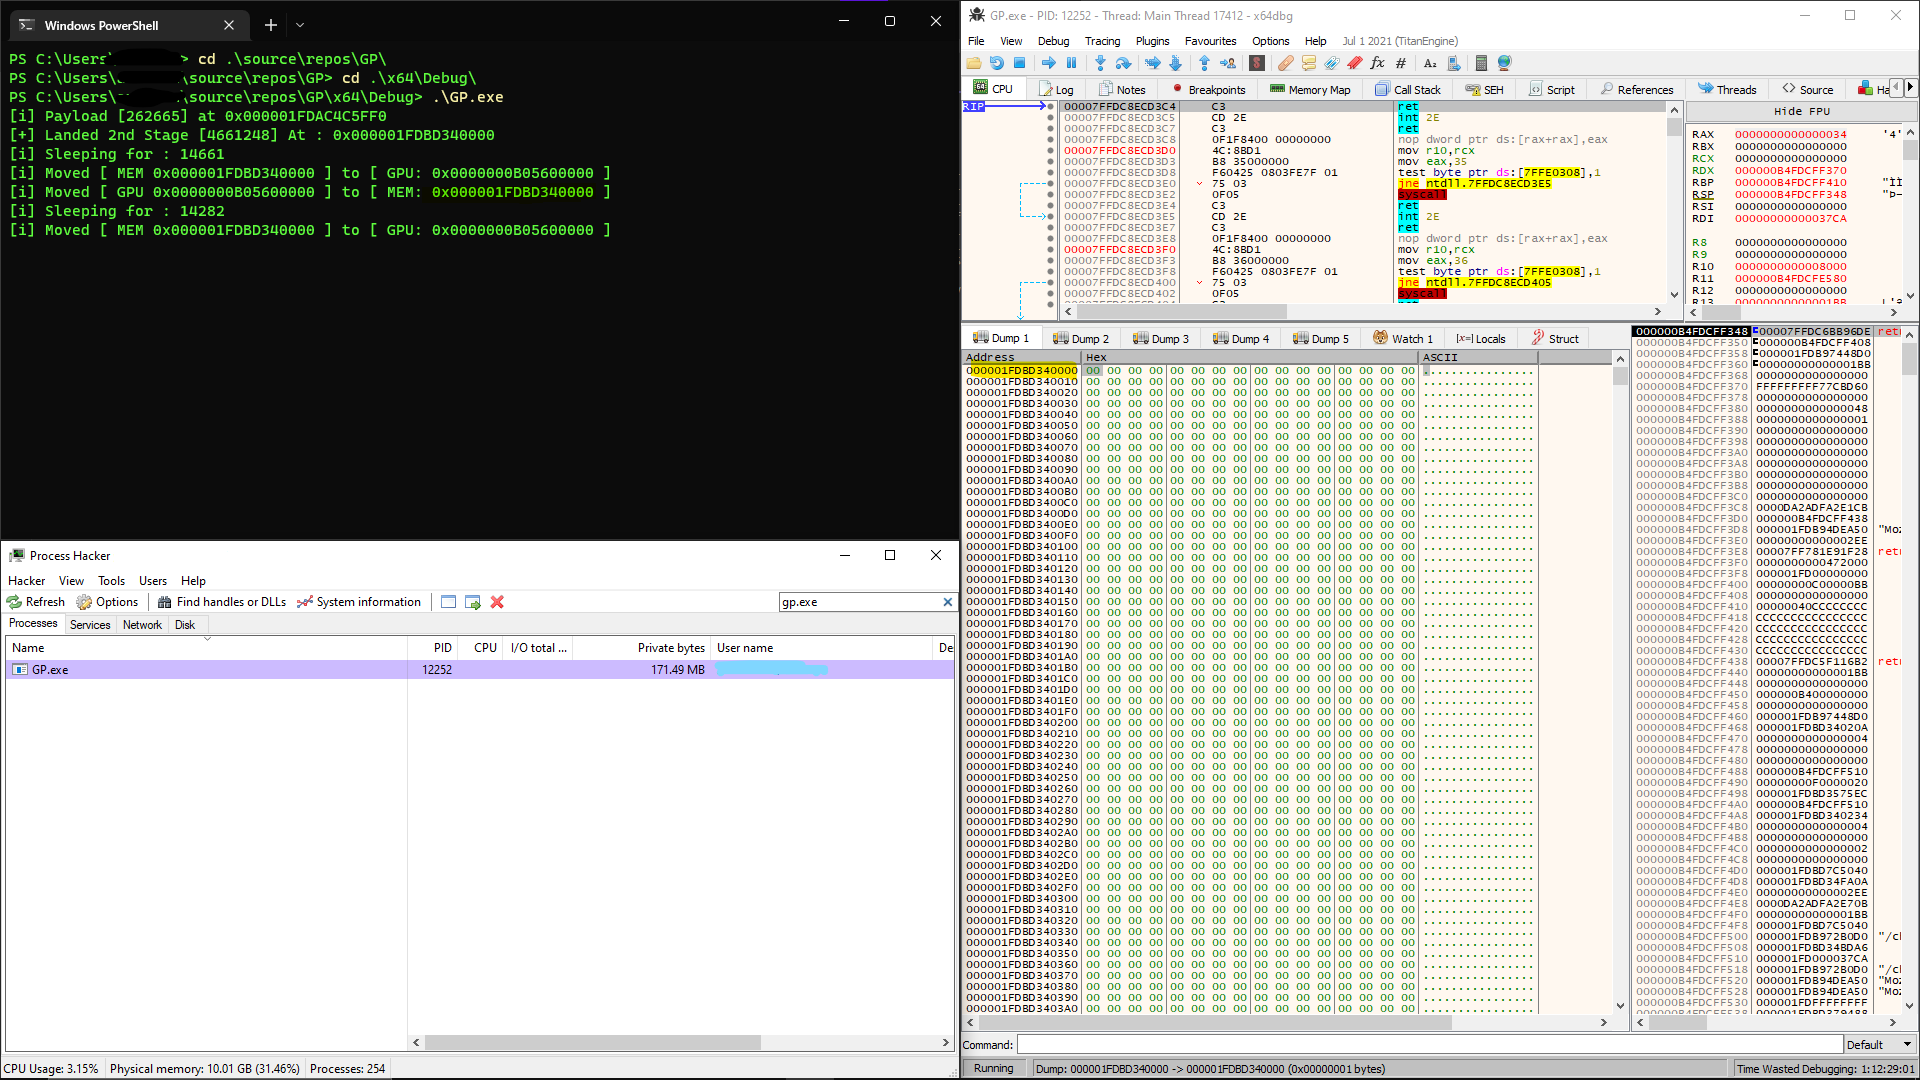 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.