
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/jwillyamz/ezemu
Defensive ToolsPenetration TestingLearning & EducationRed TeamingAdversarial AttackLabs & Practice
GitHubjwillyamz/ezemu

ezEmu

See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)

View Repository
1099373 years agoReviewed by Kitploit
Share

ezEmu

ezEmu enables users to test adversary behaviors via various execution techniques. Sort of like an "offensive framework for blue teamers", ezEmu does not have any networking/C2 capabilities and rather focuses on creating local test telemetry.

Windows

See /Linux for ELF

ezEmu is compiled as parent.exe to simplify process trees, and will track (and also kill) child processes to enable easy searches in logs/dashboards.

Current execution techniques include:

  • Cmd.exe (T1059.003)
  • PowerShell (T1059.001)
  • Unmanaged PowerShell (T1059.001)
  • CreateProcess() API (T1106)
  • WinExec() API (T1106)
  • ShellExecute (T1106)
  • Windows Management Instrumentation (T1047)
  • VBScript (T1059.005)
  • Windows Fiber
  • WMIC XSL Script/Squiblytwo (T1220)
  • Microsoft Word VBA Macro (T1059.005)
  • Python (T1059.006)

Note: You need to enable some macro related trust center settings for the Word stuffz to work - https://support.office.com/en-us/article/enable-or-disable-macros-in-office-files-12b036fd-d140-4e74-b45e-16fed1a7e5c6. You also need Python installed and the PATH variable set for #12

Usage/Demo

ezEmu is an interactive terminal application and works much better if you run from cmd.exe
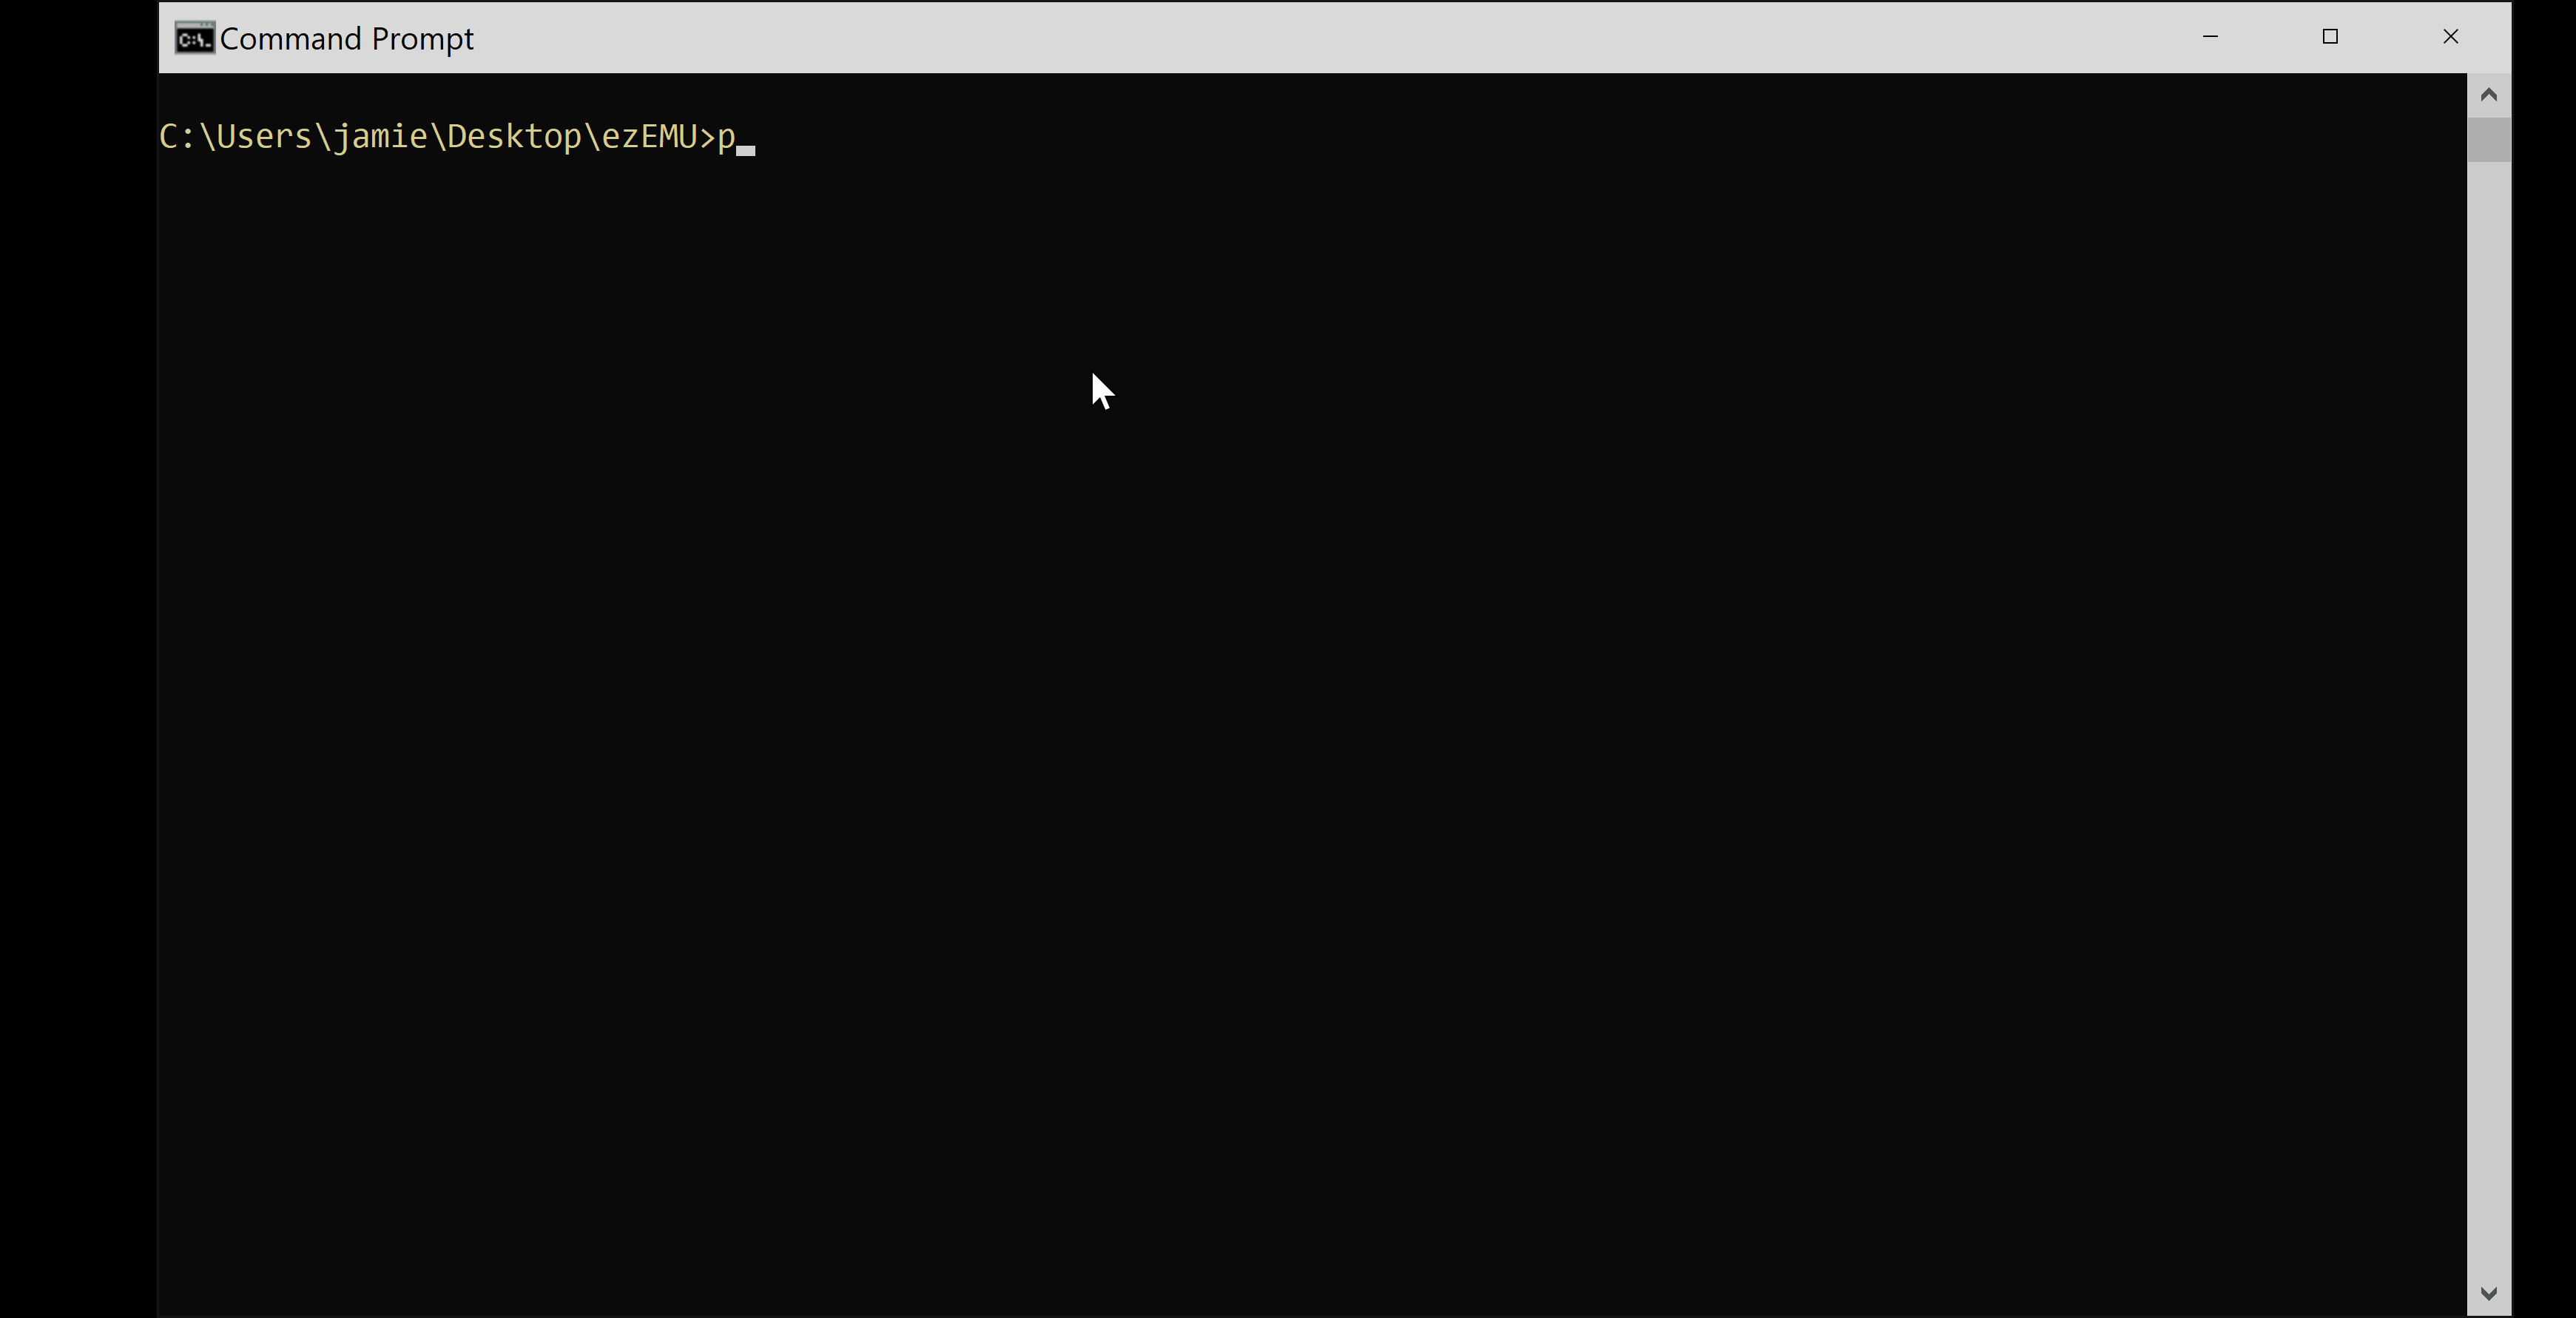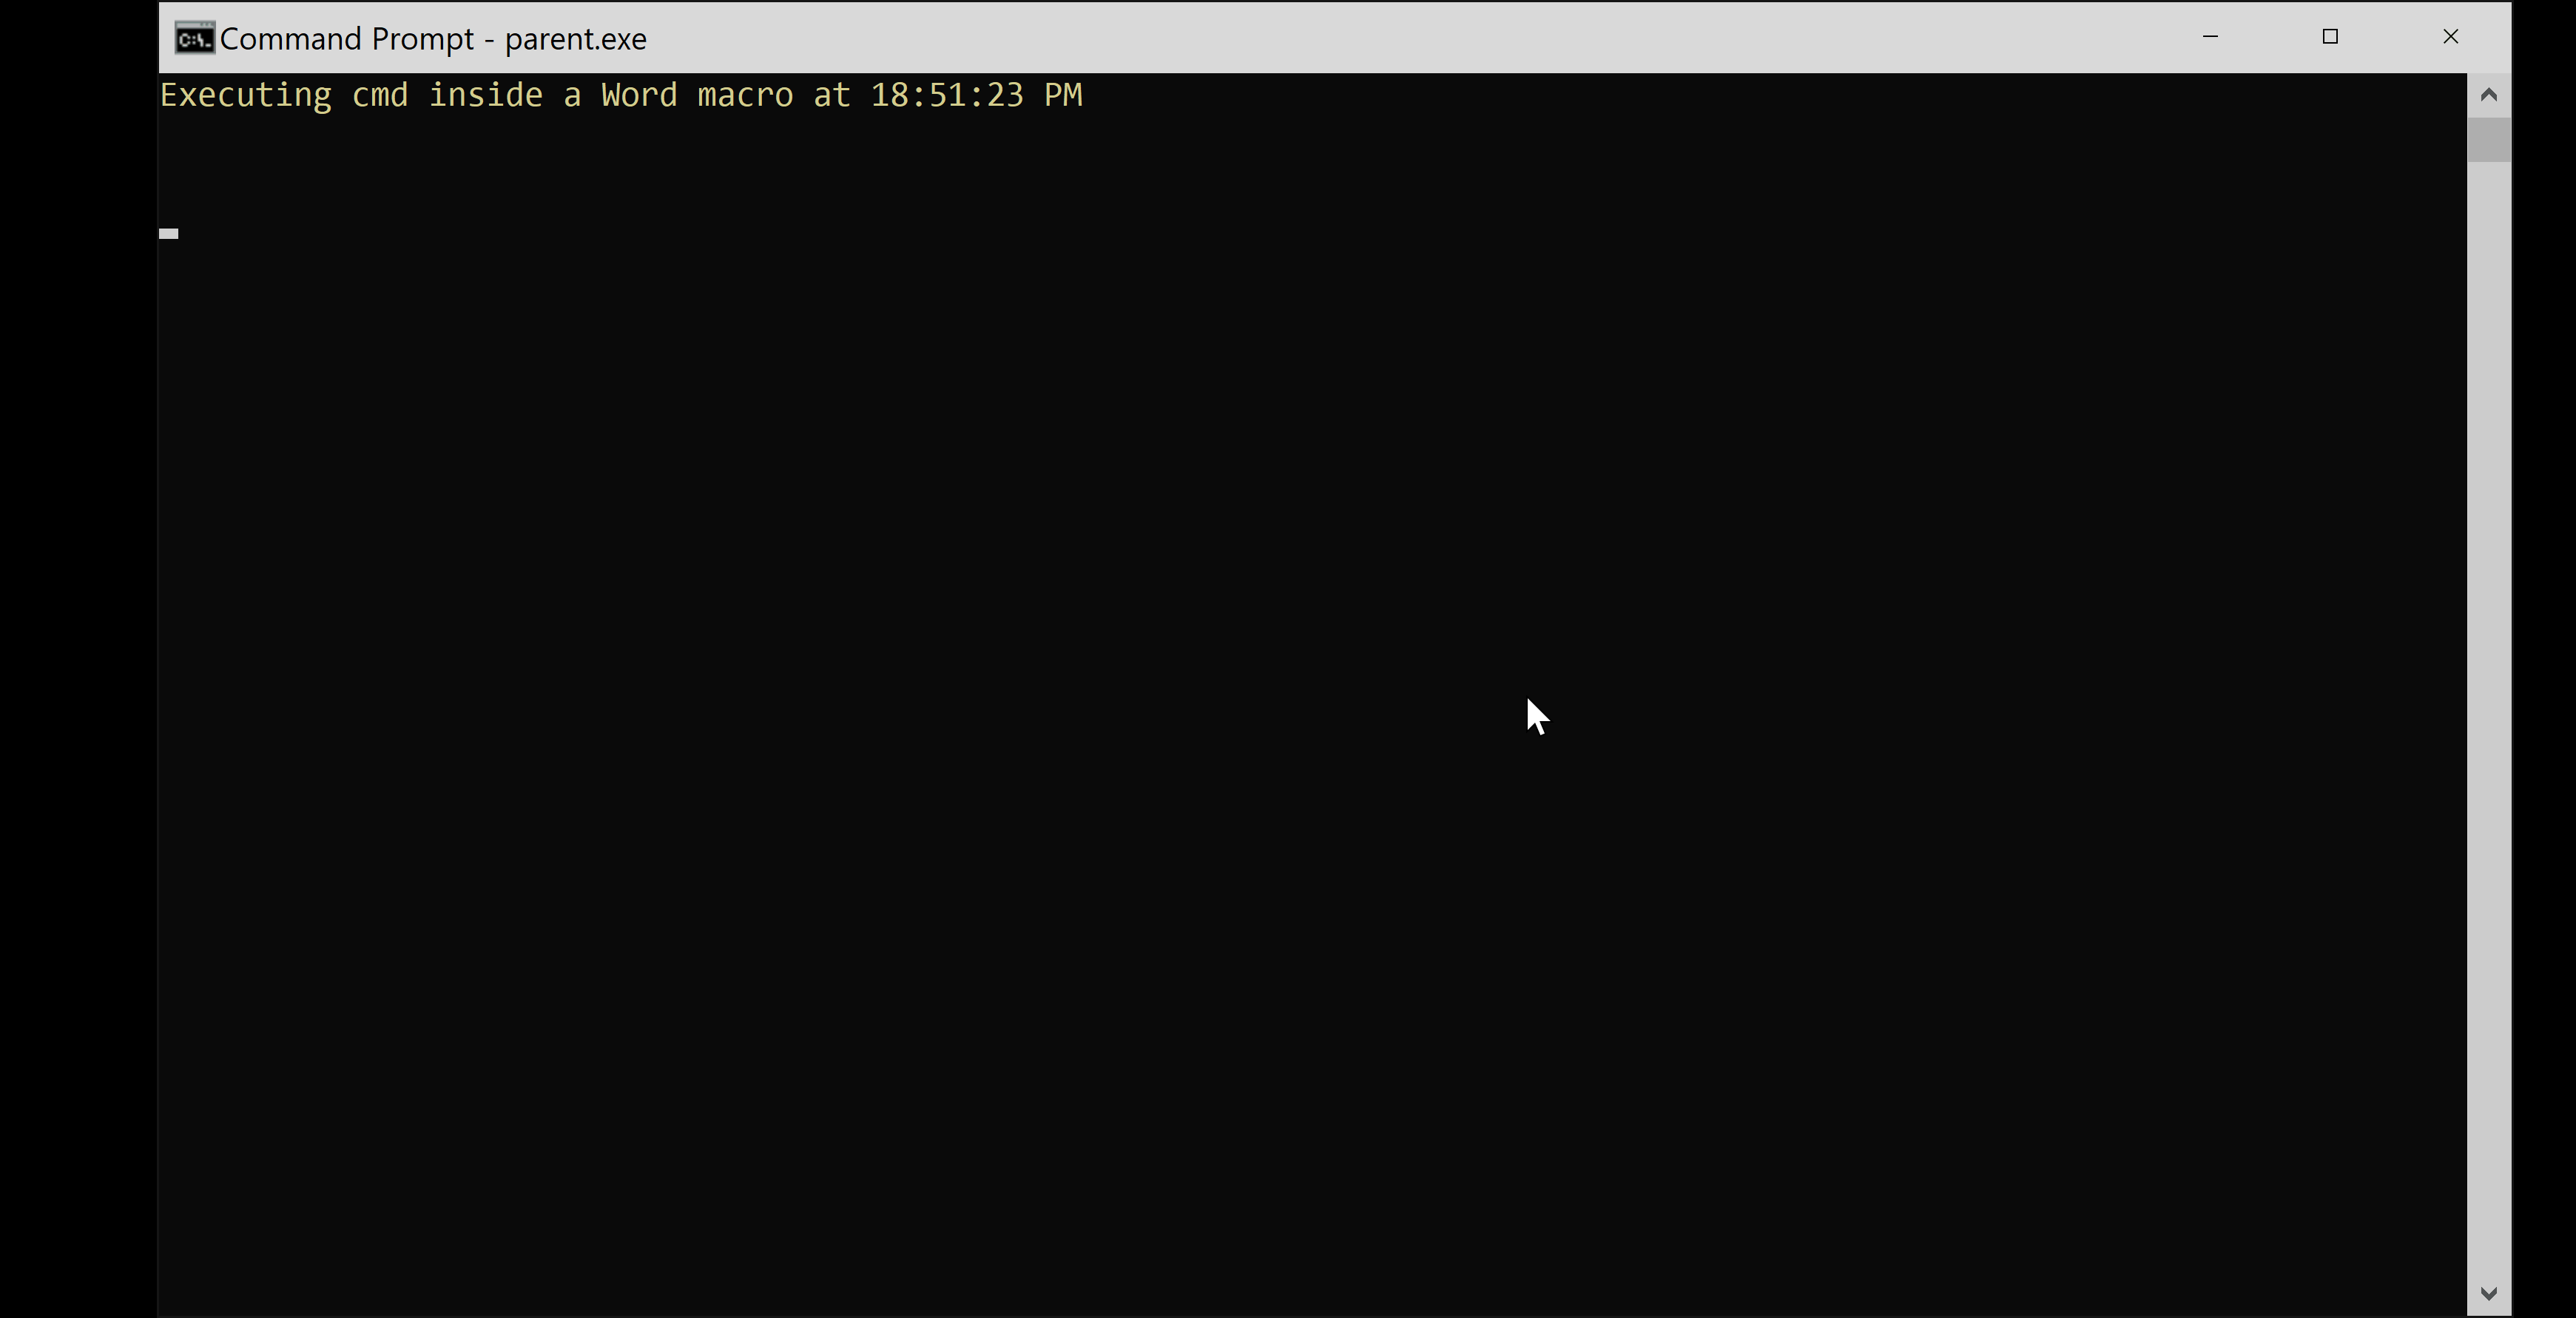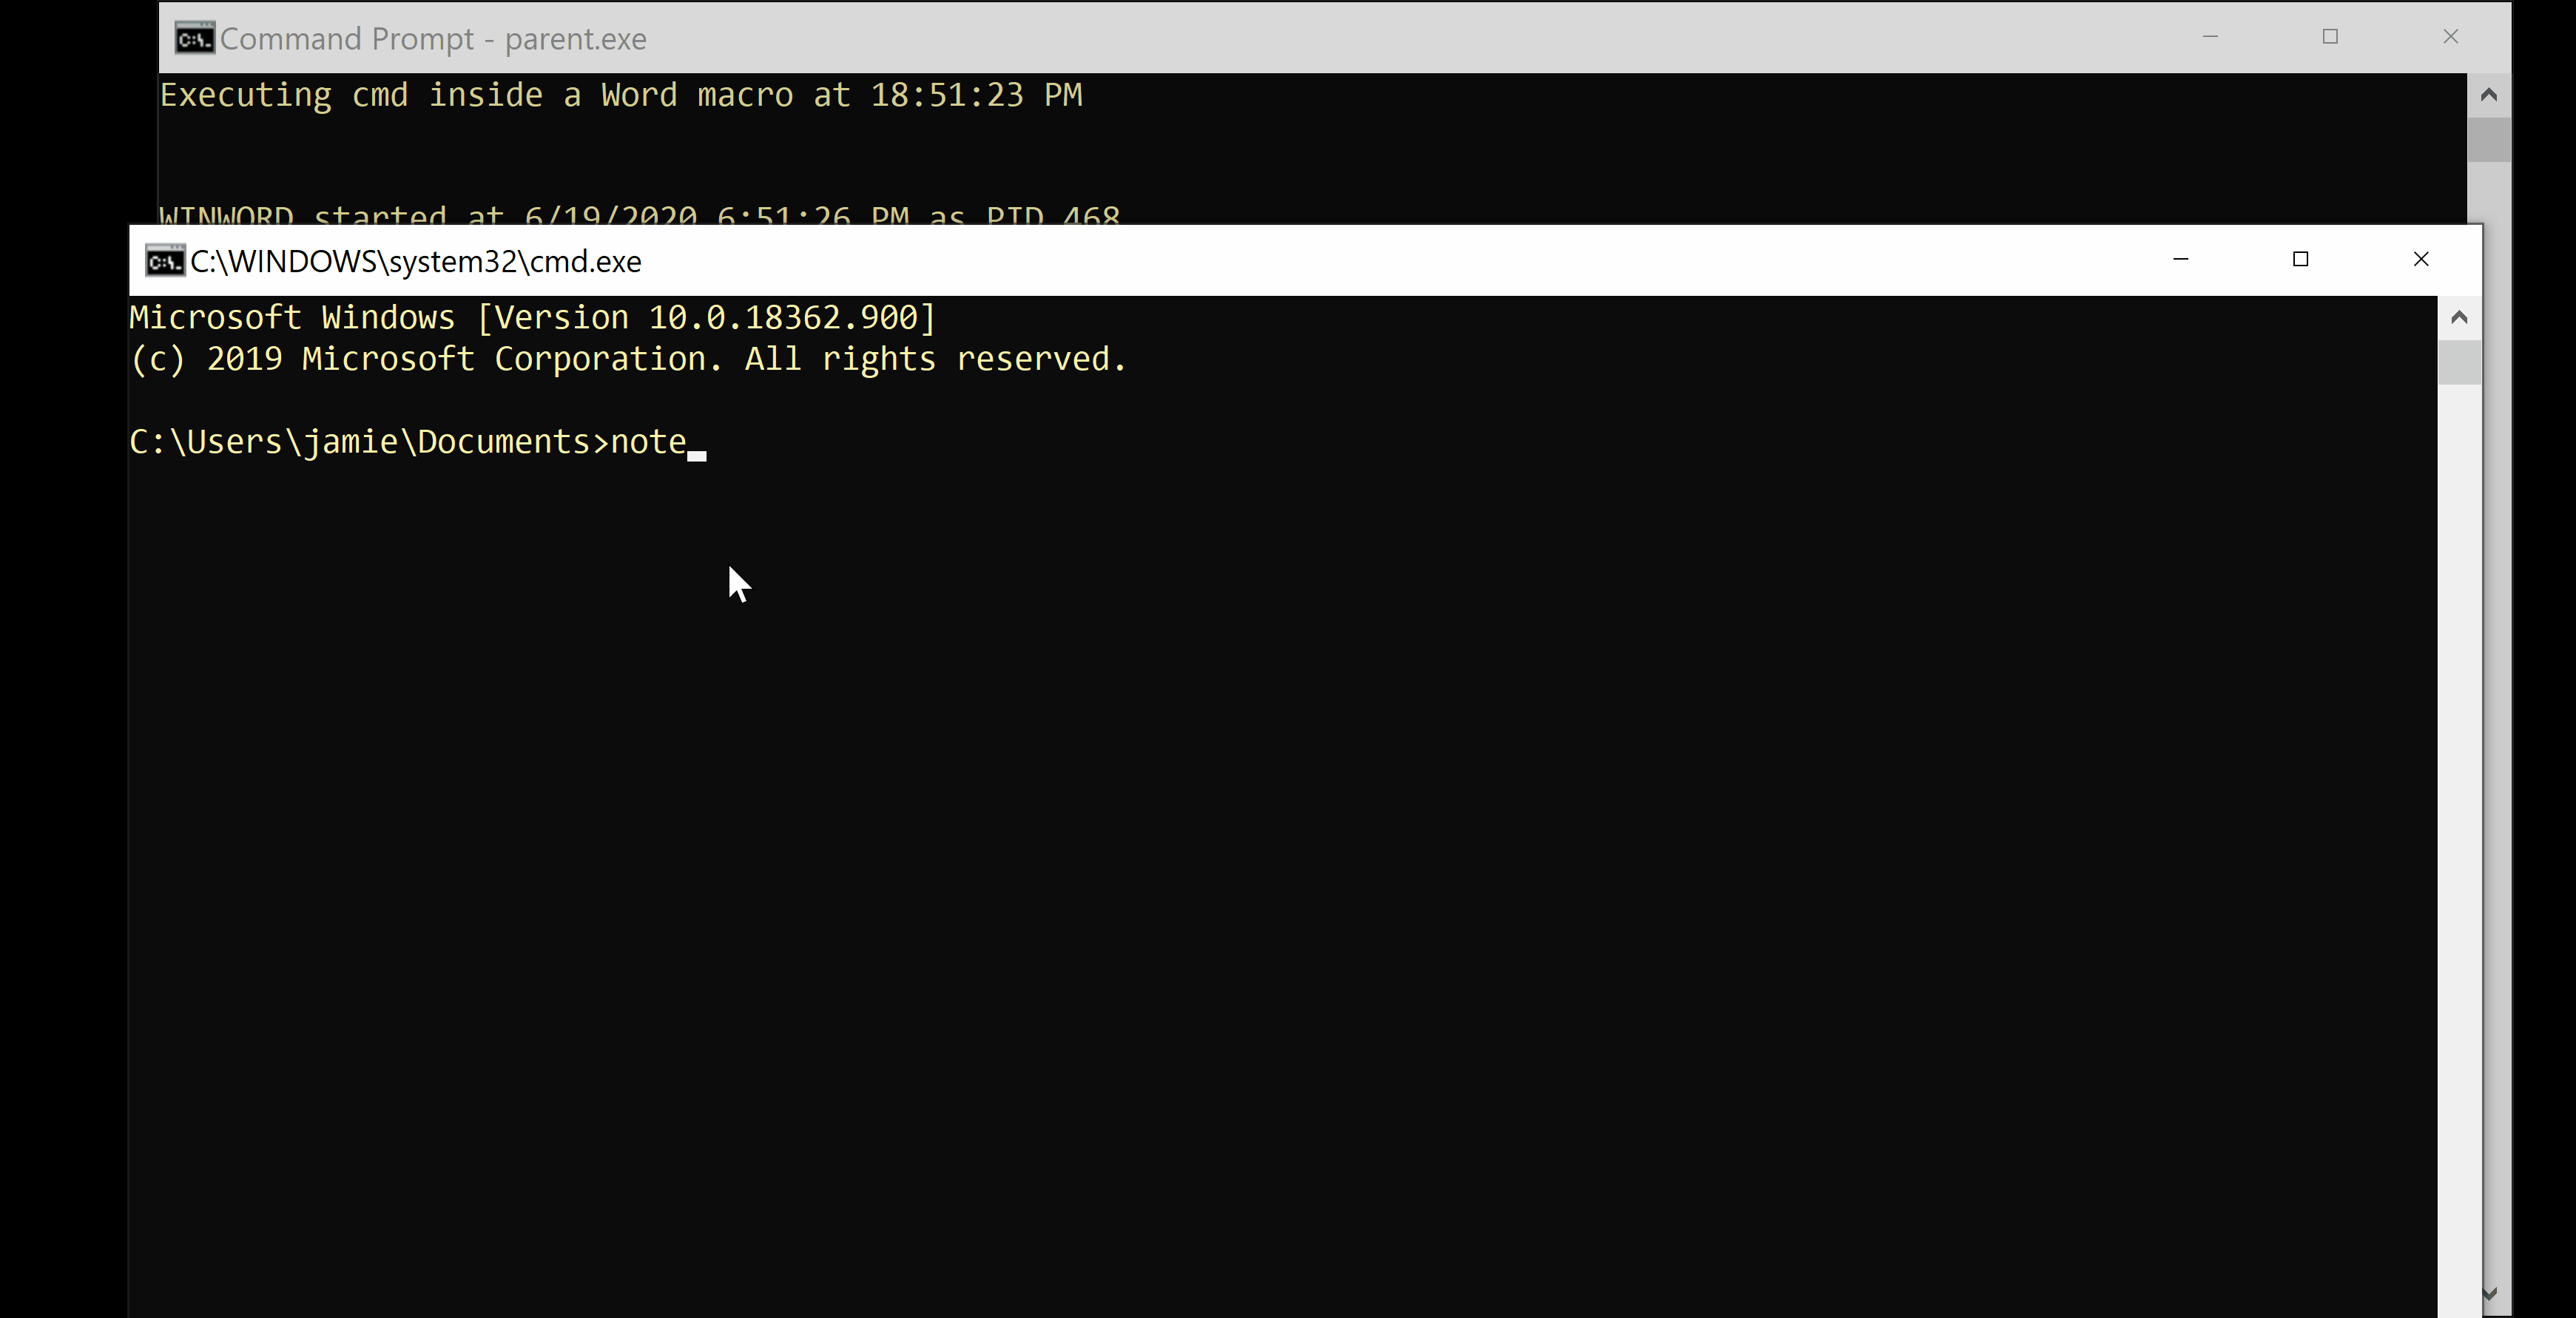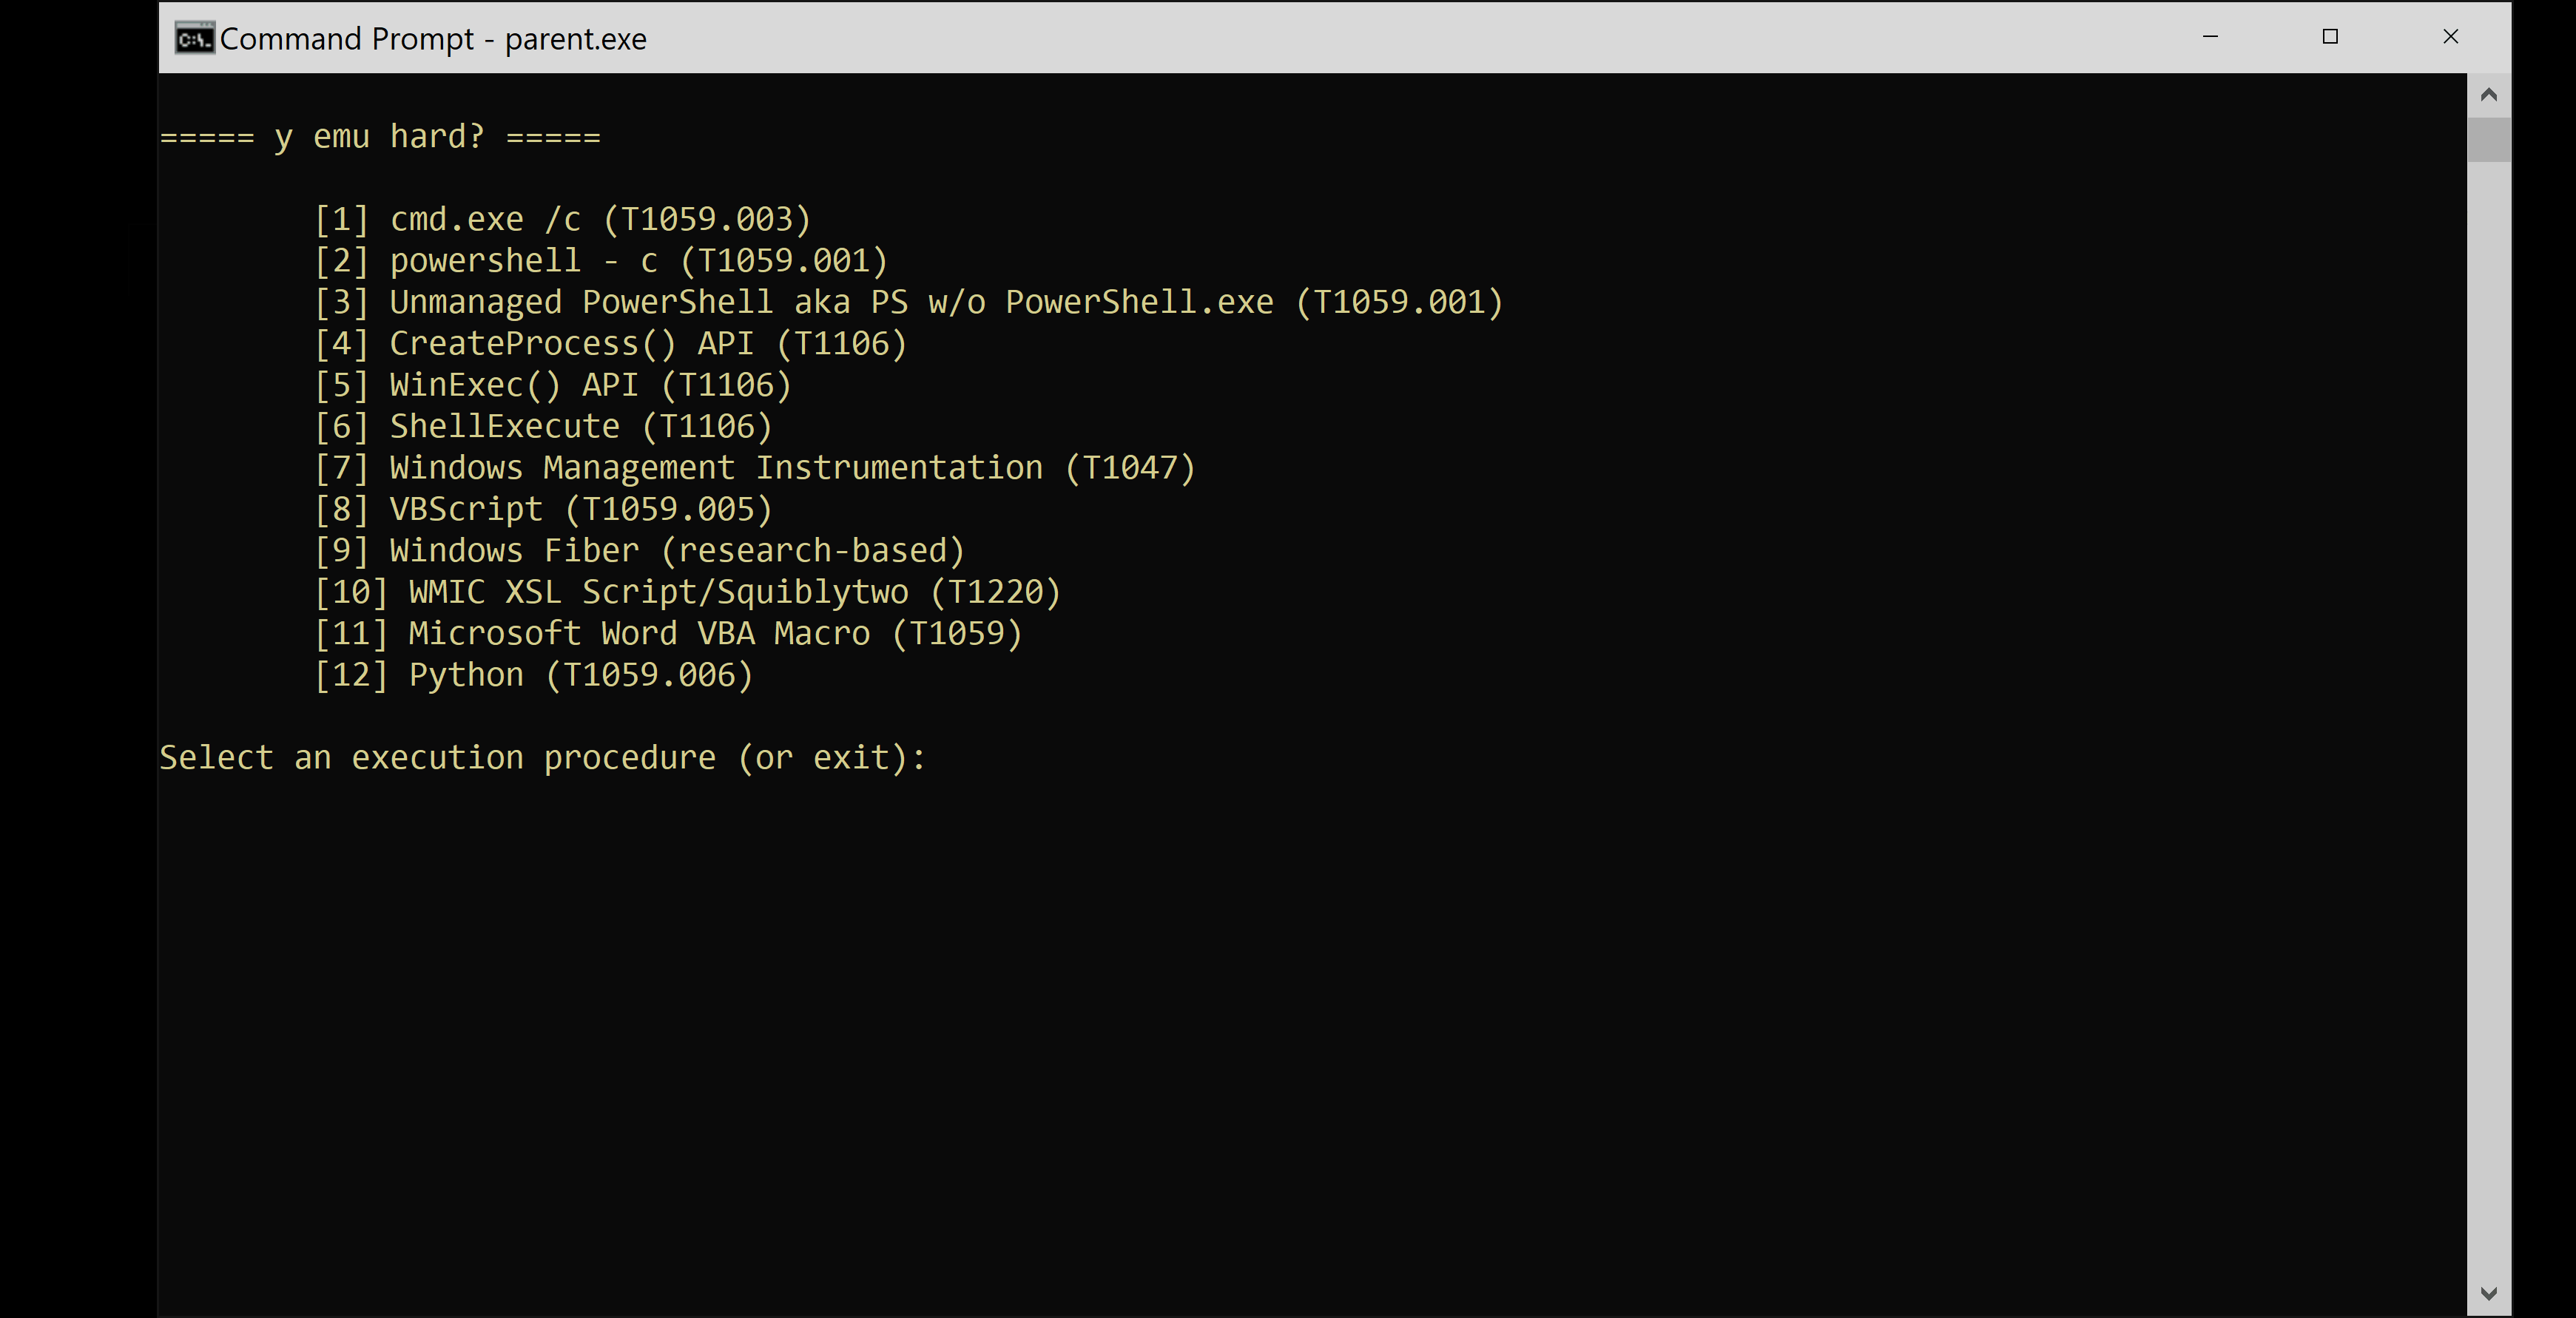
ezEmu Demo

Compile with reference to a few local DLL dependencies

(ex: csc /r:Microsoft.Office.Interop.Word.dll,Microsoft.Vbe.Interop.dll,System.Management.Automation.dll parent.cs)

Feedback/Contribute

This started as just simple personal research/putzing and is definitely not intended to be "clean code" (this is very much Jamie-code™️). That said, I am happy to accept issues and further suggestions!

TODO: Log output file (perhaps), more CTI + learning >> more execution techniques (always)


Notice

©2020 The MITRE Corporation. All Rights Reserved.

Approved for Public Release; Distribution Unlimited. Case Number 20-1357.

Licensed under the Apache License, Version 2.0 (the "License"); you may not use this file except in compliance with the License. You may obtain a copy of the License at

http://www.apache.org/licenses/LICENSE-2.0

Unless required by applicable law or agreed to in writing, software distributed under the License is distributed on an "AS IS" BASIS, WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied. See the License for the specific language governing permissions and limitations under the License.

The author's affiliation with The MITRE Corporation is provided for identification purposes only, and is not intended to convey or imply MITRE's concurrence with, or support for, the positions, opinions or view points expressed by the author.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →




