
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-0708 — Scanner PoC for CVE-2019-0708 RDP RCE vuln | Kitploit

Tools/GitHubGitHub/victor0013/cve-2019-0708
Vulnerability ScannersExploit FrameworksExploitationWeb Application ExploitationNetwork SecurityPenetration Testing
GitHubvictor0013/cve-2019-0708

CVE-2019-0708

Scanner PoC for CVE-2019-0708 RDP RCE vuln

View Repository
3362307 years agoNot yet reviewed
Share

CVE-2019-0708

CVE-2019-0708 Scanner PoC by @JaGoTu and @zerosum0x0.
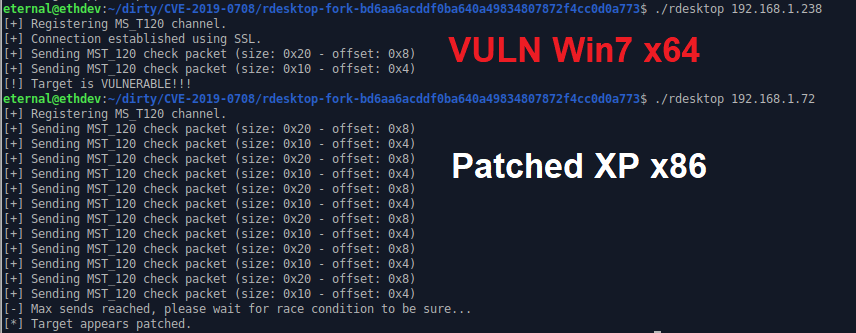
CVE-2019-0708 Scanner

In this repo

A scanner fork of rdesktop that can detect if a host is vulnerable to CVE-2019-0708 Microsoft Windows Remote Desktop Services Remote Code Execution vulnerability.

It shouldn't cause denial-of-service, but there is no 100% guarantee across all vulnerable versions of the RDP stack over the years.

There is also a Metasploit module, which is a current work in progress (MSF does not have an RDP library).

Building

There is a pre-made binary, but the steps to building from source are as follows:

git clone https://github.com/zerosum0x0/CVE-2019-0708.git
cd CVE-2019-0708/rdesktop-fork-bd6aa6acddf0ba640a49834807872f4cc0d0a773/
./bootstrap
./configure --disable-credssp --disable-smartcard
make

Please refer to the normal rdesktop compilation instructions.

Is this dangerous?

Small details of the vulnerability have already begun to reach mainstream. This tool in no way enables attackers to achieve a theoretical RCE.

Modifying this PoC to trigger the denial-of-service does lower the bar but will also require some amount of effort. We offer no explanation of how this scanner works other than to tell the user it seems to be accurate in testing and follows a logical path.

System administrators need tools like this to discover vulnerable hosts. This tool is offered for legal purposes only and to forward the security community's understanding of this vulnerability.

License

rdesktop fork is licensed as GPLv3.

Metasploit module is licensed as Apache 2.0.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





