
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-39031 — Stored Cross-Side Scripting (XSS) leads to privilege escalation in SilverPeas social-networking portal | Kitploit
Tools/GitHubGitHub/toneemarqus/cve-2024-39031
Privilege EscalationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & Education
GitHubtoneemarqus/cve-2024-39031

CVE-2024-39031

Stored Cross-Side Scripting (XSS) leads to privilege escalation in SilverPeas social-networking portal

View Repository
222 years agoNot yet reviewed
Share

CVE-2024-39031 : Silverpeas Core Stored XSS in in Mes agendas

Information

Description: In Mes Agendas, a user can create new events and add them to their calendar. Additionally, users can invite others from the same domain, including administrators, to these events. A standard user can inject an XSS payload into the "Titre" and "Description" fields when creating an event and then add the administrator or any user to the event. When the invited user (victim) views their own profile, the payload will be executed on their side, even if they do not click on the event.

Versions Affected: <= 6.3.5

Version Fixed: 6.3.5

Researcher: Tonee Marqus with Phronesis Security (https://www.phronesissecurity.com/)

Applied Fix: https://github.com/Silverpeas/Silverpeas-Core/pull/1346

Related Links:

  • https://security.snyk.io/vuln/SNYK-JAVA-ORGSILVERPEASCORE-7443649
  • https://avd.aquasec.com/nvd/2024/cve-2024-39031/
  • https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2024-39031
  • https://nvd.nist.gov/vuln/detail/CVE-2024-39031

Proof-of-Concept

Step 1

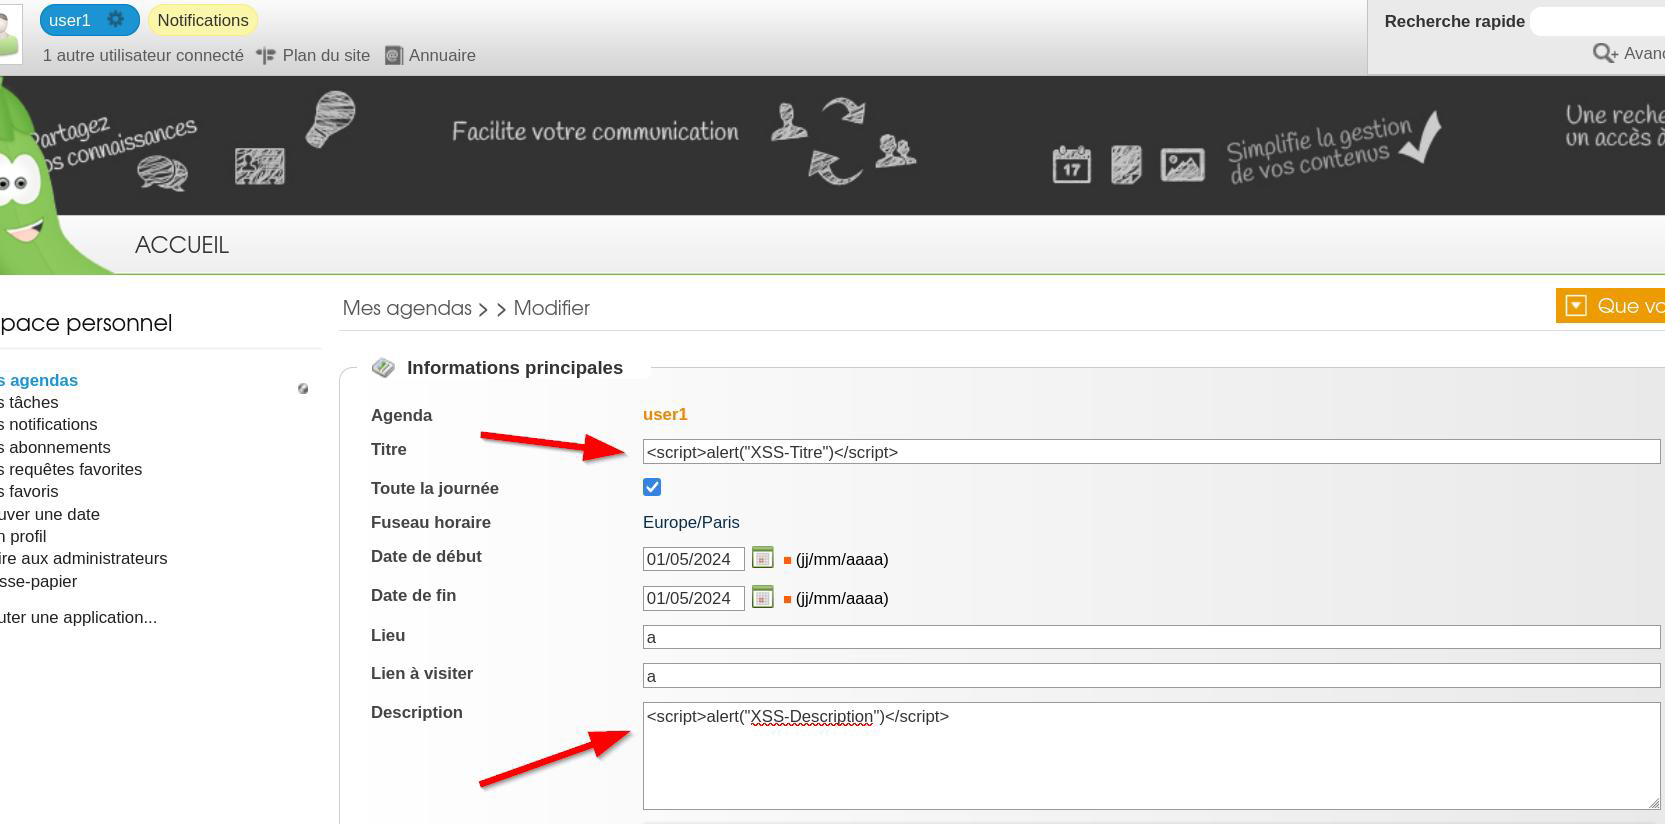
login as an any user and create a new event (agenda) in the mes agendas. Inside the “Titre” and “Description” put the following XSS payloads:

<script>alert("XSS-Titre")</script>

And

<script>alert("XSS-Description")</script>
image

Step 2

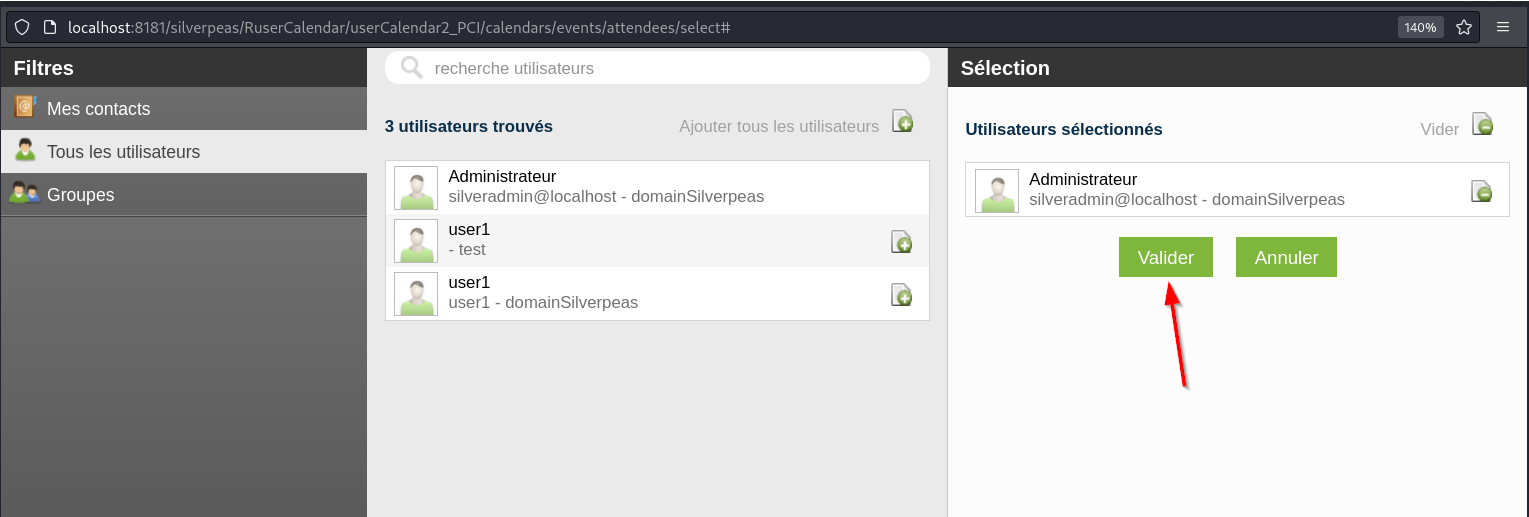
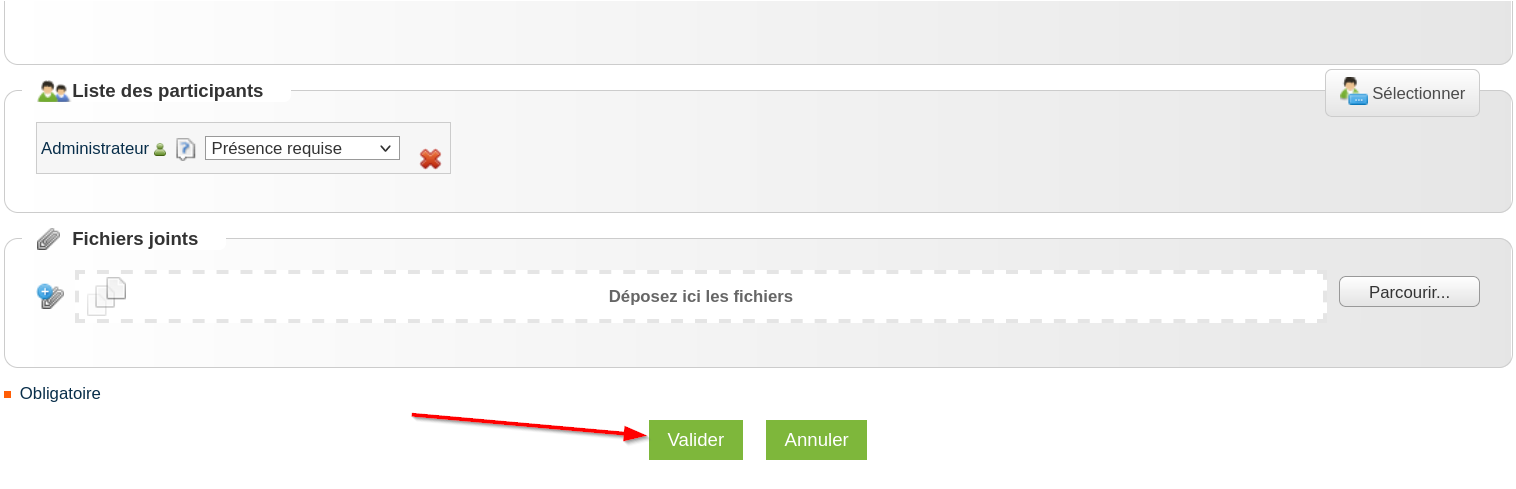
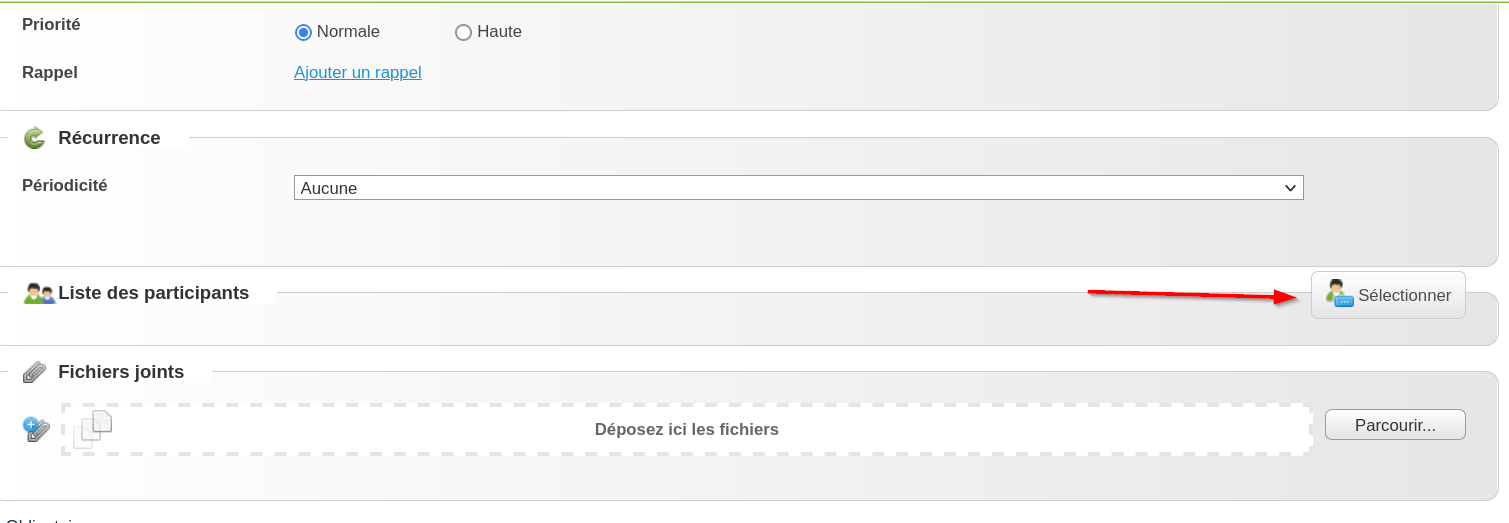
Add another user as a participant, for example, here an administrator was added. image image Save the event: image
Step 3

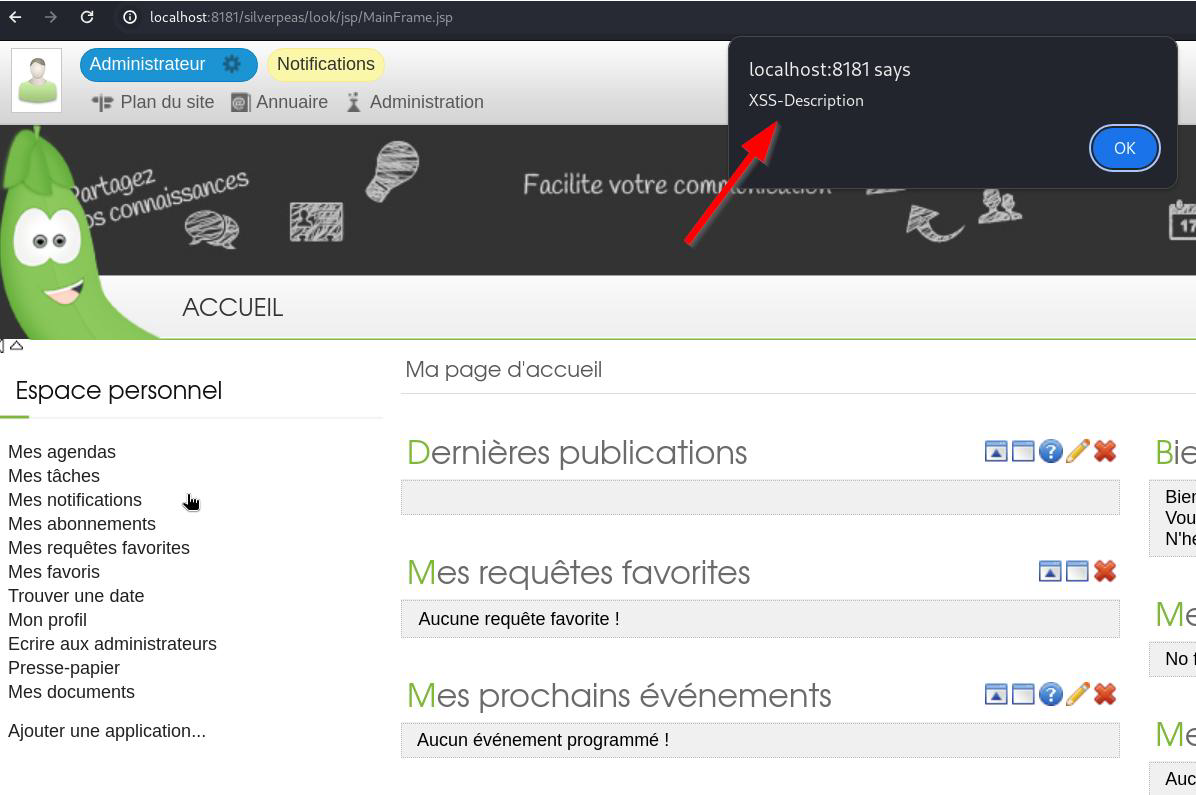
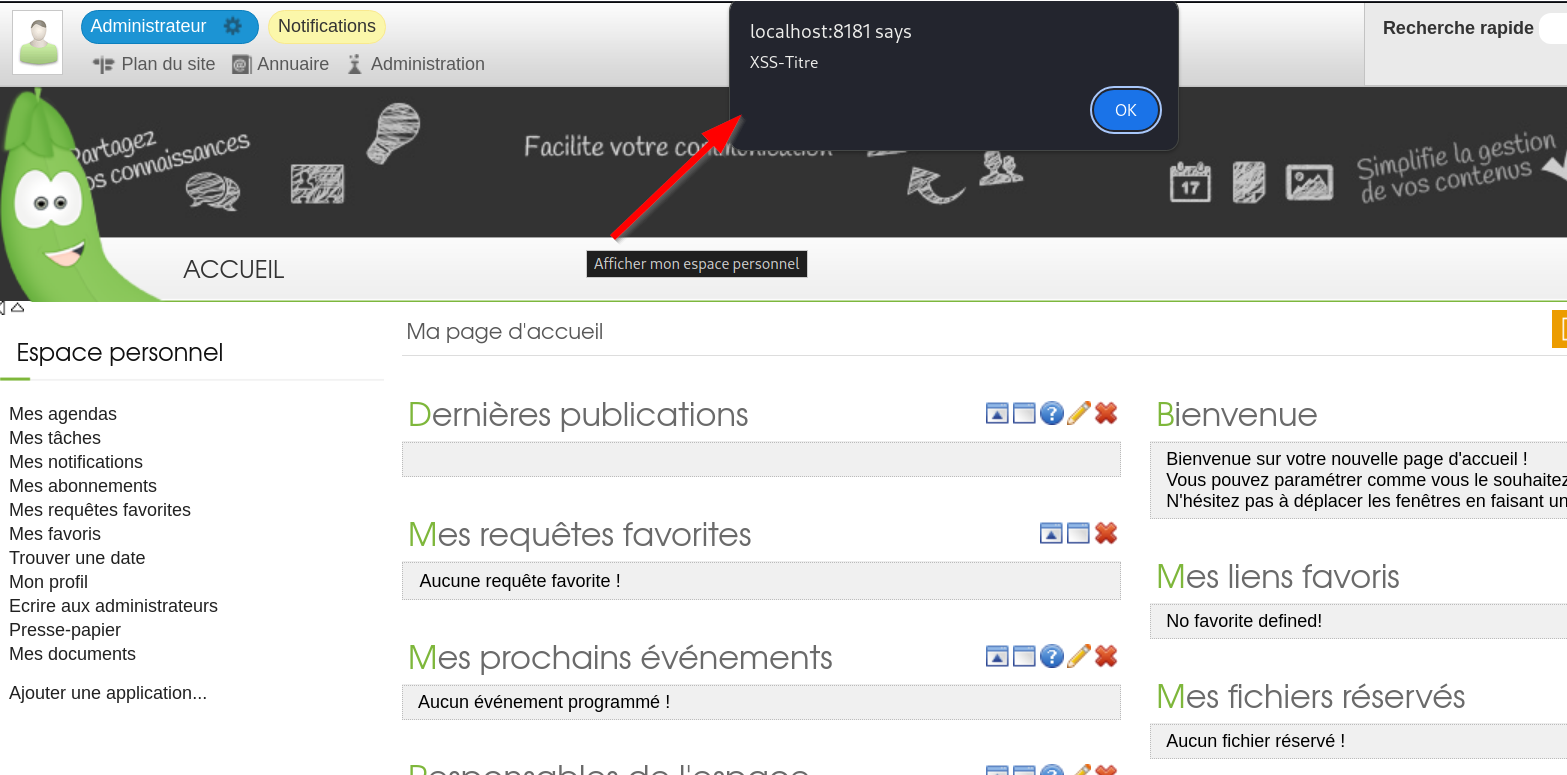
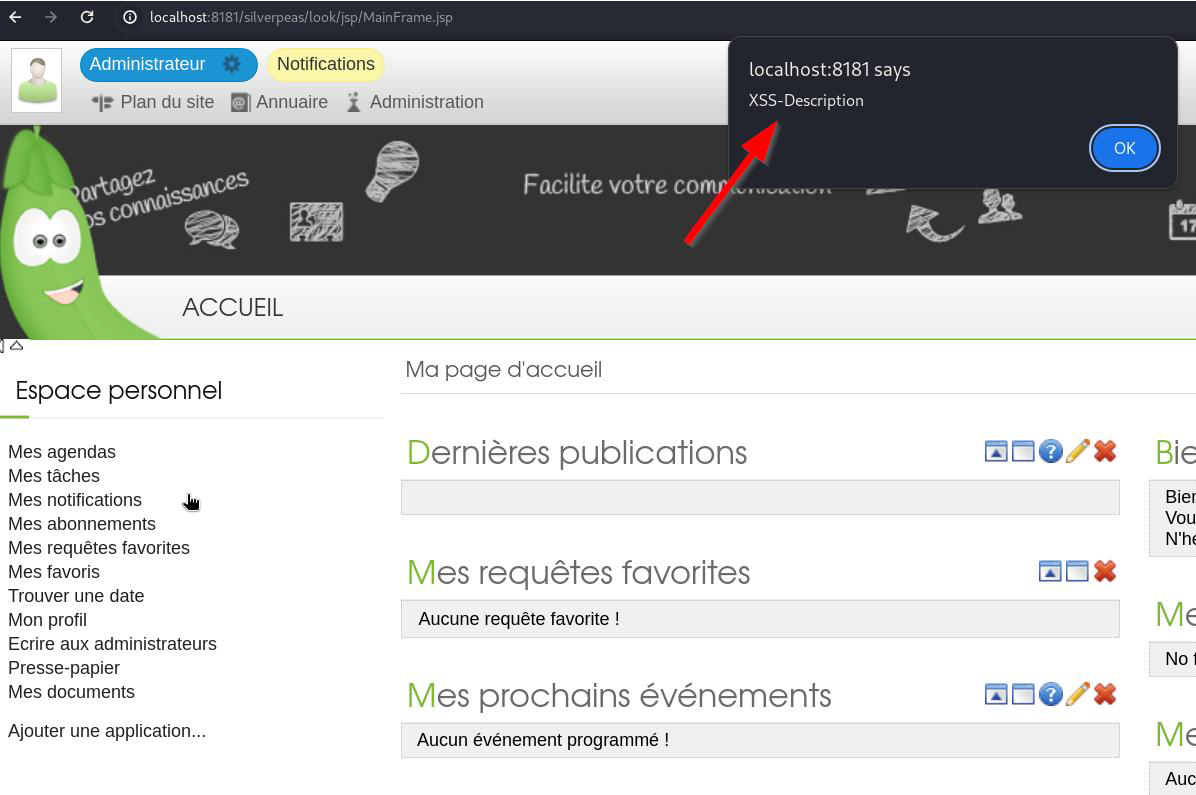
Login to the administrator account and click on the administrator button in the top left to enter administrator profile, once you click, the XSS alert for “Titre” will pop up. image If you click OK, the other XSS payload will also pop up for “description” image
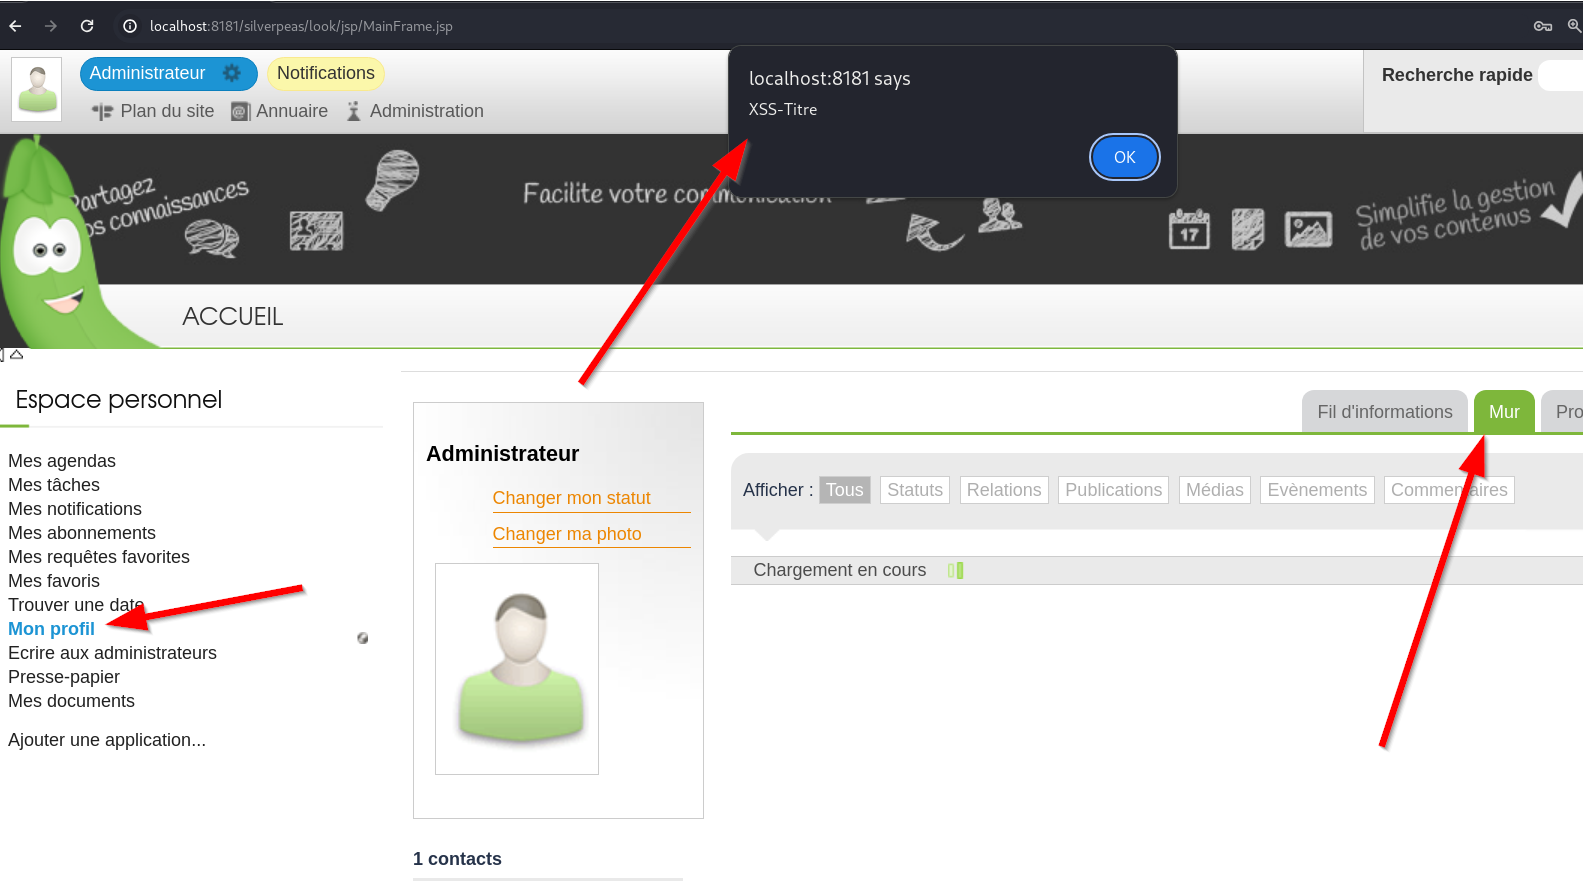
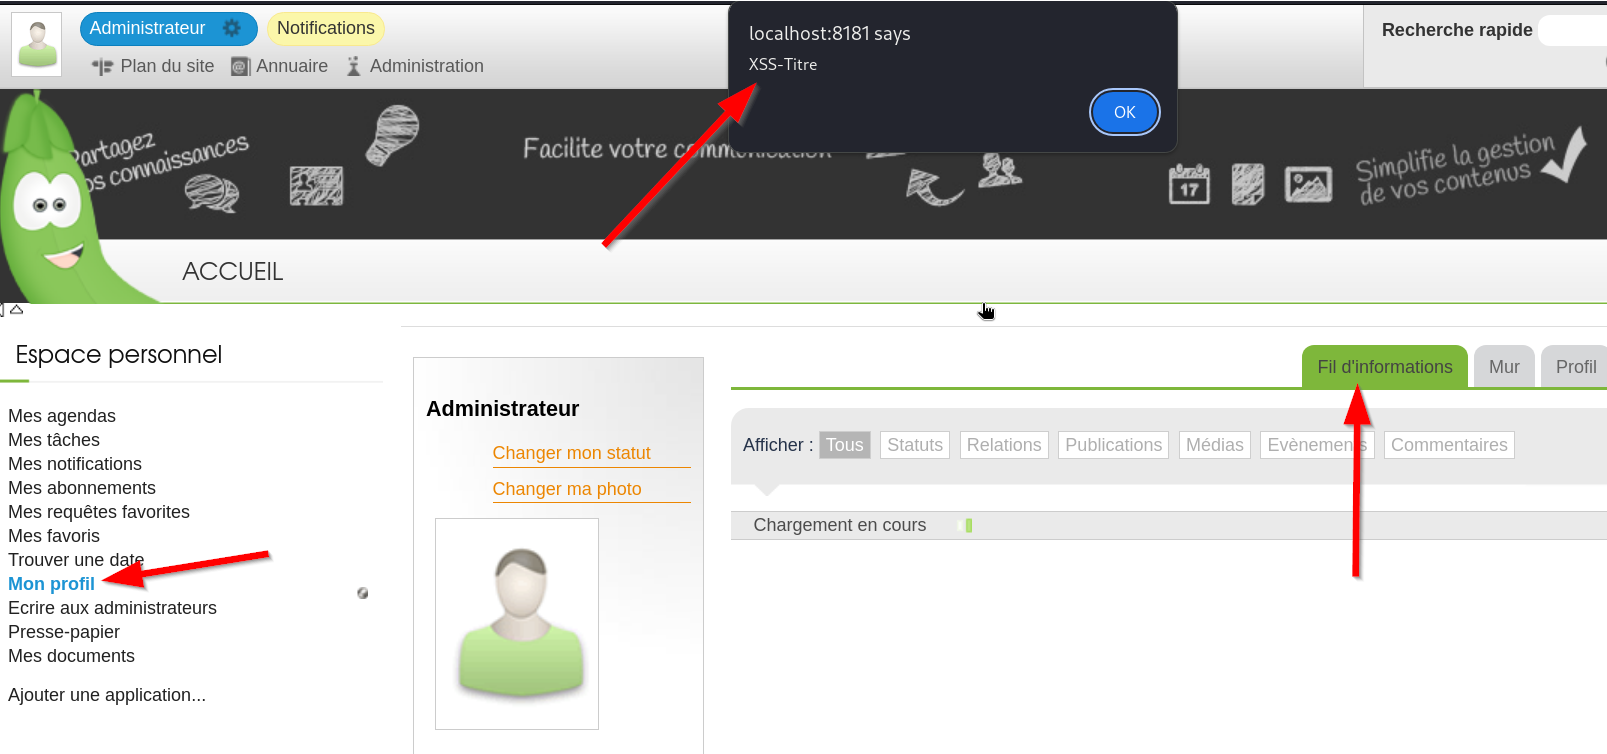
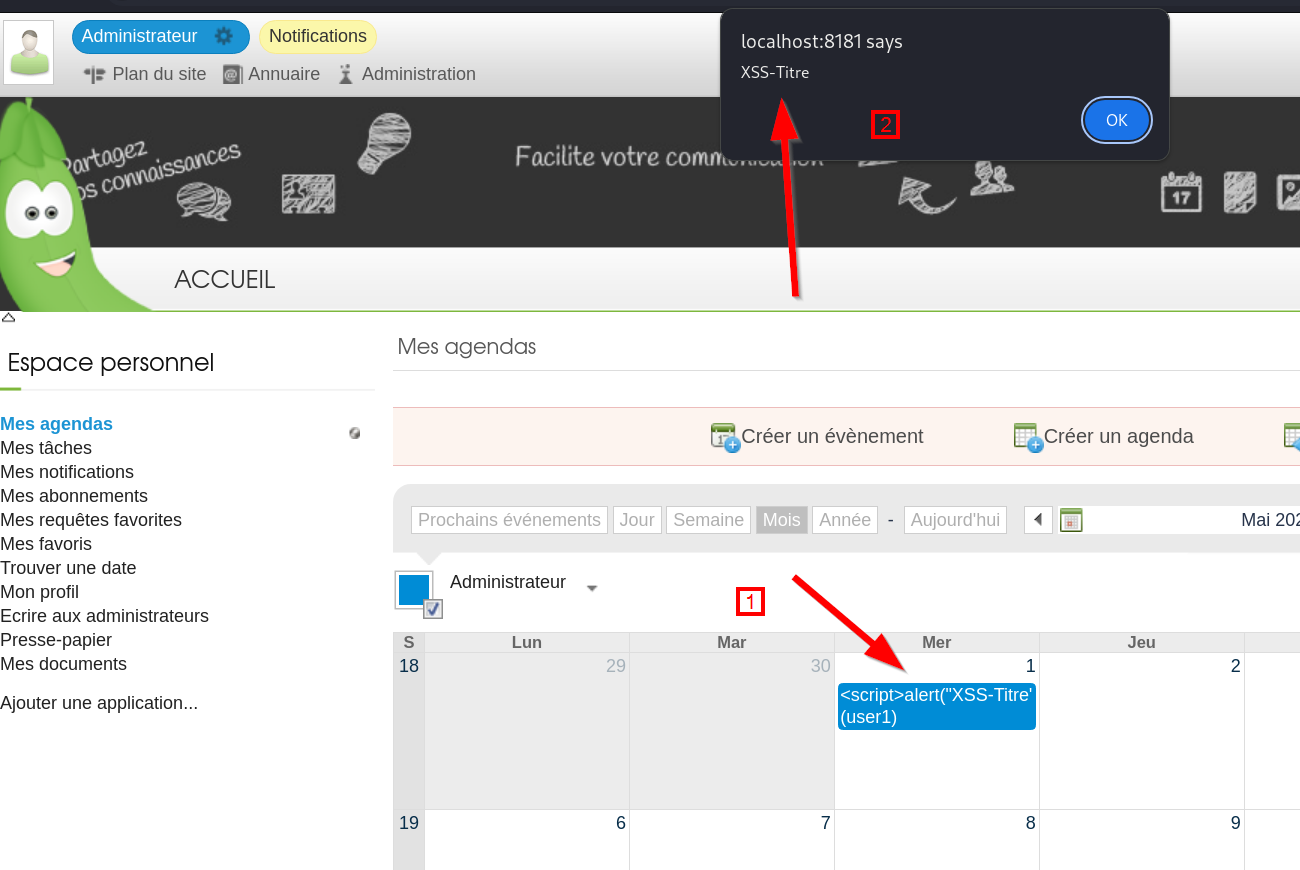
Additionally, the XSS payload can be triggered in many other places, for example when we click on the event from the calendar: image Or from Mon profile → Mur image Finally, from Fil d'informations: image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    565
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    327
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    258
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    256

Explore all tools

Browse our collection of tools

View all tools →