
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-39459 — Unauthenticated Privilege Escalation | Kitploit
Tools/GitHubGitHub/thebl4ckph4nt0m/cve-2025-39459
Privilege EscalationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationRed Teaming
GitHubthebl4ckph4nt0m/cve-2025-39459

CVE-2025-39459

Unauthenticated Privilege Escalation

View Repository
11178 months agoNot yet reviewed
Share

CVE-2025-39459

Real Estate 7 <= 3.5.2 - Unauthenticated Privilege Escalation
🧨 CVE-2025-39459 — Real Estate 7 (<= 3.5.2) Unauthenticated Privilege Escalation

Nxploited

📌 Overview

This repository contains a Python proof-of-concept tool for CVE-2025-39459, affecting the Real Estate 7 WordPress theme in versions <= 3.5.2.

The vulnerability allows an unauthenticated attacker to register a new user and escalate privileges to administrator, resulting in full site compromise.

  • Product: Real Estate 7 (WordPress theme)
  • Vulnerability: Unauthenticated Privilege Escalation
  • Affected versions: <= 3.5.2
  • CVE: CVE-2025-39459
  • CVSS: 9.8 (Critical)

⚙️ How It Works (High Level)

The script:

  1. Reads targets from a file (default: list.txt)
  2. For each target, requests the registration page to extract a nonce (ct_register_nonce)
  3. Submits a crafted request to wp-admin/admin-ajax.php (action=ct_add_new_member) with:
    • a randomized username/email
    • a fixed password (default: xplpass)
    • administrator role specified in the payload
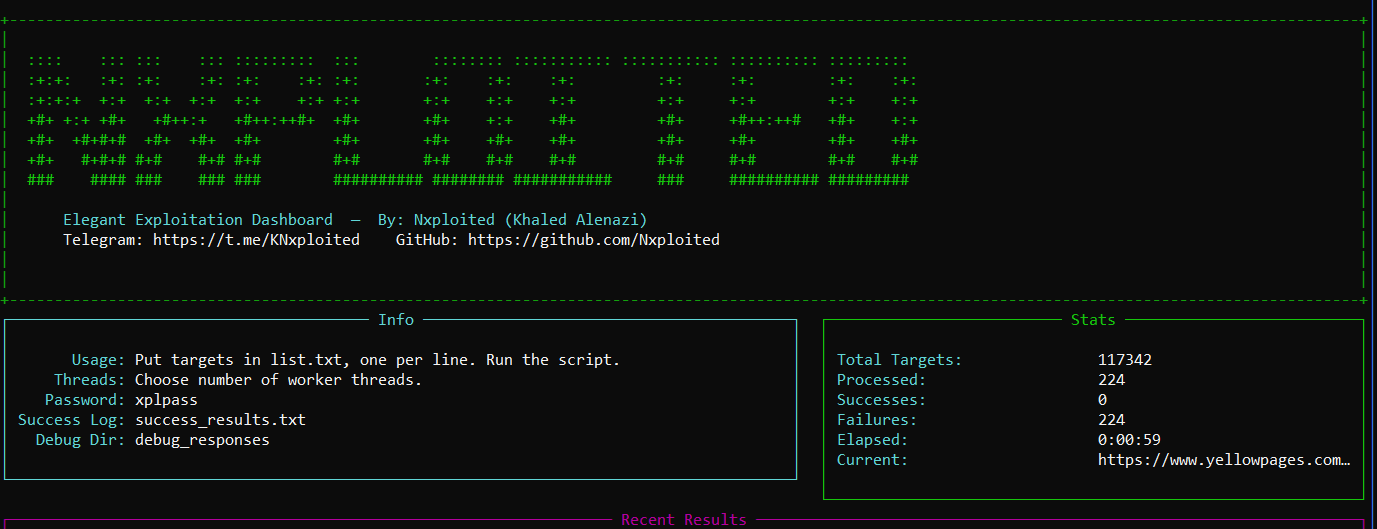
  4. If exploitation succeeds, the created credentials are saved to success_results.txt
  5. Debug responses are written to debug_responses/ for troubleshooting and validation

🧰 Features

  • Multi-threaded scanning/exploitation (configurable threads)
  • Clean Rich-based dashboard:
    • total/processed/success/fail stats
    • current target
    • recent results table
  • Automatic nonce extraction
  • Automatic credential generation (prefix: Nxploited_####)
  • Output logging:
    • success_results.txt for successful hits
    • debug_responses/ for captured server responses

✅ Requirements

  • Python 3.9+ recommended
  • Dependencies:
    • requests
    • urllib3
    • rich

Install:

pip install -r requirements.txt

If you don’t have requirements.txt, install directly:

pip install requests urllib3 rich

🚀 Usage

1) Prepare targets

Create list.txt (one target per line):

https://example.com
http://target.tld
target-without-scheme.com

The tool will auto-add http:// if the scheme is missing.

2) Run

python3 CVE-2025-39459.py

You will be prompted for:

  • Targets file name (default: list.txt)
  • Number of threads (default: 10)

📁 Output Files

  • success_results.txt
    Contains exploited targets and created credentials in the form:

    https://target | USER: Nxploited_1234 | PASS: xplpass | EMAIL: [email protected]
    
  • debug_responses/
    Stores raw responses for each target (useful when nonce is missing, JSON parsing fails, or the theme isn’t present).


🛠️ Configuration Notes

Key defaults inside the script:

  • Password: xplpass
  • Username prefix: Nxploited
  • Threads default: 10
  • Requests:
    • verify=False (TLS verification disabled)
    • timeout ~ 16s

If you need to tune speed/stability:

  • Reduce threads for slower networks
  • Increase timeout if targets respond slowly

🔎 Vulnerability Details

Real Estate 7 <= 3.5.2 — Unauthenticated Privilege Escalation

Description
The Real Estate 7 WordPress theme is vulnerable to Privilege Escalation in all versions up to, and including, 3.5.2. This makes it possible for unauthenticated attackers to elevate their privileges to that of an administrator.

  • CVE: CVE-2025-39459
  • CVSS: 9.8 (Critical)
  • By: Nxploited

⚠️ Disclaimer

This project is provided for educational and authorized security testing purposes only.
You are responsible for complying with all applicable laws and regulations.
Do not use this tool against systems you do not own or do not have explicit permission to test.
The author(s) assume no liability for misuse or damage caused by this tool.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →




