

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/tea9/cve-2020-0014-toast
Android SecurityVulnerability AnalysisExploitationPenetration TestingMobile SecuritySocial Engineering
GitHubtea9/cve-2020-0014-toast

CVE-2020-0014-Toast

CVE-2020-0014-Toast-复现

View Repository
64446 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    696
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    499
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    396
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    340
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2020-0014 Toast Reproduction

This vulnerability allows a malicious app to intercept user operations on the screen by constructing a clickable Toast view, thereby achieving the purpose of collecting sensitive information such as user passwords.
Affected versions: Android 8.0, 8.1, 9, 10
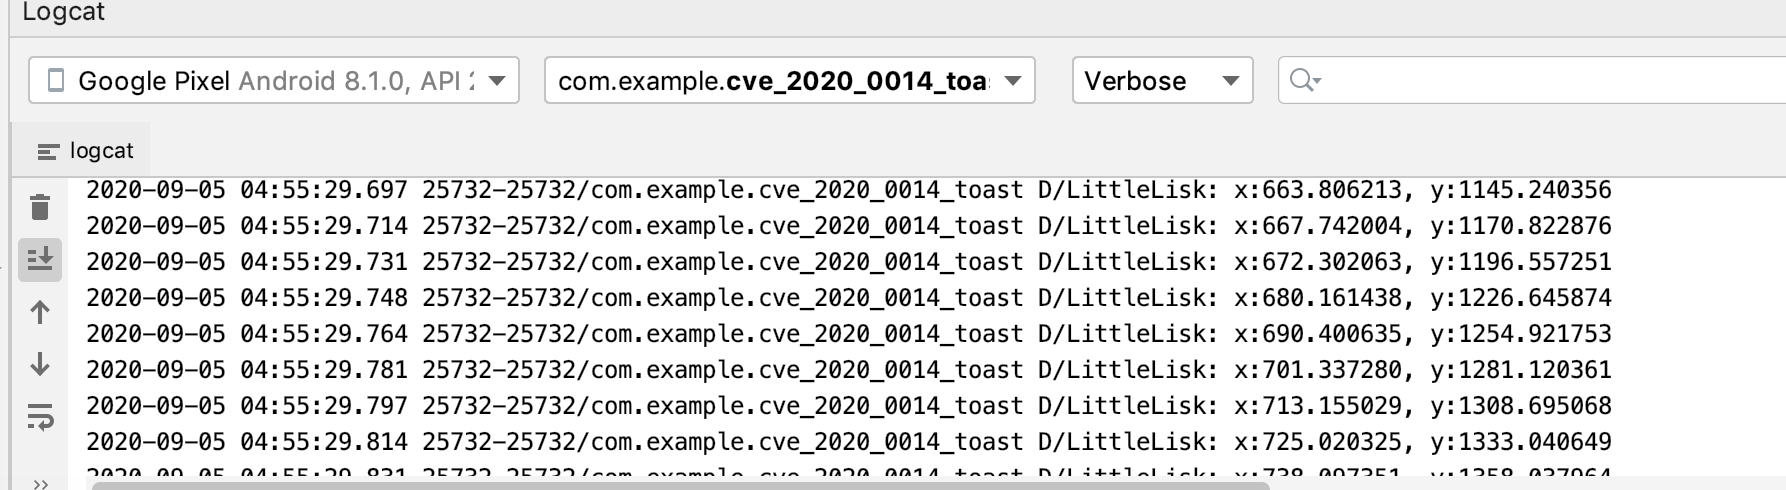
log

Only feasibility has been verified; the actual harm that the vulnerability can cause has not been verified.
release

LINKS

Tapjacking via the latest Android Toast vulnerability
Android Security Bulletin
CVE-2020-0014

Download Tool






