
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Am-I-affected-by-Meltdown — Proof-of-concept / Exploit / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a | Kitploit
Tools/GitHubGitHub/speecyy/am-i-affected-by-meltdown
Vulnerability AnalysisExploitationHardware SecurityBinary AnalysisLearning & Education
GitHubspeecyy/am-i-affected-by-meltdown

Am-I-affected-by-Meltdown

Proof-of-concept / Exploit / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a

View Repository
11298 years agoNot yet reviewed
Share

Am I affected by Meltdown?! Meltdown (CVE-2017-5754) checker

Alt text

What am I?

Proof-of-concept /

Exploit /

Checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.

The basic idea is that user will know whether or not the running system is properly patched with something like KAISER patchset (https://lkml.org/lkml/2017/10/31/884) for example.

*** Only works on Linux for now ***

How it works?

It works by using /proc/kallsyms to find system call table and checking whether the address of a system call found by exploiting MELTDOWN match the respective one in /proc/kallsyms.

What to do when you face this error "Unable to read /proc/kallsyms..."

That's because your system may be preventing the program from reading kernel symbols in /proc/kallsyms due to /proc/sys/kernel/kptr_restrict set to 1. The following command will do the tricky:

sudo sh -c "echo 0  > /proc/sys/kernel/kptr_restrict"

Please open an issue if you have an idea on how to fallback to another approach in this scenario.

Getting started

Run make to compile the project

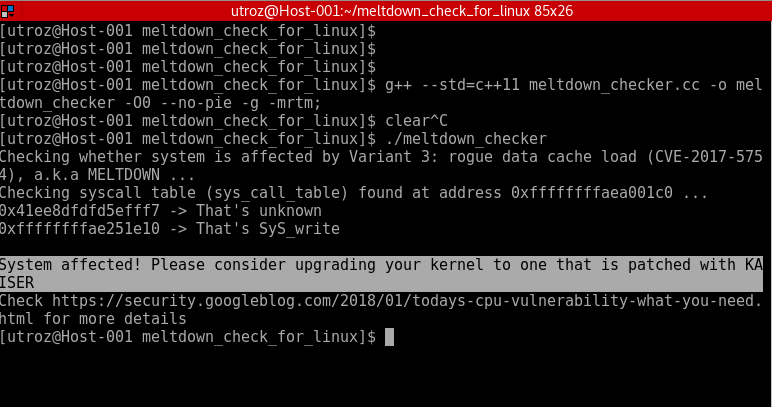
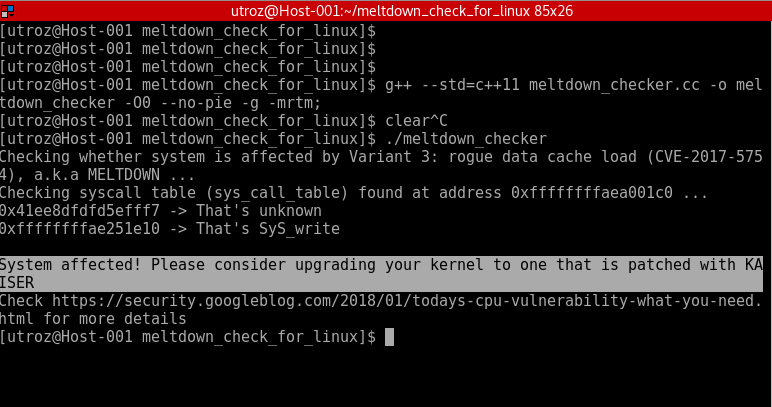
Example output for a system affected by Meltdown:

Alt text

Checking whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN ...
Checking syscall table (sys_call_table) found at address 0xffffffffaea001c0 ...
0xc4c4c4c4c4c4c4c4 -> That's unknown
0xffffffffae251e10 -> That's SyS_write

System affected! Please consider upgrading your kernel to one that is patched with KAISER
Check https://security.googleblog.com/2018/01/todays-cpu-vulnerability-what-you-need.html for more details

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    668
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    496
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    394
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    254

Explore all tools

Browse our collection of tools

View all tools →