Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-0688-Scanner — Quick tool for checking CVE-2020-0688 on multiple hosts with a non-intrusive method. | Kitploit
Tools/GitHubGitHub/onsec-fr/cve-2020-0688-scanner
ReconnaissanceVulnerability ScannersExploitationInformation GatheringWeb SecurityPenetration Testing
GitHubonsec-fr/cve-2020-0688-scanner

CVE-2020-0688-Scanner

Quick tool for checking CVE-2020-0688 on multiple hosts with a non-intrusive method.

View Repository
3710195 years agoReviewed by Kitploit
Share

CVE-2020-0688-Scanner

Quick C# tool for checking CVE-2020-0688 on multiple hosts with a non-intrusive method.

Features

  • Scan hosts from an input file.
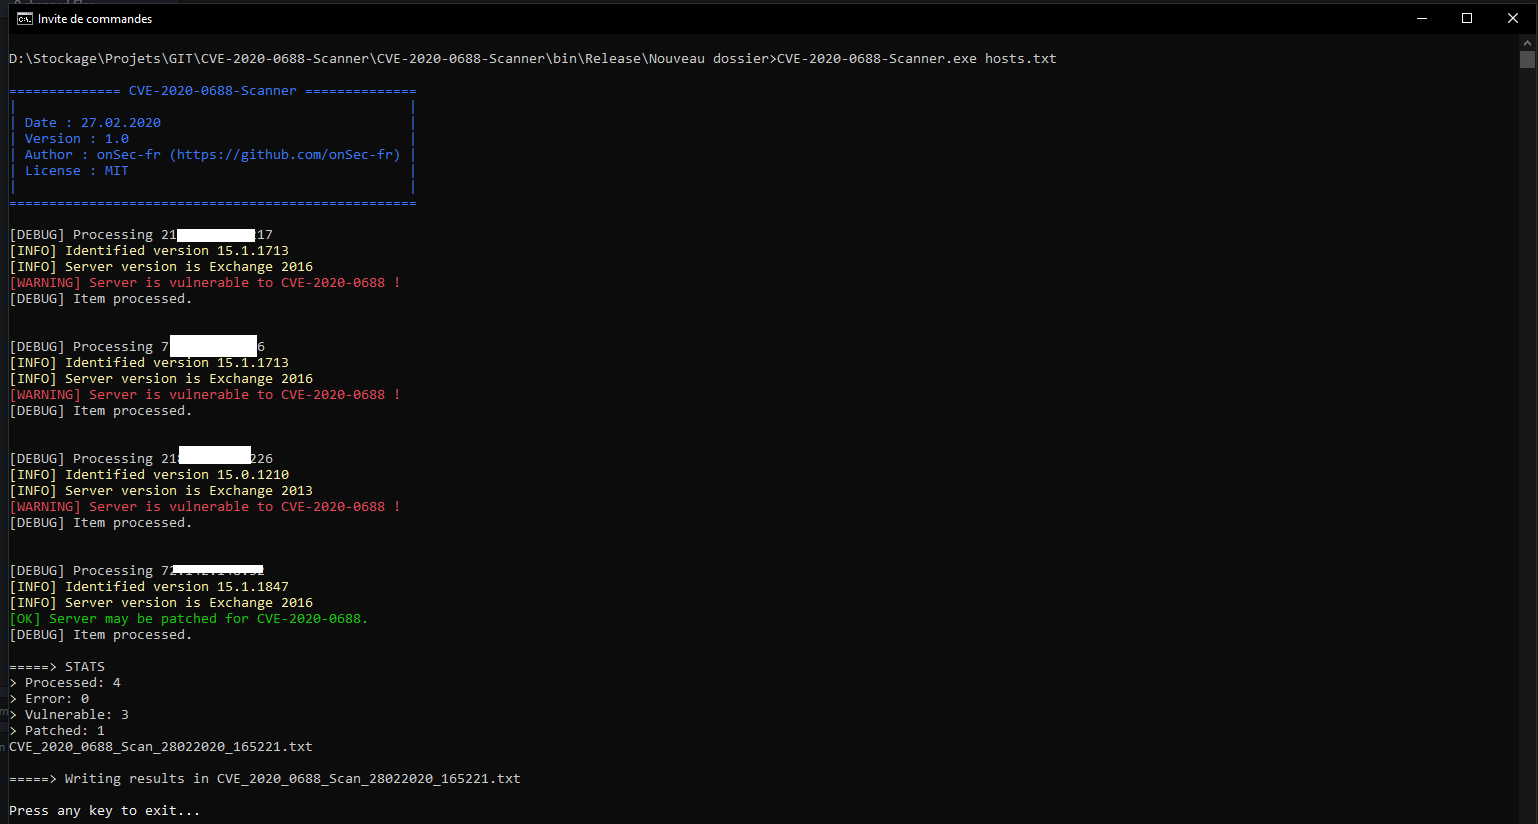
  • Passive check : grab exchange version by scraping html content.
  • Produces an output file.

Demo

How to use

Prerequisite

  • Windows
  • .NET framework 4.5.2

Download

git clone https://github.com/onSec-fr/CVE-2020-0688-Scanner.git

Run

./CVE-2020-0688-Scanner.exe [path_to_input_file]

Note : the input file can contain ip addresses, hostnames and FQDN.

Disclaimer

This tool has been developed to test your own system or for authorized security testing. Make sure you check with your local laws before running this tool.

Limitations

Since Exchange 2013, only the first 3 parts of the version number can be retrieved in this way. This means that sometimes the server may be vulnerable if it has not the very last cumulative update. In this case the server is flagged as "maybe patched".

References

  • Unofficial build chart lists all of the known KB articles, hotfixes, update rollups and other builds of MS Exchange Server 2019, 2016, 2013, 2010, 2007, 2003, 2000, 5.5, 5.0 and 4.0 that have been released. : https://exchangeserverversions.blogspot.com/
  • Analysis of CVE-2020-0688 : https://www.thezdi.com/blog/2020/2/24/cve-2020-0688-remote-code-execution-on-microsoft-exchange-server-through-fixed-cryptographic-keys
  • https://fr.tenable.com/blog/cve-2020-0688-microsoft-exchange-server-static-key-flaw-could-lead-to-remote-code-execution
  • nmap implementation by Kevin Beaumont : https://github.com/PwnPeter/0day-scripts/blob/2845b2d7a62c1baec581afab8fb065dde4f63413/nmap-nse/http-vuln-exchange.nse
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →








