
 mistyfir/cve-2024-21338-exploit
Proof-of-concept exploit for CVE-2024-21338, a Windows AppLocker driver (appid.sys) privilege escalation vulnerability used by Lazarus group as a 0day. Achieves kernel read/write via crafted IOCTL requests and PreviousMode manipulation.

This is a POC for CVE-2024-21338, a privilege escalation vulnerability in the Windows AppLocker driver (appid.sys). It was exploited as a 0-day by the Lazarus group for local privilege escalation on Windows.
CVE-2024-21338 is a privilege escalation vulnerability disclosed in the Microsoft Patch Tuesday of February 13, 2024. It was exploited by the Lazarus hacker group to gain kernel access for deploying the FudModule rootkit.
The vulnerability exists in the 0x22A018 control code of the appid.sys driver. An attacker can trigger the vulnerability by sending a specially crafted IOCTL request, enabling arbitrary callback invocations and ultimately obtaining kernel read/write permissions.
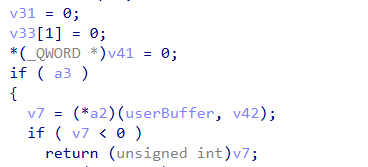
The vulnerability resides in the AppHashComputeImageHashInternal function of the appid.sys driver. AipDeviceIoControlDispatch does not properly check PreviousMode when processing the 0x22A018 request, allowing user-mode processes to trigger kernel-mode callback functions.
Obtain Local Service Privilege: The vulnerability requires Local Service privileges to access the \\Device\\AppID device. Therefore, the tool first finds and impersonates a Local Service process.
Construct IOCTL Request: The tool crafts a specially crafted IOCTL request containing a controllable function pointer and parameters.
Trigger the Vulnerability: By sending the IOCTL request, the vulnerability is triggered, invoking a kernel gadget function that modifies the PreviousMode field of the current thread, changing it from user mode to kernel mode.
Gain Kernel Read/Write Permissions: After modifying PreviousMode, the user-mode process can use NtReadVirtualMemory and NtWriteVirtualMemory to read and write arbitrary kernel memory.
| File Name | Description |
|---|---|
| main.cpp | Main function, responsible for the flow control of the exploit |
| CVE-2024-21338.h | Vulnerability-related structure and function declarations |
| CVE-2024-21338.cpp | Implementation functions for the prerequisites of the exploit |
| export_func.h | Declaration of exported functions |
| gadget_search.cpp | Implementation of kernel gadget search |
| Native.h | Definition of native Native API |
| PE.h | Utility functions for processing PE files |
Compile this project using Visual Studio 2022, requiring Windows SDK and C++ compiler support.
Enable the Application Identity service on an unpatched Windows system (e.g., Windows 10 1709).
Run the compiled executable with administrator privileges.
The tool will automatically find a Local Service process and impersonate it.
The tool loads the appid.sys driver and constructs an IOCTL request to trigger the vulnerability.
After successful exploitation, the tool prompts for the kernel address and value to modify, enabling kernel memory modification.
This project is intended for educational and research purposes only. It must not be used for illegal activities.






