
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cve-2021-21735-zte-zxhn-h168n-admin-compromise — CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full admin compromise. | Kitploit
Tools/GitHubGitHub/minanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise
Embedded Systems SecurityVulnerability AnalysisExploitationInformation GatheringPenetration TestingFirmware Analysis
GitHubminanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise

cve-2021-21735-zte-zxhn-h168n-admin-compromise

Share

CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full admin compromise.

View RepositoryWebsite
3386 months agoNot yet reviewed

CVE-2021-21735: ZTE ZXHN H168N Information Leak to Full Admin Compromise

Technical case study and GitHub Pages-ready write-up for CVE-2021-21735 in the ZTE ZXHN H168N V3.5.

This repository focuses on the firmware routing flaw behind the exposed wizard endpoints, the disclosure timeline, the scoring split between the vendor advisory and NVD, and the practical path from information leak to full administrative compromise.
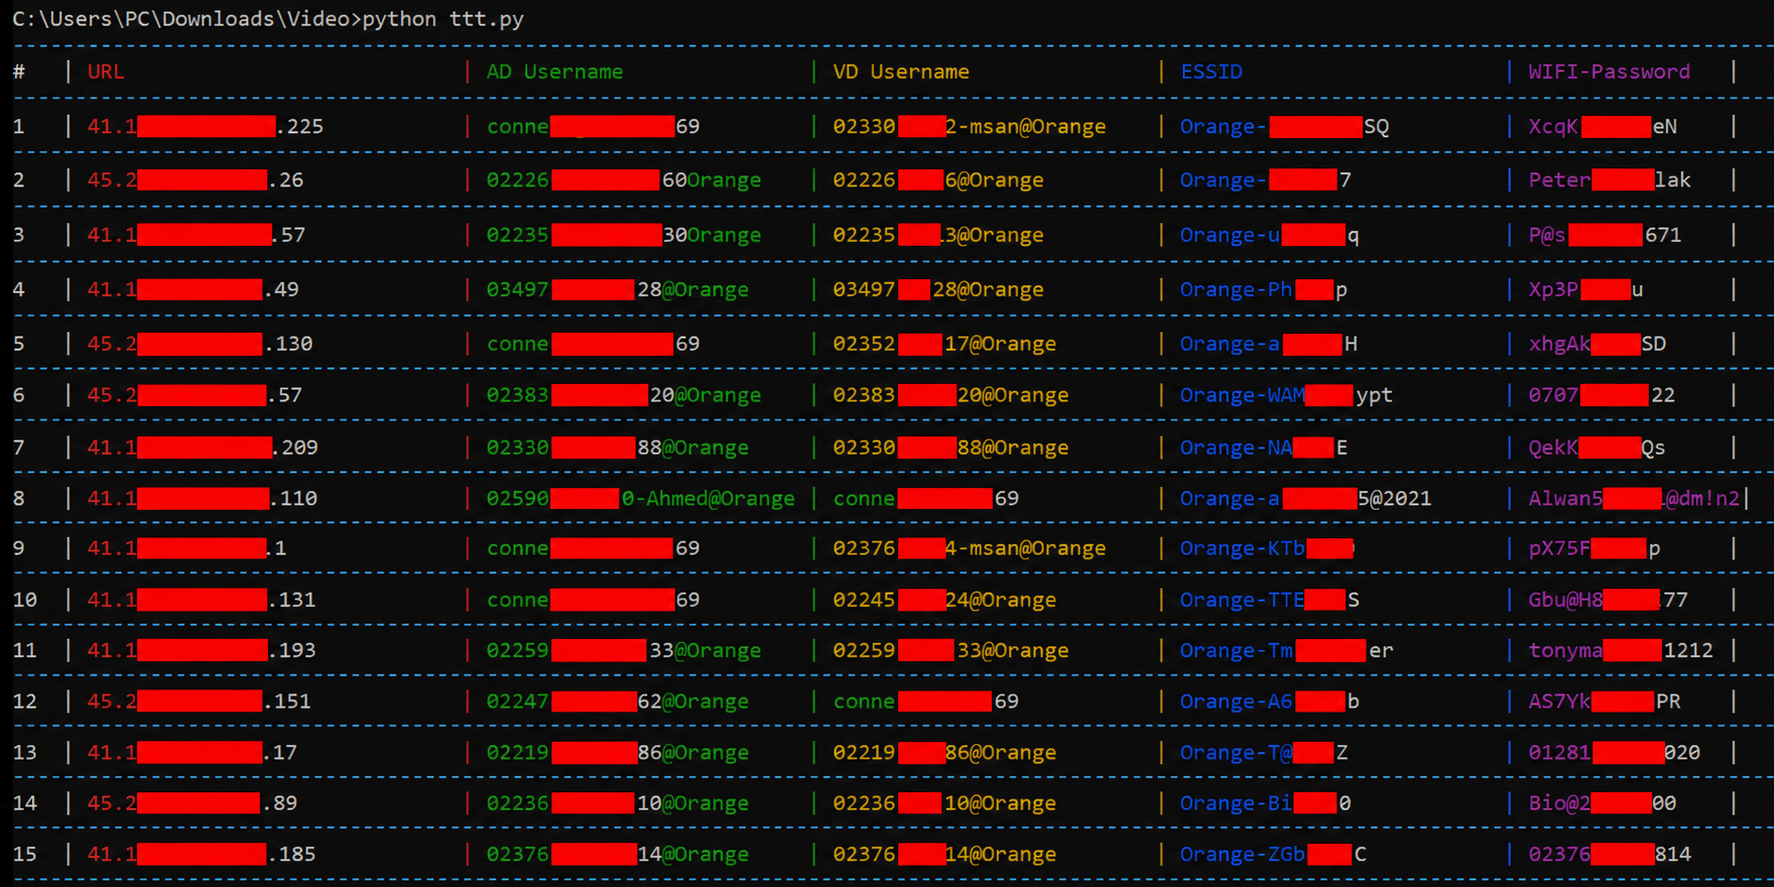
Redacted proof image for CVE-2021-21735

What This Repo Contains

  • index.html: the main article page, designed for GitHub Pages
  • zte_zxhn_h168n_bulk_poc.py: bulk proof-of-concept script for the exposed wizard endpoints
  • requirements.txt: minimal Python dependencies for the PoC
  • hero.png: hero visual used in the article header
  • Codecleaned.png: cleaned firmware screenshot used in the root cause analysis
  • Redacted.png: redacted proof image used in the evidence section

Core Angle

This write-up treats CVE-2021-21735 as more than a generic information disclosure:

  • exposed wizard handlers returned PPPoE and WLAN data
  • firmware allowlisting appears to admit sensitive setup routes through a QuickSetupEnable branch
  • deployment-side credential practices could turn the leak into full admin compromise

PoC

The repository includes a bulk PoC that demonstrates the exposed wizard-page behavior described in the write-up across a host list:

python -m pip install -r requirements.txt
python .\zte_zxhn_h168n_bulk_poc.py --input .\urls.txt

The script fetches:

  • PPPoE ADUsername
  • PPPoE VDUsername
  • WLAN ESSID
  • WLAN KeyPassphrase via the unauthenticated GetPassword action

Expected input:

  • urls.txt: newline-delimited list of target hosts or IPs

Publishing Note

The repository is prepared for GitHub Pages, but Pages is not being enabled yet because a published GitHub Pages site becomes publicly accessible even when the repository itself remains private.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    972
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    666
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    424
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    389
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    337
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    331

Explore all tools

Browse our collection of tools

View all tools →


